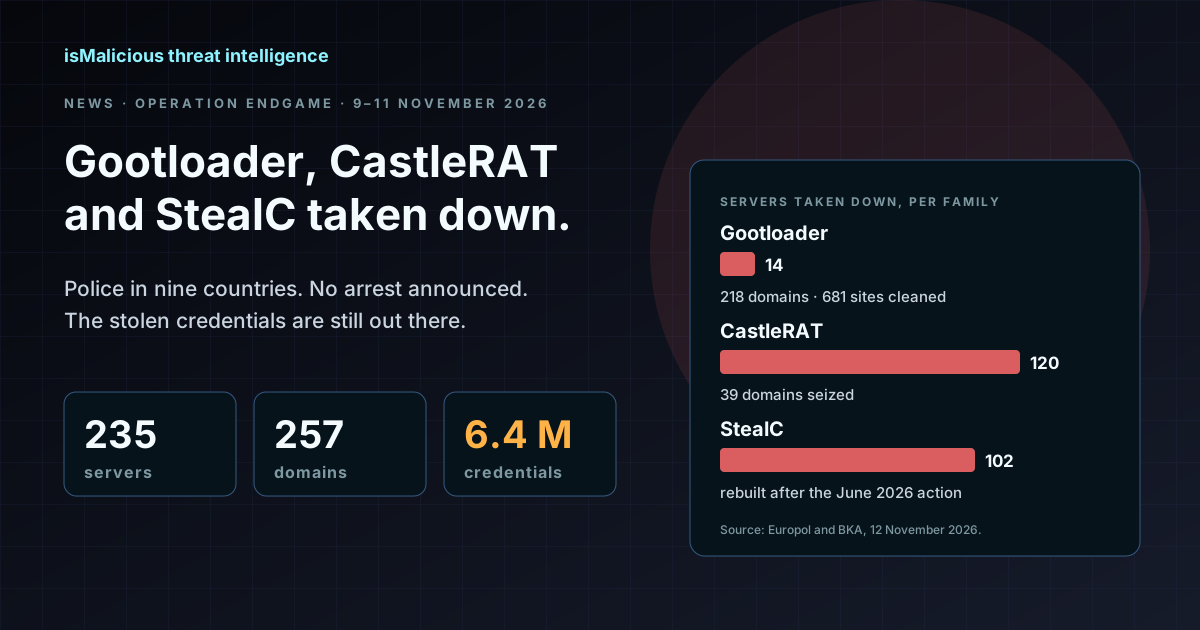
Operation Endgame Takes Down Gootloader, CastleRAT and StealC: What Defenders Should Hunt Now
Between 9 and 11 November 2026, Operation Endgame took down the servers and domains behind Gootloader, CastleRAT and StealC and secured about 6.4 million stolen credentials. No arrest was announced. The infrastructure is gone; the infected hosts, the stolen passwords and the access already sold are not.
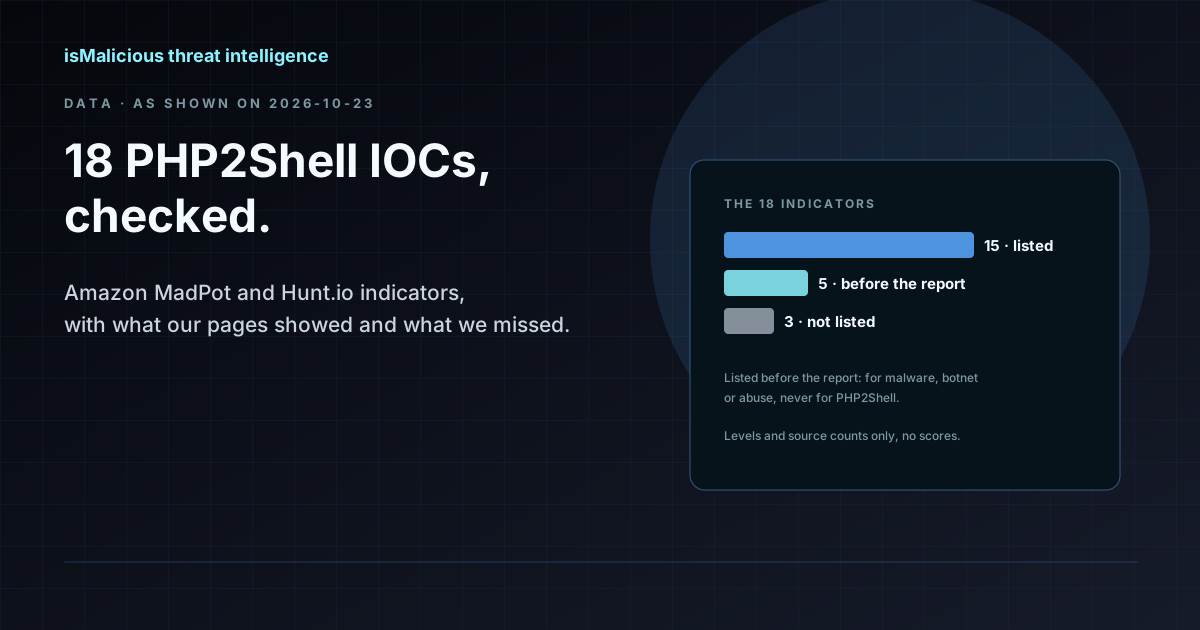
PHP2Shell IOCs from Amazon and Hunt.io, checked against isMalicious
18 published PHP2Shell indicators, looked up on 23 October 2026: 15 listed, 5 provably before the report that named them, for malware or abuse, and 3 missed.
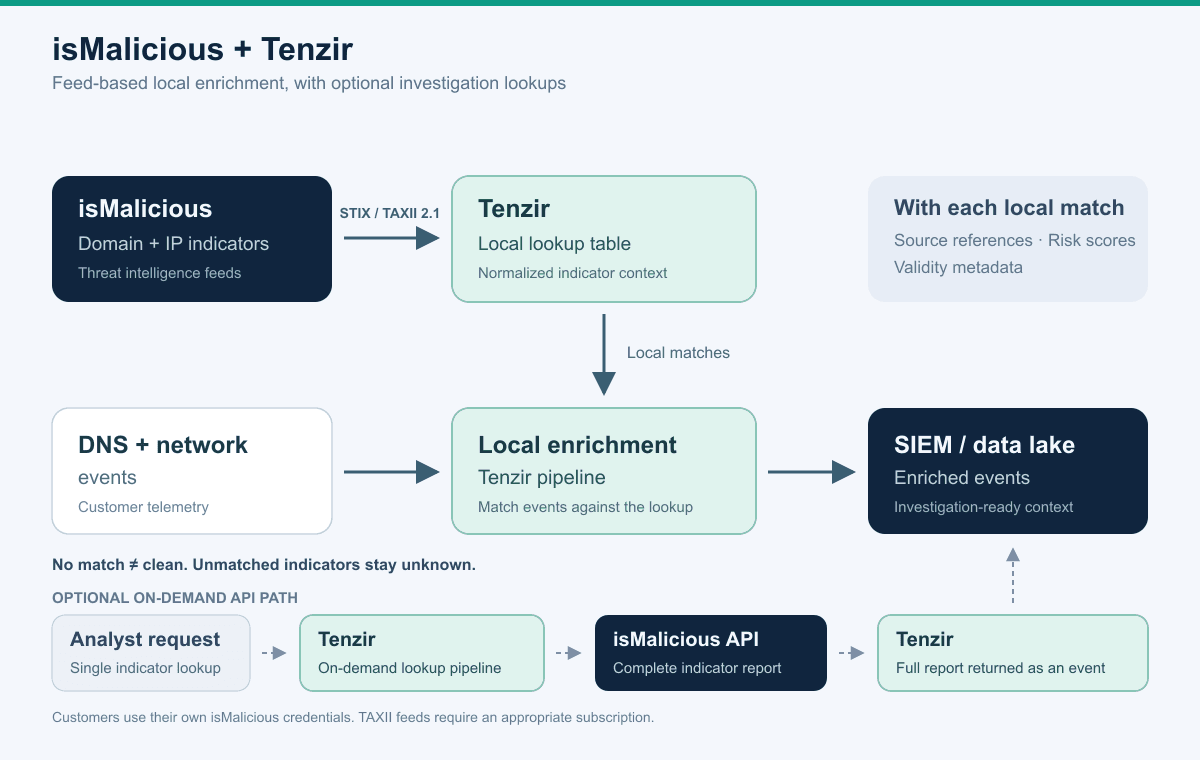
isMalicious + Tenzir: Threat Intel in Your Pipeline
Connect isMalicious domain and IP feeds to Tenzir over STIX/TAXII for local DNS and network enrichment, with optional API lookups for investigations.
Revoked Certificates: Interpret OCSP and CRL Results
Separate revocation, expiration, and domain reputation. Verify the exact certificate, status freshness, and behavior observed by the client.
STIX: Indicator vs Observed Data
Separate a detection pattern, an observed fact, and a STIX Sighting so your IOC pipeline does not turn every recorded event into a threat.
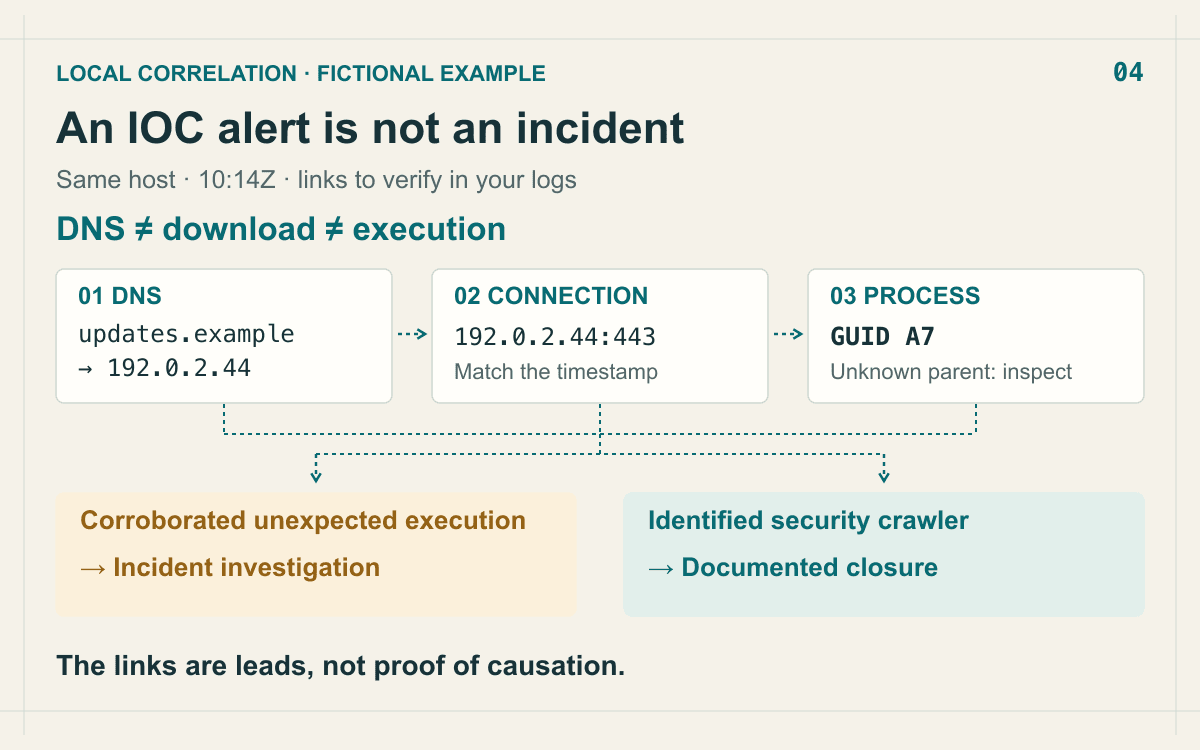
Defang and Refang: Handle hxxp and IOCs Correctly
Share defanged IOCs while retaining usable evidence: separate display, conversion, validation and submission to external services.
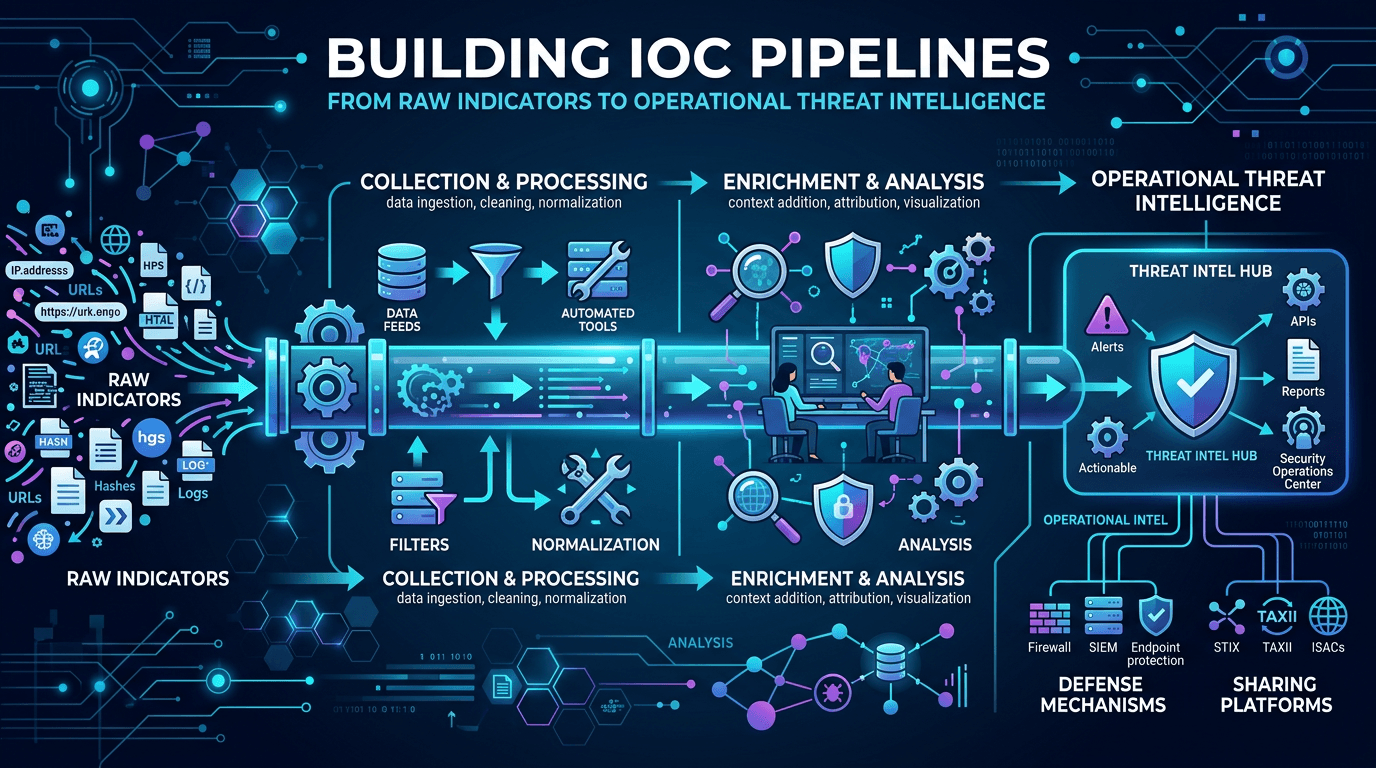
URL Normalization: Avoid Incorrect IOC Matches
Compare URLs while preserving evidence: case, encoding, parameters and fragments need explicit rules and tests for values that must stay distinct.
DNS TTL: Investigate a Change of IP Address
Reconstruct DNS address changes using dated responses, caches and network views, without confusing TTL with the lifetime of a threat.
CNAME Cloaking: Investigate a Third-Party Subdomain
Trace CNAME records, identify the provider, and inspect transmitted cookies before deciding whether a subdomain should remain authorized.
Parked Domains: Assess the Risk Before Blocking
Distinguish domain parking, expiration, and malicious behavior. Examine actual use and choose a restriction supported by the evidence.
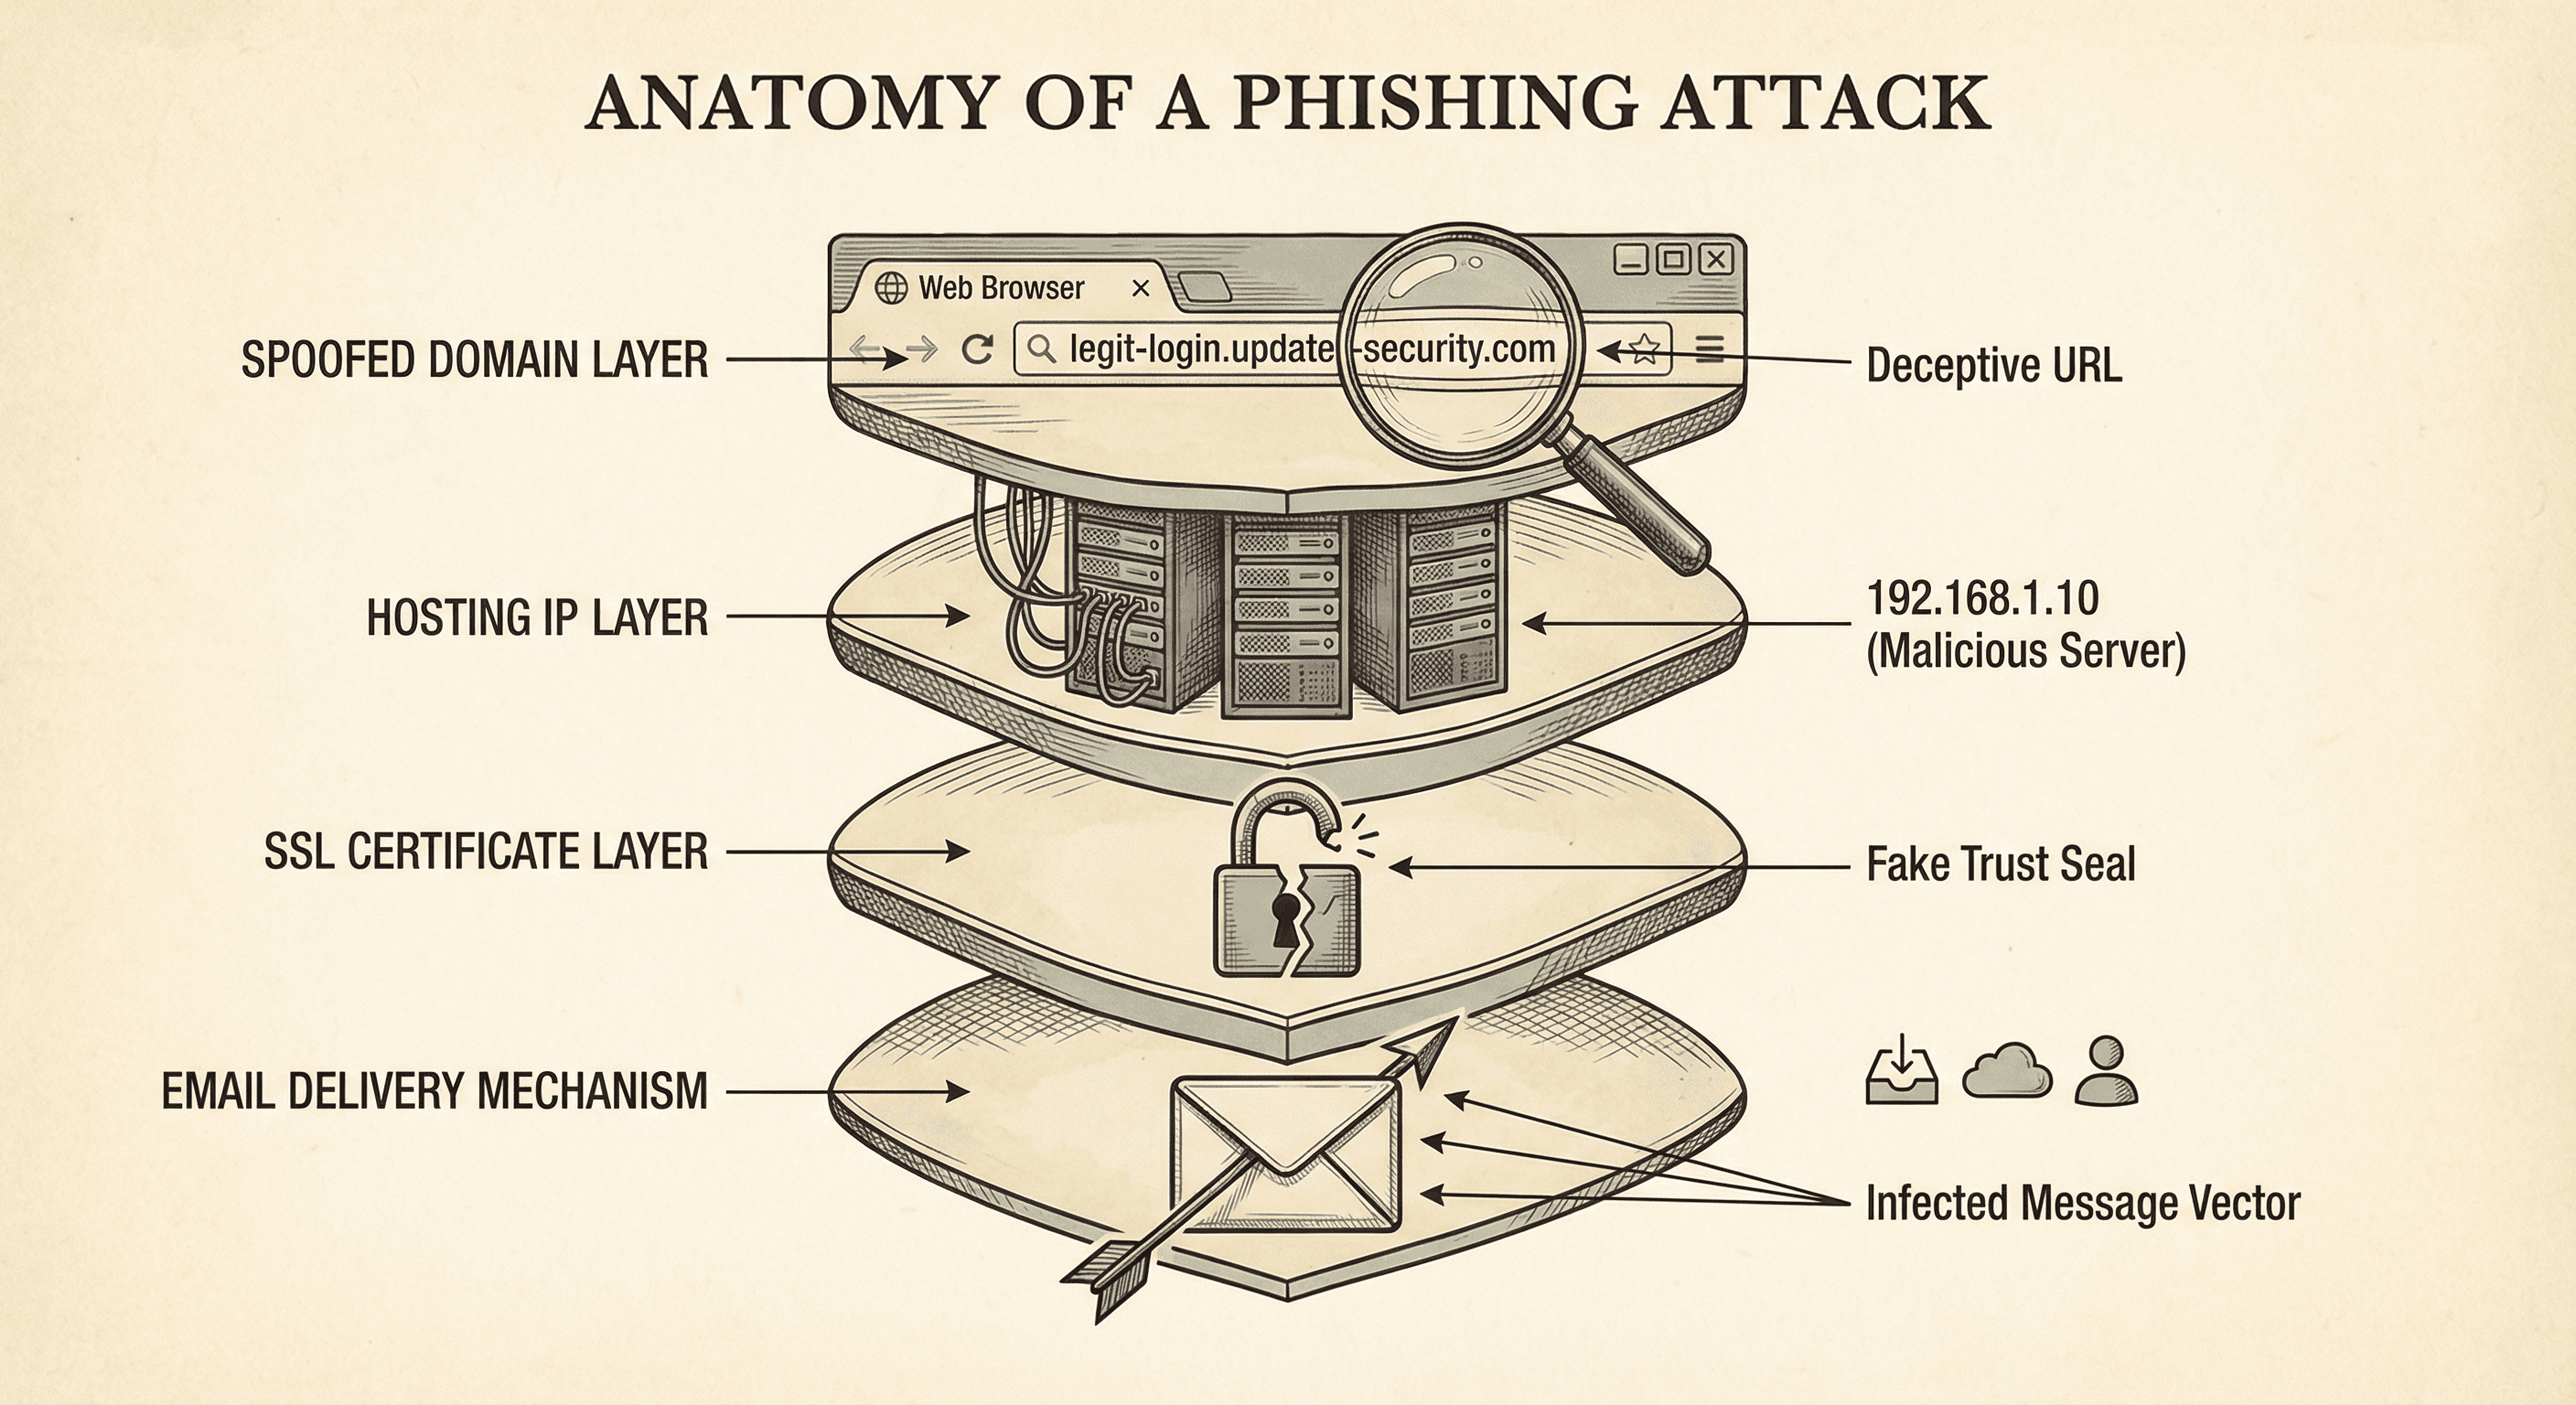
RDAP: Read Domain Data During an Investigation
Use RDAP events, statuses, and contacts to document a suspicious domain without misattributing an identity or claiming an unproven compromise.
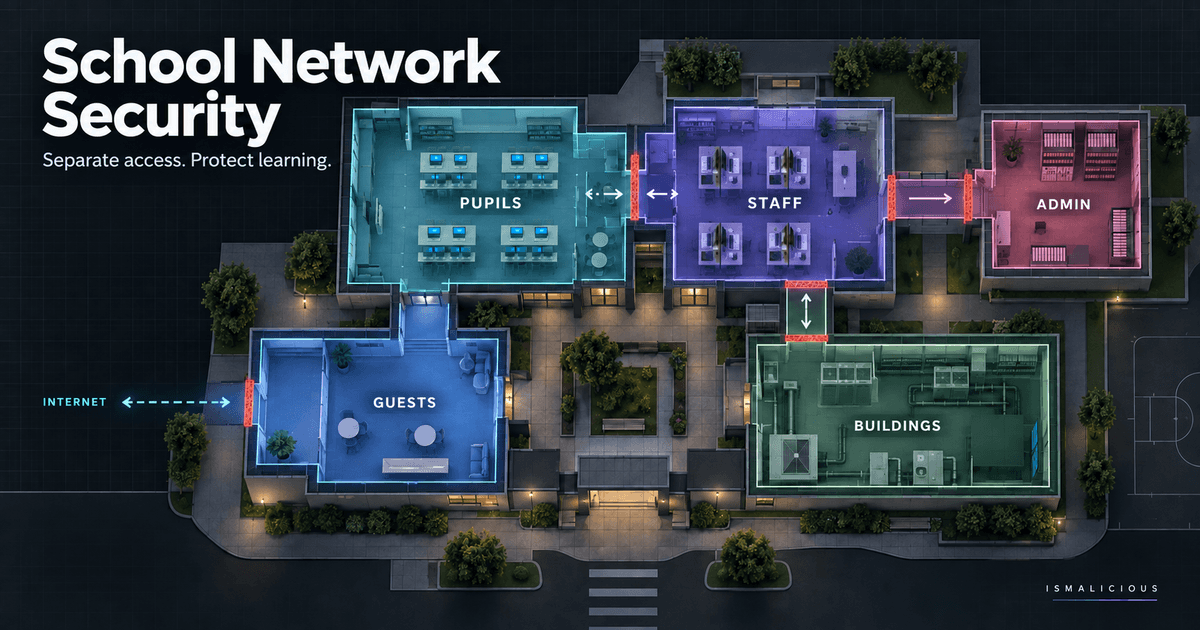
School Network Security: Test Segmentation That Works
Plan school network segmentation around teaching needs, test permitted and blocked paths, protect administration, and manage changes without losing access.
CTI Analyst Portfolio: Build a Safe, Reproducible Lab
Build a CTI analyst portfolio with offline datasets, evidence-led assessments, reproducible results, and a review rubric that shows how you make decisions.
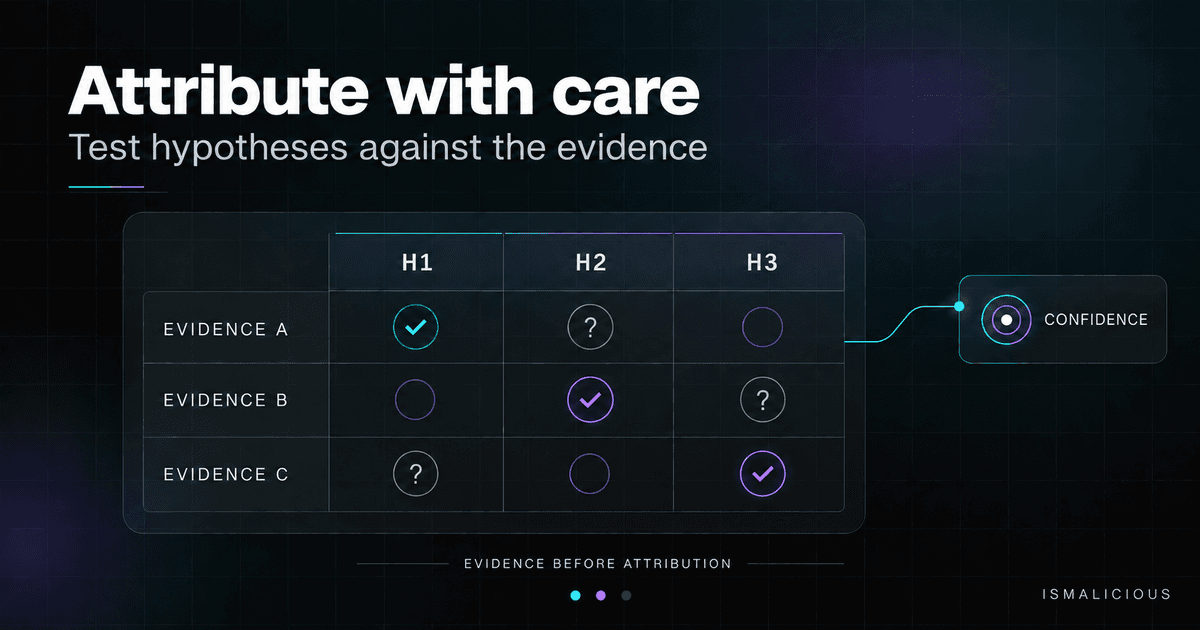
Cyber Attribution: Confidence and Competing Hypotheses
Assess cyber attribution with evidence, competing hypotheses, and explicit confidence. Use a practical judgment record without treating an IOC as an identity.
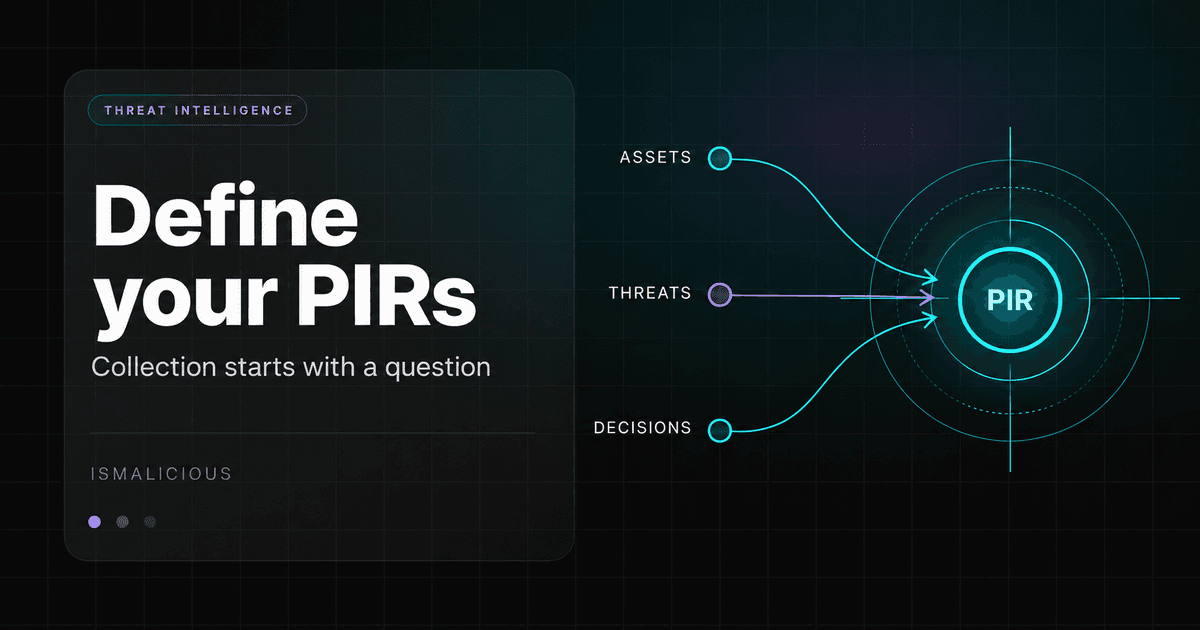
Threat Intelligence PIRs: A Workbook and Collection Plan
Turn threat intelligence requests into useful PIRs with a decision worksheet, collection plan, evidence requirements, ownership, and practical stopping rules.
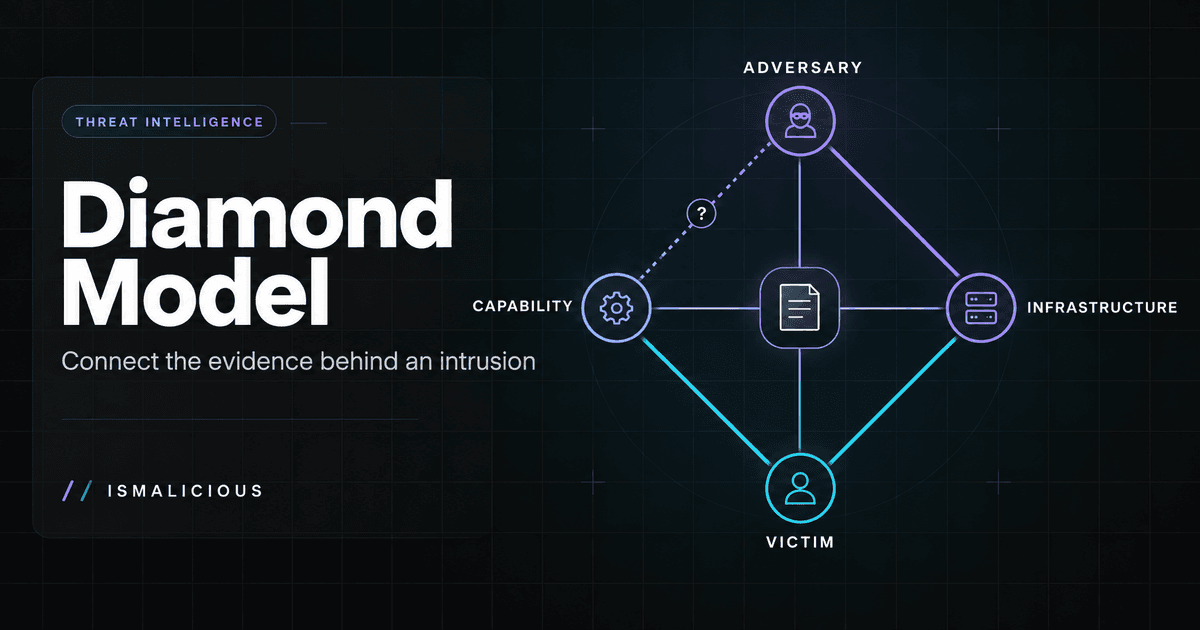
Diamond Model: A Practical CTI Investigation Walkthrough
Use the Diamond Model to connect evidence, test competing explanations, build activity threads, and turn a phishing investigation into defensible decisions.
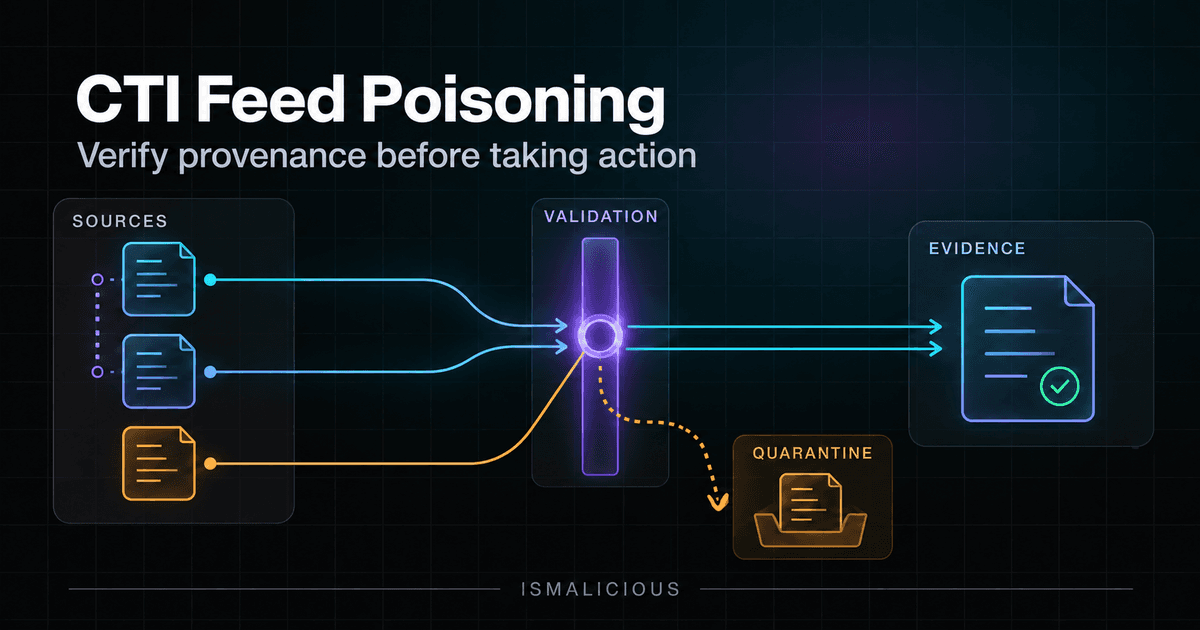
Threat Intelligence Feed Poisoning: Protect Your Evidence
Protect CTI decisions from misleading data with source provenance, mirror detection, contradiction handling, safe ingestion, human review, and tested rollback.
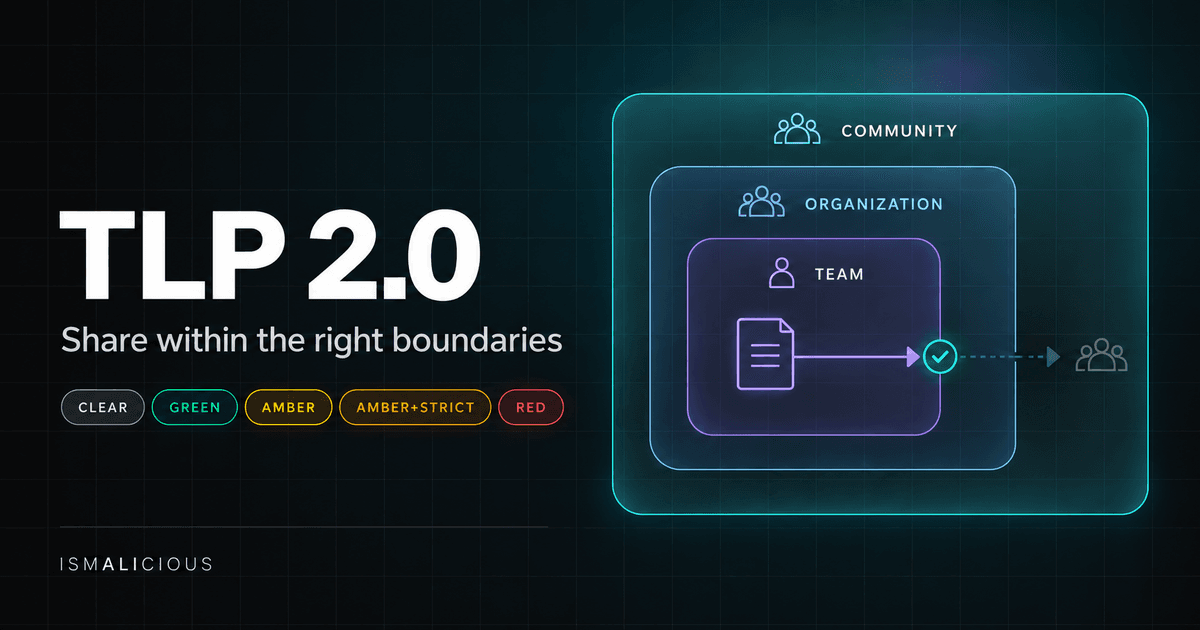
TLP 2.0: Share Threat Intelligence Without Leaking Data
Apply TLP 2.0 to CTI reports, indicators, and supplier exchanges with practical sharing boundaries, permission checks, data minimization, and export controls.
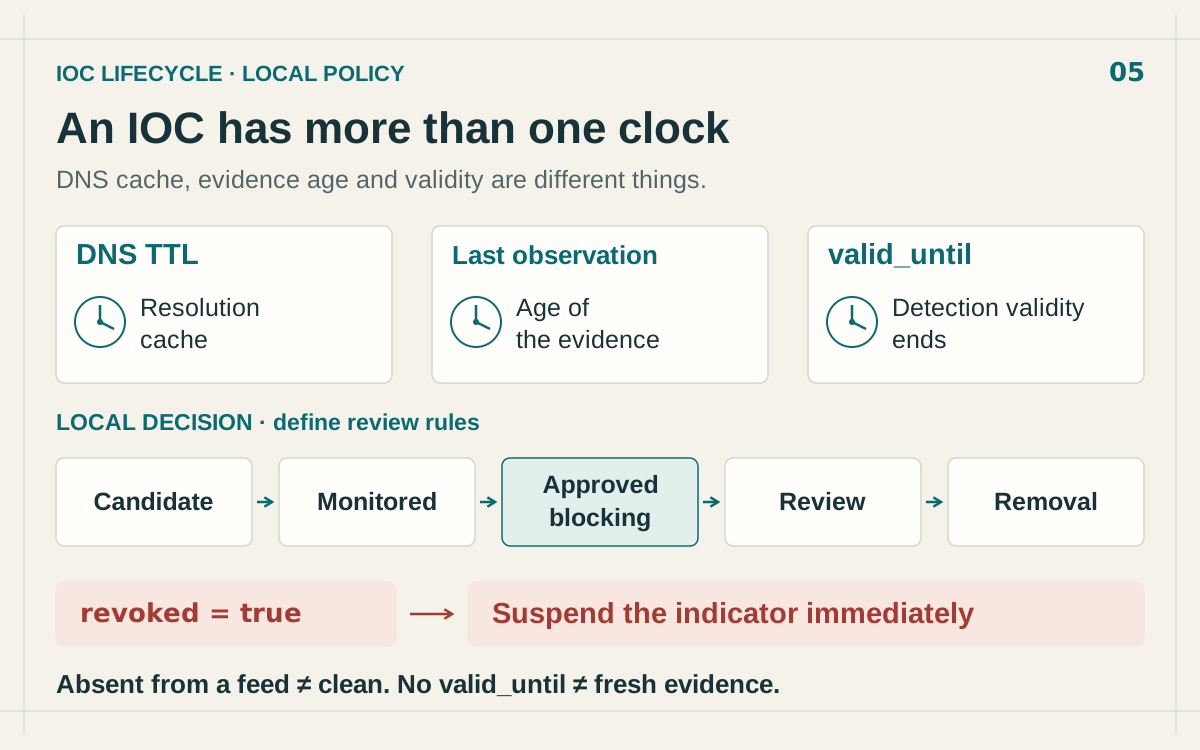
IOC Expiration: When to Remove an IP From a Blocklist
Manage IOC expiration with separate DNS, evidence and STIX validity clocks. Review stale IP blocks, process withdrawals and preserve the audit trail.
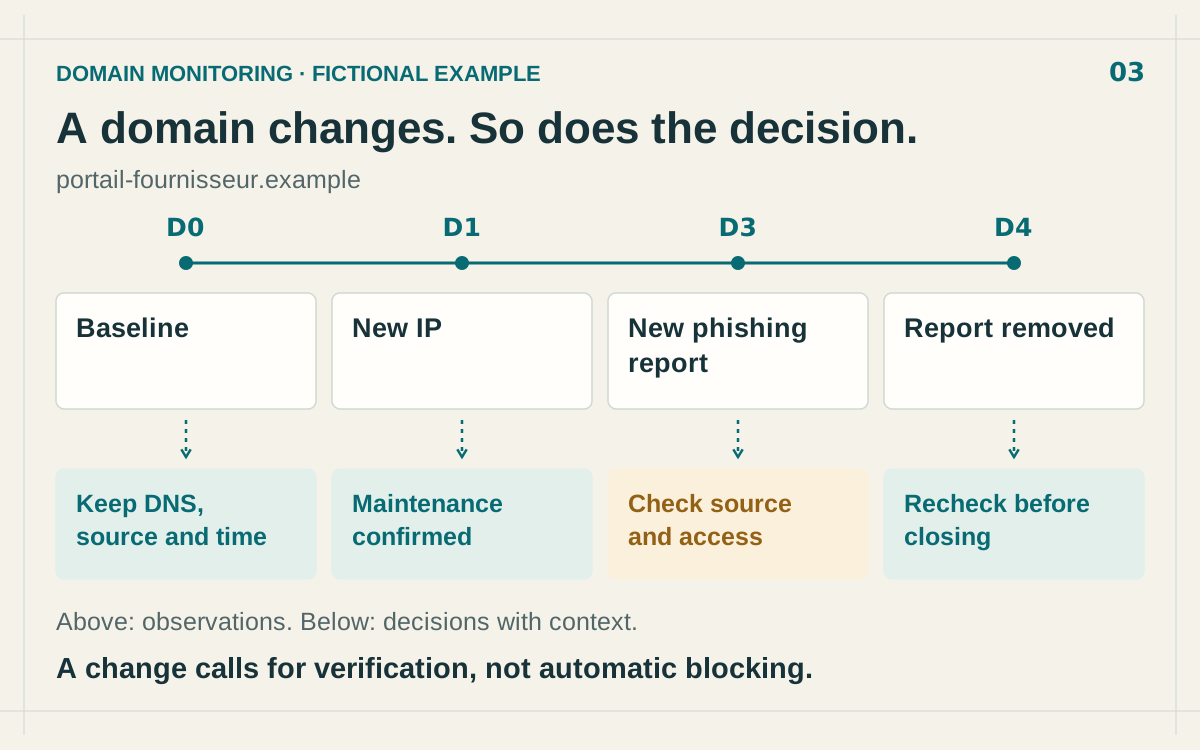
Domain Reputation Monitoring: Which Changes Need Action?
Track domain reputation over time: distinguish a new phishing report from expected DNS changes, then decide what to verify before restricting access.
Smart Lookup: Check Any Threat Indicator from One Search
Paste an IP, domain, URL, email, phone number, wallet, file hash, or a complete suspicious message. Smart Lookup routes each indicator to the right threat report.
Composite Threat Reports: Triage Multiple IOCs Together
A phishing message or security alert rarely contains one indicator. Use a composite threat report to scope several IOCs without losing the evidence behind each result.
Threats Dashboard: Turn Current Intelligence into Priorities
Use the isMalicious Threats dashboard to move from a broad threat picture to the sectors, ransomware groups, malware, victims, and evidence that matter to your team.
TAXII Threat Feeds: Build a Continuous SIEM Integration
Connect an isMalicious TAXII collection to your SIEM with safe pagination, durable checkpoints, validation, monitoring, and recovery.