Splunk HEC
Push IOCs and SOC events through HTTP Event Collector, configured in the dashboard. Not a Splunkbase app.
Push indicators to Splunk, Elastic or Sentinel, or poll TAXII 2.1. Feed access requires Pro or Enterprise.
Pro: €99/month. Enterprise: quotation. TAXII polling does not consume the monthly lookup quota. The Free plan does not include feed access.
Current indicator counts available through TAXII and the API.
29 986 142
Total threats
20 416 459
Malicious domains
9 569 683
Malicious IPs
591
Sources in the corpus
No credit card required · Free: a 10% sample of each list · full lists on paid plans
Push IOCs and SOC events through HTTP Event Collector, configured in the dashboard. Not a Splunkbase app.
Index IOCs through the Elastic Bulk API from the dashboard. Not a Fleet package.
Ingest indicators with Sentinel’s built-in TAXII connector. Optional Log Analytics destination for events.
Poll TAXII 2.1 collections of STIX 2.1 indicators with any client your SIEM supports.
REST API for custom enrichment inside your SIEM pipelines.
Add source context to selected events, then review the result.
Match events against imported indicators, keeping source context for review.
Write detection rules on imported indicators.
Keep imported indicators and their sources as audit evidence.
Check the returned reputation, source evidence and dates against your telemetry before adding a blocking rule. A score alone proves neither attribution nor intent.
Blog post
Connect an isMalicious TAXII collection to your SIEM with safe pagination, durable checkpoints, validation, monitoring, and recovery.
Read more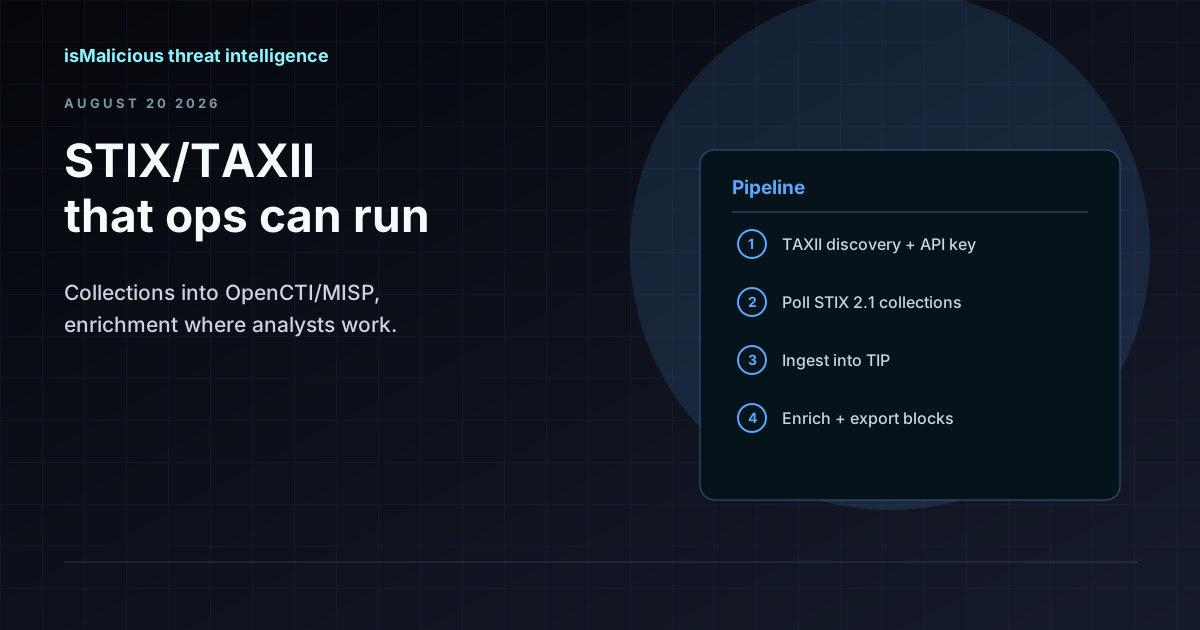
Blog post
How to wire STIX 2.1 and TAXII 2.1 collections into OpenCTI, MISP, or your SIEM — what to poll, how to handle confidence and aging indicators, and where enrichment APIs fit alongside feed ingestion.
Read more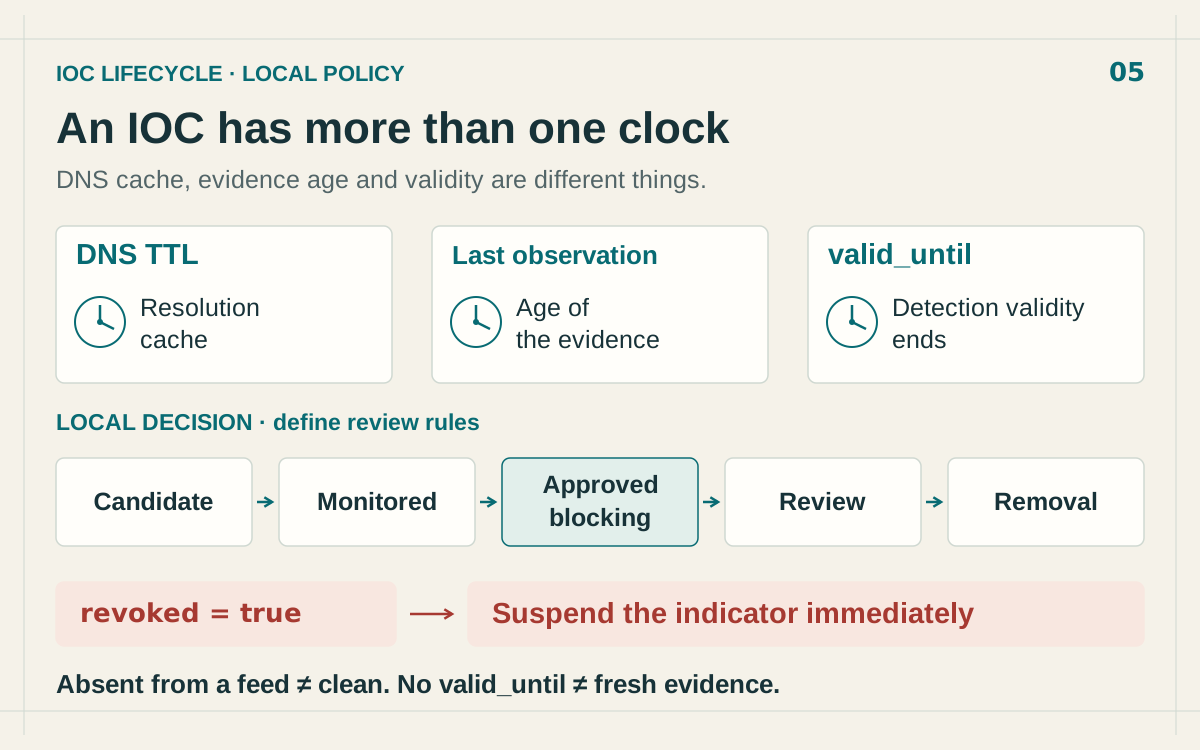
Blog post
Manage IOC expiration with separate DNS, evidence and STIX validity clocks. Review stale IP blocks, process withdrawals and preserve the audit trail.
Read moreTell us your current tool, the gap to close, expected volume and decision date. We scope an evaluation against your sources.
Pro: €99/month. Enterprise: quotation. TAXII polling does not consume the monthly lookup quota. The Free plan does not include feed access.