Firewall guides
Step-by-step guides for iptables, pfSense, FortiGate and Palo Alto. Any firewall that reads a URL list works.
Point your firewall at a blocklist URL: IPs, domains, URLs or hashes, by severity or category.
No credit card required · Free API key
Blocklist categories available as firewall feeds.
29 986 142
Total threats
20 416 459
Malicious domains
9 569 683
Malicious IPs
591
Sources in the corpus
No credit card required · Free: a 10% sample of each list · full lists on paid plans
Step-by-step guides for iptables, pfSense, FortiGate and Palo Alto. Any firewall that reads a URL list works.
Lists are rebuilt on a schedule; /blocklist/stats shows each file’s freshness, no key needed.
Malicious IPs by severity or category, including C2, botnet, brute force, Tor and proxy.
Phishing, malware, scam and spam domains, also in hosts, dnsmasq and AdGuard formats.
Pick a severity level from critical to low, or a single category, for each list.
Report a wrong listing at /delist. Pro and Enterprise teams can also exclude it from their TAXII pulls.
Block known malicious IPs at the network edge.
Cut malware off from its command-and-control servers.
Block access to phishing and scam domains.
Load domain lists into dnsmasq or AdGuard resolvers.
Blog post
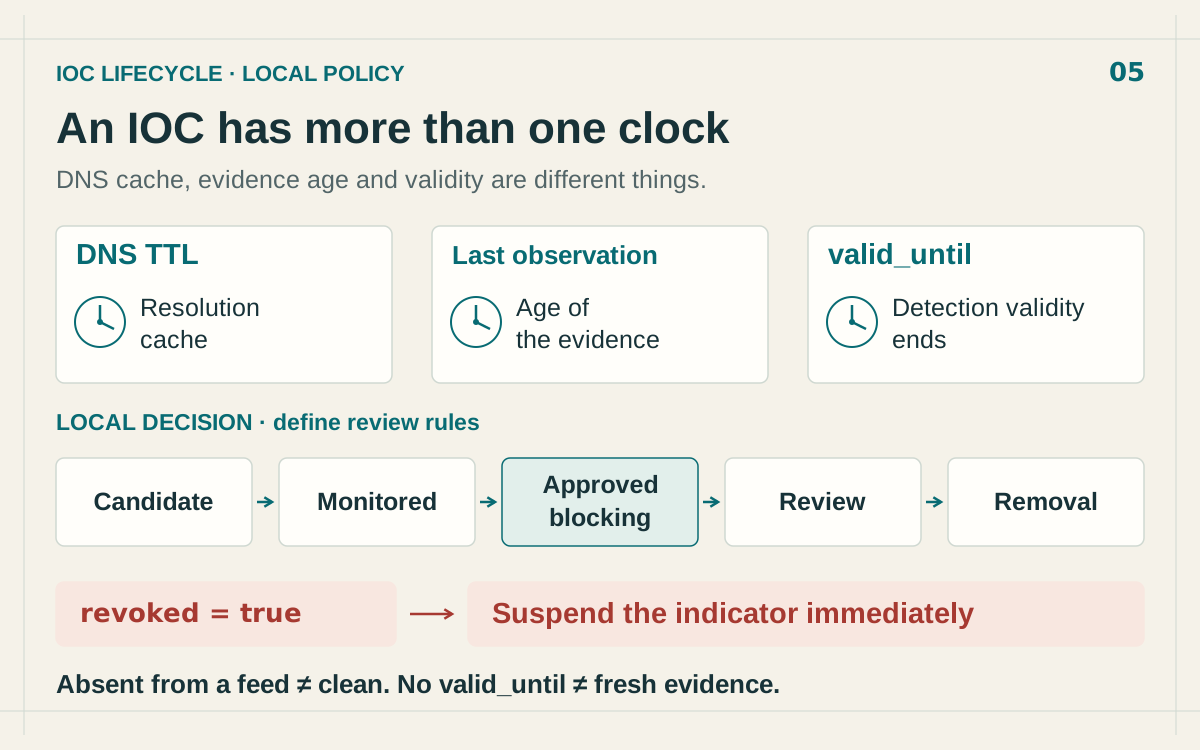
Manage IOC expiration with separate DNS, evidence and STIX validity clocks. Review stale IP blocks, process withdrawals and preserve the audit trail.
Read more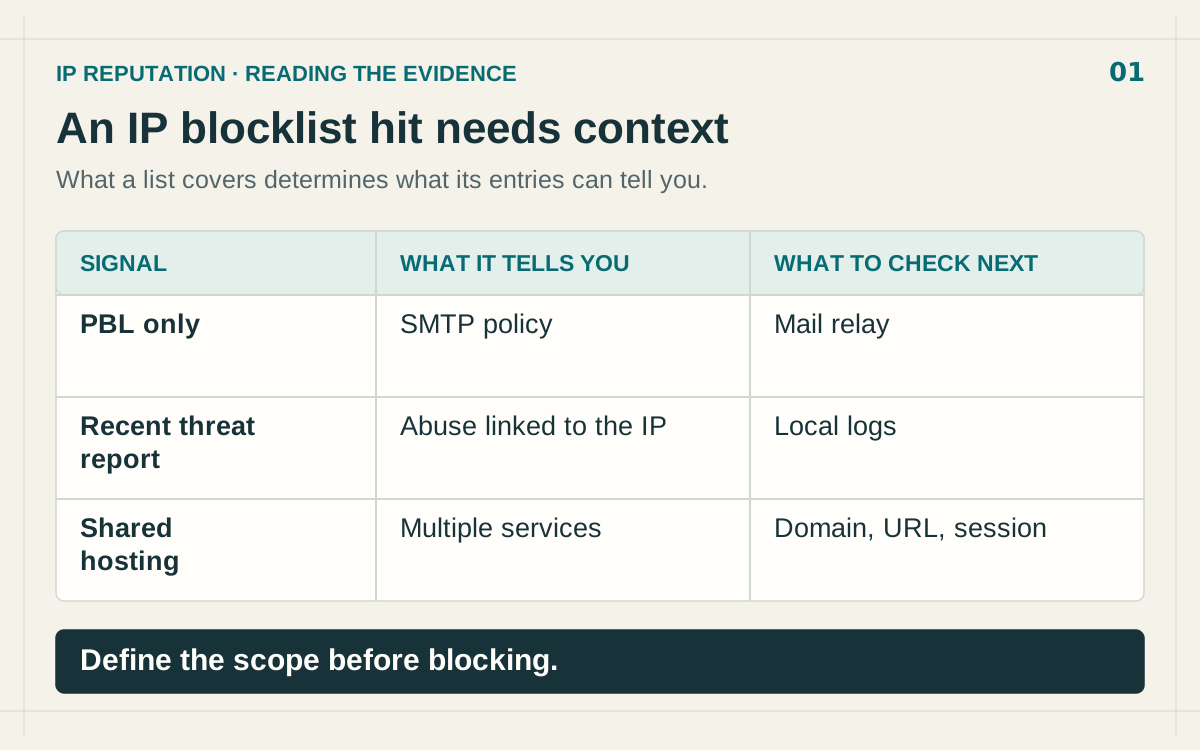
Blog post
Check DNSBL scope, shared IPs, stale evidence and lookup errors to find why an IP was blacklisted and choose a proportionate response.
Read more
Blog post
Zero Trust security demands constant verification. Discover how integrating malicious IP and domain reputation checks strengthens your threat intelligence and prevents phishing.
Read moreThe free plan includes 50 lookups a month. Check the sources and limits, then connect the API.
No credit card required · Free API key