Threat Intelligence Blog
Research, insights, and updates from the isMalicious team.

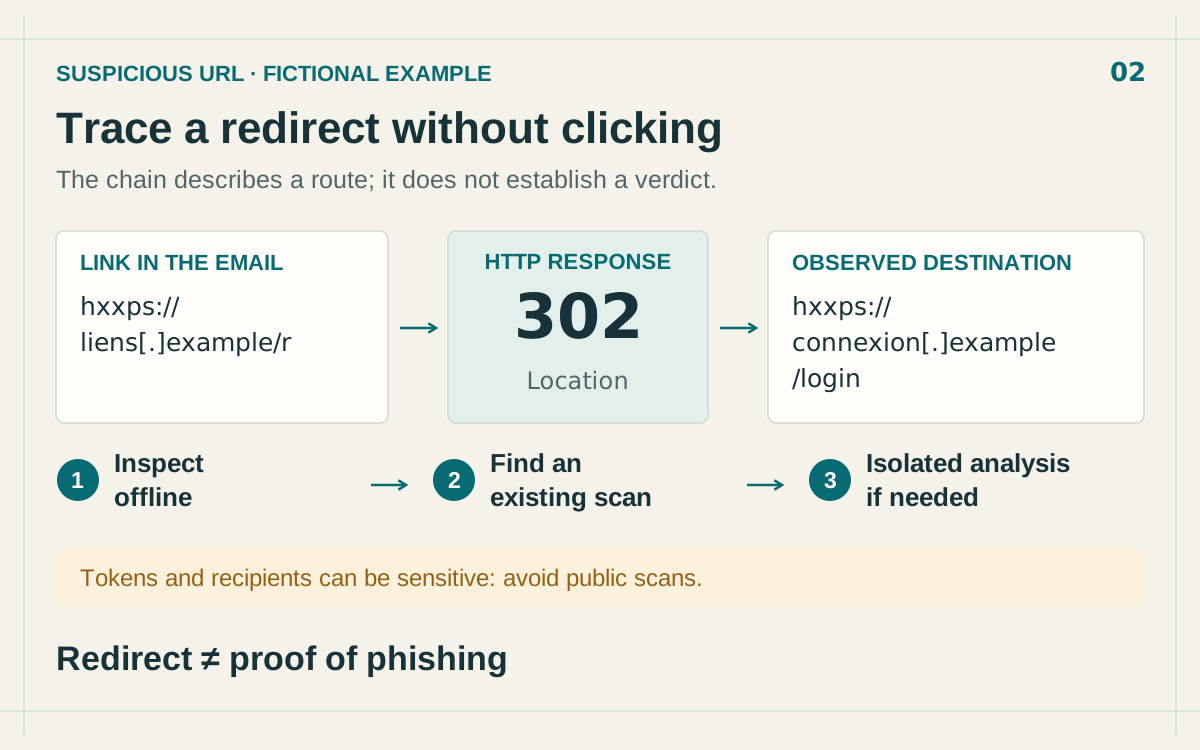
Suspicious URL? Check Redirects Without Opening It
Inspect a suspicious link, find previously observed redirects and protect private tokens before deciding whether to run an isolated scan.
Browser-in-the-Browser Phishing: Detection Guide
Understand browser-in-the-browser phishing, spot fake SSO windows, detect campaign infrastructure, and reduce risk with phishing-resistant authentication.
Certificate Transparency for Phishing Detection
Use Certificate Transparency logs to find rogue certificates, phishing subdomains, brand impersonation, and exposed assets before they become incidents.

How to Use an NRD Feed to Catch Phishing Before It Lands in the Inbox
Newly registered domains are where most phishing campaigns start. This guide walks through NRD feed workflows for brand monitoring, mail gateway hygiene, and SOC triage — without treating domain age as a blunt block rule.
WHOIS Lookup for Security Investigations: Reading a Record After Redaction
Privacy services stripped the registrant name out of most WHOIS records, but the fields that matter for triage survived. Here is what a WHOIS record still tells an analyst, and how to read it.
The Kratos Phishing Kit Takedown: 200 Servers Gone, 1,800 Copies Still Out There
German and US law enforcement dismantled Kratos, the AiTM phishing service behind roughly 15,000 Microsoft 365 campaigns a month. The infrastructure is offline, but the kit is not. Here is what to hunt for now.
SSO Vishing And SaaS Data Theft: Domain Monitoring Before The Helpdesk Call
ShinyHunters-style SSO vishing shows how fake login domains, MFA enrollment abuse, and SaaS access can become data theft. Domain monitoring gives defenders early warning.
Mobile Smishing Defense: URL Scanners And Domain Reputation For July 2026
Mobile phishing keeps gaining operational relevance. Security teams need URL scanning, domain reputation checks, DNS pivots, and employee reporting workflows built for SMS and chat.
Outsider Enterprise Takedown: AI Phishing Infrastructure Is Now A Domain Reputation Problem
The FBI, Google, and Black Lotus Labs disruption of Outsider Enterprise shows why AI phishing defense needs URL scanning, domain reputation checks, blocklists, and fast API enrichment.

AI-Enabled Device Code Phishing: How OAuth Tokens Became the New Credential Theft Target
Device code phishing turns a legitimate OAuth flow into a token theft path. Learn how AI-assisted lures, Entra ID abuse, and session token replay change phishing detection in 2026.
OAuth Consent Phishing: Detecting Malicious App Grants Before Data Exfiltration
OAuth consent phishing tricks users into granting access instead of giving up passwords. Learn how malicious app grants work, which permissions matter, and how to detect abuse early.
Compromised Domains in Phishing: When Trusted Sites Become Attack Infrastructure
Attackers increasingly host phishing pages, redirects, and malware on compromised legitimate domains. Learn why reputation bypass works and how to detect hidden malicious paths.
Brand Impersonation and Lookalike Domains: A Practical Monitoring Playbook for Security, Legal, and Fraud Teams
Typosquats and homoglyphs are cheap to register and expensive to ignore. Learn how to discover, prioritize, and remove lookalike infrastructure before it harvests credentials or poisons your customers’ trust in search and email.
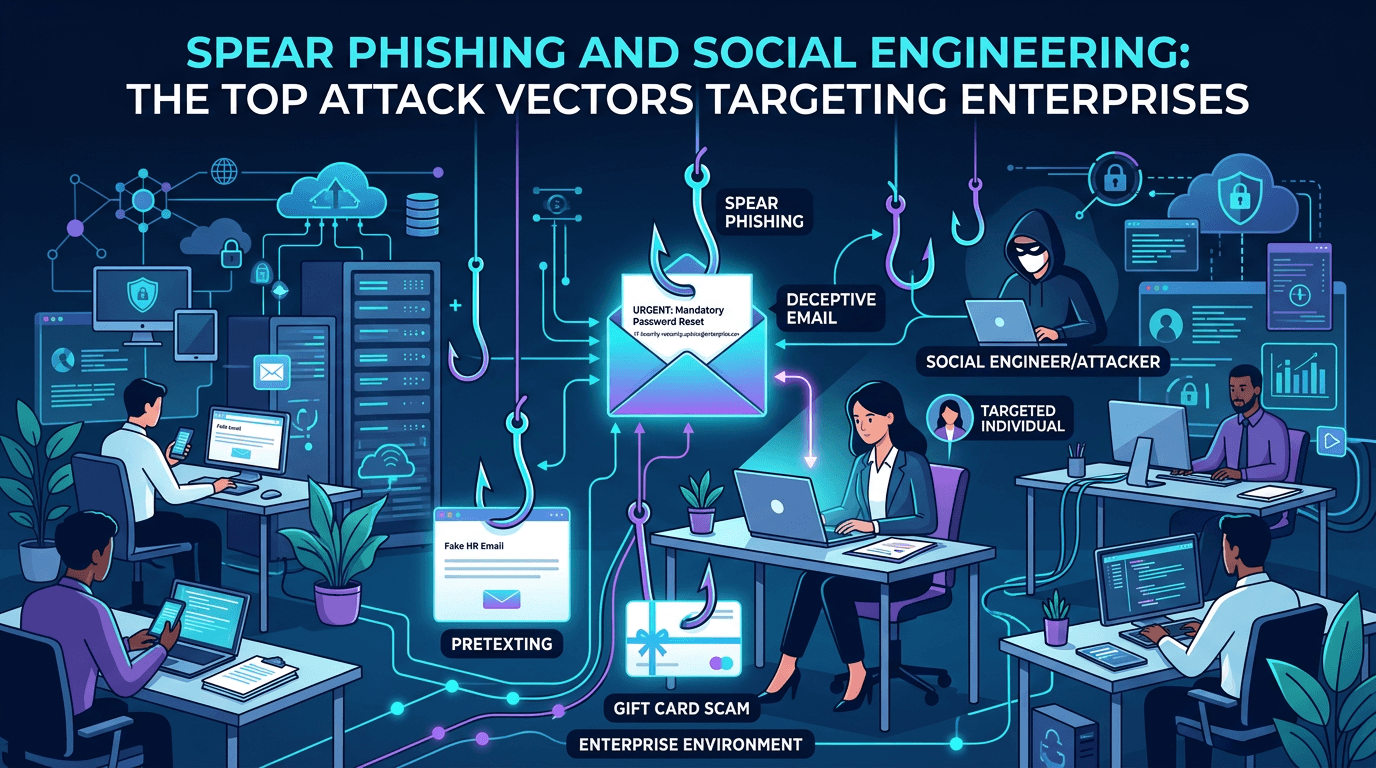
Spear Phishing and Social Engineering: The Top Attack Vectors Targeting Enterprises in 2026
A complete guide to modern spear phishing and social engineering attack vectors—how threat actors plan, lure, and pivot, with detailed defensive controls for email, identity, training, and infrastructure reputation.
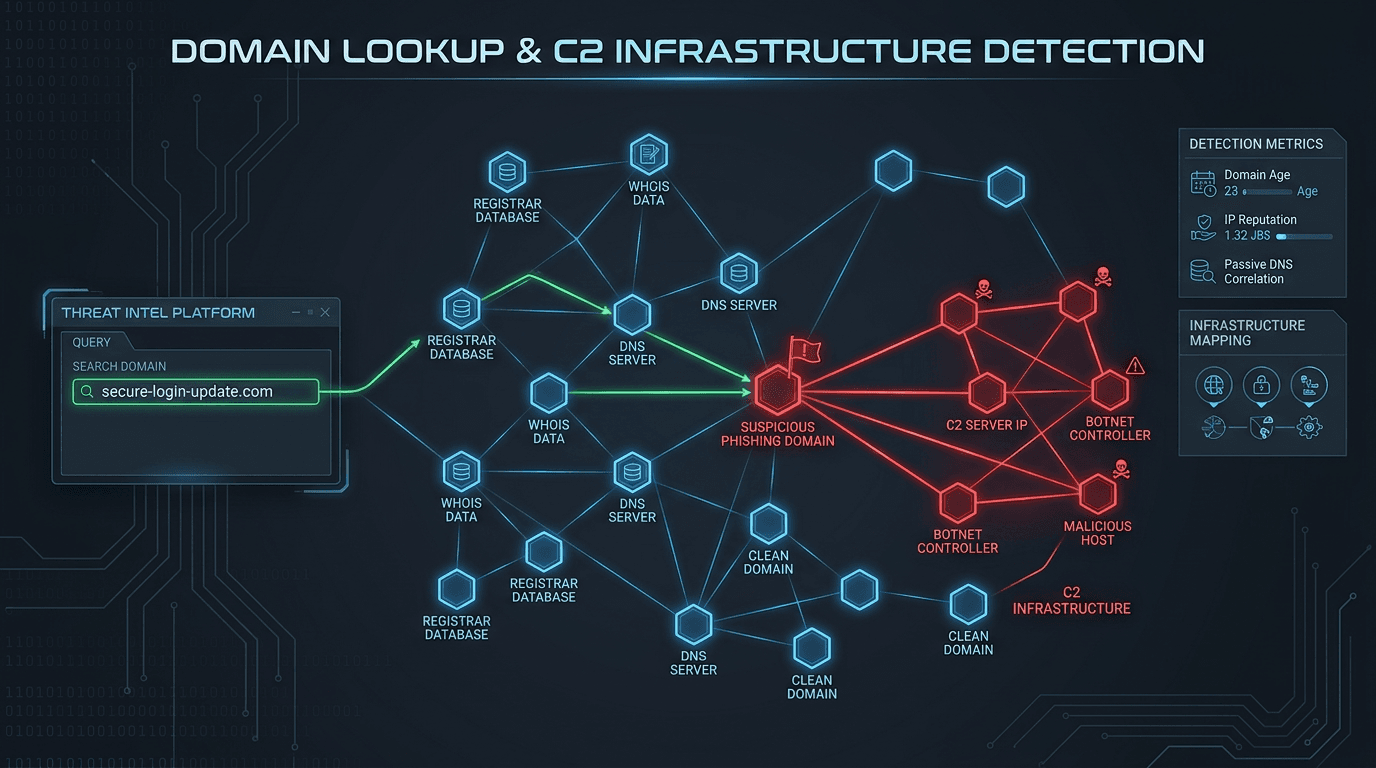
Domain Lookup for Phishing and C2 Infrastructure Detection
Phishing campaigns and malware operations depend on domain infrastructure that leaves detectable traces. Learn how advanced domain lookup techniques help security teams uncover phishing sites and command-and-control servers before they compromise your organization.
Domain Lookup: How to Identify Malicious Websites Before They Strike
Malicious websites are the launchpad for phishing, malware distribution, and credential theft. Learn how domain lookup tools use reputation data, WHOIS analysis, and threat feeds to identify dangerous domains before your users click.
Malvertising and Search Poisoning: Threats Hiding in Plain Sight
Malicious ads and manipulated search results push users toward malware and phishing without email. Learn how malvertising and SEO poisoning work and how teams can reduce risk.
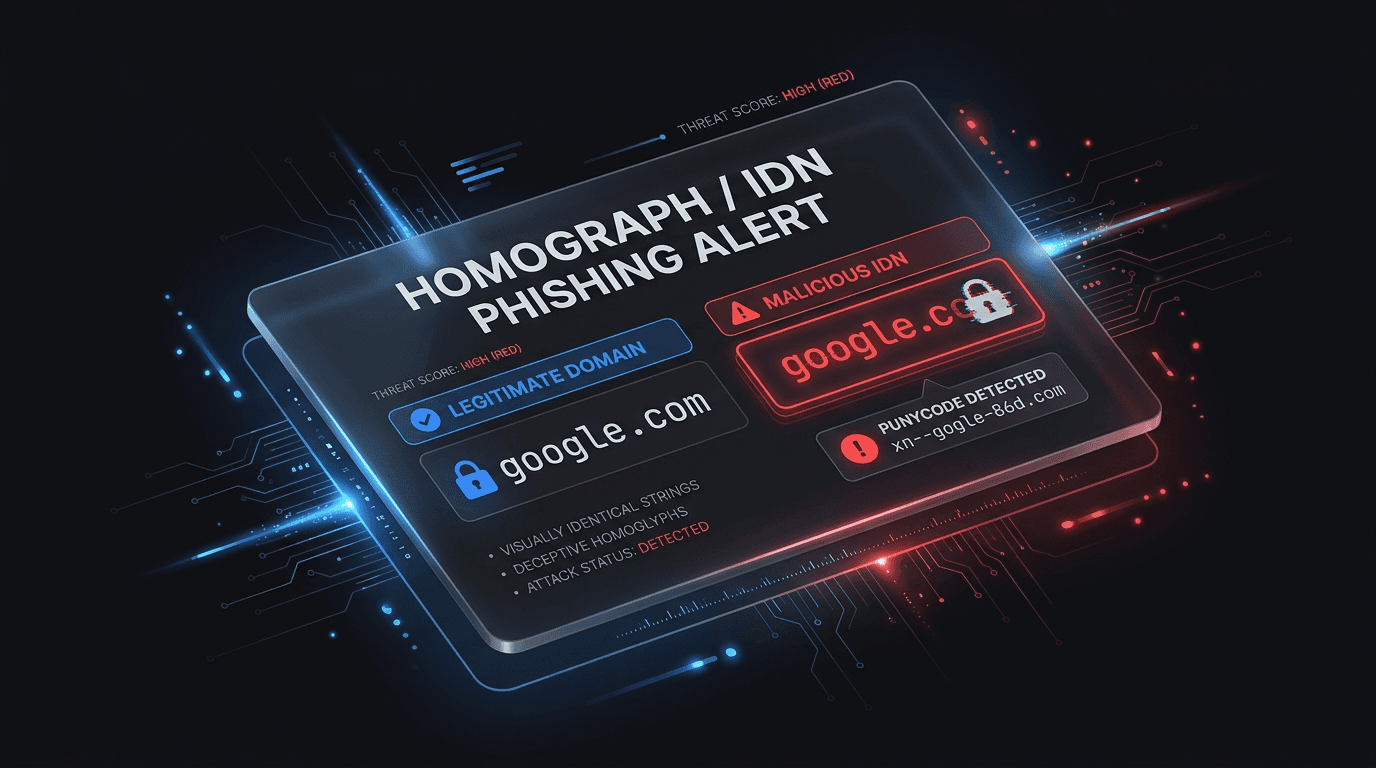
IDN and Homograph Phishing: When the Domain Looks Right But Is Wrong
Internationalized domain names and look-alike characters let attackers spoof trusted brands in the address bar. Learn how homograph attacks work and how to defend users and SOC teams.
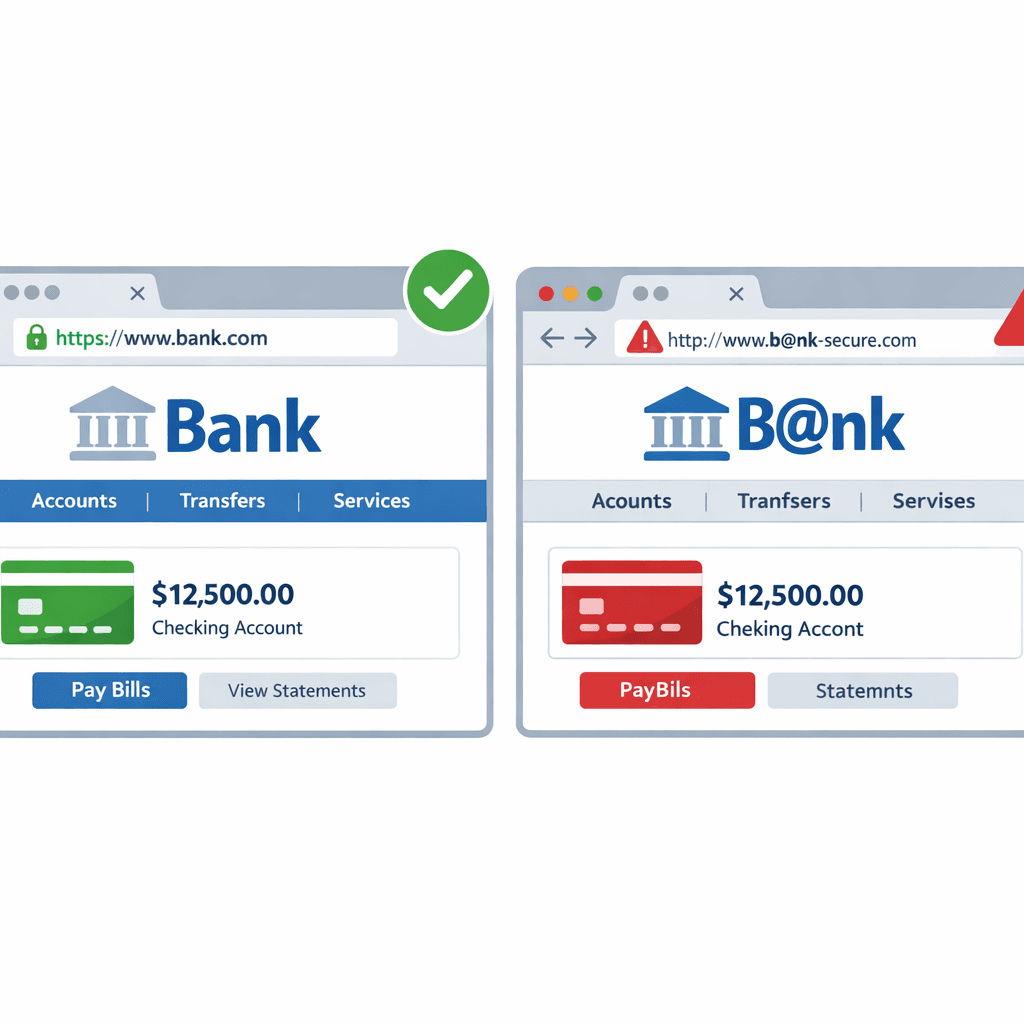
How Hackers Use "Typosquatting" to Trick You (and How to Spot It)
Typosquatting relies on your fingers slipping. Learn how attackers register look-alike domains to steal your data and how to check URLs before you click.
Domain Reputation Scoring: The First Line of Defense Against Phishing
Not all domains are created equal. Discover how real-time domain reputation scoring helps organizations proactively identify and block phishing infrastructure, fake websites, and parked domains used by cybercriminals.
Phishing Explained: How to Check a Domain for Threats
What is phishing? Learn how to spot fake websites and check domains for threats before you enter your personal information.
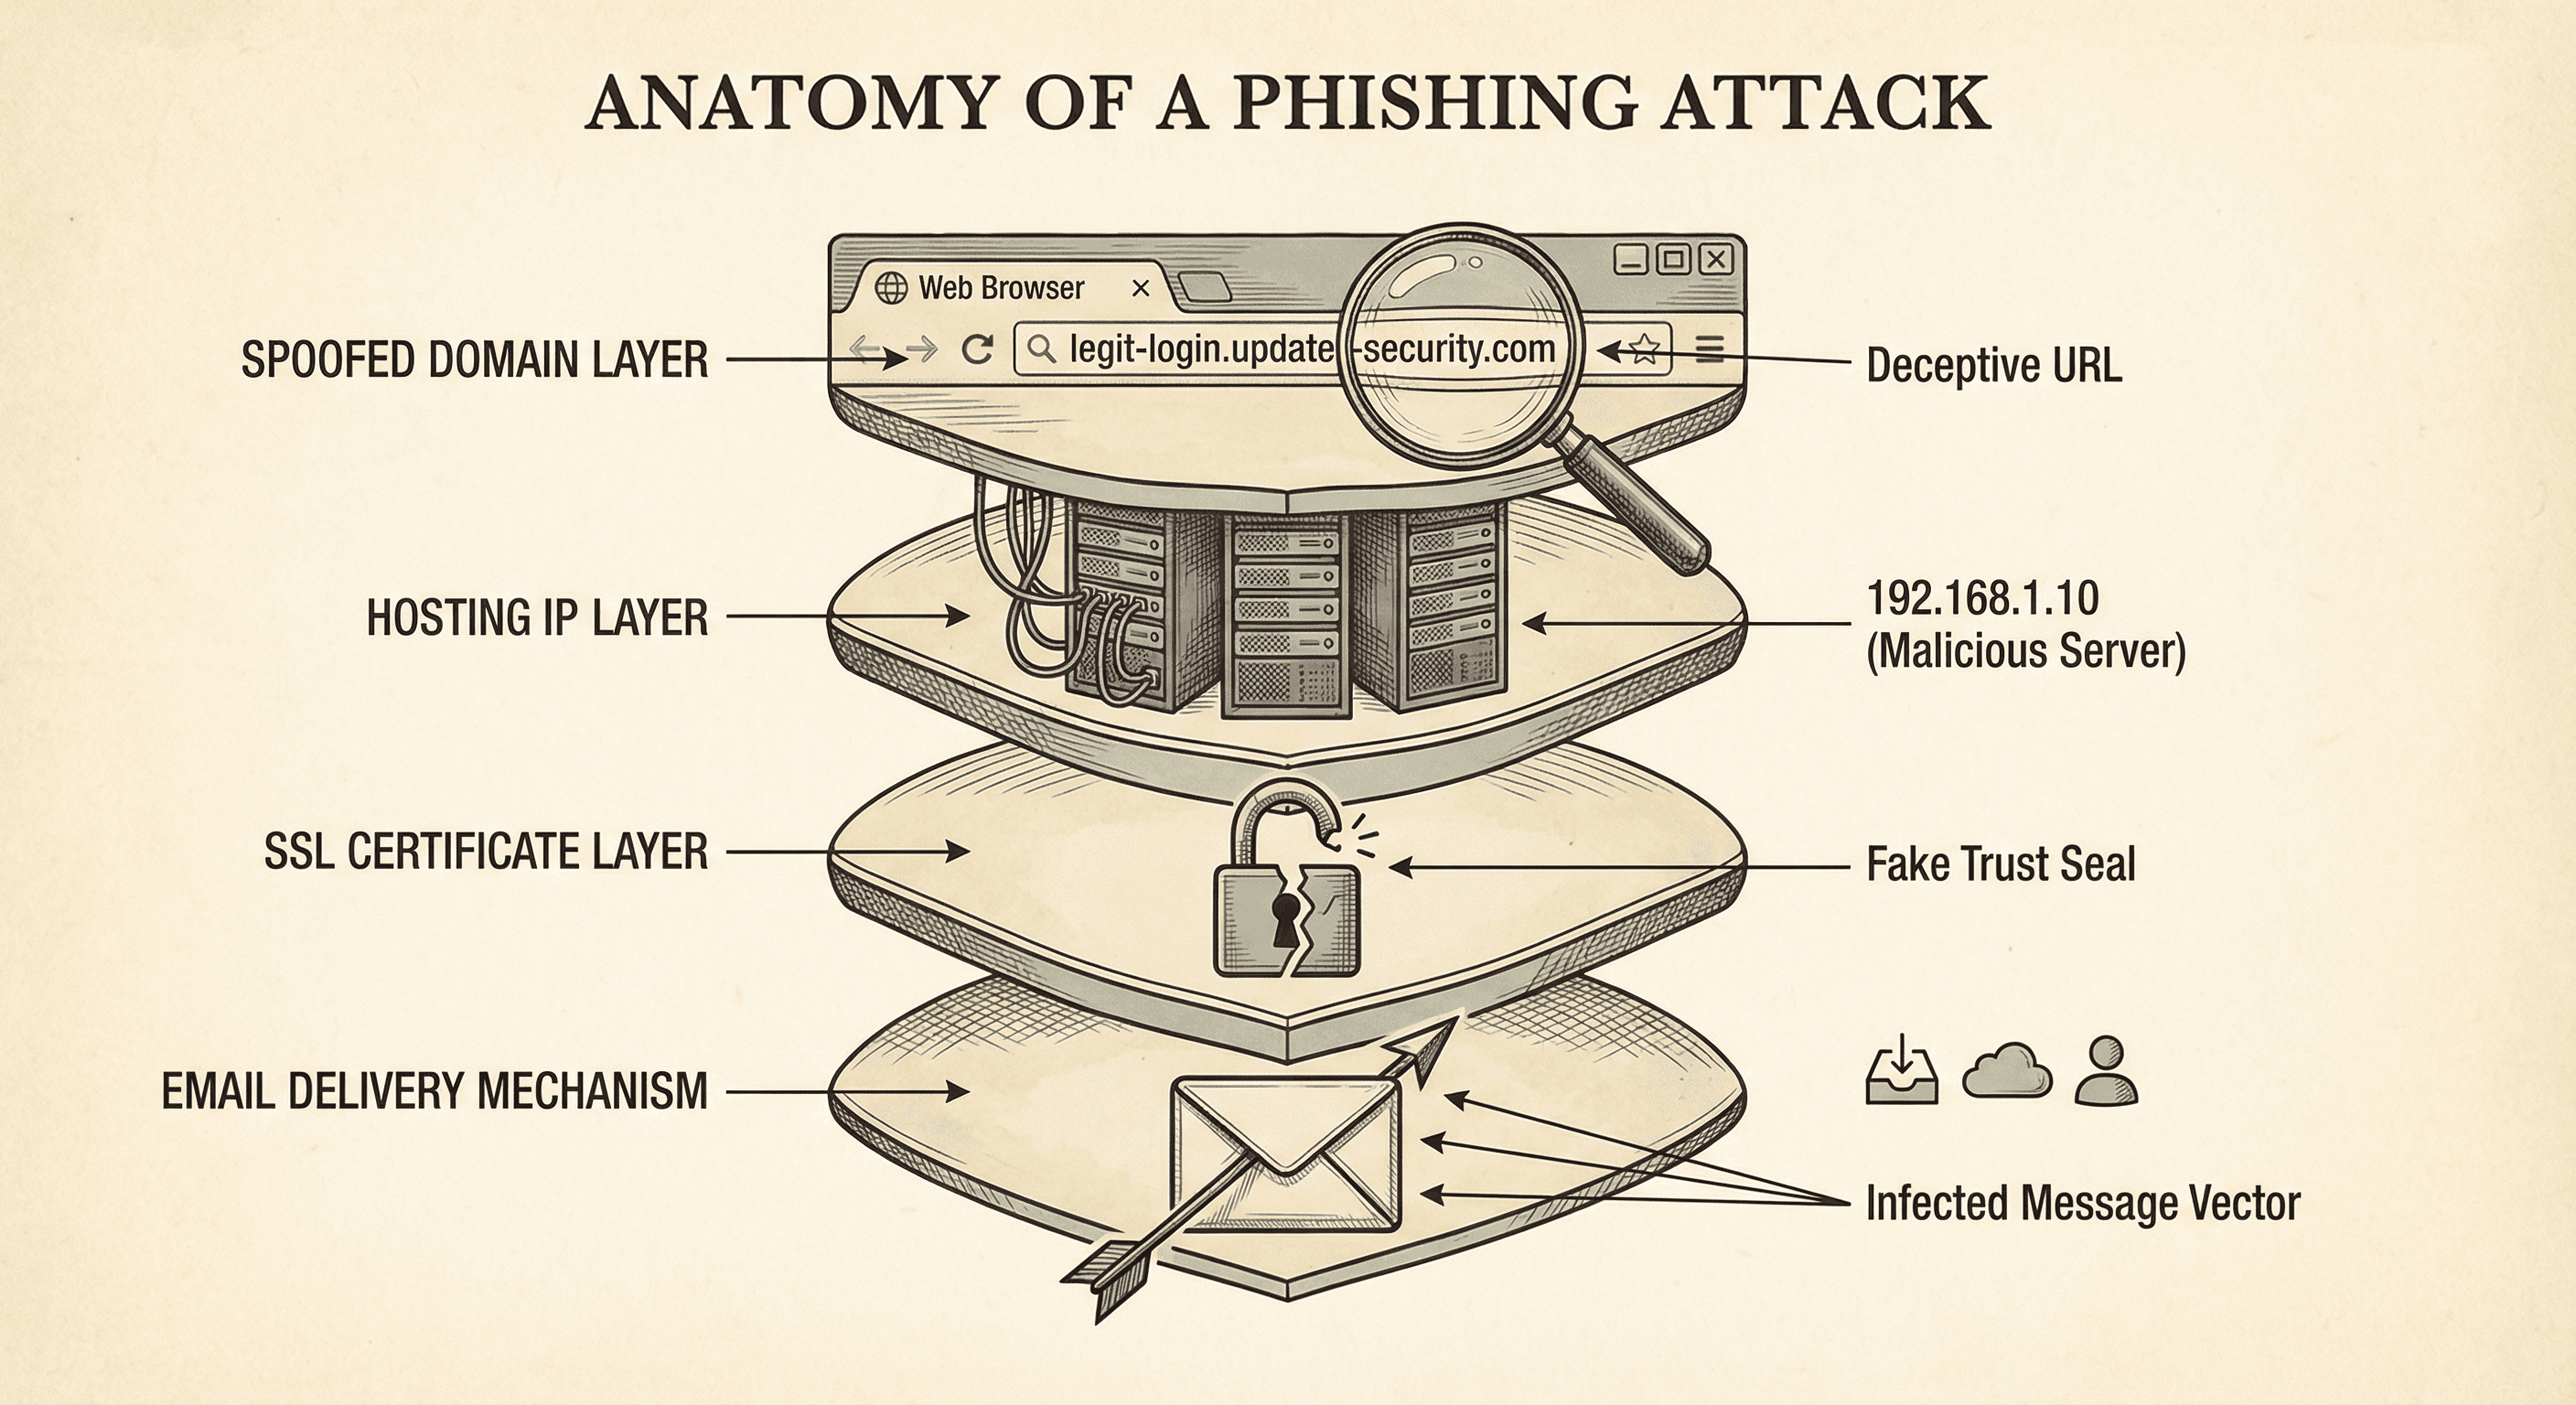
Anatomy of Phishing Infrastructure: How Attackers Build Their Trap
Peel back the layers of a modern phishing attack. From spoofed domains to SSL certificates, understand the infrastructure attackers use and how to detect it.
Beyond Phishing: Modern Social Engineering Tactics
Social engineering has evolved beyond simple phishing emails. Discover the latest tactics used by attackers, including vishing, smishing, and pigmenting, and how to spot them.
Expert Threat Intelligence Analysis
Our blog features in-depth analysis from our threat research team. Each article is backed by real data from our analysis of millions of malicious domains, IPs, and URLs across the global threat landscape. Topics include ransomware campaigns, phishing techniques, malware distribution networks, and emerging threat trends. We publish specific intelligence that security teams can immediately use to improve their defenses.
Practical Security Guidance
Beyond threat analysis, we share practical guidance for security practitioners. Our tutorials cover API integration, SIEM configuration, threat hunting techniques, and building effective threat intelligence programs. Whether you're a SOC analyst, security engineer, or CISO, you'll find content tailored to your role and experience level.
Stay Ahead of Emerging Threats
The threat landscape evolves constantly. Our blog keeps you informed about the latest attack techniques, newly discovered vulnerabilities, and emerging threat actors. Subscribe to our newsletter for weekly digests of the most important developments in cybersecurity.
Subscribe to Our Newsletter
Weekly threat intelligence insights delivered to your inbox.