Research & guides
Threat Intelligence Blog
Threat research, attack analysis and integration guides from the isMalicious team.
- Articles
- 263
- Categories
- 24
- Latest

DNS TTL: Investigate a Change of IP Address
Reconstruct DNS address changes using dated responses, caches and network views, without confusing TTL with the lifetime of a threat.
NXDOMAIN: Diagnose a DNS Security Anomaly
Separate nonexistent names, negative caching, filtering and suspicious activity before treating NXDOMAIN errors as a security incident.
CNAME Cloaking: Investigate a Third-Party Subdomain
Trace CNAME records, identify the provider, and inspect transmitted cookies before deciding whether a subdomain should remain authorized.

Protective DNS for the Public Sector: A Deployment Guide
Deploy protective DNS across public-sector sites and remote staff. Test coverage, handle exceptions and keep essential services available during failures.
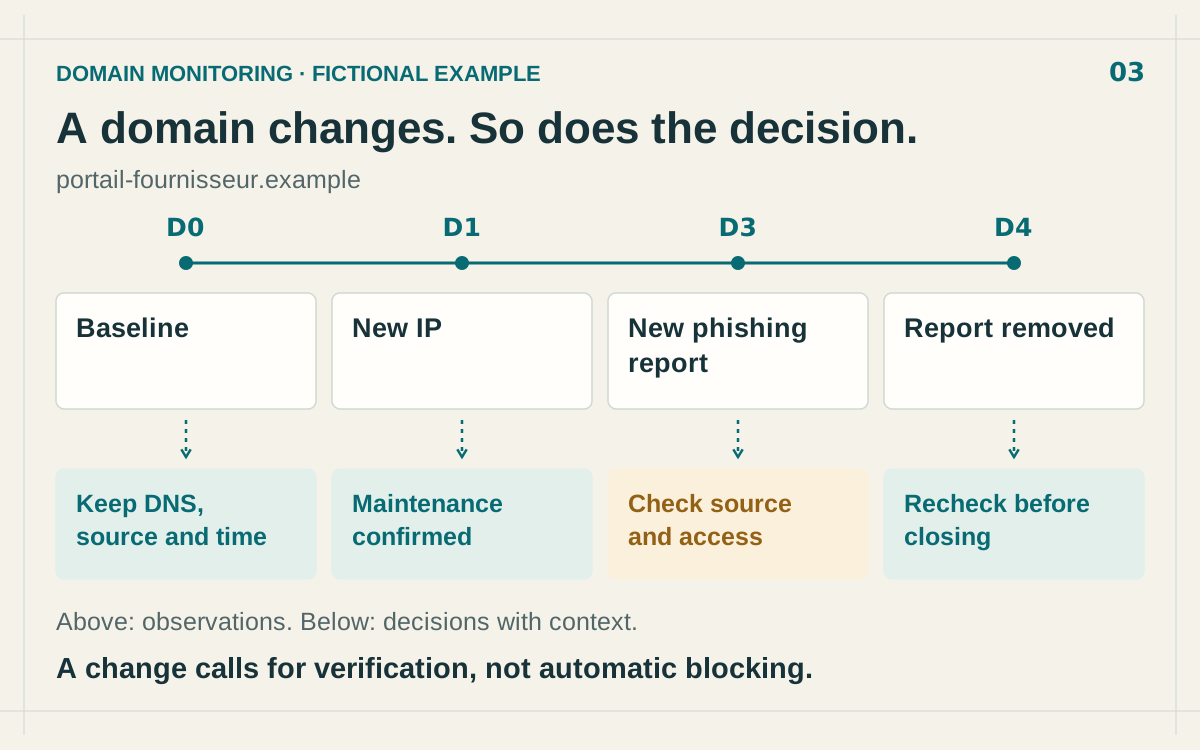
Domain Reputation Monitoring: Which Changes Need Action?
Track domain reputation over time: distinguish a new phishing report from expected DNS changes, then decide what to verify before restricting access.
Subdomain Takeover: Find Dangling DNS First
Prevent subdomain takeover by finding dangling DNS records, linking names to cloud owners, monitoring certificates, and fixing decommissioning order.
Domain Shadowing: Detect Compromised DNS at Scale
Detect domain shadowing by monitoring DNS changes, certificate issuance, subdomain behavior, account security, and infrastructure relationships.
DNS over HTTPS Security: Detect DoH Abuse
Secure DNS over HTTPS without losing visibility: govern resolvers, detect bypass attempts, correlate endpoint telemetry, and preserve user privacy.
DGA Detection: Find Algorithmically Generated Domains
Detect domain generation algorithms with lexical, DNS, endpoint, and reputation signals while controlling false positives in production.
Fast-Flux DNS: Detect Rotating Attack Infrastructure
Learn how to detect fast-flux DNS using TTL, passive DNS, ASN diversity, reputation signals, and a repeatable SOC investigation workflow.
Subdomain Enumeration for Security Teams: Attack Surface Discovery and DNS Reconnaissance
Subdomain enumeration surfaces forgotten dev servers, dangling DNS, and shadow IT before attackers do. Passive and active recon techniques compared.
DNS Security: Poisoning, Hijacking, and Hardening That Actually Sticks
DNS is easy to ignore until it routes your users to malware. Learn how cache poisoning, hijacking, and secure DNS practices fit together.
DNS Blocklists: Stop Malware at the Resolver
Protective DNS blocks malware before the connection opens. Setup guides for Pi-hole, AdGuard, and enterprise resolvers with live blocklists.
Topics
Browse by topic. One hub per subject.
- threat intelligence90 articles
- SOC56 articles
- incident response47 articles
- IOC enrichment31 articles
- threat intelligence API26 articles
- CVE21 articles
- phishing20 articles
- SIEM16 articles
- vulnerability management14 articles
- KEV12 articles
- patch management11 articles
- identity security10 articles
- CVE Watch9 articles
- EPSS9 articles
- malware detection8 articles
- ransomware8 articles
- file hash7 articles
- SOAR7 articles
- ransomware intelligence6 articles
- MITRE ATT&CK5 articles
Expert Threat Intelligence Analysis
Our blog features in-depth analysis from our threat research team. Each article is backed by real data from our analysis of millions of malicious domains, IPs, and URLs across the global threat landscape. Topics include ransomware campaigns, phishing techniques, malware distribution networks, and emerging threat trends. We publish specific intelligence that security teams can immediately use to improve their defenses.
Practical Security Guidance
Beyond threat analysis, we share practical guidance for security practitioners. Our tutorials cover API integration, SIEM configuration, threat hunting techniques, and building effective threat intelligence programs. Whether you're a SOC analyst, security engineer, or CISO, you'll find content tailored to your role and experience level.
Stay Ahead of Emerging Threats
The threat landscape evolves constantly. Our blog keeps you informed about the latest attack techniques, newly discovered vulnerabilities, and emerging threat actors. Subscribe to our newsletter for weekly digests of the most important developments in cybersecurity.
Get new research by email
New articles and product news, straight to your inbox.