Threat Intelligence Blog
Research, insights, and updates from the isMalicious team.

JA4 TLS Fingerprinting for Threat Hunting
Use JA4 TLS fingerprints for threat hunting, malware clustering, allowlisting, and anomaly detection without treating a fingerprint as identity.
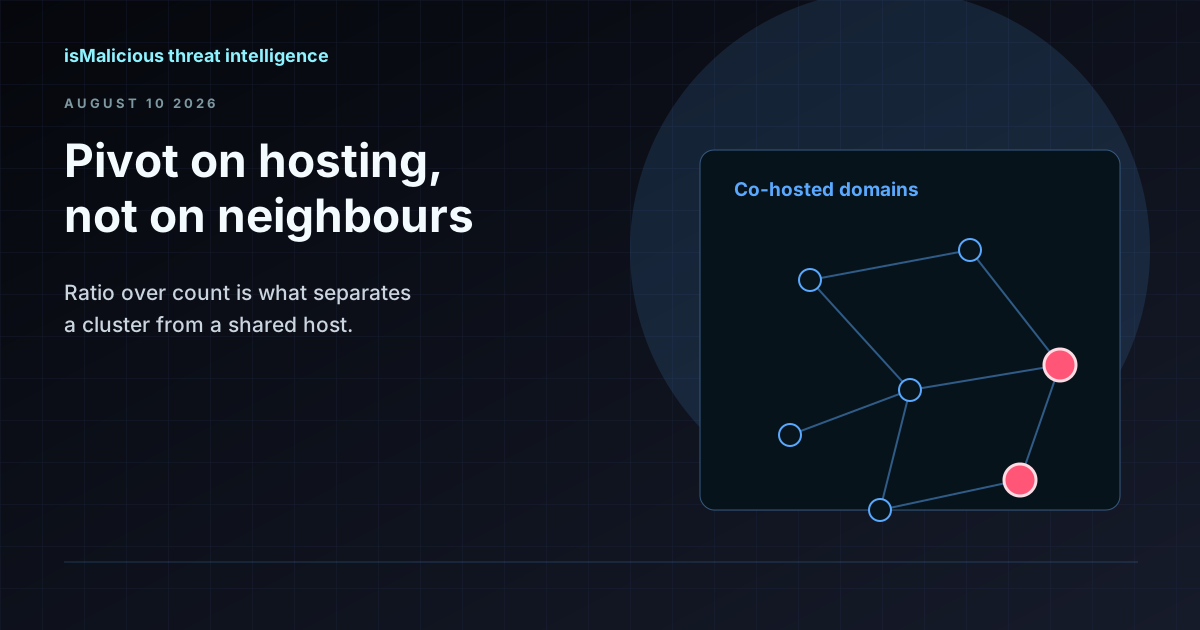
Reverse IP Lookup: Pivoting on Infrastructure Without Drowning in Shared Hosting
A reverse IP lookup turns one indicator into a cluster — or into a thousand innocent neighbours. Here is how to tell the difference, and how to pivot on hosting infrastructure without generating false positives.
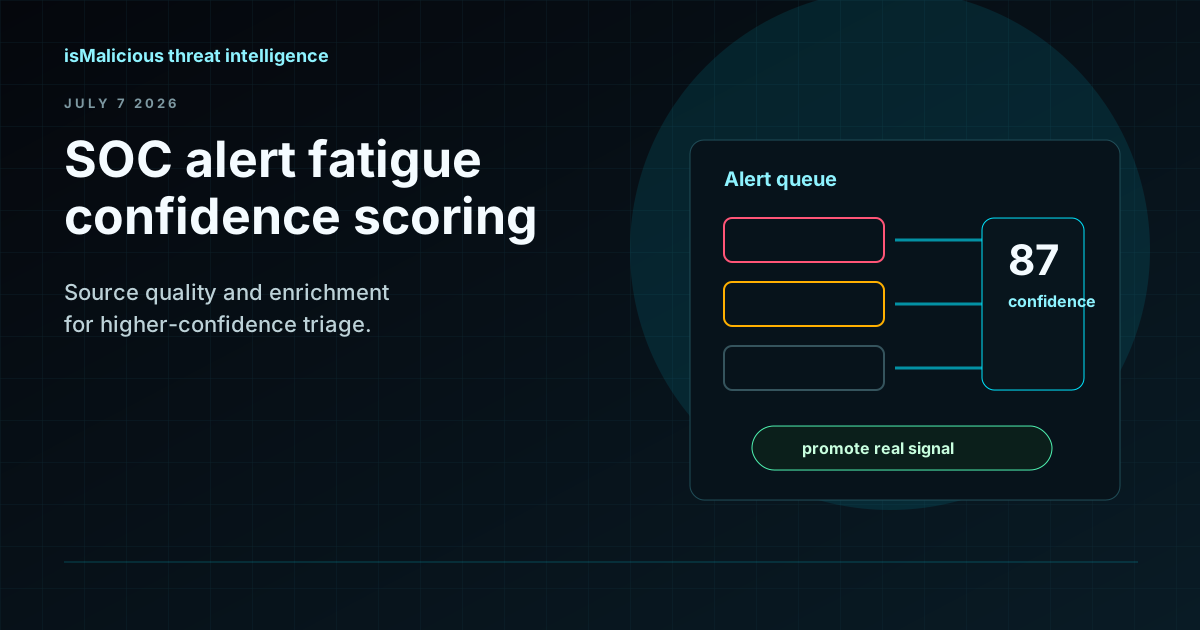
SOC Alert Fatigue In July 2026: Confidence Scoring Beats More Noise
Vectra AI research shows alert overload remains a resilience problem. SOC teams need source quality, confidence scoring, enrichment, and SIEM workflows that suppress noise without hiding risk.
SOC Alert Fatigue: How Threat Intelligence Reduces False Positives Without Hiding Real Attacks
Alert fatigue is not a staffing problem alone. SOC teams need better evidence, source quality, confidence bands, and enrichment workflows that turn noisy alerts into defensible decisions.
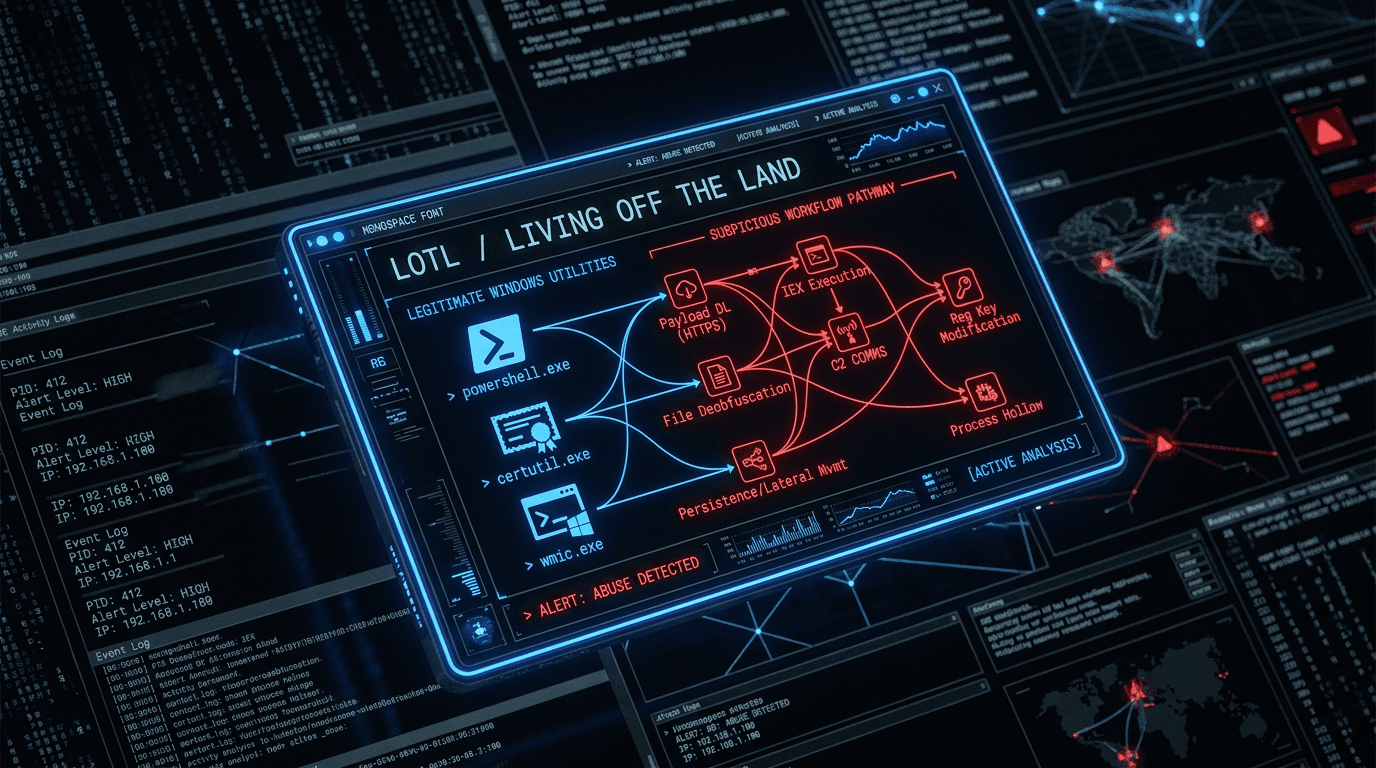
Living Off the Land (LOTL): Why “No Malware File” Still Means Breach
Attackers increasingly abuse built-in OS binaries and scripts to avoid dropping traditional malware. Understand LOTL tradecraft and what to log, detect, and hunt for.
What Is a C2 Server? Detection Explained
Command-and-control servers run botnets and ransomware. How C2 traffic works, what it looks like on your network, and how to detect it.
Building a Custom SOC Dashboard: Integrating Real-Time Threat Feeds
Enhance your Security Operations Center visibility. A step-by-step guide to aggregating threat data, enriching logs, and building custom security dashboards using modern Threat Intelligence APIs.
Threat Hunting: Proactive Security Detection Beyond Automated Alerts
Waiting for alerts means waiting for attacks to succeed. Learn how proactive threat hunting helps security teams discover hidden threats, improve defenses, and stay ahead of sophisticated adversaries.
Lateral Movement Detection: Stopping Attackers from Spreading Through Your Network
After initial compromise, attackers move laterally to reach valuable targets. Learn how to detect lateral movement techniques, implement segmentation, and stop attackers before they reach critical assets.
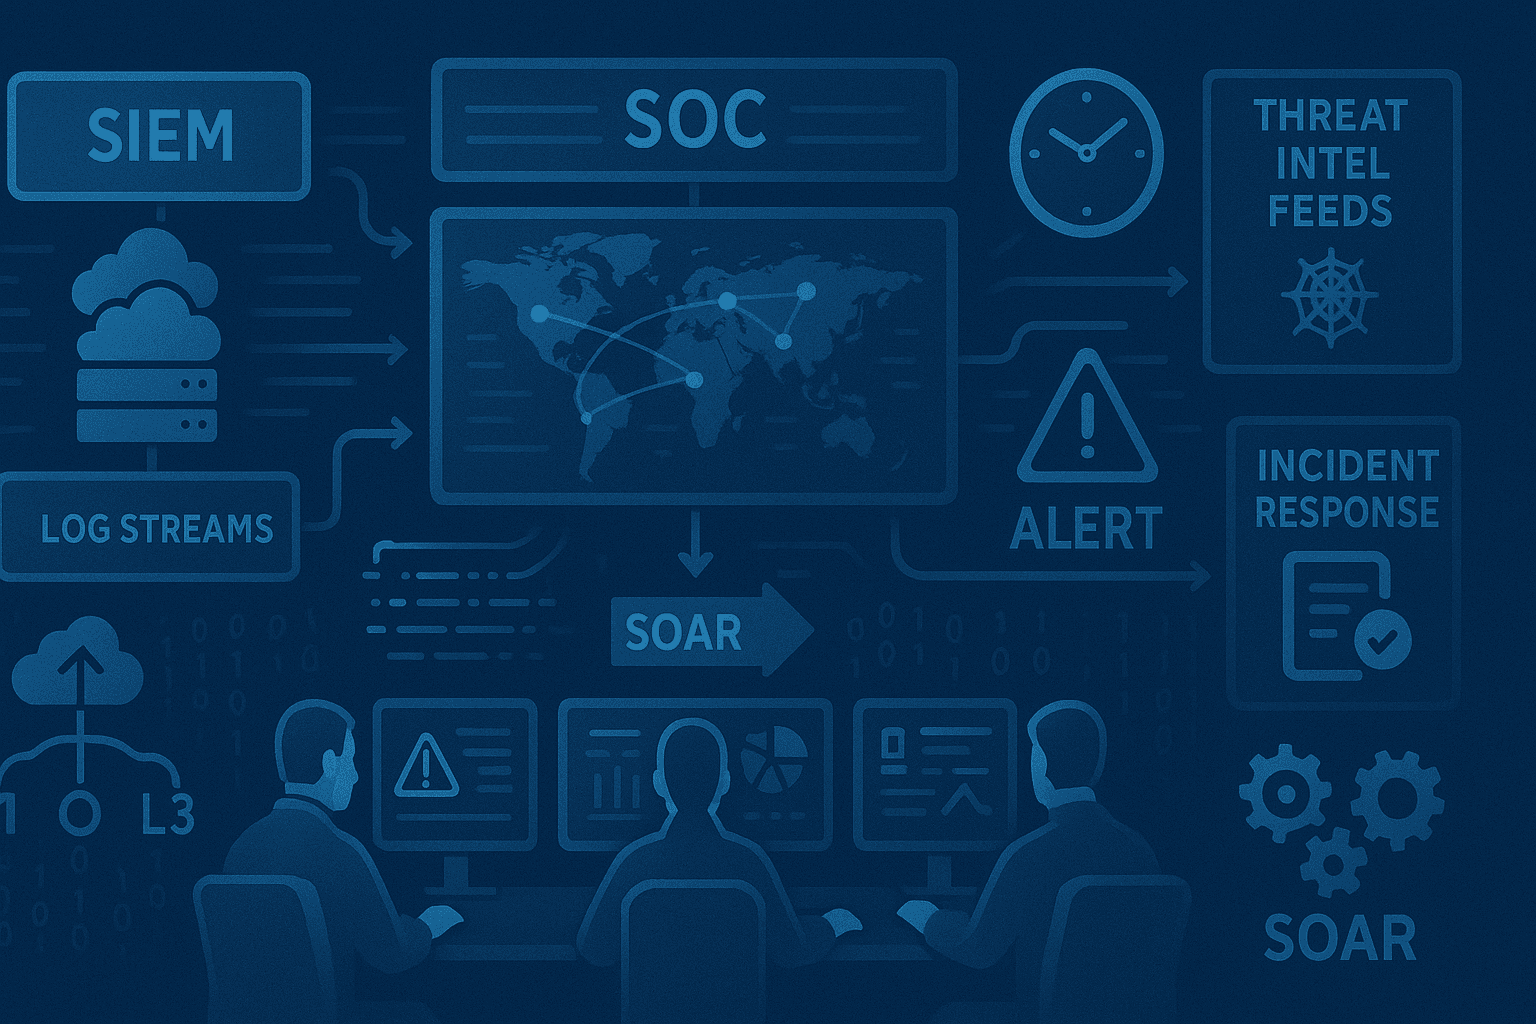
Building a Modern SOC with Threat Intelligence: A Practical Guide
Learn how to build an effective Security Operations Center (SOC) powered by threat intelligence. Discover essential tools, processes, and best practices for detecting, analyzing, and responding to cyber threats in real-time.
Expert Threat Intelligence Analysis
Our blog features in-depth analysis from our threat research team. Each article is backed by real data from our analysis of millions of malicious domains, IPs, and URLs across the global threat landscape. Topics include ransomware campaigns, phishing techniques, malware distribution networks, and emerging threat trends. We publish specific intelligence that security teams can immediately use to improve their defenses.
Practical Security Guidance
Beyond threat analysis, we share practical guidance for security practitioners. Our tutorials cover API integration, SIEM configuration, threat hunting techniques, and building effective threat intelligence programs. Whether you're a SOC analyst, security engineer, or CISO, you'll find content tailored to your role and experience level.
Stay Ahead of Emerging Threats
The threat landscape evolves constantly. Our blog keeps you informed about the latest attack techniques, newly discovered vulnerabilities, and emerging threat actors. Subscribe to our newsletter for weekly digests of the most important developments in cybersecurity.
Subscribe to Our Newsletter
Weekly threat intelligence insights delivered to your inbox.