Threat Intelligence Blog
Research, insights, and updates from the isMalicious team.

Agentic AI Threat Mapping: MITRE ATT&CK Needs Evidence-Rich Workflows
Anthropic mapped AI-enabled cyber activity to MITRE ATT&CK and found gaps around autonomous orchestration. SOC teams need AI summaries tied to evidence, not unsupported verdicts.
Shadow AI Governance: How Security Teams Can Detect Risk Without Blocking Innovation
Shadow AI is the new shadow IT: fast adoption, weak visibility, and serious data leakage risk. Security teams need discovery, domain intelligence, policy, training, and monitoring.
AI-Enabled Cyberattacks and MITRE ATT&CK: Turning New Threat Maps Into SOC Action
AI-enabled threats are being mapped into ATT&CK language, but mapping is only useful when it drives enrichment, detection, triage, and response workflows.
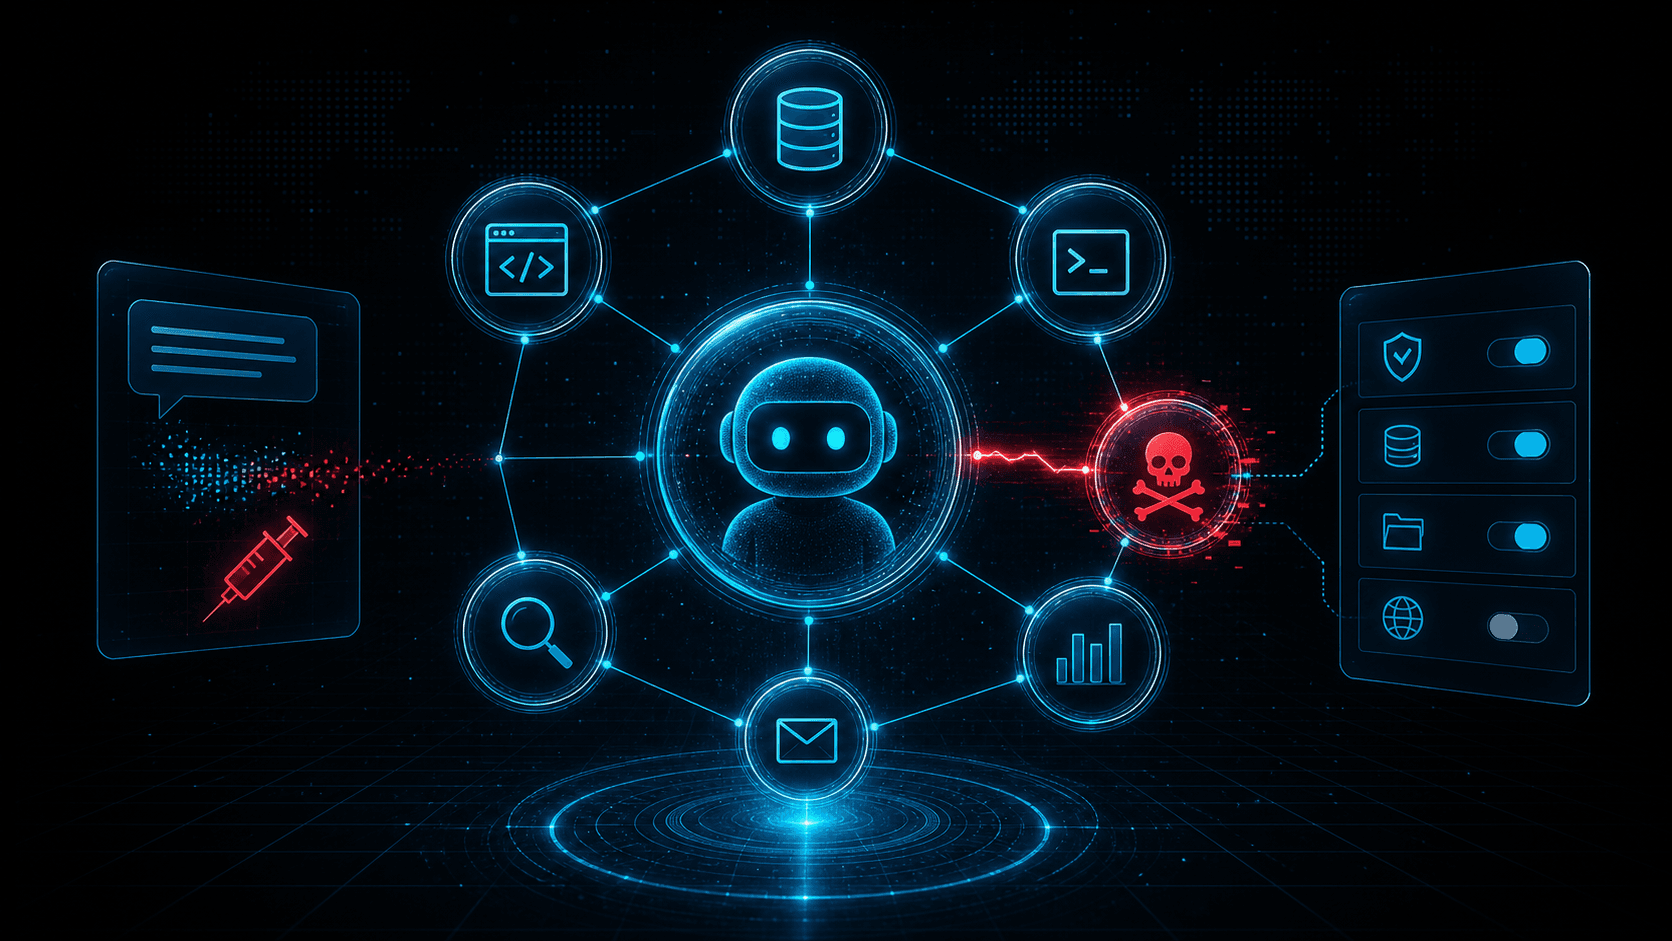
MCP Security Risks: Tool Poisoning, Prompt Injection, and the New AI Agent Attack Surface
Model Context Protocol integrations give agents access to tools, files, and services. That power creates new risks: tool poisoning, prompt injection, overbroad permissions, and untrusted server abuse.
Security LLM and Agent Workflows: When (and How) to Check Malicious Domains, IPs, and URLs Before Acting
AI assistants in SOAR, IDEs, and browser extensions can exfiltrate data or run malicious code if they fetch the wrong link. This guide gives guardrails: schema for tool calls, policy tiers, and where threat intelligence checks belong in the loop.
Automated Threat Classification using Machine Learning
Machine Learning is transforming how we classify threats. Discover how AI models can analyze vast amounts of data to categorize attacks instantly.
Biometric Spoofing: Defeating Authentication in an AI World
Are fingerprints and facial recognition truly secure? We explore the techniques attackers use to spoof biometric sensors, from 3D-printed faces to synthetic voice cloning.
The Deepfake Threat: Protecting Enterprise Security in the Era of AI
AI-generated video and audio are becoming indistinguishable from reality. Explore the rising threat of deepfakes to enterprise security and how to defend against synthetic media attacks.
AI-enabled Cyberattacks: How Threat Actors Use Machine Learning
Cybercriminals are weaponizing artificial intelligence to launch sophisticated attacks at unprecedented scale. Learn how AI-enabled threats work and how threat intelligence can help you defend against them.
Expert Threat Intelligence Analysis
Our blog features in-depth analysis from our threat research team. Each article is backed by real data from our analysis of millions of malicious domains, IPs, and URLs across the global threat landscape. Topics include ransomware campaigns, phishing techniques, malware distribution networks, and emerging threat trends. We publish specific intelligence that security teams can immediately use to improve their defenses.
Practical Security Guidance
Beyond threat analysis, we share practical guidance for security practitioners. Our tutorials cover API integration, SIEM configuration, threat hunting techniques, and building effective threat intelligence programs. Whether you're a SOC analyst, security engineer, or CISO, you'll find content tailored to your role and experience level.
Stay Ahead of Emerging Threats
The threat landscape evolves constantly. Our blog keeps you informed about the latest attack techniques, newly discovered vulnerabilities, and emerging threat actors. Subscribe to our newsletter for weekly digests of the most important developments in cybersecurity.
Subscribe to Our Newsletter
Weekly threat intelligence insights delivered to your inbox.