Research & guides
Threat Intelligence Blog
Threat research, attack analysis and integration guides from the isMalicious team.
- Articles
- 263
- Categories
- 24
- Latest

GitHub Actions OIDC: Secure Cloud Deployments
Replace long-lived cloud secrets with GitHub Actions OIDC while constraining claims, permissions, environments, reusable workflows, and incident response.
Sigstore and Cosign: Verify Container Images
Sign and verify container images with Cosign, keyless identities, transparency evidence, digest pinning, and admission policies that check the signer.
SLSA Provenance: Verify the Software Supply Chain
Use SLSA provenance to trace artifacts to source and build systems, verify expectations, improve CI controls, and respond to tampering.
Malicious PyPI Packages: Detect Supply-Chain Attacks
Detect malicious PyPI packages through provenance, dependency controls, install behavior, network telemetry, hashes, and a Python incident playbook.
GitHub Actions and CI/CD Pipeline Compromise: A Growing Supply Chain Attack Vector
CI/CD pipeline compromises keep recurring across GitHub Actions ecosystems. Learn the detection signals, hardening steps, and enrichment workflow security teams need.
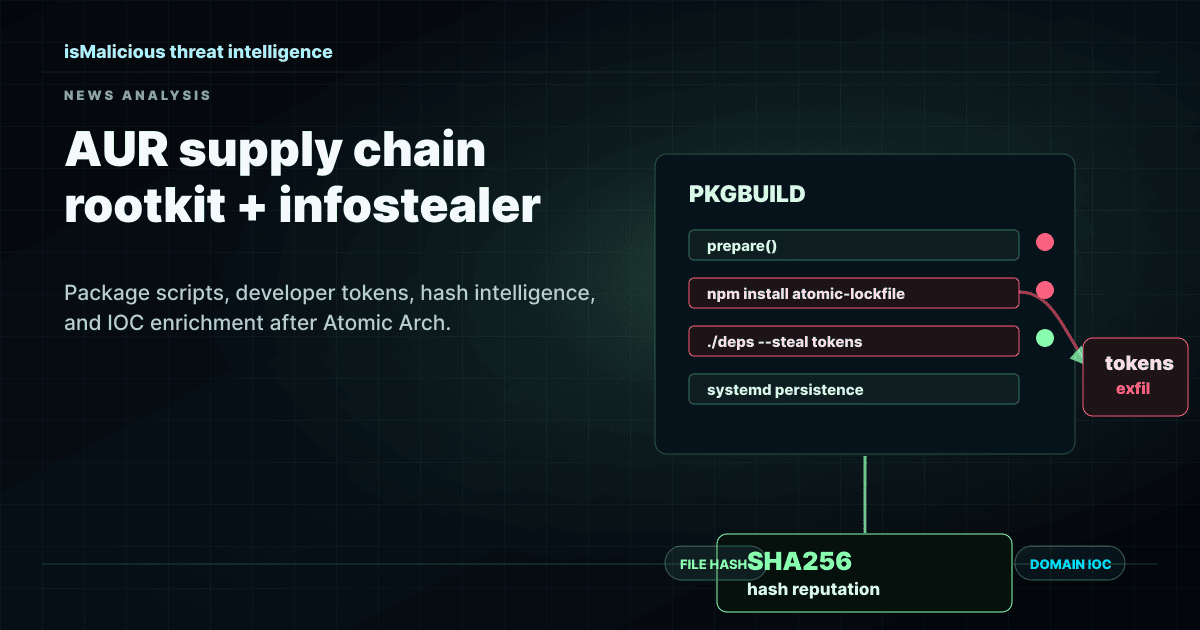
Arch AUR Rootkit And Infostealer Campaign: Supply Chain Defense Starts With Hash Intelligence
The June 2026 Arch User Repository compromise shows why supply chain security needs package review, file hash reputation, developer credential protection, and fast IOC enrichment.
Malicious npm Packages: Detecting Open-Source Supply Chain Compromise
Malicious npm packages use typosquatting, dependency confusion, install scripts, and maintainer compromise to steal secrets and backdoor builds. Learn practical detection and response.
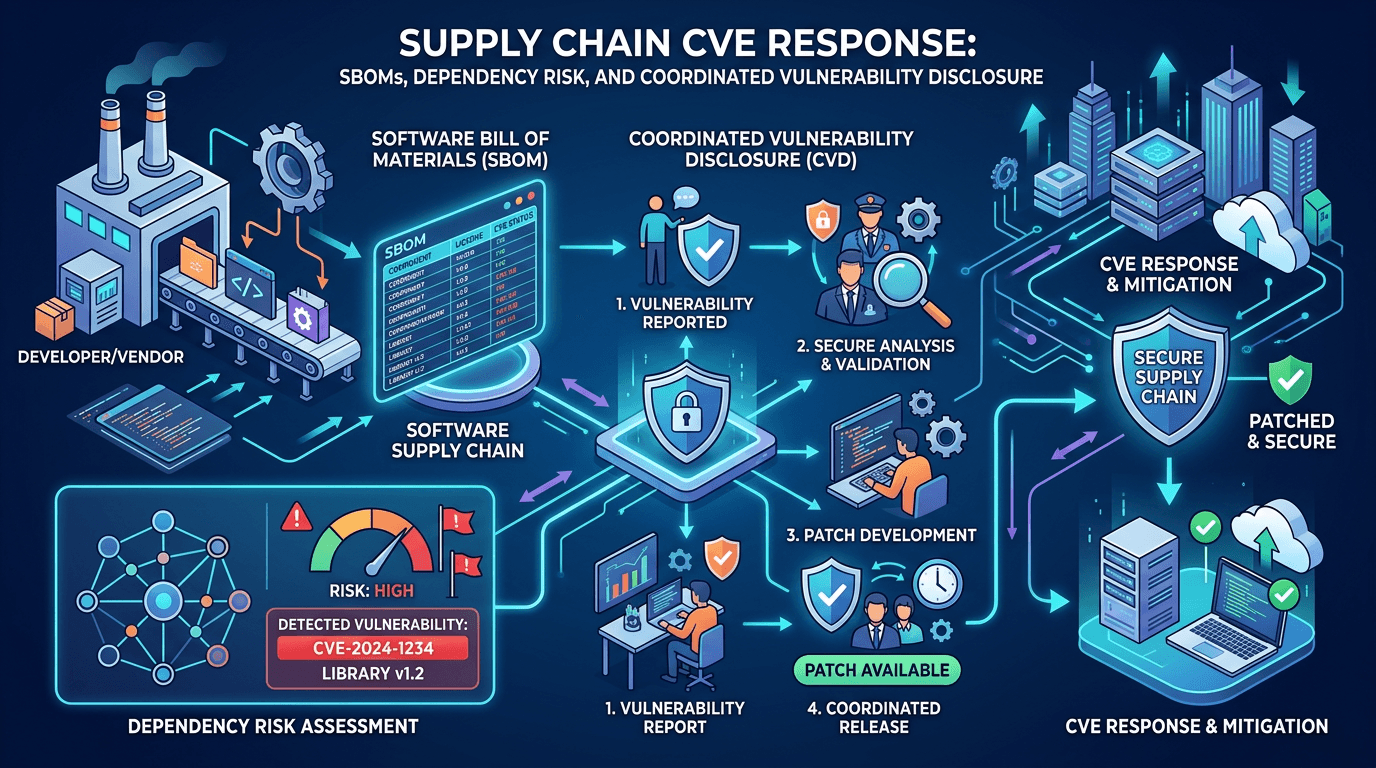
Supply Chain CVE Response: SBOMs, Dependency Risk, and Coordinated Vulnerability Disclosure
Build a modern supply-chain security program: generate SBOMs, map CVEs to components, integrate EPSS and KEV, and coordinate fixes across vendors and open-source maintainers.
SBOM and Supply Chain Security: What Security Teams Actually Need
Software bills of materials are not paperwork for compliance alone. Learn how SBOMs reduce third-party risk and speed response when a dependency blows up.
DevSecOps: Integrating Security into the CI/CD Pipeline
Security should not be an afterthought. Learn how to implement DevSecOps to automate security testing and vulnerability scanning within your development workflow.
Supply Chain Attack Detection: Lessons from SolarWinds to MOVEit
Supply chain attacks have become the weapon of choice for sophisticated threat actors. Learn how to detect compromised vendors, monitor third-party risk, and protect your organization before your suppliers become your vulnerability.
Topics
Browse by topic. One hub per subject.
- threat intelligence90 articles
- SOC56 articles
- incident response47 articles
- IOC enrichment31 articles
- threat intelligence API26 articles
- CVE21 articles
- phishing20 articles
- SIEM16 articles
- vulnerability management14 articles
- KEV12 articles
- patch management11 articles
- identity security10 articles
- CVE Watch9 articles
- EPSS9 articles
- malware detection8 articles
- ransomware8 articles
- file hash7 articles
- SOAR7 articles
- ransomware intelligence6 articles
- MITRE ATT&CK5 articles
Expert Threat Intelligence Analysis
Our blog features in-depth analysis from our threat research team. Each article is backed by real data from our analysis of millions of malicious domains, IPs, and URLs across the global threat landscape. Topics include ransomware campaigns, phishing techniques, malware distribution networks, and emerging threat trends. We publish specific intelligence that security teams can immediately use to improve their defenses.
Practical Security Guidance
Beyond threat analysis, we share practical guidance for security practitioners. Our tutorials cover API integration, SIEM configuration, threat hunting techniques, and building effective threat intelligence programs. Whether you're a SOC analyst, security engineer, or CISO, you'll find content tailored to your role and experience level.
Stay Ahead of Emerging Threats
The threat landscape evolves constantly. Our blog keeps you informed about the latest attack techniques, newly discovered vulnerabilities, and emerging threat actors. Subscribe to our newsletter for weekly digests of the most important developments in cybersecurity.
Get new research by email
New articles and product news, straight to your inbox.