Threat Intelligence Blog
Research, insights, and updates from the isMalicious team.
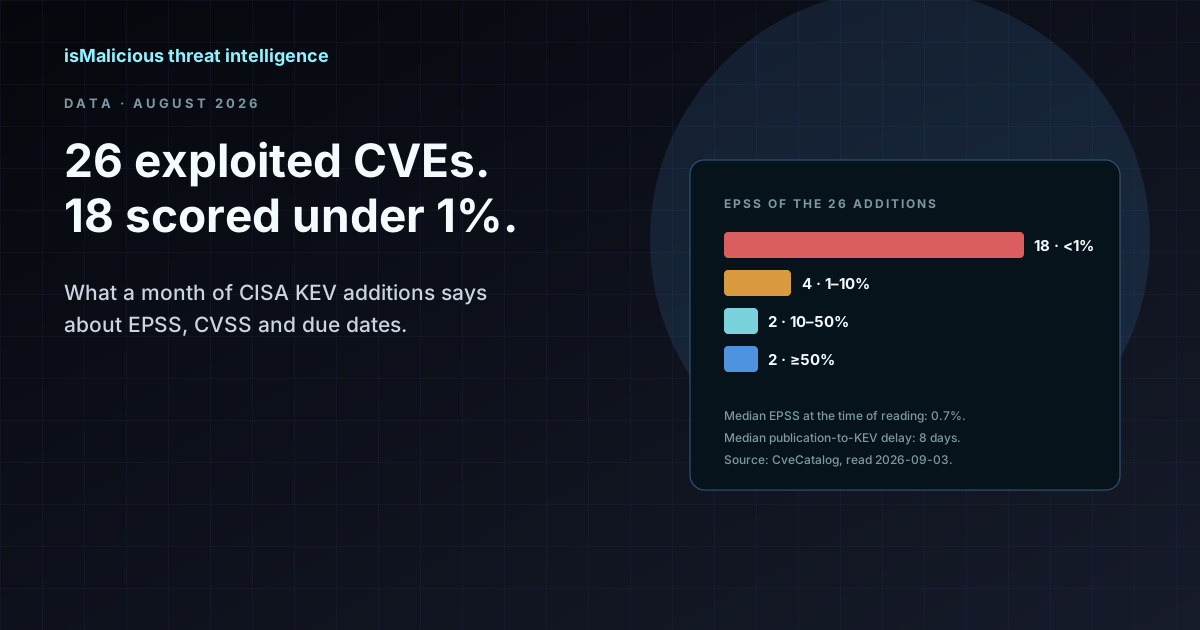

CVE Watch Perimeters: Prioritize Findings by Real Exposure
Map products to CVE Watch perimeters, then combine active exploitation, CISA KEV, EPSS, CVSS, product context, and remediation status to focus vulnerability work.

CVE-2026-63077 Puts Unauthenticated RCE on Every TeamCity On-Premises Server
A deserialization flaw in the agent polling protocol gives attackers TeamCity server privileges without credentials. JetBrains patched in 2025.11.7 and 2026.1.3 — CISA KEV and a 3-day federal deadline mean hunt now, not after the next release train.
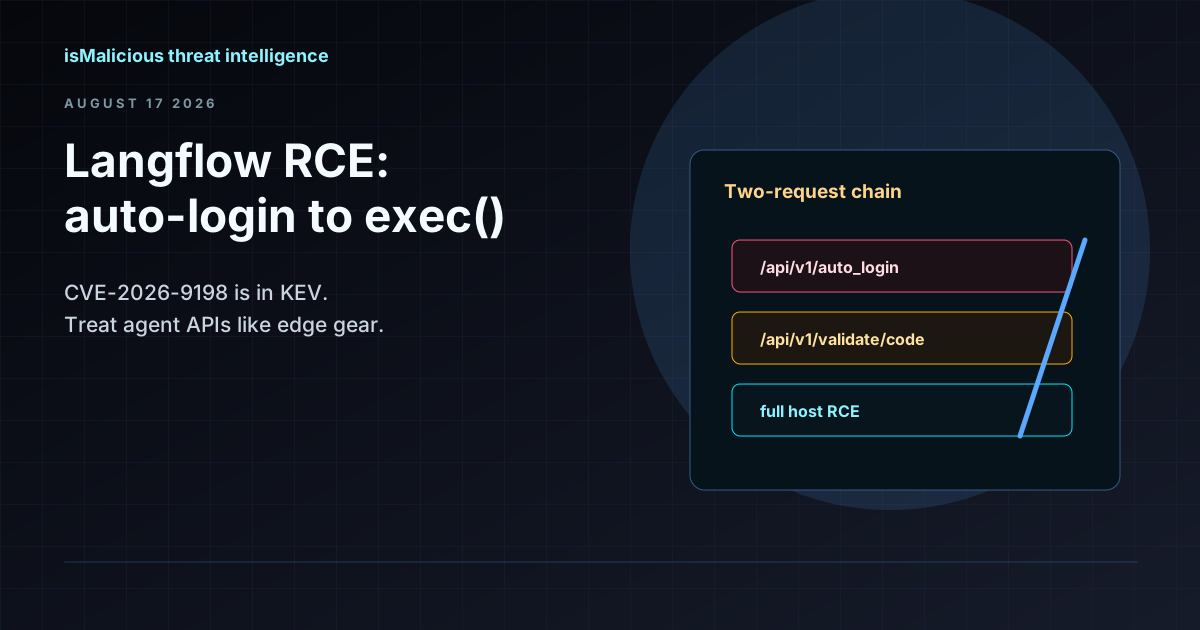
CVE-2026-9198 Gives Unauthenticated RCE in IBM Langflow OSS Agent Control Planes
A SUPERUSER token minted through /api/v1/auto_login chains with Python exec() in /api/v1/validate/code. Langflow 1.10.1 fixes the flaw — but internet-exposed instances need hunting now, not after the next sprint.
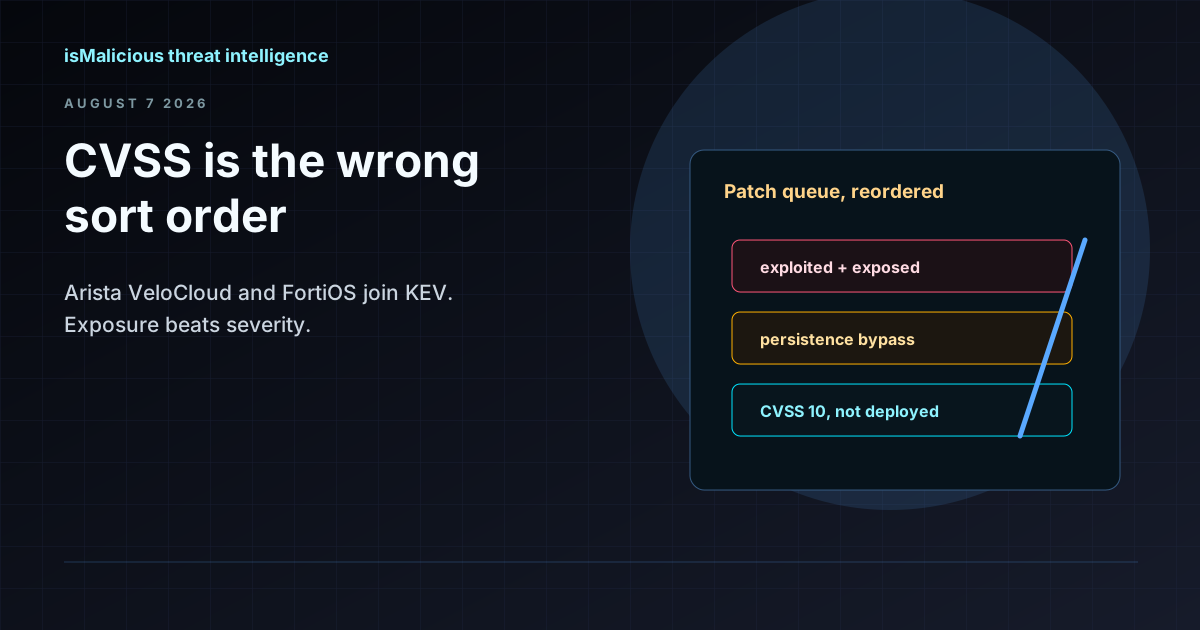
CISA KEV Adds Arista VeloCloud and FortiOS Flaws: Why CVSS Is the Wrong Sort Order
On 27 July 2026 CISA added a CVSS 10.0 command injection in Arista VeloCloud Orchestrator and a medium-severity FortiOS patch bypass to KEV. The pairing shows why exposure and persistence beat severity when ordering a patch queue.
When Vulnerability Exploitation Overtakes Credentials: CVE Prioritization In 2026
Verizon DBIR reporting highlights vulnerability exploitation as a top breach path. CVE Watch, KEV, EPSS, and exposure context help teams patch what attackers actually use.
BlueHammer Defender Exploitation: July 2026 Patch SLA For Windows Fleets
BlueHammer coverage shows why endpoint patching, CISA KEV context, CVE Watch, and IOC enrichment have to work together when local privilege escalation becomes ransomware tradecraft.
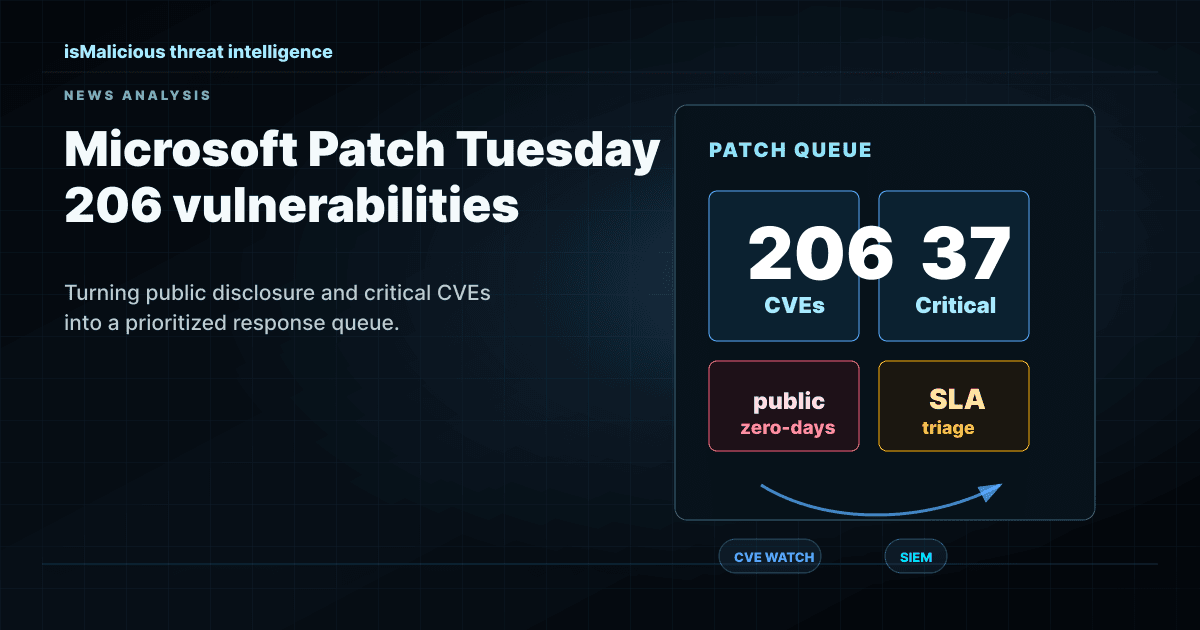
Microsoft June 2026 Patch Tuesday: Turning 206 Vulnerabilities Into A SOC Priority Queue
Microsoft patched 206 vulnerabilities in June 2026, including publicly disclosed zero-days. Security teams need CVE Watch, KEV context, exploit evidence, and enrichment to avoid patch fatigue.
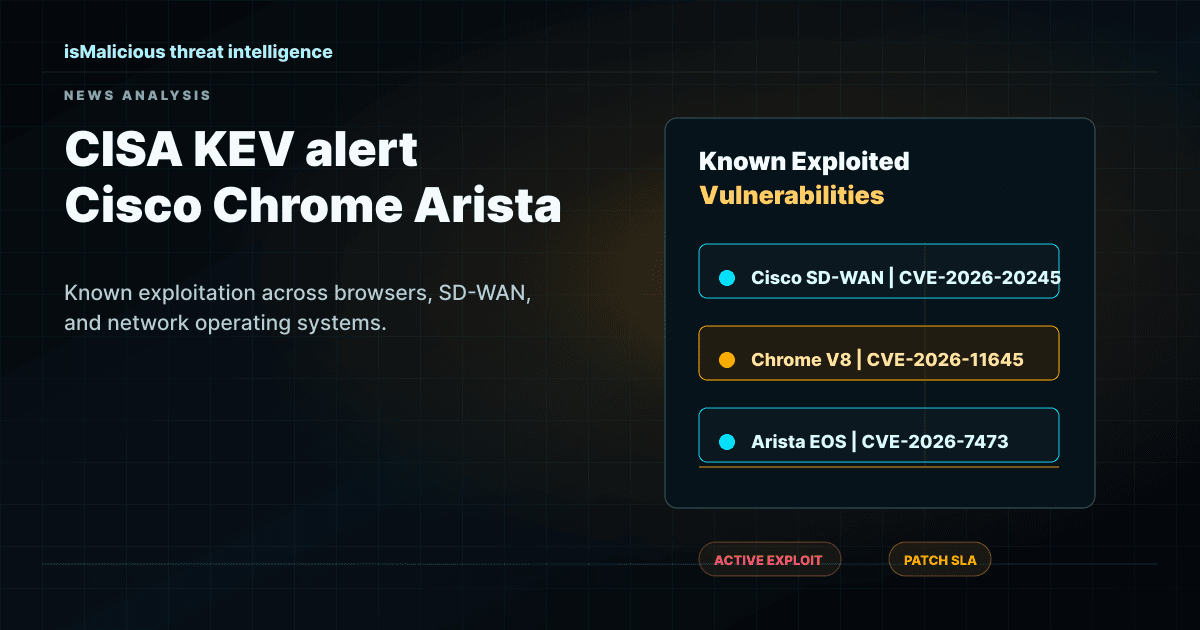
CISA KEV Adds Cisco, Chrome, And Arista Flaws: How To Prioritize Active Exploitation
CISA added Cisco SD-WAN, Google Chromium V8, and Arista EOS vulnerabilities to KEV in June 2026. Here is how SOC and vulnerability teams should turn that signal into action.
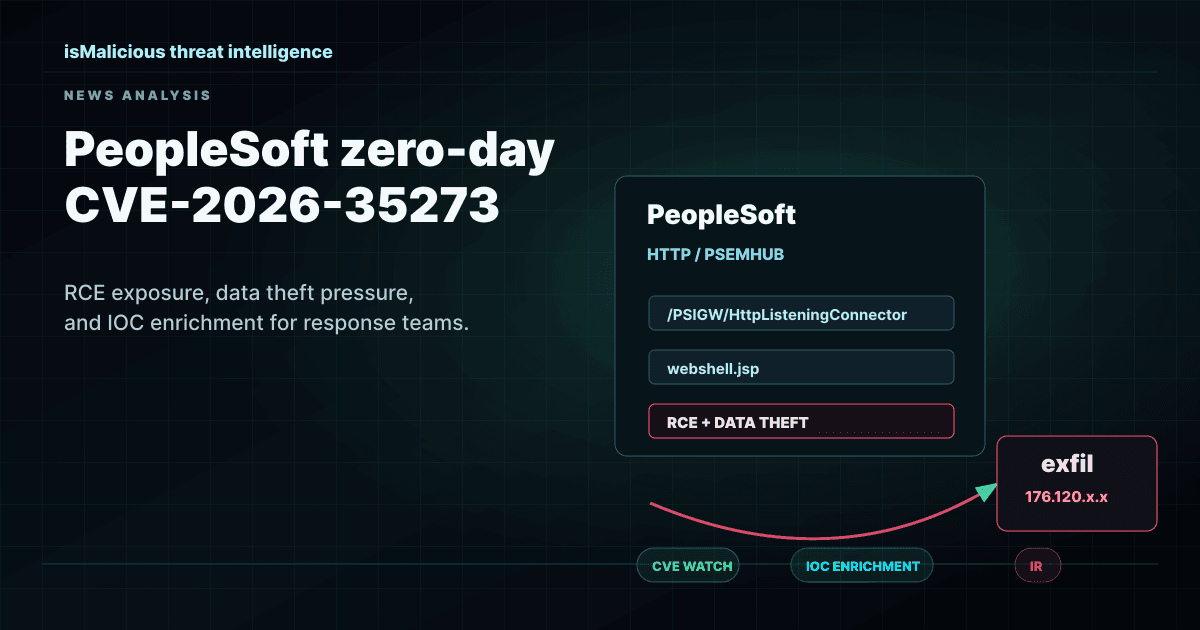
Oracle PeopleSoft Zero-Day: CVE-2026-35273 Shows Why CVE Watch Needs IOC Enrichment
The PeopleSoft CVE-2026-35273 exploitation reports show how vulnerability response, ransomware intelligence, IP enrichment, and incident response must work together.
YellowKey and BitLocker Bypass: How Security Teams Should Re-Baseline Stolen-Device Risk
YellowKey made a quiet assumption loud again: encrypted endpoints still need vulnerability intelligence, asset context, and incident workflows. Here is how to respond when a last-resort control becomes a live risk.
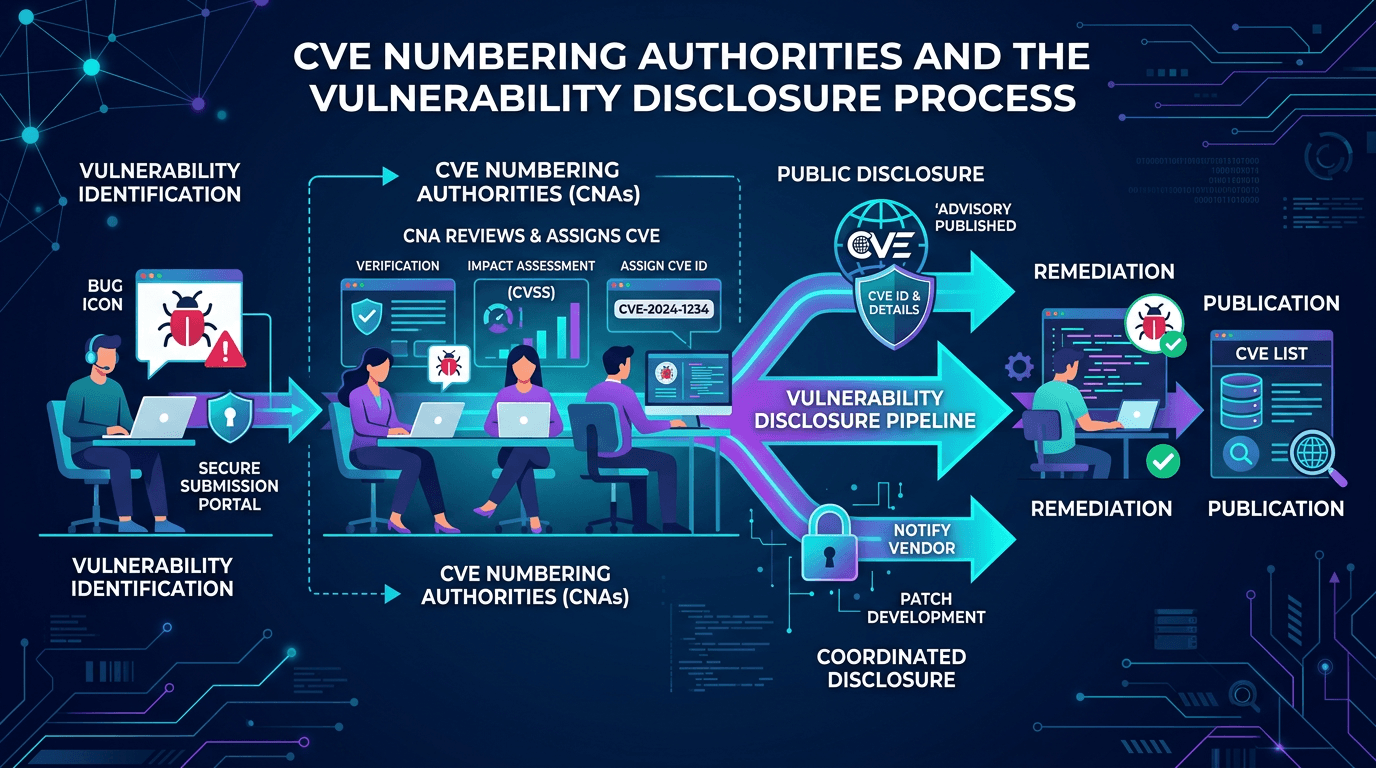
CVE Numbering Authorities and the Vulnerability Disclosure Process: A 2026 Practitioner Guide
Understand how CVEs are born—from initial vulnerability discovery through CNA assignment, coordinated disclosure, and publication—plus how this pipeline shapes defender priorities and SEO-visible vulnerability data.
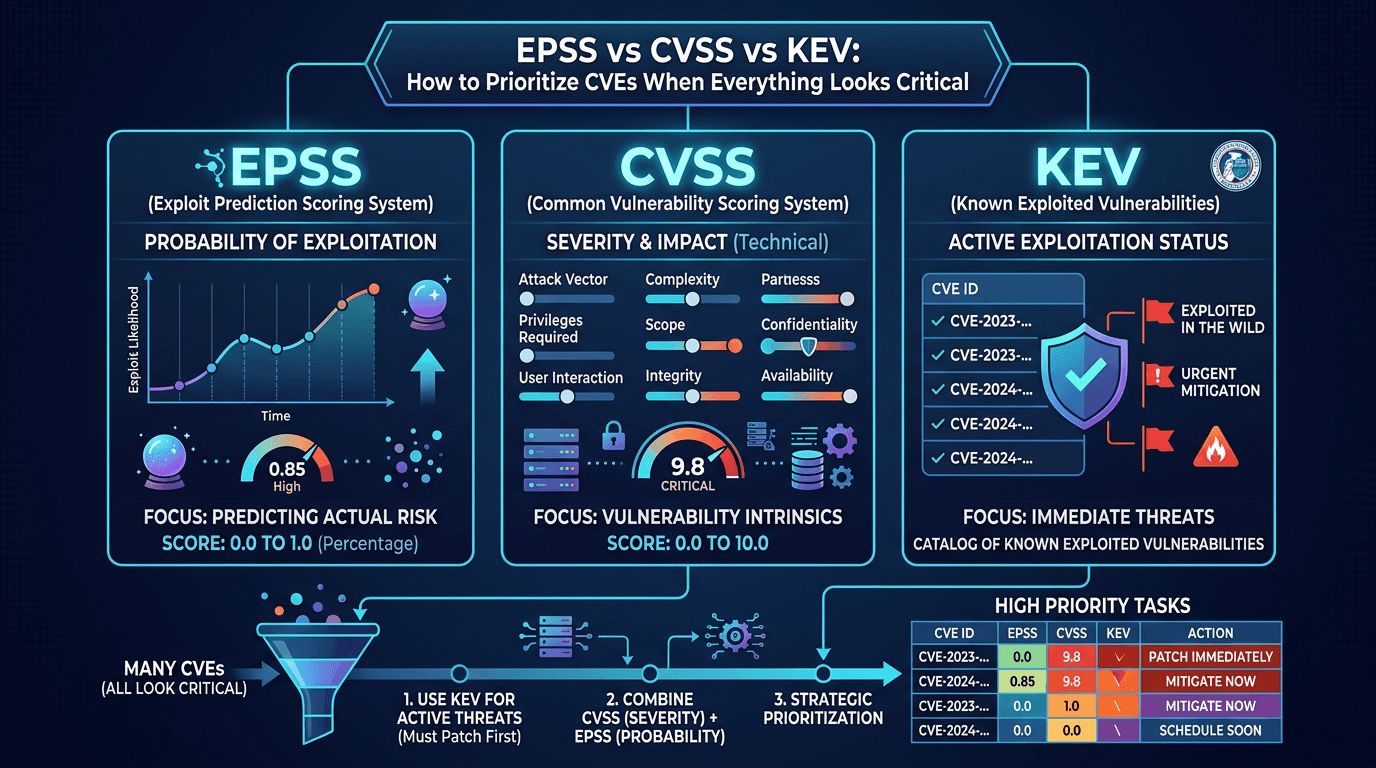
EPSS vs CVSS vs KEV: How to Prioritize CVEs When Everything Looks Critical
Cut through scoring confusion: compare CVSS severity, EPSS exploit probability, and CISA KEV active exploitation—and learn a practical model for patch and compensating-control decisions.
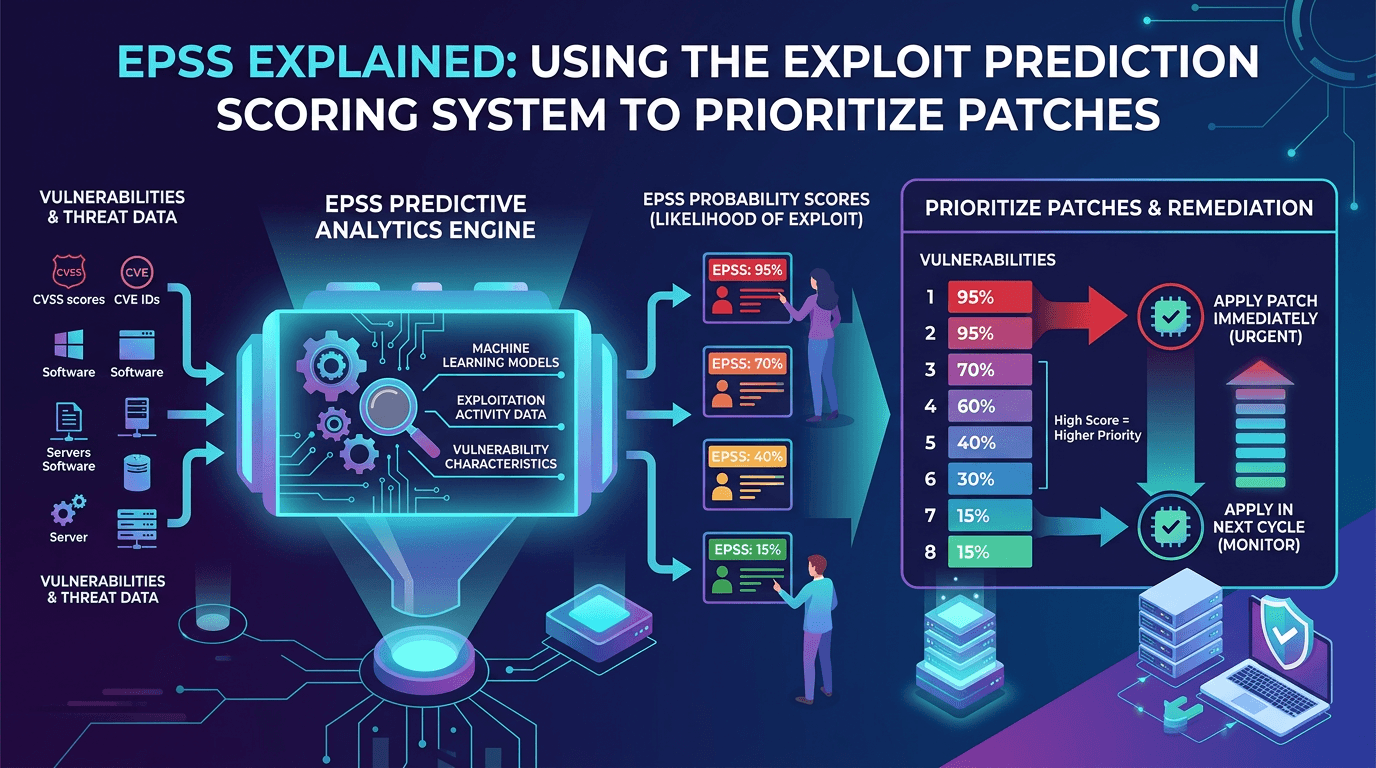
EPSS Explained: Using the Exploit Prediction Scoring System to Prioritize Patches in 2026
A practical guide to the Exploit Prediction Scoring System (EPSS)—how it works, how it complements CVSS and KEV, and how security teams can use EPSS probabilities to prioritize vulnerability management at scale.
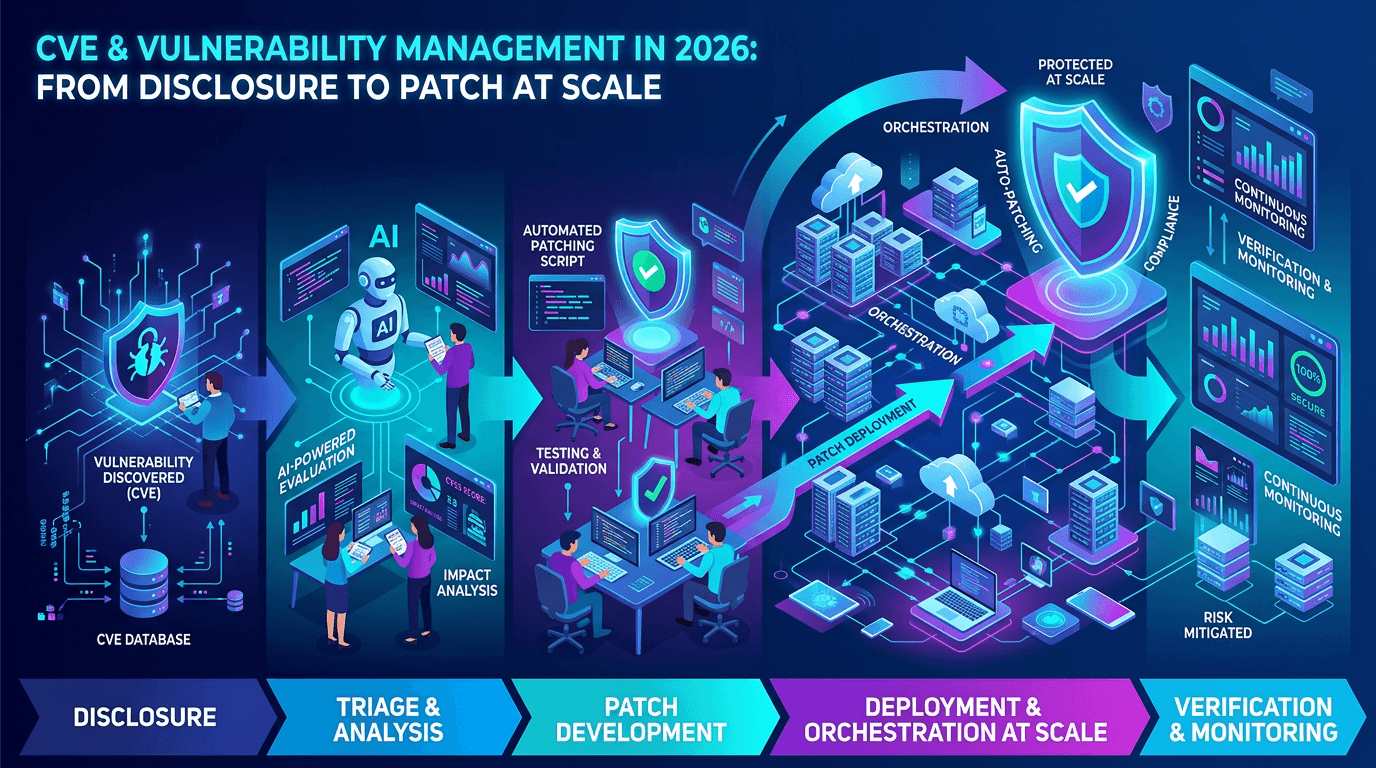
CVE & Vulnerability Management in 2026: From Disclosure to Patch at Scale
A practical guide to the CVE ecosystem, CVSS scoring, exploitability signals, and how security teams prioritize vulnerabilities without drowning in scanner noise.
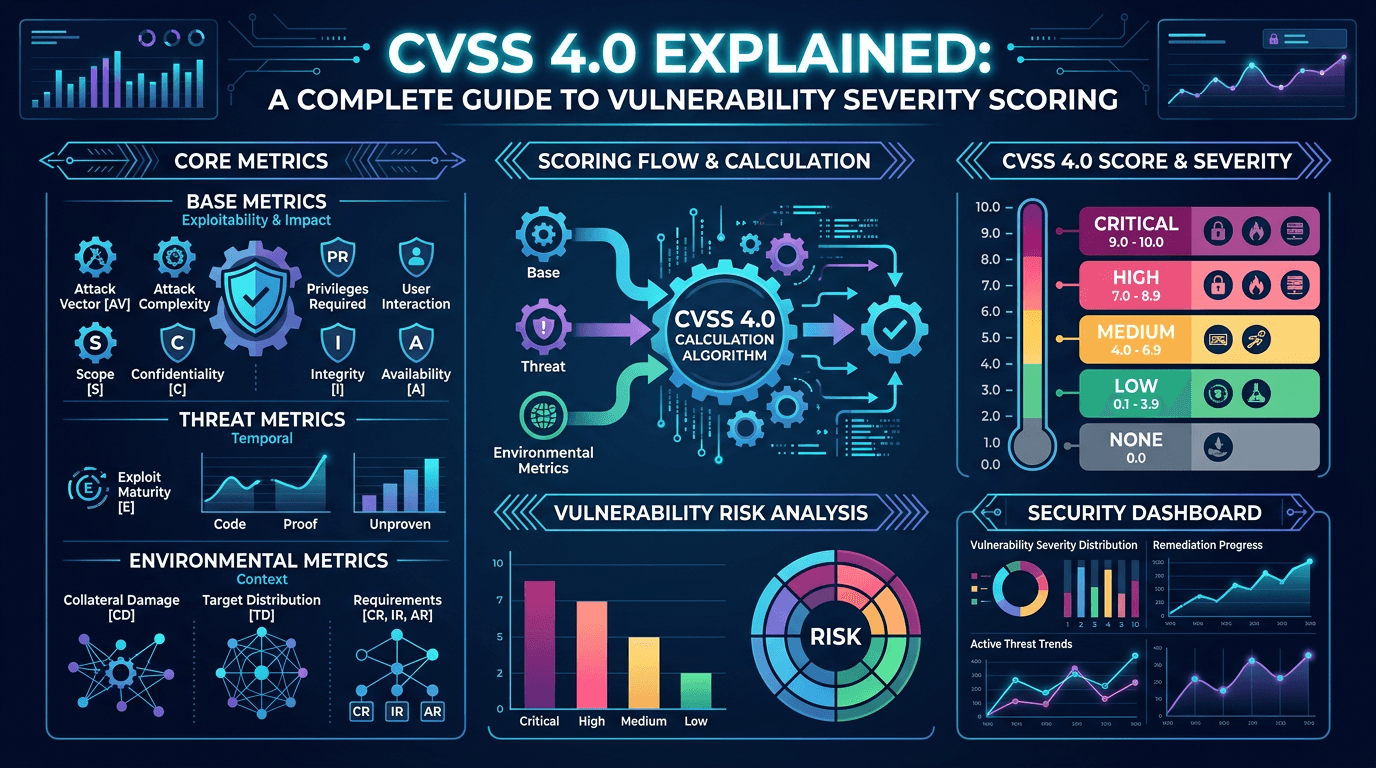
CVSS 4.0 Explained: A Complete Guide to Vulnerability Severity Scoring in 2026
Master the Common Vulnerability Scoring System v4.0 with a practical breakdown of base, threat, environmental, and supplemental metrics—and learn how to translate CVSS into real-world risk decisions.

Satellite Internet Security: Vulnerabilities in Low Earth Orbit (LEO)
Attack surfaces expand vertically as LEO constellations integrate with enterprise networks. This post details orbital jamming, ground station spoofing, and the lack of encryption standards in commercial satellite systems for security engineers.
Penetration Testing vs. Vulnerability Scanning: What's the Difference?
Often confused, these two security practices serve very different purposes. Discover when to use automated scanning and when to invest in a manual penetration test.
Zero-Day Vulnerabilities: Detection, Response, and Threat Intelligence
Zero-day vulnerabilities pose one of the greatest cybersecurity challenges. Learn how to detect exploitation attempts, respond effectively, and use threat intelligence to protect your organization from unknown threats.
Expert Threat Intelligence Analysis
Our blog features in-depth analysis from our threat research team. Each article is backed by real data from our analysis of millions of malicious domains, IPs, and URLs across the global threat landscape. Topics include ransomware campaigns, phishing techniques, malware distribution networks, and emerging threat trends. We publish specific intelligence that security teams can immediately use to improve their defenses.
Practical Security Guidance
Beyond threat analysis, we share practical guidance for security practitioners. Our tutorials cover API integration, SIEM configuration, threat hunting techniques, and building effective threat intelligence programs. Whether you're a SOC analyst, security engineer, or CISO, you'll find content tailored to your role and experience level.
Stay Ahead of Emerging Threats
The threat landscape evolves constantly. Our blog keeps you informed about the latest attack techniques, newly discovered vulnerabilities, and emerging threat actors. Subscribe to our newsletter for weekly digests of the most important developments in cybersecurity.
Subscribe to Our Newsletter
Weekly threat intelligence insights delivered to your inbox.