Threat Intelligence Blog
Research, insights, and updates from the isMalicious team.


Public Sector Supplier Remote Access: Control Every Session
Control supplier remote access with named identities, agreed work windows, bounded paths and verified revocation, using a practical public sector example.
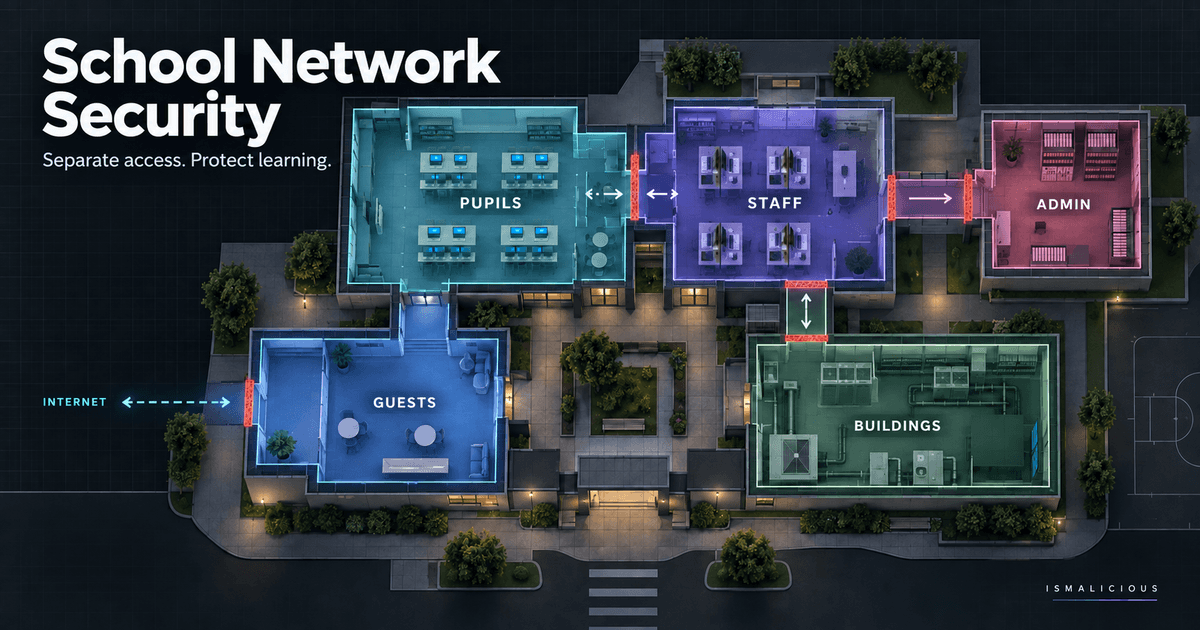
School Network Security: Test Segmentation That Works
Plan school network segmentation around teaching needs, test permitted and blocked paths, protect administration, and manage changes without losing access.
Proxy, VPN, Tor, and Datacenter IPs: A Decision Matrix for WAF, Fraud, and SIEM Rules (Without Breaking Real Users)
Not every "datacenter" IP is malicious, and not every Tor exit is a fraudster. This matrix-style guide helps you combine IP type signals with reputation and product context for safer, explainable security decisions.
Cognitive Hacking: The Battle for Your Mind
Cognitive hacking targets the user, not the machine. It manipulates perception and decision-making through disinformation and psychological triggers.
The Splinternet: Navigating a Fragmented World Wide Web
The global internet is fracturing into regional, regulated intranets. We explore the rise of the "Splinternet" and its impact on cybersecurity and global business.
Steganography: Hiding Secrets in Plain Sight
Steganography hides data within innocent-looking files like images or audio. Learn how hackers use digital steganography to smuggle malware and steal data.

Space Systems Cyber Threats: Securing the Final Frontier
As space becomes accessible, it becomes a target. From satellite hijacking to ground station jamming, we analyze the unique threats to orbital assets and how threat intelligence secures the new space race.

Metaverse Security: Privacy and Identity in Virtual Worlds
As the enterprise Metaverse expands, so does the attack surface. From avatar impersonation to spatial data theft, we explore the new frontier of virtual threats and how IP reputation protects digital assets.
Detecting VPNs, Proxies & Tor: The Hidden Threat in Anonymized Traffic
Legitimate users rarely hide behind Tor or anonymous proxies. Discover how attackers exploit anonymization layers to bypass defenses, and how IP intelligence helps you unmask high-risk traffic in real-time.

Drone Defense Security: Mitigating Unauthorized UAV Threats
Unauthorized drones pose a threat to critical infrastructure, stadiums, and prisons. This post explores Counter-Unmanned Aircraft Systems (C-UAS), detection methods, and how strict "no-fly" zones are enforced electronically.

Smart City Security: Protecting Critical Infrastructure from Cyber Attack
Connected traffic lights, sensors, and water systems create a vast attack surface in modern cities. We examine the vulnerabilities of smart city infrastructure and the cascading failures a cyberattack could cause.
Cyber Threats 101: Understanding Online Dangers
A beginner's guide to common cyber threats. Understand malware, viruses, and hackers, and learn how to protect yourself online.
Healthcare IoT Security: The Critical Risk to Patient Safety
Connected medical devices (IoMT) introduce life-critical vulnerabilities into hospital networks. From MRI machines to insulin pumps, this guide analyzes the unique challenges of securing legacy firmware and unpatched operating systems.
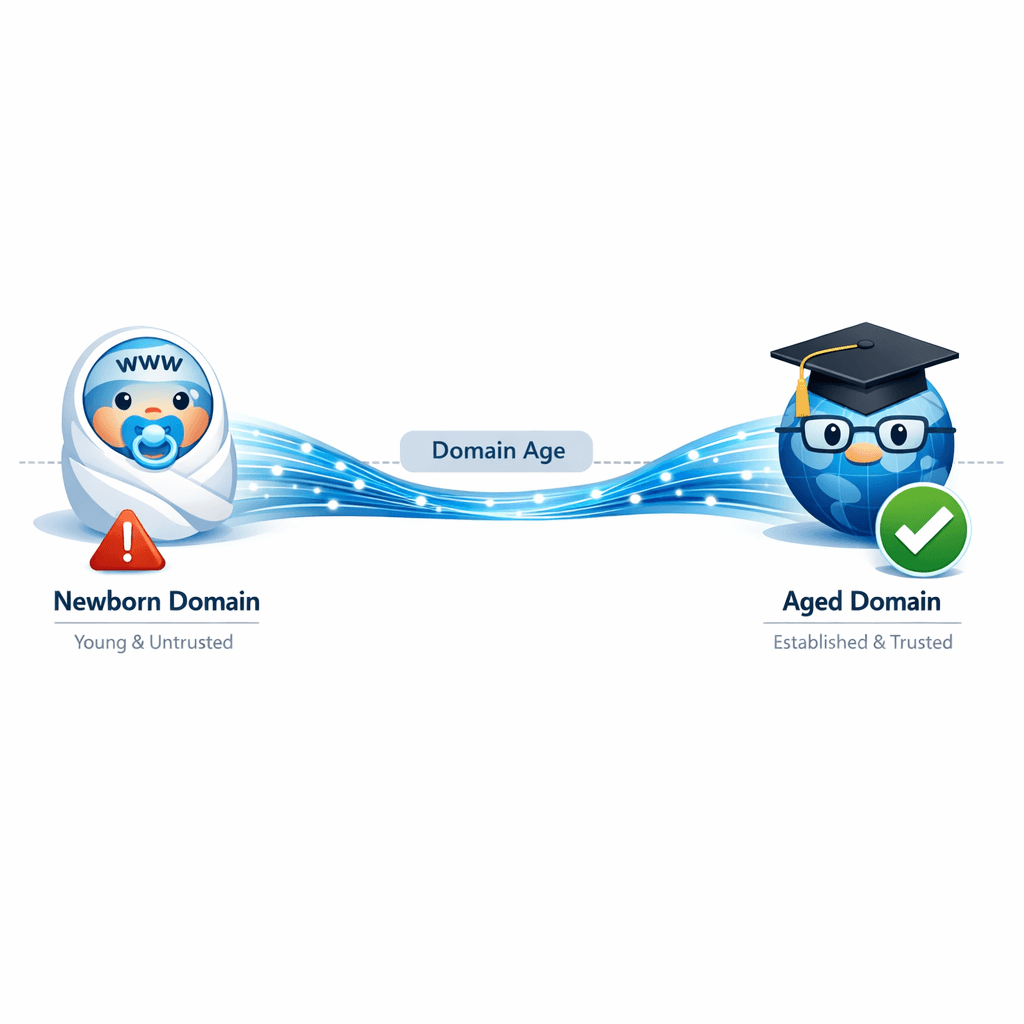
Domain Age as a Risk Indicator: Why "New" Often Means "Danger"
Newly registered domains (NRDs) are a favorite tool for threat actors. Learn why domain age is a critical signal in your threat intelligence stack and how to use it effectively.
Navigating Data Privacy: GDPR, CCPA, and Cybersecurity Compliance
Privacy regulations are reshaping cybersecurity strategies. Understand the key requirements of GDPR and CCPA and how to align your security program with privacy compliance.
Automotive Cybersecurity: Hacking Connected Cars in 2026
With cars becoming data centers on wheels, the attack surface expands into the powertrain, infotainment, and OTA update systems. We analyze CAN bus injection vulnerabilities and the security risks of V2X communication protocols.

Shadow IT Risk Management: Securing Unauthorized Applications and Services
Employees use unauthorized apps and services that IT cannot see. Learn how to discover shadow IT, assess risks from unsanctioned tools, and implement governance without stifling innovation.
IoT Security Threats: Protecting Your Smart Devices from Cyberattacks
Internet of Things devices are increasingly targeted by cybercriminals. Learn how to identify IoT vulnerabilities, secure smart devices, and protect your network from IoT-based attacks.
DDoS Attacks: Prevention That Works
What actually stops a DDoS attack: detection signals, mitigation layers, and the preparation that decides whether you stay online.
Data Exfiltration Prevention: DLP Strategies to Protect Sensitive Information
Data theft can occur through countless channels. Learn how to detect and prevent data exfiltration, implement effective DLP strategies, and protect your organization most valuable assets from leaving your control.
Mobile App Security: Protecting iOS and Android Applications
Mobile applications are prime targets for cybercriminals. Learn about common mobile security threats and how to protect your iOS and Android apps from reverse engineering and malware.
Understanding IP Maliciousness: A new way to protect your network.
Discover how assessing the potential maliciousness of an IP can safeguard your systems against cyber threats. Learn about the indicators, methods, and tools that help identify malicious IPs and take proactive measures.
Expert Threat Intelligence Analysis
Our blog features in-depth analysis from our threat research team. Each article is backed by real data from our analysis of millions of malicious domains, IPs, and URLs across the global threat landscape. Topics include ransomware campaigns, phishing techniques, malware distribution networks, and emerging threat trends. We publish specific intelligence that security teams can immediately use to improve their defenses.
Practical Security Guidance
Beyond threat analysis, we share practical guidance for security practitioners. Our tutorials cover API integration, SIEM configuration, threat hunting techniques, and building effective threat intelligence programs. Whether you're a SOC analyst, security engineer, or CISO, you'll find content tailored to your role and experience level.
Stay Ahead of Emerging Threats
The threat landscape evolves constantly. Our blog keeps you informed about the latest attack techniques, newly discovered vulnerabilities, and emerging threat actors. Subscribe to our newsletter for weekly digests of the most important developments in cybersecurity.
Subscribe to Our Newsletter
Weekly threat intelligence insights delivered to your inbox.