Threat Intelligence Blog
Research, insights, and updates from the isMalicious team. Page 9 of 10.


Healthcare IoT Security: The Critical Risk to Patient Safety
Connected medical devices (IoMT) introduce life-critical vulnerabilities into hospital networks. From MRI machines to insulin pumps, this guide analyzes the unique challenges of securing legacy firmware and unpatched operating systems.
isMalicious vs Shodan: Threat Reputation vs Attack Surface Discovery
Shodan maps internet-connected devices. isMalicious checks if IPs and domains are malicious. Compare these complementary threat intelligence tools across features, use cases, and pricing to choose the right one.
The Deepfake Threat: Protecting Enterprise Security in the Era of AI
AI-generated video and audio are becoming indistinguishable from reality. Explore the rising threat of deepfakes to enterprise security and how to defend against synthetic media attacks.
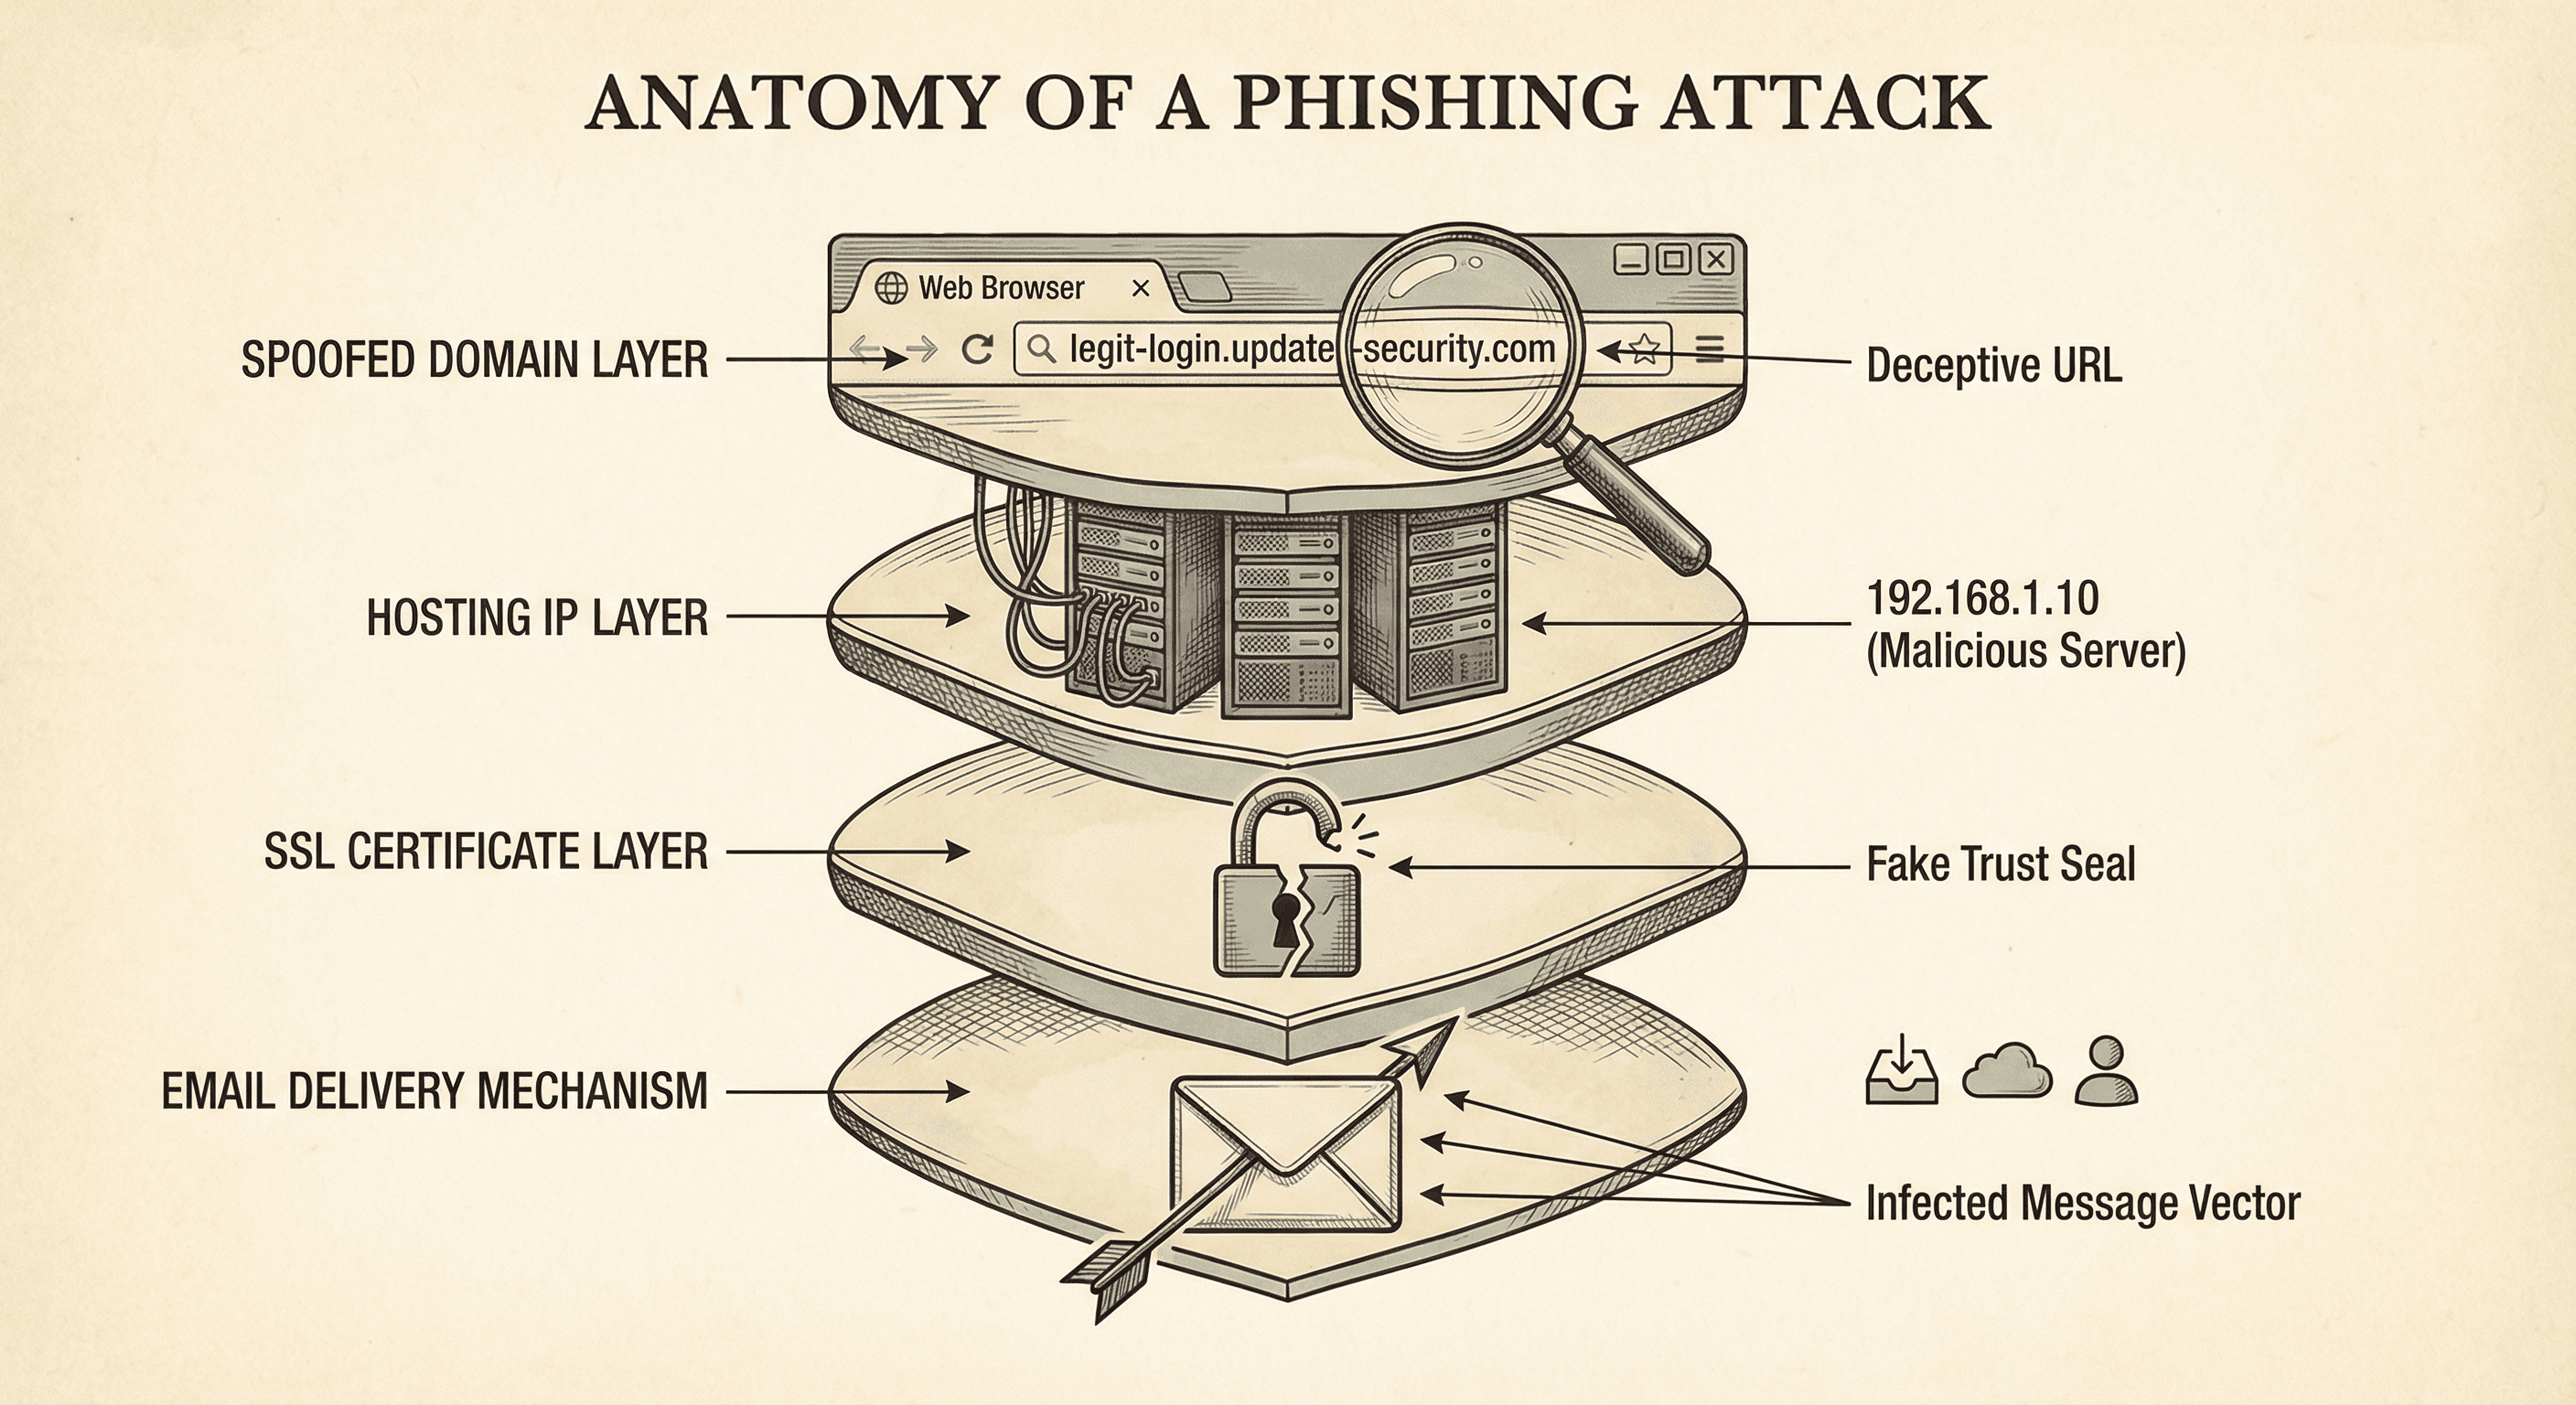
Anatomy of Phishing Infrastructure: How Attackers Build Their Trap
Peel back the layers of a modern phishing attack. From spoofed domains to SSL certificates, understand the infrastructure attackers use and how to detect it.
Automating Threat Intelligence: Speed is Your Best Defense
Manual analysis cannot keep up with machine-speed attacks. Learn how to automate threat data ingestion and response to block threats in milliseconds, not minutes.
Contextual Threat Intelligence: Moving Beyond Static Blacklists
Static IP blacklists are no longer enough. Discover the power of contextual threat intelligence—connecting IPs, domains, and behavior to see the full attack picture.
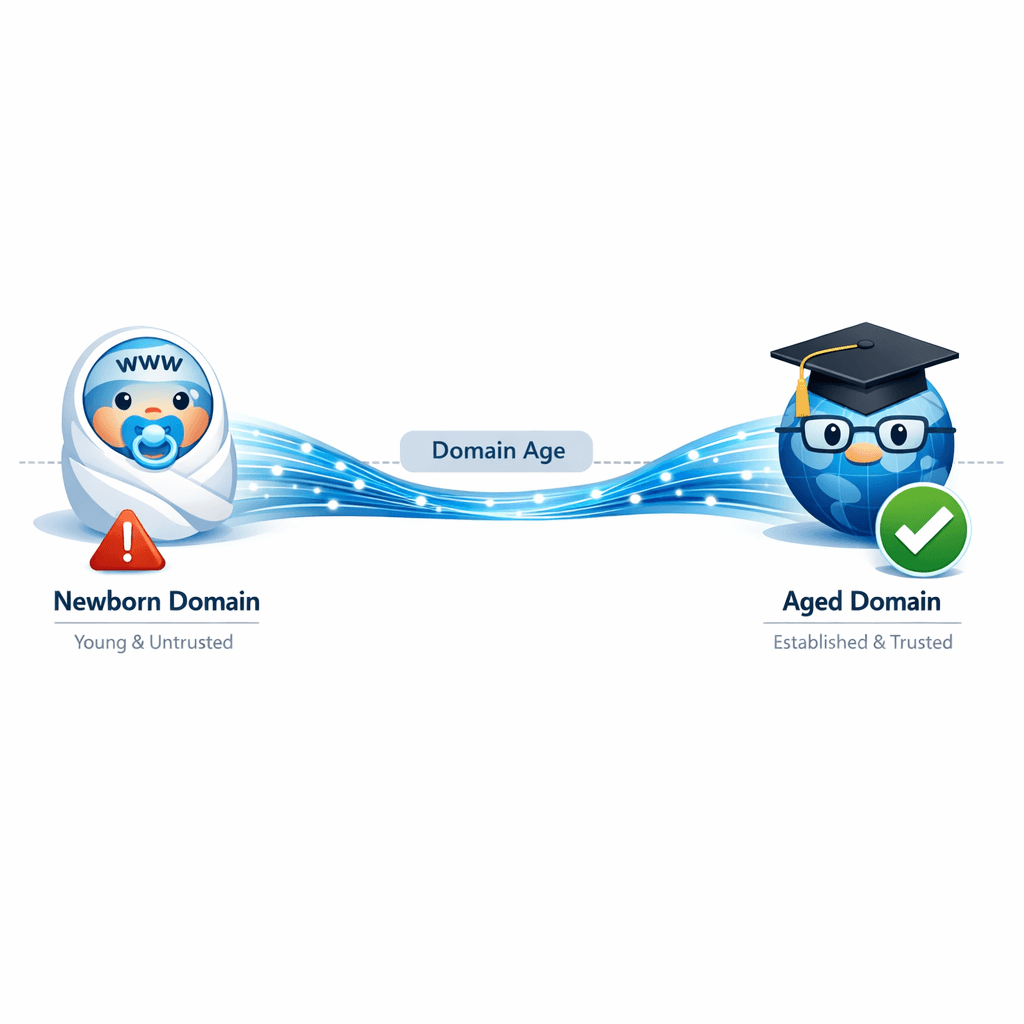
Domain Age as a Risk Indicator: Why "New" Often Means "Danger"
Newly registered domains (NRDs) are a favorite tool for threat actors. Learn why domain age is a critical signal in your threat intelligence stack and how to use it effectively.
Best Threat Intelligence APIs in 2026
isMalicious, VirusTotal, AbuseIPDB, OTX, Shodan, URLhaus — free tiers, rate limits, coverage, and which API fits which job, in one table.
Navigating Data Privacy: GDPR, CCPA, and Cybersecurity Compliance
Privacy regulations are reshaping cybersecurity strategies. Understand the key requirements of GDPR and CCPA and how to align your security program with privacy compliance.
Automotive Cybersecurity: Hacking Connected Cars in 2026
With cars becoming data centers on wheels, the attack surface expands into the powertrain, infotainment, and OTA update systems. We analyze CAN bus injection vulnerabilities and the security risks of V2X communication protocols.
API Security Best Practices: Defending Against the OWASP Top 10
APIs are the backbone of modern applications but are often left vulnerable. Learn how to secure your APIs against common attacks like broken object level authorization and injection.
Threat Hunting: Proactive Security Detection Beyond Automated Alerts
Waiting for alerts means waiting for attacks to succeed. Learn how proactive threat hunting helps security teams discover hidden threats, improve defenses, and stay ahead of sophisticated adversaries.

Shadow IT Risk Management: Securing Unauthorized Applications and Services
Employees use unauthorized apps and services that IT cannot see. Learn how to discover shadow IT, assess risks from unsanctioned tools, and implement governance without stifling innovation.
DevSecOps: Integrating Security into the CI/CD Pipeline
Security should not be an afterthought. Learn how to implement DevSecOps to automate security testing and vulnerability scanning within your development workflow.
Lateral Movement Detection: Stopping Attackers from Spreading Through Your Network
After initial compromise, attackers move laterally to reach valuable targets. Learn how to detect lateral movement techniques, implement segmentation, and stop attackers before they reach critical assets.
IoT Security Threats: Protecting Your Smart Devices from Cyberattacks
Internet of Things devices are increasingly targeted by cybercriminals. Learn how to identify IoT vulnerabilities, secure smart devices, and protect your network from IoT-based attacks.
Insider Threat Detection: Identifying and Managing Employee Security Risks
Insider threats pose unique challenges to organizational security. Learn how to detect malicious insiders, prevent data leakage, and build an effective insider threat program.
Email Authentication: Implementing DMARC, SPF, and DKIM for Email Security
Email spoofing enables phishing and business email compromise attacks. Learn how DMARC, SPF, and DKIM authentication protocols protect your domain from being impersonated in cyberattacks.
What is EDR? A Guide to Endpoint Detection and Response
Traditional antivirus is no longer enough. Explore why Endpoint Detection and Response (EDR) is essential for modern cybersecurity and how it differs from legacy solutions.
DDoS Attacks: Prevention That Works
What actually stops a DDoS attack: detection signals, mitigation layers, and the preparation that decides whether you stay online.
Data Exfiltration Prevention: DLP Strategies to Protect Sensitive Information
Data theft can occur through countless channels. Learn how to detect and prevent data exfiltration, implement effective DLP strategies, and protect your organization most valuable assets from leaving your control.
Dark Web Monitoring: Protecting Your Brand and Detecting Leaked Data
Stolen credentials and sensitive data often surface on the dark web before being exploited. Learn how dark web monitoring helps detect breaches early and protect your organization from cybercriminal activities.
Container and Kubernetes Security: Protecting Cloud-Native Applications
Container environments introduce unique security challenges. Learn how to secure Docker containers, Kubernetes clusters, and cloud-native applications from emerging threats and misconfigurations.
Beyond Phishing: Modern Social Engineering Tactics
Social engineering has evolved beyond simple phishing emails. Discover the latest tactics used by attackers, including vishing, smishing, and pigmenting, and how to spot them.
Subscribe to Our Newsletter
Weekly threat intelligence insights delivered to your inbox.