Reverse IP Lookup: Pivoting on Infrastructure Without Drowning in Shared Hosting
A reverse IP lookup turns one indicator into a cluster — or into a thousand innocent neighbours. Here is how to tell the difference, and how to pivot on hosting infrastructure without generating false positives.
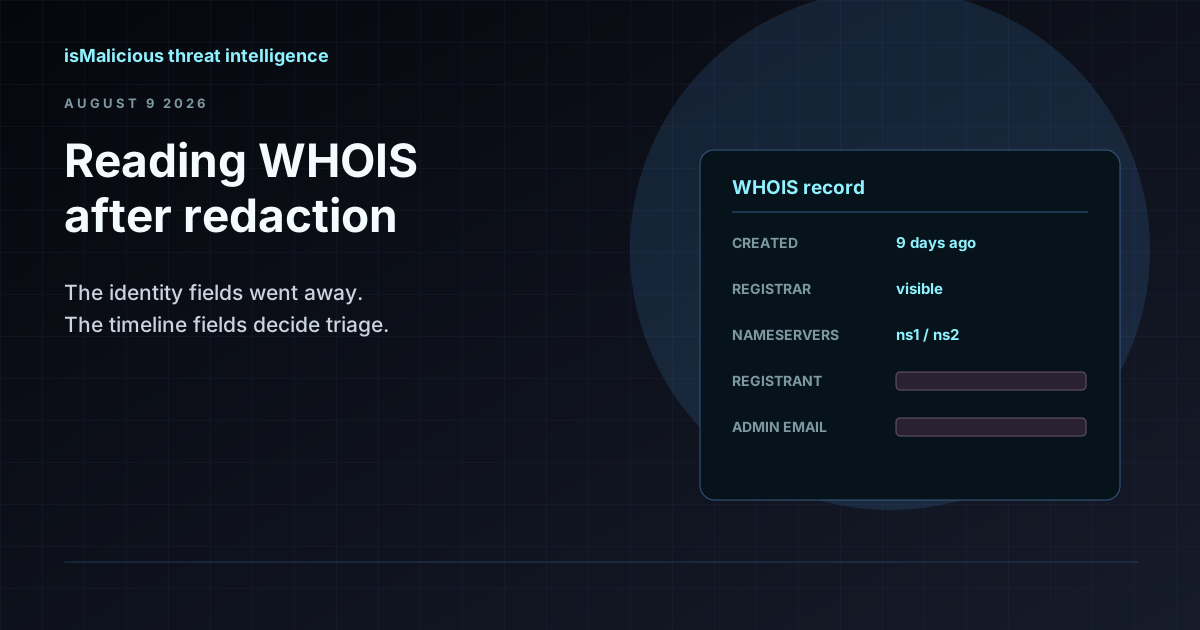
WHOIS Lookup for Security Investigations: Reading a Record After Redaction
Privacy services stripped the registrant name out of most WHOIS records, but the fields that matter for triage survived. Here is what a WHOIS record still tells an analyst, and how to read it.
The Kratos Phishing Kit Takedown: 200 Servers Gone, 1,800 Copies Still Out There
German and US law enforcement dismantled Kratos, the AiTM phishing service behind roughly 15,000 Microsoft 365 campaigns a month. The infrastructure is offline, but the kit is not. Here is what to hunt for now.
Subdomain Enumeration for Security Teams: Attack Surface Discovery and DNS Reconnaissance
Subdomain enumeration surfaces forgotten dev servers, dangling DNS, and shadow IT before attackers do. Passive and active recon techniques compared.
China Edge Device Campaigns: Passive DNS And Certificates For Early Warning
Dutch intelligence warnings about Chinese cyber capability reinforce a practical defense priority: monitor edge devices, VPNs, routers, DNS history, and certificate reuse.
Agentic AI Threat Mapping: MITRE ATT&CK Needs Evidence-Rich Workflows
Anthropic mapped AI-enabled cyber activity to MITRE ATT&CK and found gaps around autonomous orchestration. SOC teams need AI summaries tied to evidence, not unsupported verdicts.
SOC Alert Fatigue In July 2026: Confidence Scoring Beats More Noise
Vectra AI research shows alert overload remains a resilience problem. SOC teams need source quality, confidence scoring, enrichment, and SIEM workflows that suppress noise without hiding risk.
AI-Enabled Cyberattacks and MITRE ATT&CK: Turning New Threat Maps Into SOC Action
AI-enabled threats are being mapped into ATT&CK language, but mapping is only useful when it drives enrichment, detection, triage, and response workflows.
Cyber Extortion Now Includes Physical Threats: What Incident Response Teams Must Change
Cyber incidents are no longer always contained to systems and data. As extortion crews add physical threats, responders need ransomware intelligence, safety escalation, IOC enrichment, and executive-ready evidence.
SOC Alert Fatigue: How Threat Intelligence Reduces False Positives Without Hiding Real Attacks
Alert fatigue is not a staffing problem alone. SOC teams need better evidence, source quality, confidence bands, and enrichment workflows that turn noisy alerts into defensible decisions.

AI-Enabled Device Code Phishing: How OAuth Tokens Became the New Credential Theft Target
Device code phishing turns a legitimate OAuth flow into a token theft path. Learn how AI-assisted lures, Entra ID abuse, and session token replay change phishing detection in 2026.
MCP Security Risks: Tool Poisoning, Prompt Injection, and the New AI Agent Attack Surface
Model Context Protocol integrations give agents access to tools, files, and services. That power creates new risks: tool poisoning, prompt injection, overbroad permissions, and untrusted server abuse.
LLMjacking Explained: How Attackers Abuse Cloud Credentials to Steal AI Compute
LLMjacking combines cloud credential theft with expensive AI workloads. Learn how attackers find exposed keys, abuse model APIs, hide compute costs, and how defenders can detect the pattern.
OAuth Consent Phishing: Detecting Malicious App Grants Before Data Exfiltration
OAuth consent phishing tricks users into granting access instead of giving up passwords. Learn how malicious app grants work, which permissions matter, and how to detect abuse early.
Session Token Theft: Why Infostealers Bypass MFA and How Defenders Respond
Infostealers increasingly target browser cookies, session tokens, and refresh tokens. Learn why MFA is not enough, what token theft looks like, and how to detect replay.
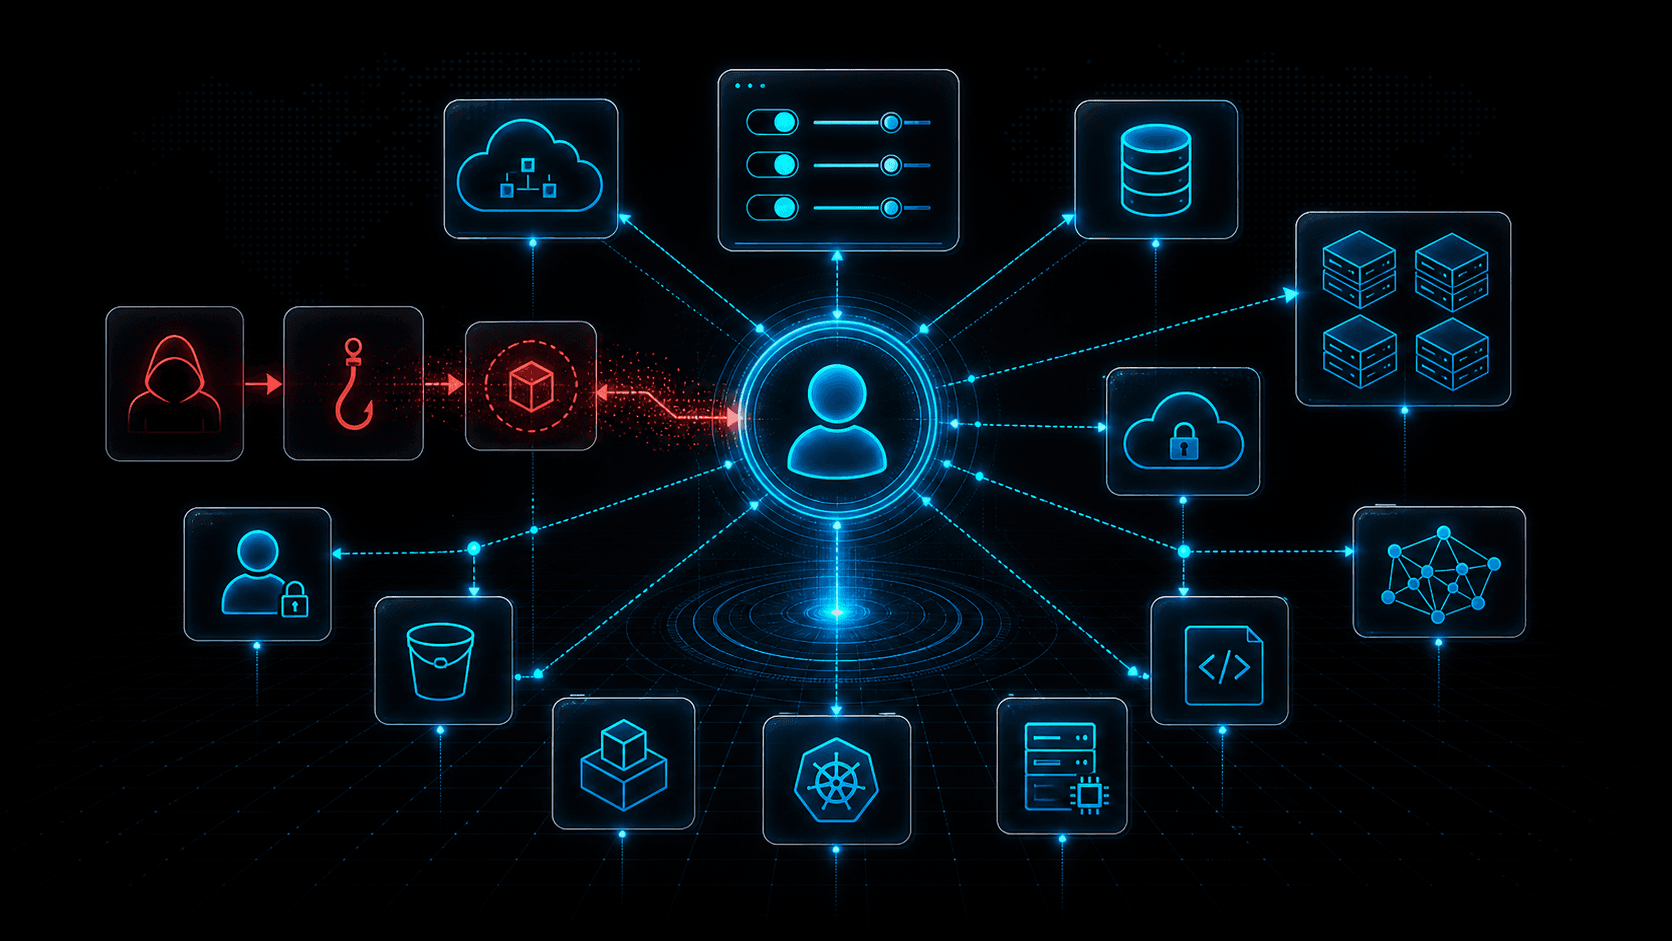
Cloud Control Plane Attacks: Why Identity Is the New Kill Chain
Cloud breaches increasingly target the control plane: identities, tokens, policies, APIs, and automation. Learn how attackers move from one credential to full cloud control.
Security LLM and Agent Workflows: When (and How) to Check Malicious Domains, IPs, and URLs Before Acting
AI assistants in SOAR, IDEs, and browser extensions can exfiltrate data or run malicious code if they fetch the wrong link. This guide gives guardrails: schema for tool calls, policy tiers, and where threat intelligence checks belong in the loop.
Malicious npm Packages: Detecting Open-Source Supply Chain Compromise
Malicious npm packages use typosquatting, dependency confusion, install scripts, and maintainer compromise to steal secrets and backdoor builds. Learn practical detection and response.
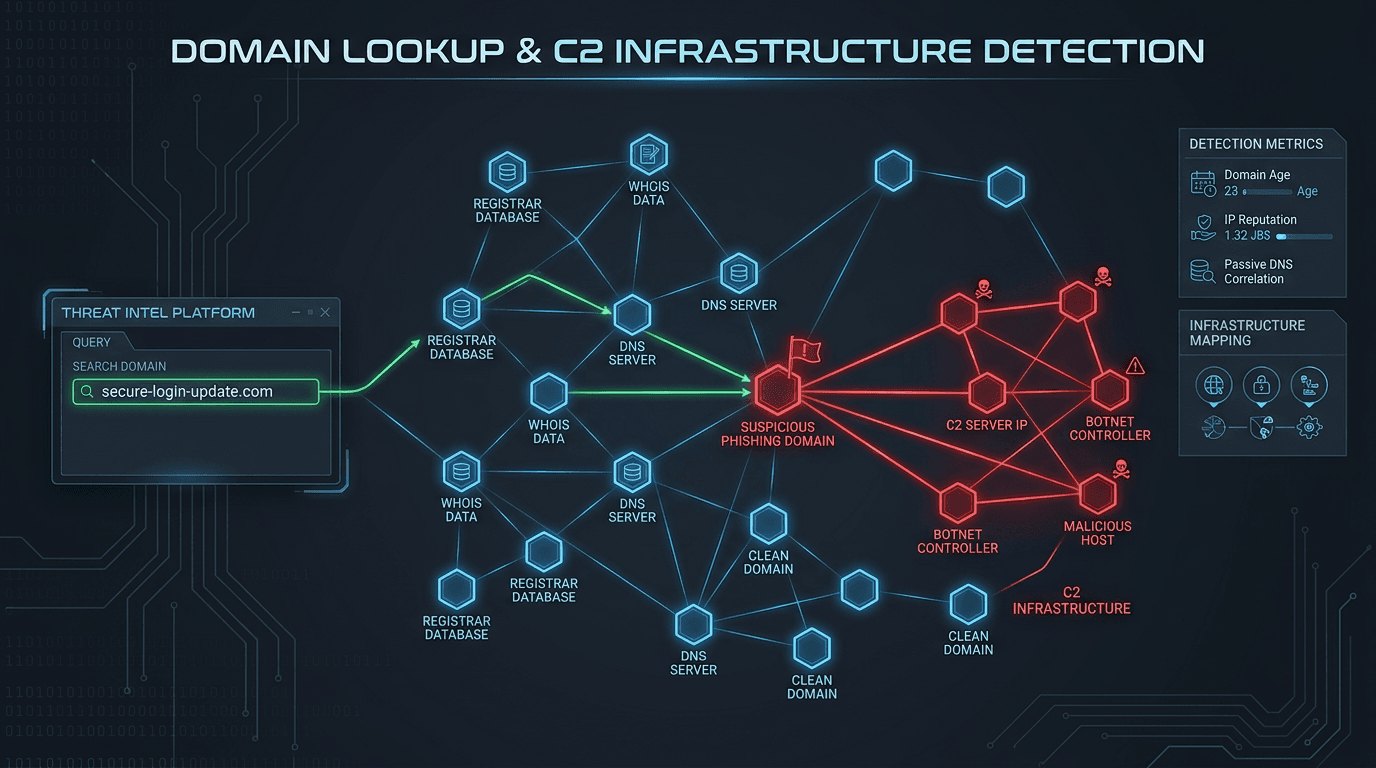
Malicious Infrastructure Clustering: How Passive DNS, TLS Certificates, and ASNs Reveal Shared Campaigns
A single C2 IP is a clue; shared signing patterns and DNS co-occurrence are a map. This guide explains how defenders cluster infrastructure without chasing ghosts—and how to document findings for IR, threat intel, and law enforcement handoffs.
Compromised Domains in Phishing: When Trusted Sites Become Attack Infrastructure
Attackers increasingly host phishing pages, redirects, and malware on compromised legitimate domains. Learn why reputation bypass works and how to detect hidden malicious paths.
DPRK Remote IT Worker Threat: Identity, Insider Risk, and Cloud Access Abuse
DPRK remote IT worker schemes blend fraud, identity deception, and insider access. Learn how hiring, endpoint, SaaS, and cloud controls can reduce the risk.
SIEM and SOAR Threat Intelligence Enrichment: Workflows, Field Mapping, and the Metrics That Keep Teams Sane
A SOAR playbook without enrichment is a ticket printer. A SIEM with unbounded threat feeds is a bill. Here is a practical way to design enrichment for Splunk, Sentinel, or Elastic-style stacks—what to store, when to run playbooks, and what to report upward.
Threat Intelligence Risk Scoring: How to Calibrate Reputation, Reduce False Positives, and Defend Your Decisions
A noisy score is worse than no score. Learn what makes a reputation model trustworthy, how to combine multi-source evidence, and how to communicate uncertainty to your SOC and your executives.
Cloud IP Reputation: What AWS, Azure, and GCP Defenders Should Track in 2026
Cloud IP addresses are shared, recycled, and abused at scale. Learn how to interpret reputation signals, reduce false positives, and align network security with platform-native controls across the three major hyperscalers.