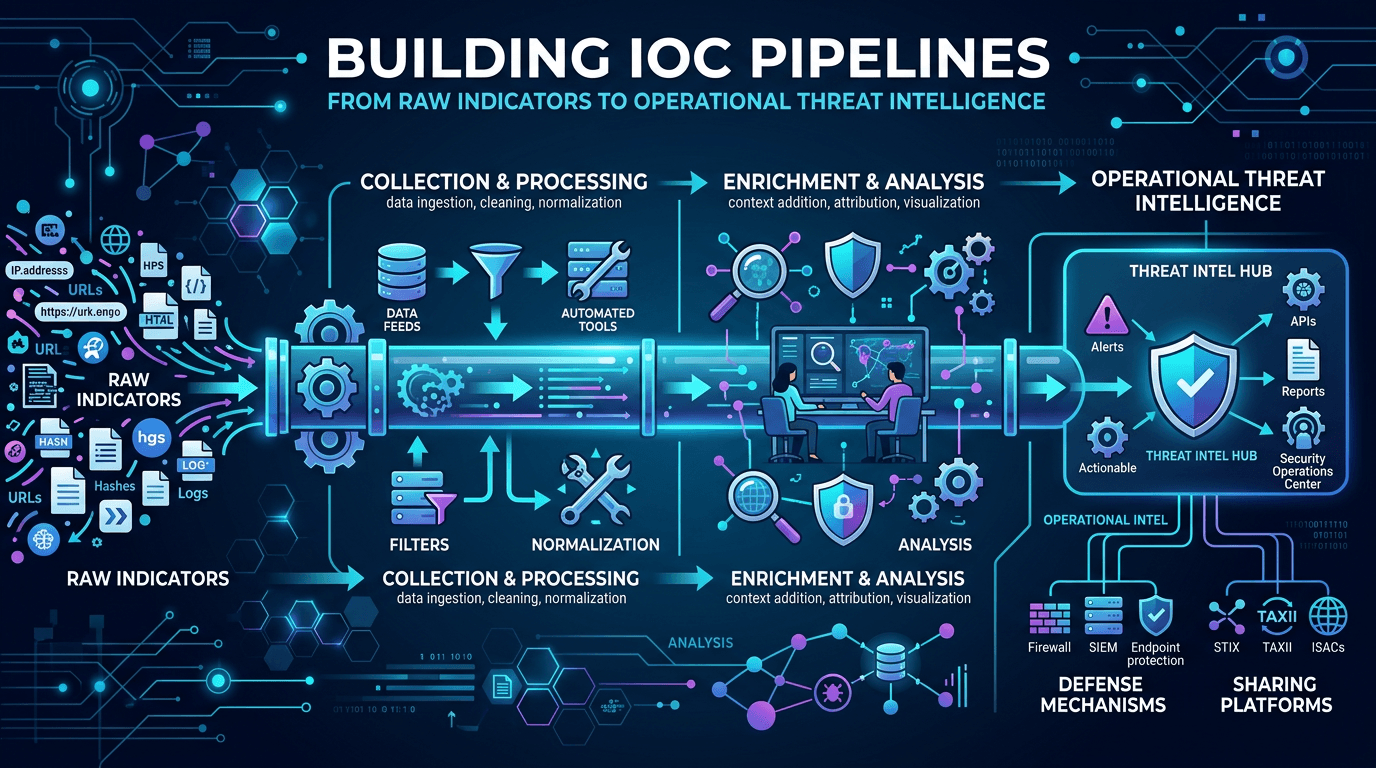
Building IOC Pipelines: From Raw Indicators to Operational Threat Intelligence in 2026
A practical engineering guide to building indicator of compromise (IOC) pipelines—ingestion, normalization, deduplication, enrichment, scoring, distribution, and feedback—to turn raw threat feeds into operational defense.
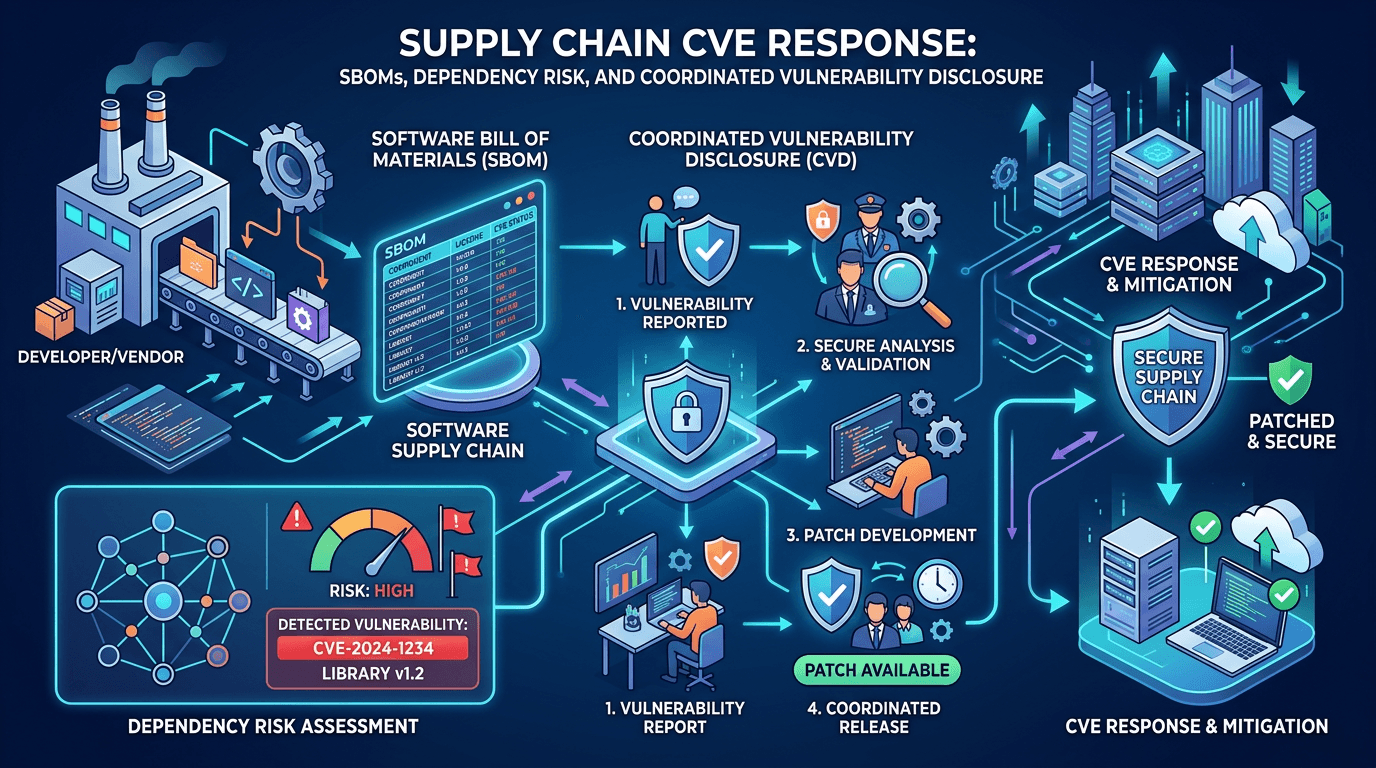
Supply Chain CVE Response: SBOMs, Dependency Risk, and Coordinated Vulnerability Disclosure
Build a modern supply-chain security program: generate SBOMs, map CVEs to components, integrate EPSS and KEV, and coordinate fixes across vendors and open-source maintainers.
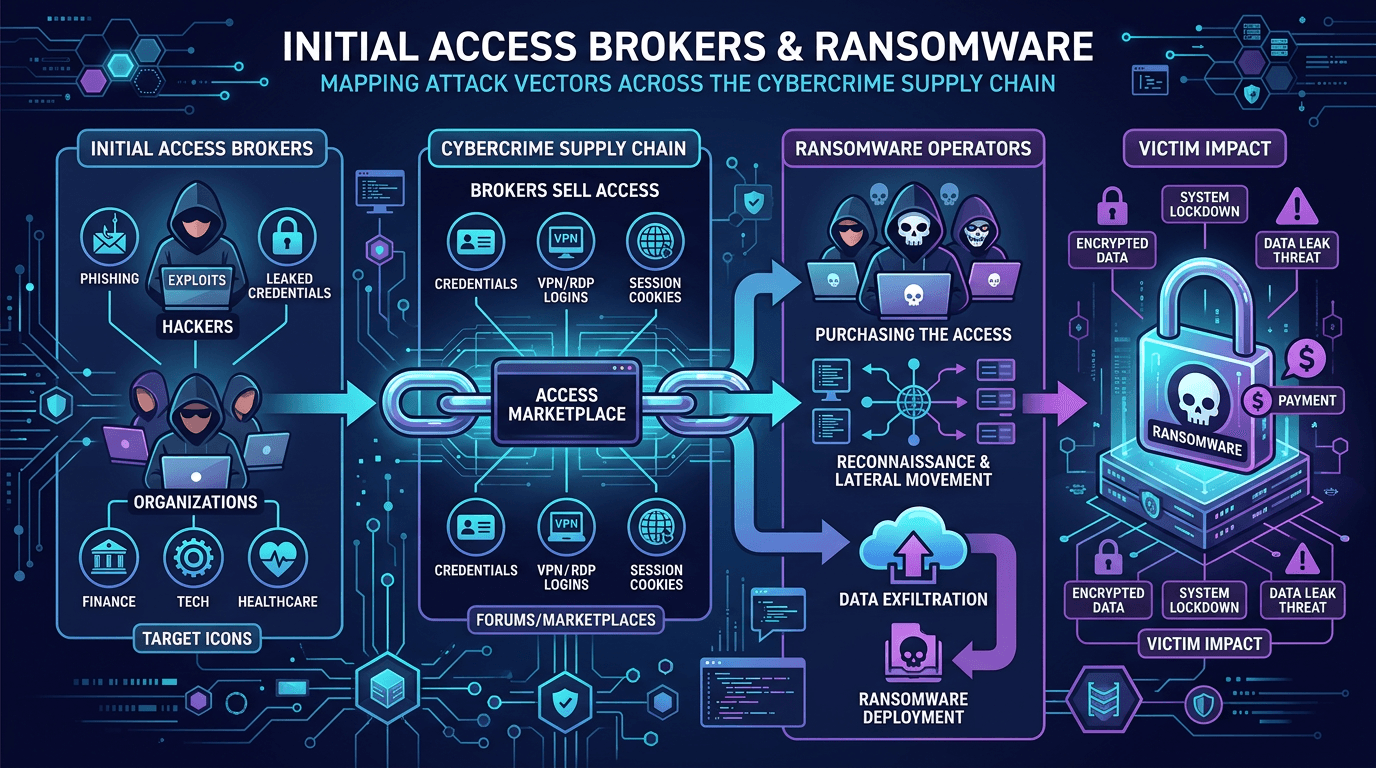
Initial Access Brokers and Ransomware: Mapping Attack Vectors Across the Cybercrime Supply Chain
Understand how access brokers monetize footholds, how ransomware affiliates purchase them, and which defensive controls break the supply chain—from phishing to exposed services.
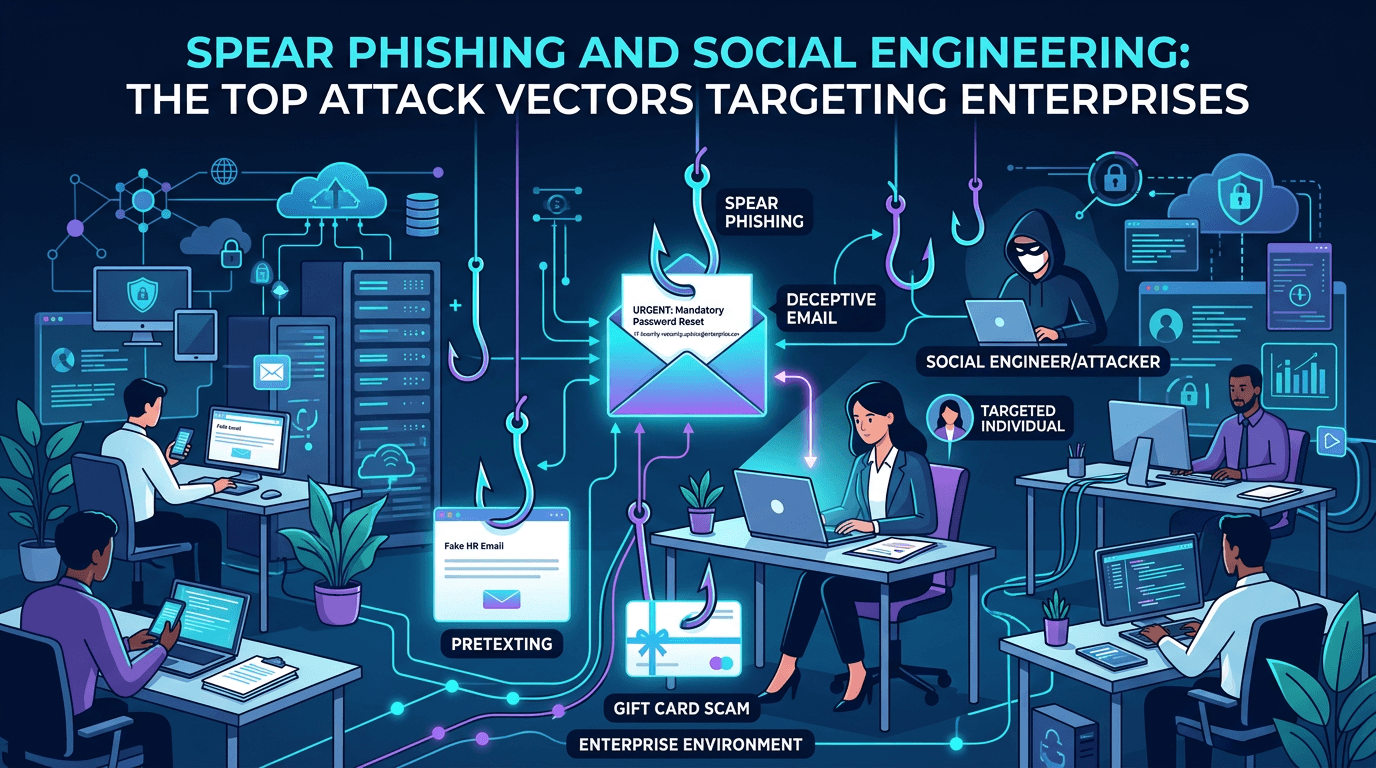
Spear Phishing and Social Engineering: The Top Attack Vectors Targeting Enterprises in 2026
A complete guide to modern spear phishing and social engineering attack vectors—how threat actors plan, lure, and pivot, with detailed defensive controls for email, identity, training, and infrastructure reputation.
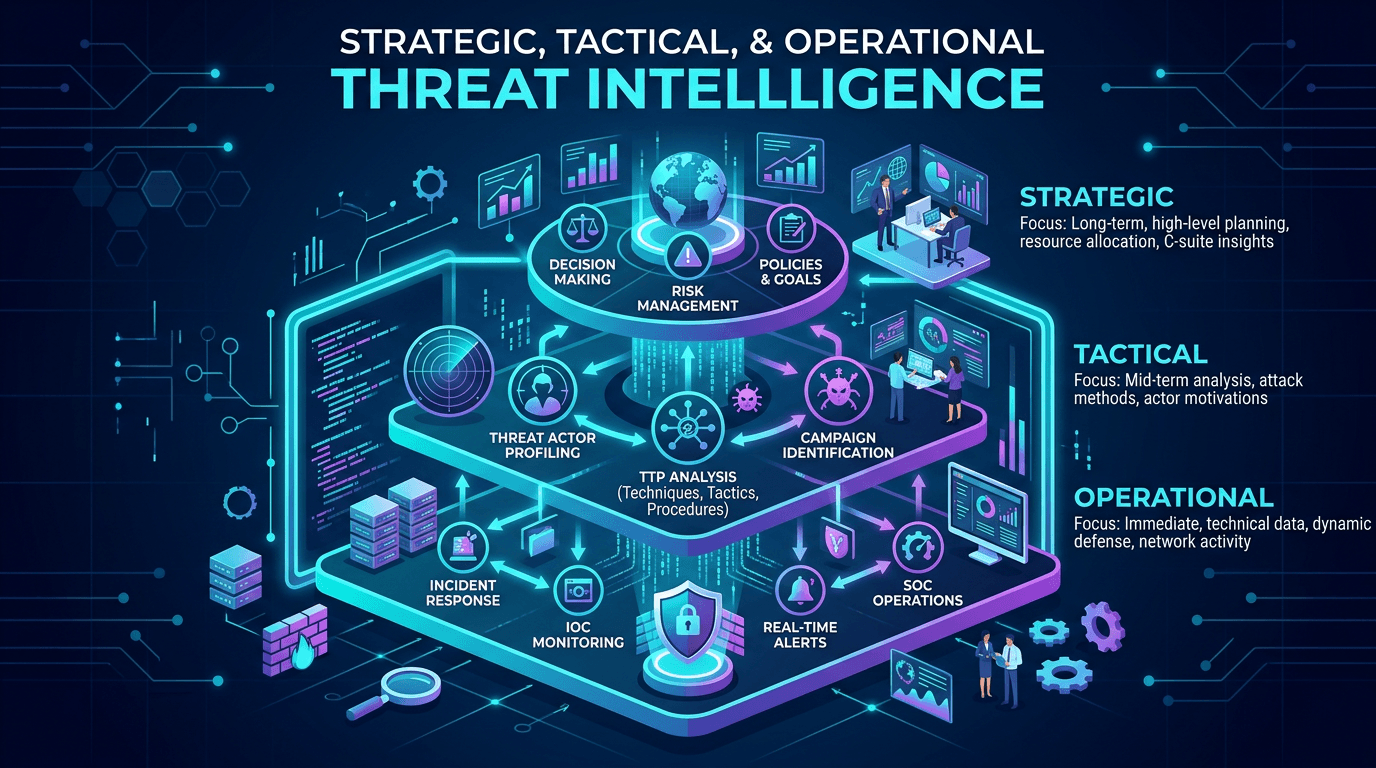
Strategic, Tactical, and Operational Threat Intelligence: Frameworks for Modern Security Programs
Align CTI outputs with audience needs: executive risk narratives, SOC-ready IOCs, and MITRE-mapped TTPs—plus governance models that keep intelligence timely and measurable.
OSINT for SOC Analysts: Turning Open Source Intelligence Into Threat intelligence analysts can use
A complete guide to open source intelligence (OSINT) for security operations—tools, techniques, workflows, and legal considerations for collecting, analyzing, and operationalizing open threat data in a modern SOC.
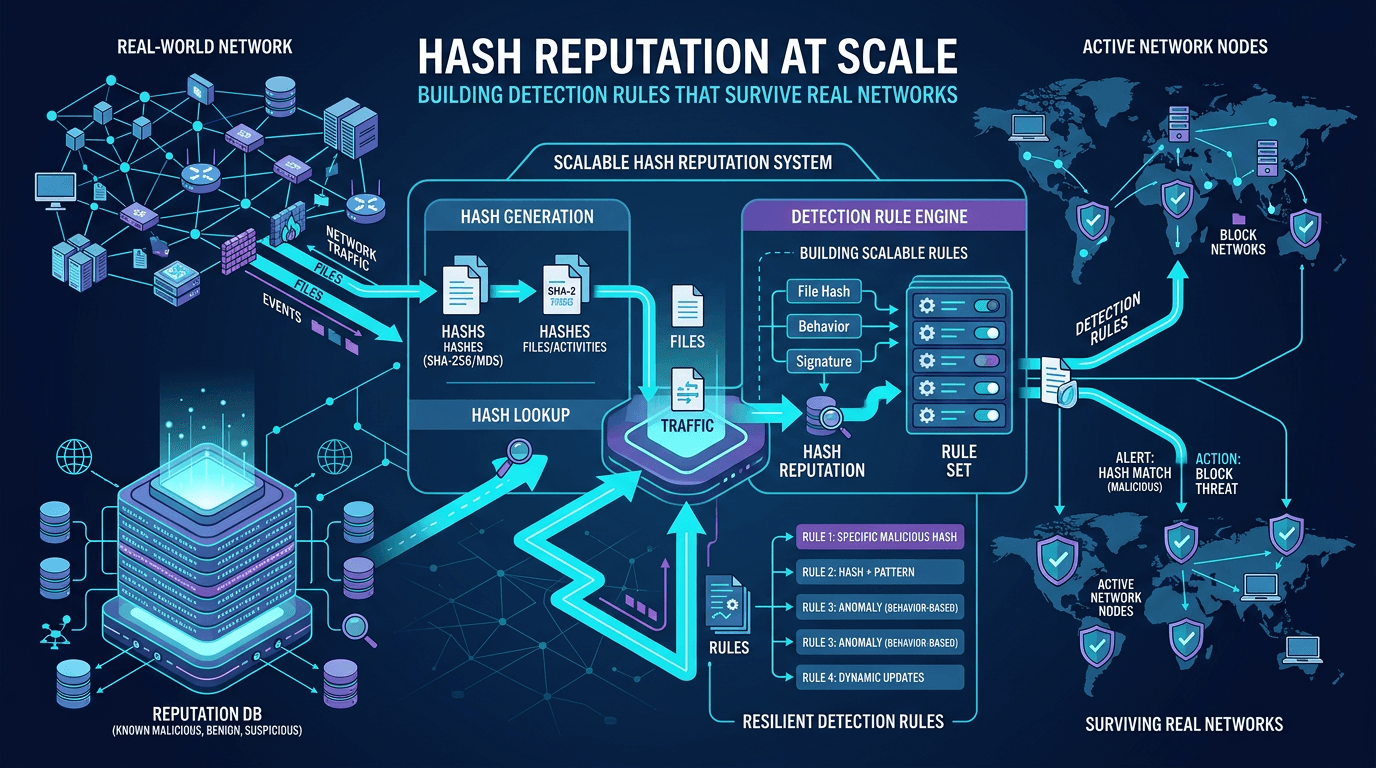
Hash Reputation at Scale: Building Detection Rules That Survive Real Networks
Move beyond one-off hash blocks: design reputation pipelines, reduce false positives, and integrate file intelligence with IP and domain context for production-ready detection engineering.
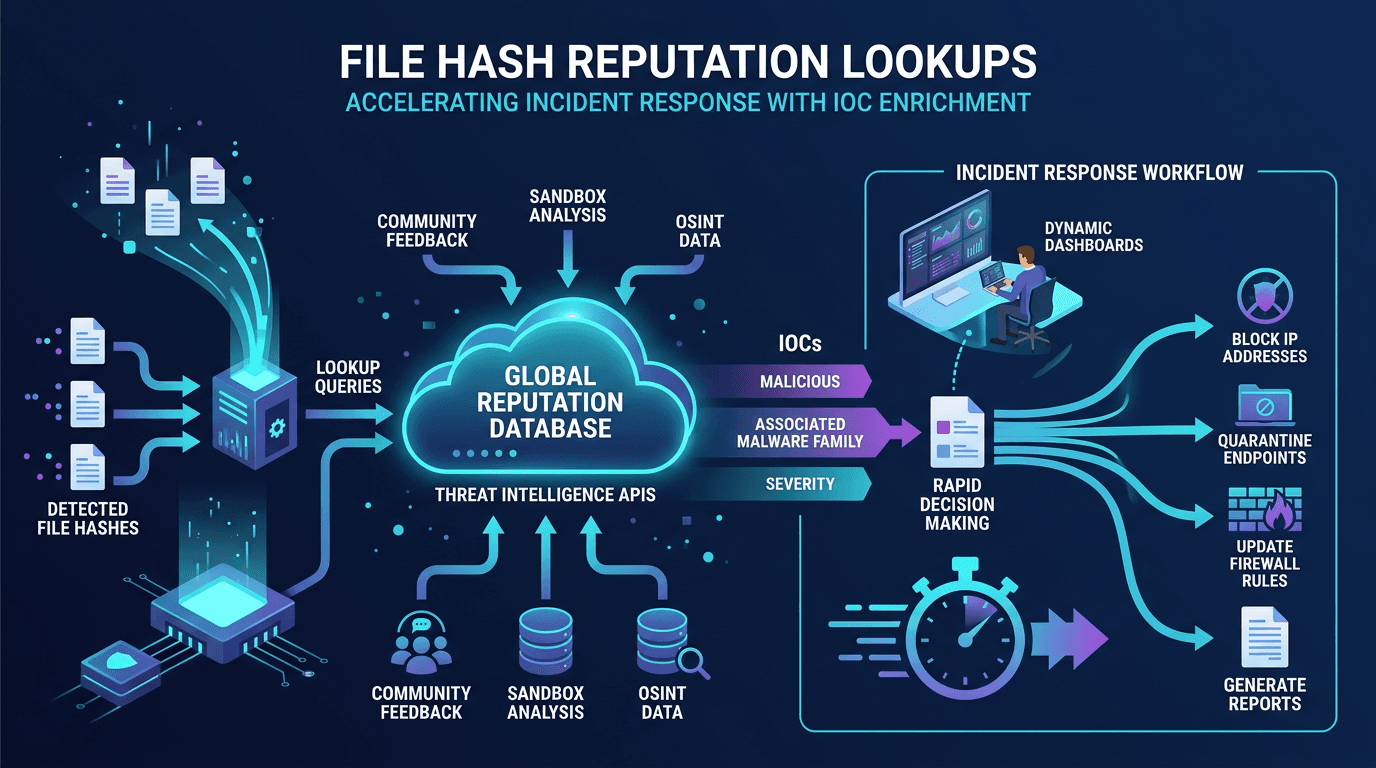
File Hash Reputation Lookups: Accelerating Incident Response With IOC Enrichment
A practitioner's guide to file hash reputation lookups—how they work, which data sources power them, how to build automated IOC enrichment pipelines, and how to integrate hash intelligence into SOC, SOAR, and incident response workflows.
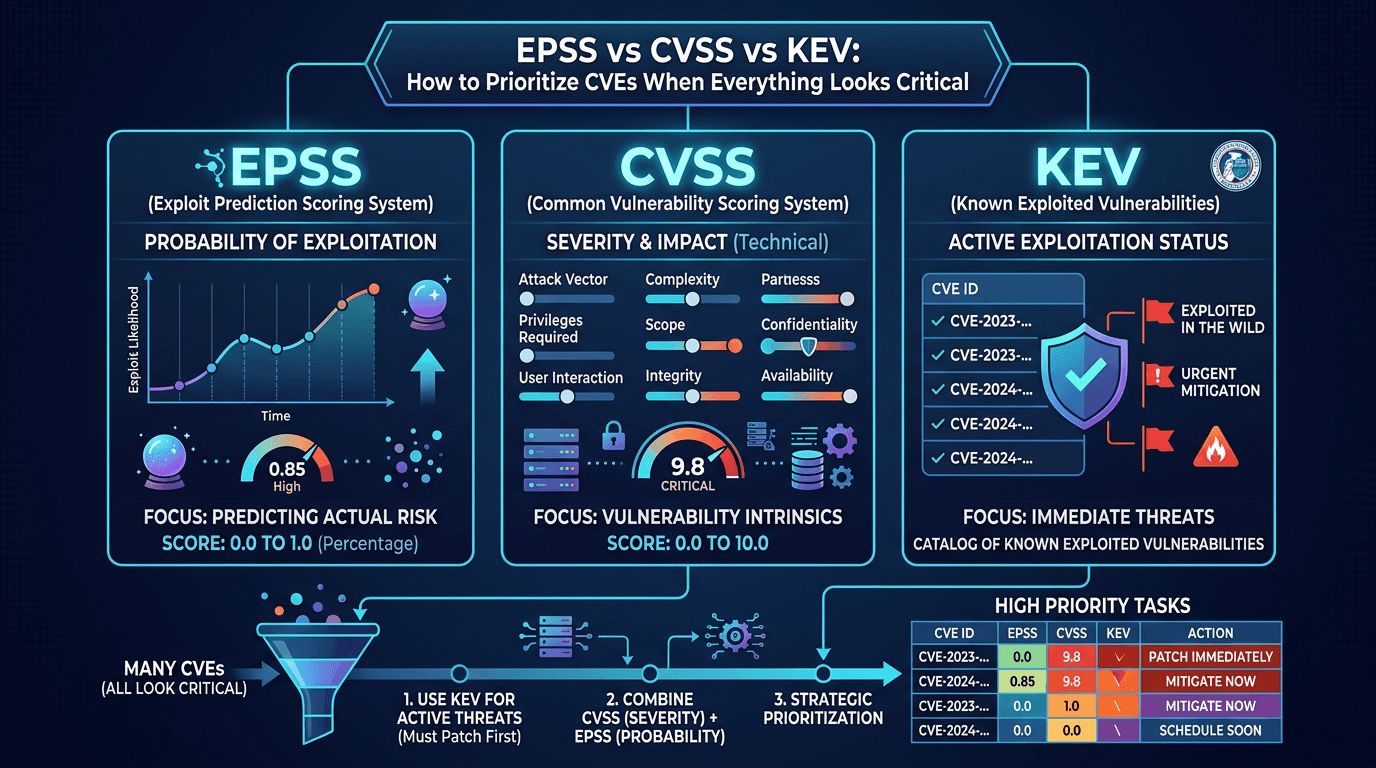
EPSS vs CVSS vs KEV: How to Prioritize CVEs When Everything Looks Critical
Cut through scoring confusion: compare CVSS severity, EPSS exploit probability, and CISA KEV active exploitation—and learn a practical model for patch and compensating-control decisions.
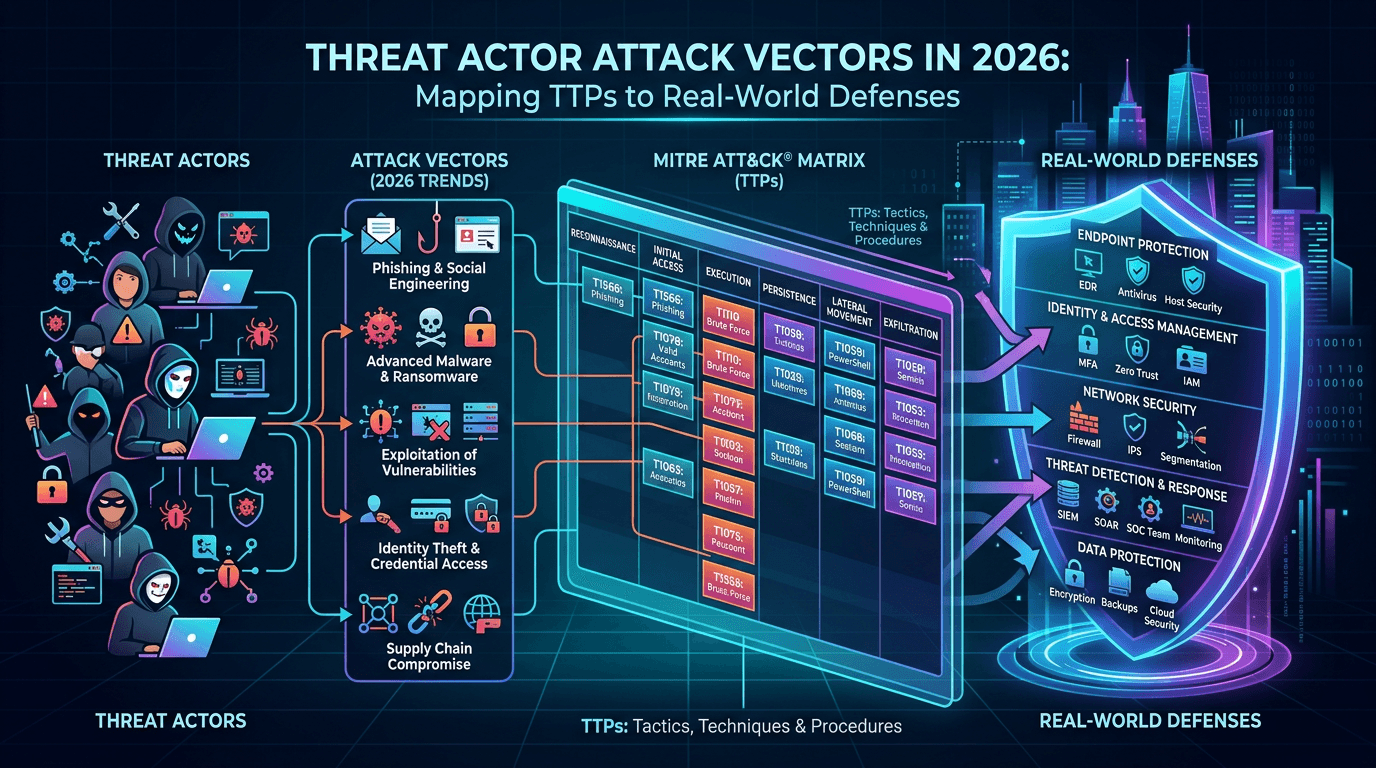
Threat Actor Attack Vectors in 2026: Mapping TTPs to Real-World Defenses
Explore how adversaries gain initial access, move laterally, and exfiltrate data—and how security teams map attack vectors to MITRE ATT&CK, detection engineering, and threat-informed defense.
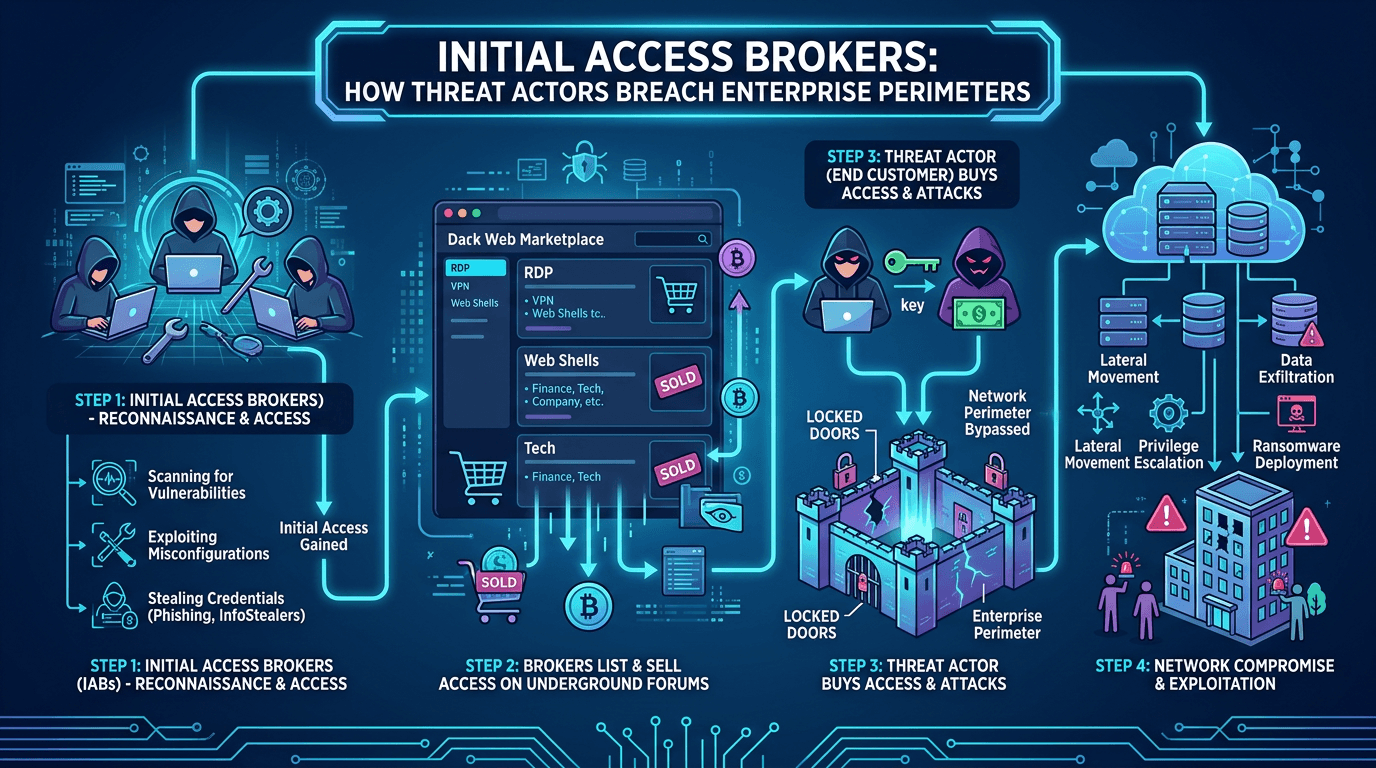
Initial Access Brokers: How Threat Actors Breach Enterprise Perimeters in 2026
A deep dive into initial access brokers (IABs)—the cybercrime specialists who sell footholds into corporate networks—covering their techniques, pricing, detection signals, and how to defend against the top attack vectors they exploit.
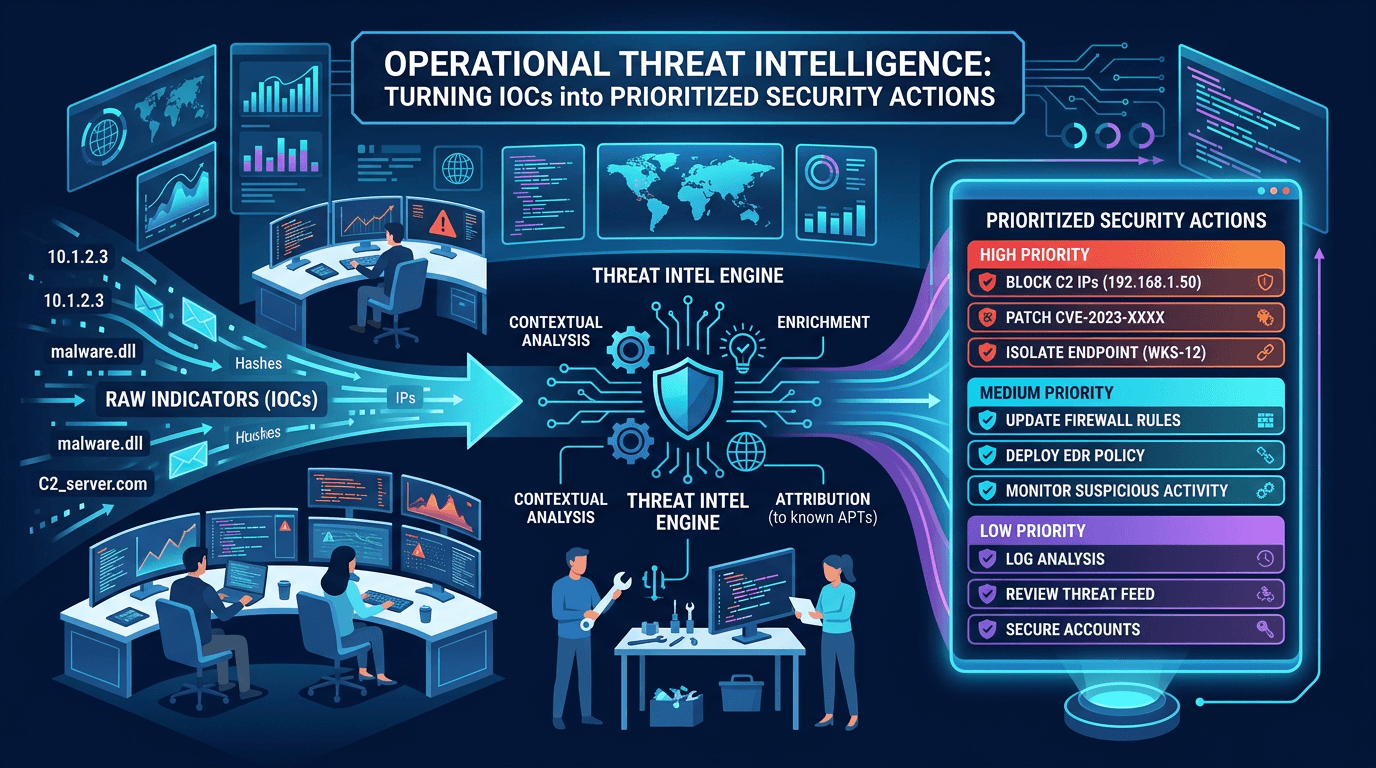
Operational Threat Intelligence: Turning IOCs into Prioritized Security Actions
Define operational CTI that SOC teams can use daily: IOC lifecycle, confidence scoring, feed hygiene, and how to align indicators with detection engineering and incident response.
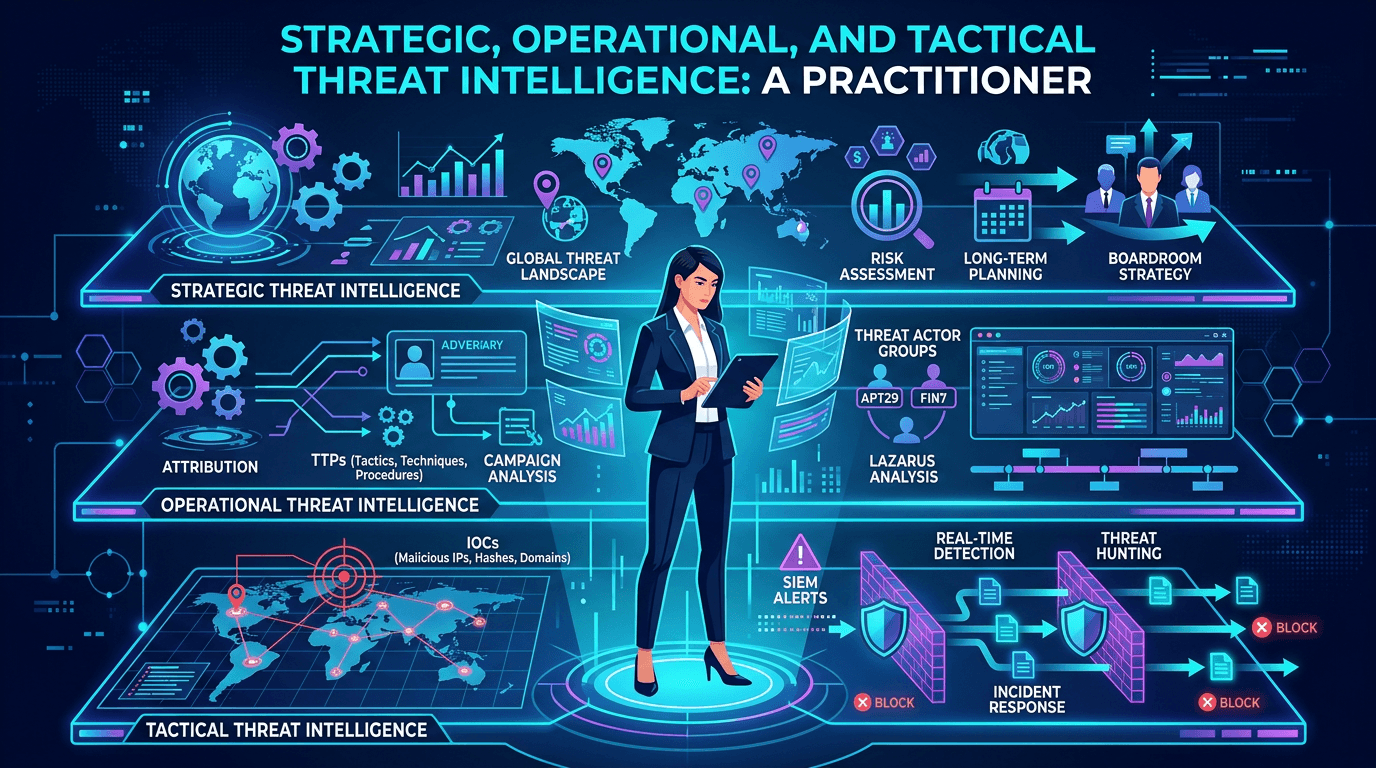
Strategic, Operational, and Tactical Threat Intelligence: A Practitioner's Framework for 2026
A complete guide to the three levels of threat intelligence—strategic, operational, and tactical—with practical examples of consumers, outputs, feeds, and how to connect them into a coherent CTI program.
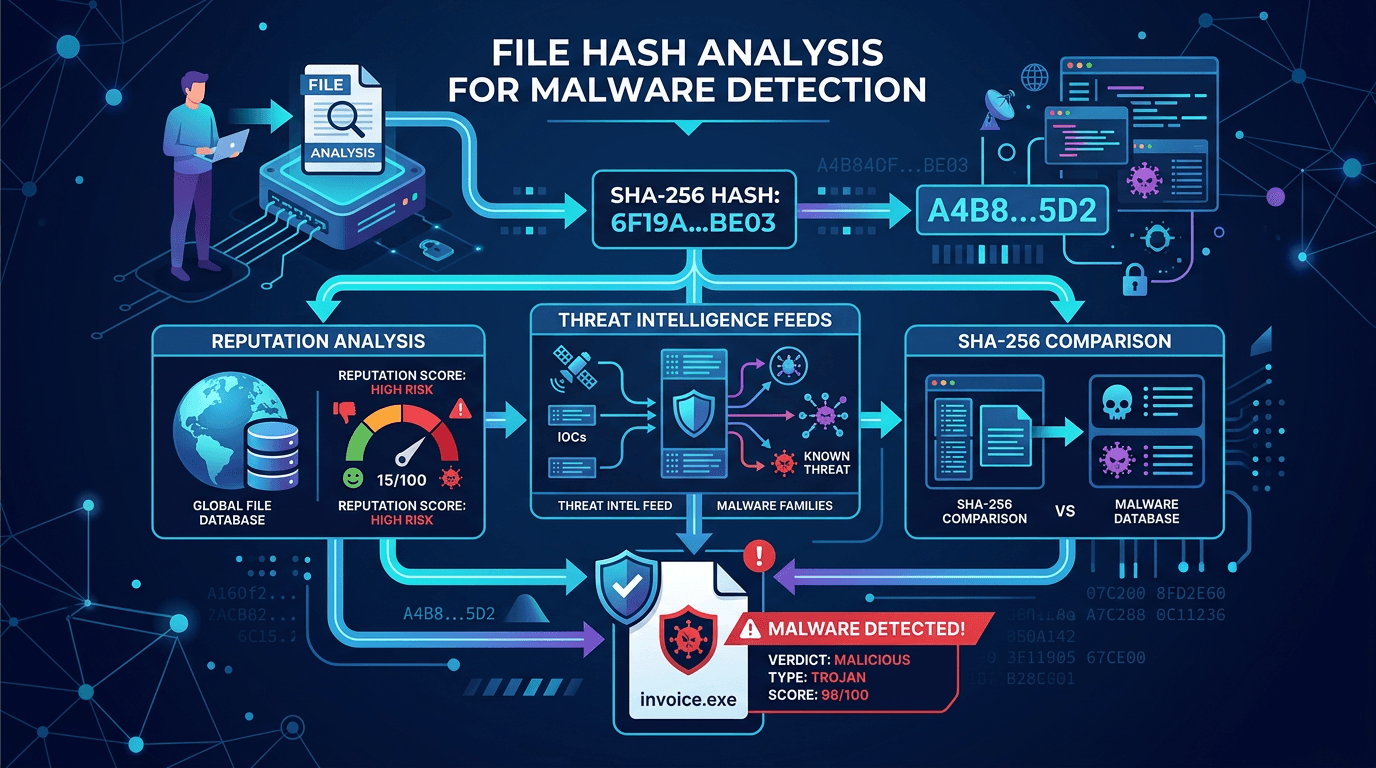
File Hash Check: Is This SHA-256 Malware?
How to check MD5, SHA-1, and SHA-256 hashes against threat intelligence, and how SOC teams use hash reputation to cut false positives.
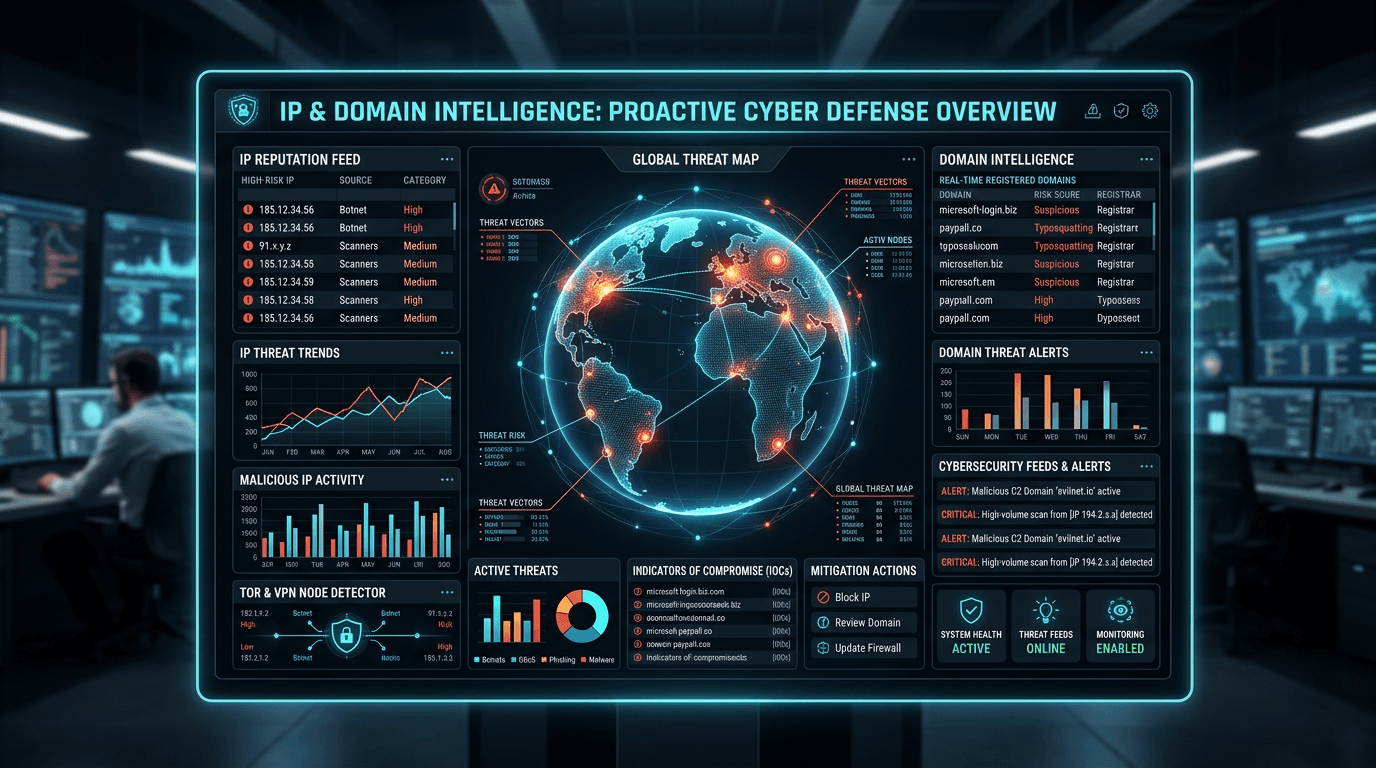
IP and Domain Intelligence: Building a Proactive Cyber Threat Defense
Reactive security leaves organizations perpetually one step behind attackers. Learn how combining IP and domain intelligence transforms your security posture from reactive incident response to proactive threat prevention that stops attacks before they start.
IP Lookup for Cyber Threat Detection: A Complete Security Guide
Learn how IP lookup works as a frontline defense against cyber threats. Discover how to use IP reputation data, threat intelligence feeds, and automated checks to block malicious actors before they reach your systems.