IPv6 Threat Intelligence: Reputation Beyond IPv4
Build IPv6 threat intelligence with correct normalization, prefix context, dual-stack logging, enrichment, and reputation decisions that avoid overblocking.
Fast-Flux DNS: Detect Rotating Attack Infrastructure
Learn how to detect fast-flux DNS using TTL, passive DNS, ASN diversity, reputation signals, and a repeatable SOC investigation workflow.

isMalicious vs Censys: Internet Discovery and Reputation Verdicts Are Different Jobs
Censys maps what exists on the internet — hosts, certificates, open ports. isMalicious assesses what is malicious. Most teams comparing the two need the second question answered, not the first.

isMalicious vs OpenCTI: Why This Is the Wrong Comparison (and How They Work Together)
OpenCTI is a threat intelligence platform and knowledge graph. isMalicious is a data provider that feeds it. Teams searching for an OpenCTI alternative usually need a feed, not a replacement TIP.

isMalicious vs Recorded Future: When a Threat Data API Makes More Sense Than an Enterprise Intel Program
Recorded Future delivers finished intelligence and analyst support at enterprise scale. isMalicious delivers self-serve enrichment and feeds without a sales cycle. The right choice depends on whether you need strategic reports or automated verdicts.

Firewall Blocklist Automation: Pulling IP and Domain Feeds Without Outages
External dynamic lists can block malware and phishing at the edge — or break payroll, CDN traffic, and vendor portals. This guide covers staged rollout, allowlists, fail-open vs fail-closed, and measuring hit rates for IP and domain blocklists.

How to Use an NRD Feed to Catch Phishing Before It Lands in the Inbox
Newly registered domains are where most phishing campaigns start. This guide walks through NRD feed workflows for brand monitoring, mail gateway hygiene, and SOC triage — without treating domain age as a blunt block rule.

CVE-2026-63077 Puts Unauthenticated RCE on Every TeamCity On-Premises Server
A deserialization flaw in the agent polling protocol gives attackers TeamCity server privileges without credentials. JetBrains patched in 2025.11.7 and 2026.1.3 — CISA KEV and a 3-day federal deadline mean hunt now, not after the next release train.
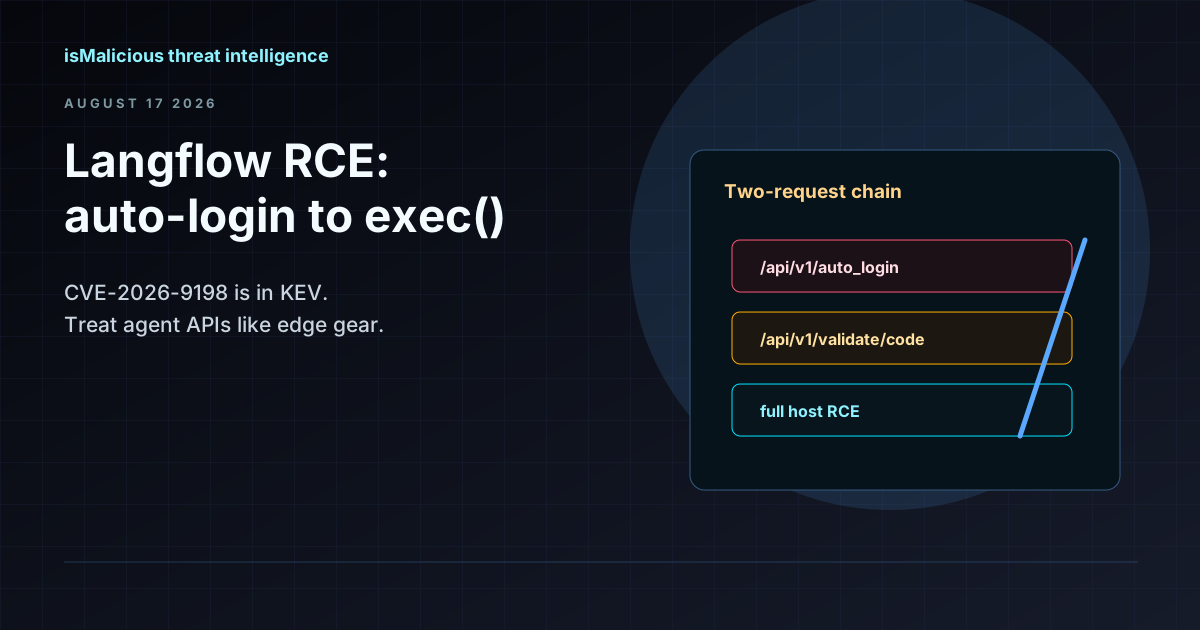
CVE-2026-9198 Gives Unauthenticated RCE in IBM Langflow OSS Agent Control Planes
A SUPERUSER token minted through /api/v1/auto_login chains with Python exec() in /api/v1/validate/code. Langflow 1.10.1 fixes the flaw — but internet-exposed instances need hunting now, not after the next sprint.
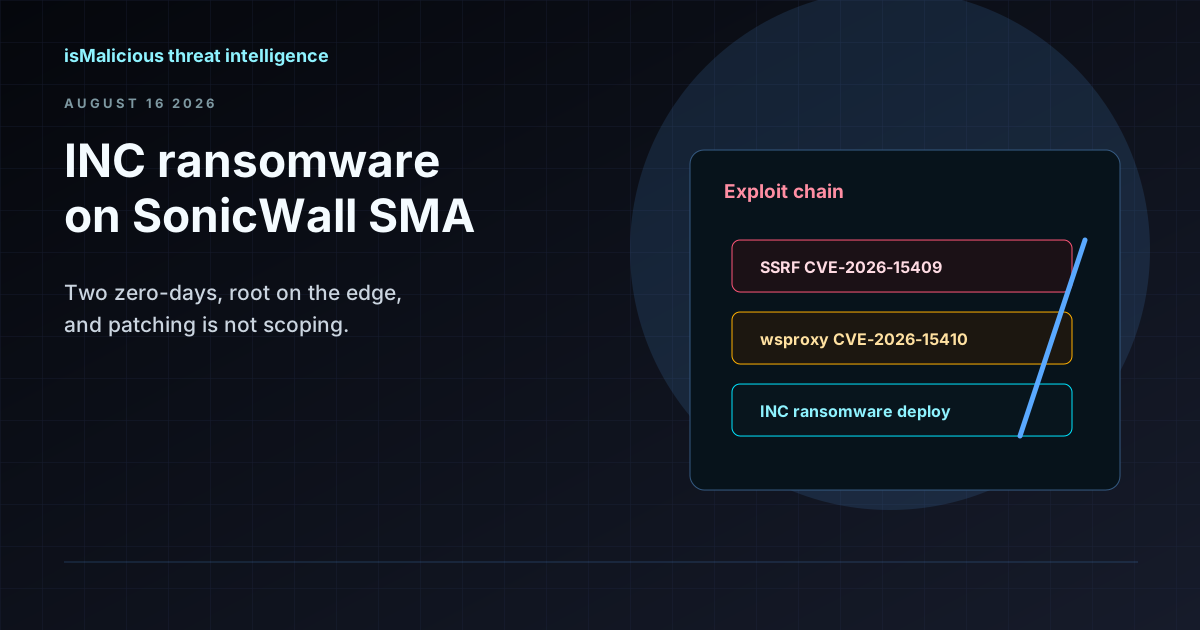
INC Ransomware Chains Two SonicWall SMA Zero-Days (CVE-2026-15409, CVE-2026-15410)
INC affiliates are weaponizing an SSRF and a post-authentication code injection in SonicWall SMA 1000 to reach internal networks. Exploitation started weeks before the July 14 patch — here is how to hunt and triage.
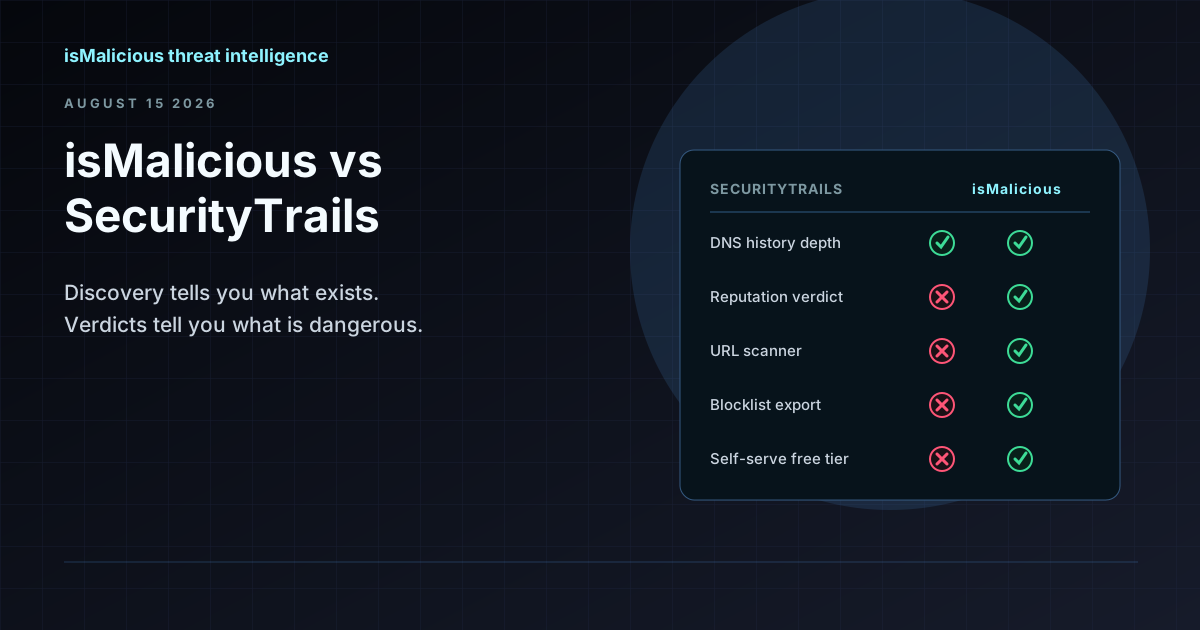
isMalicious vs SecurityTrails: Discovery Data and Reputation Verdicts Are Not the Same Product
SecurityTrails tells you what exists — every subdomain, every historical DNS record. isMalicious tells you what is dangerous. Most teams searching for a SecurityTrails alternative want the second half.
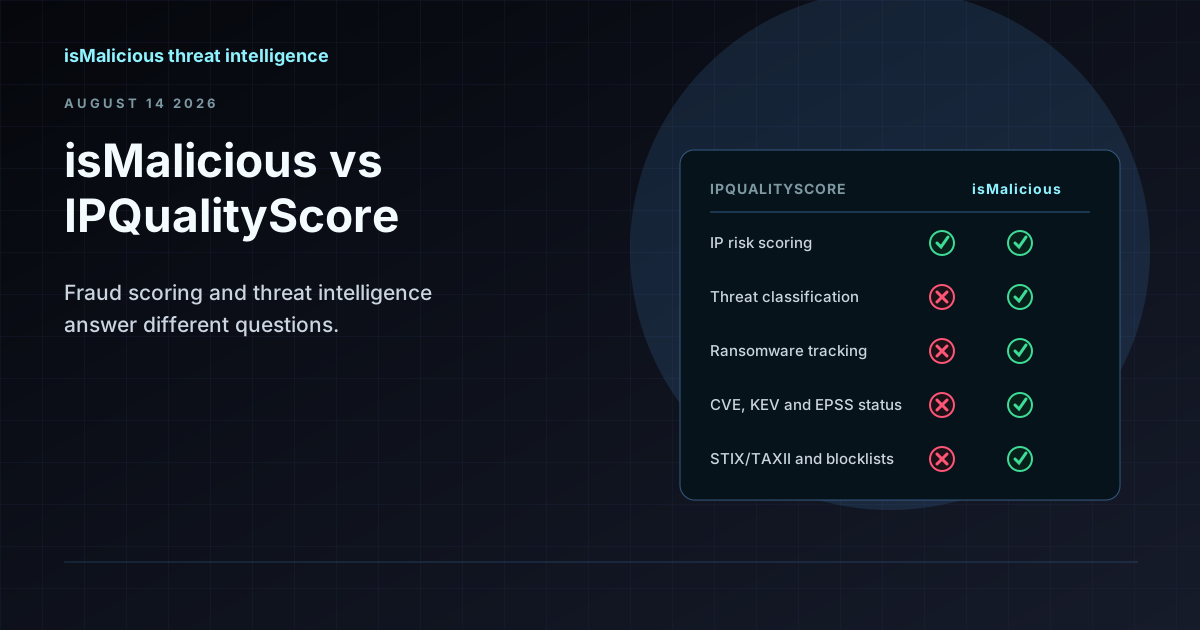
isMalicious vs IPQualityScore: Fraud Scoring and Threat Intelligence Are Different Jobs
IPQS scores whether a signup is fraudulent. isMalicious scores whether infrastructure is malicious. The two get compared constantly because both return a number about an IP address — and they answer different questions.

isMalicious vs MISP: Why This Is the Wrong Comparison (and What to Compare Instead)
MISP is where you store and share indicators. isMalicious is where indicators come from. Teams searching for a MISP alternative are usually looking for a feed, not a replacement platform.
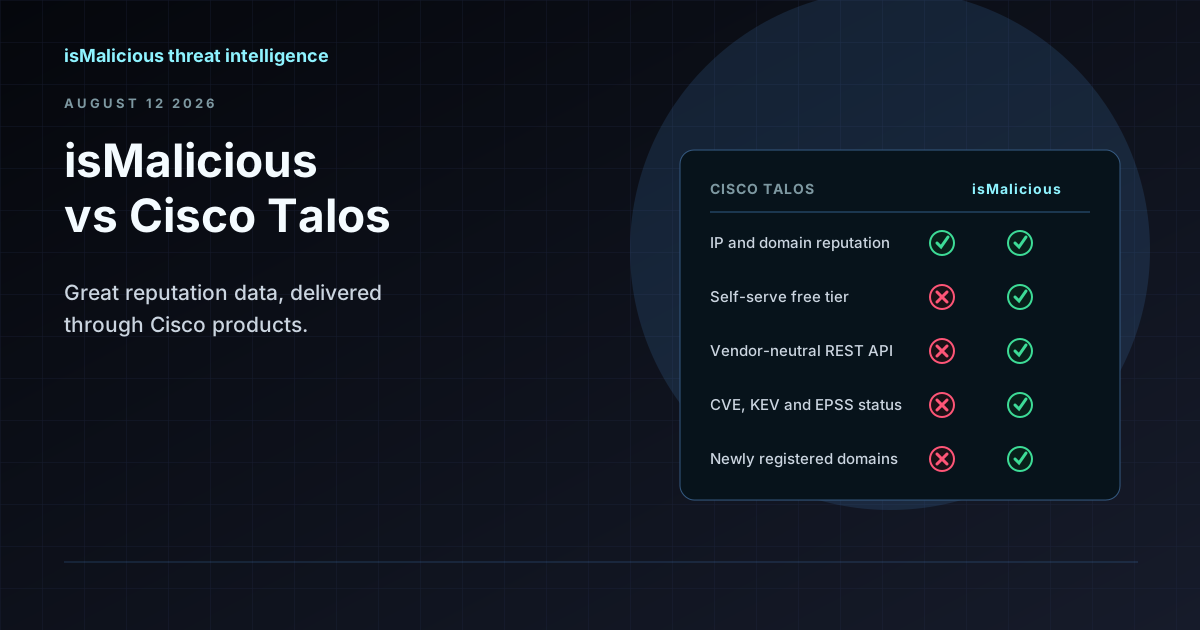
isMalicious vs Cisco Talos: Reputation Lookups Outside the Cisco Stack
Talos reputation is excellent and it lives inside Cisco products. If your stack is not Cisco, or you need an API rather than a web form, that is where the comparison starts.
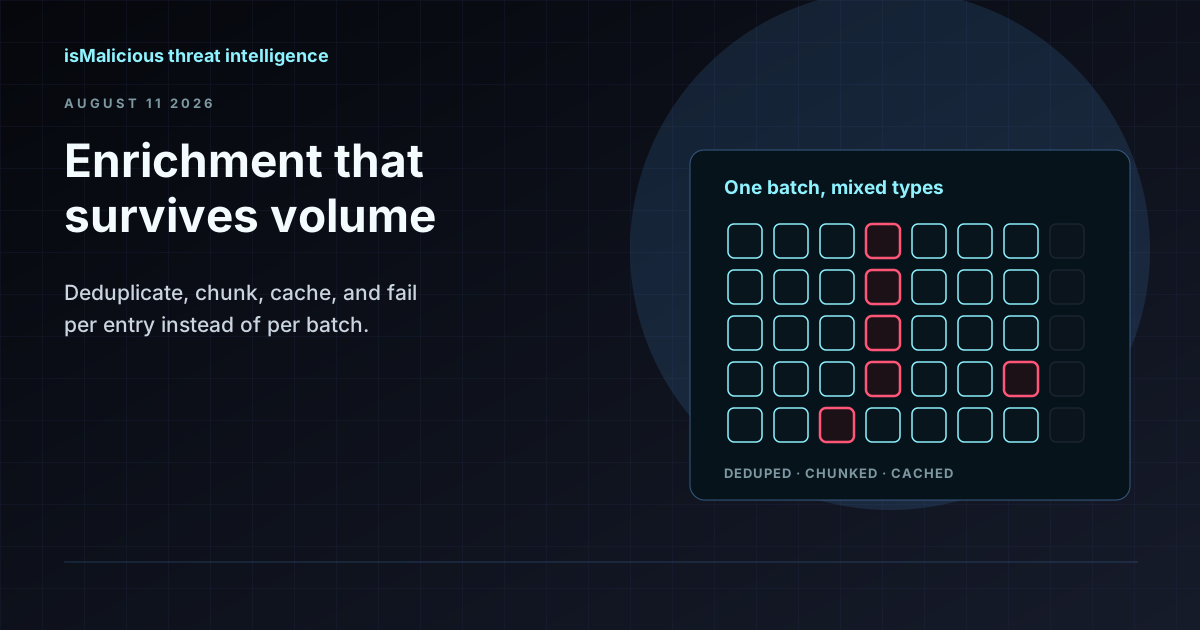
Bulk IP and Domain Lookups: Designing Indicator Enrichment That Survives Real Volume
One incident produces hundreds of indicators, and per-indicator lookups are where triage stalls. Here is how to build a batch enrichment pipeline that respects quotas, deduplicates properly, and fails gracefully.
Reverse IP Lookup: Pivoting on Infrastructure Without Drowning in Shared Hosting
A reverse IP lookup turns one indicator into a cluster — or into a thousand innocent neighbours. Here is how to tell the difference, and how to pivot on hosting infrastructure without generating false positives.
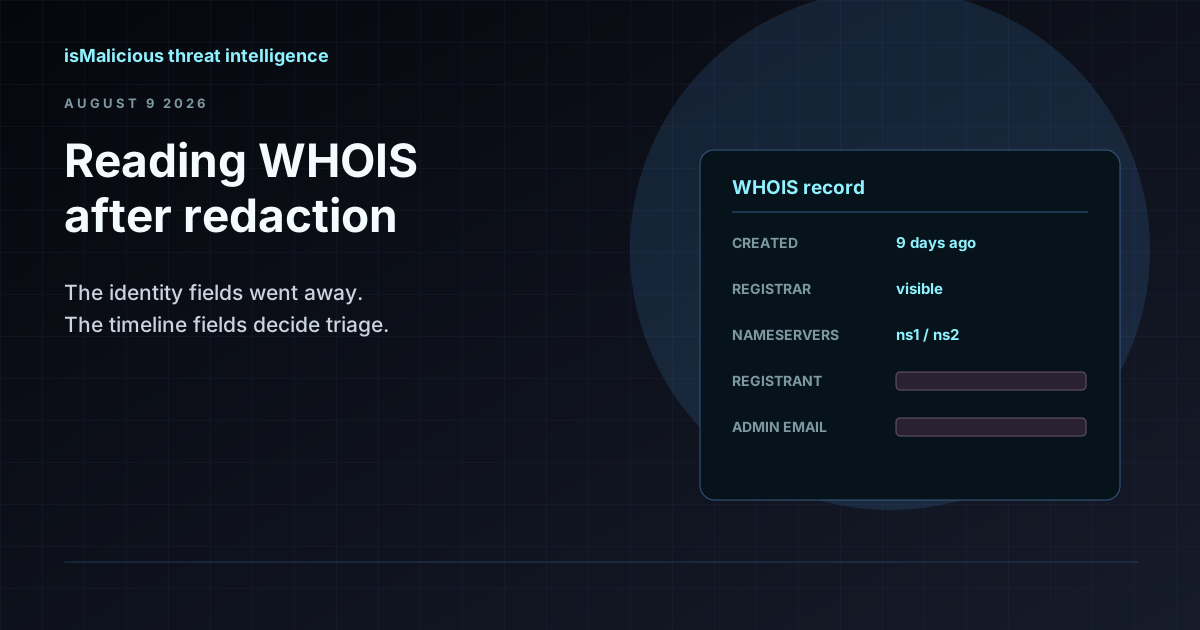
WHOIS Lookup for Security Investigations: Reading a Record After Redaction
Privacy services stripped the registrant name out of most WHOIS records, but the fields that matter for triage survived. Here is what a WHOIS record still tells an analyst, and how to read it.
The Kratos Phishing Kit Takedown: 200 Servers Gone, 1,800 Copies Still Out There
German and US law enforcement dismantled Kratos, the AiTM phishing service behind roughly 15,000 Microsoft 365 campaigns a month. The infrastructure is offline, but the kit is not. Here is what to hunt for now.
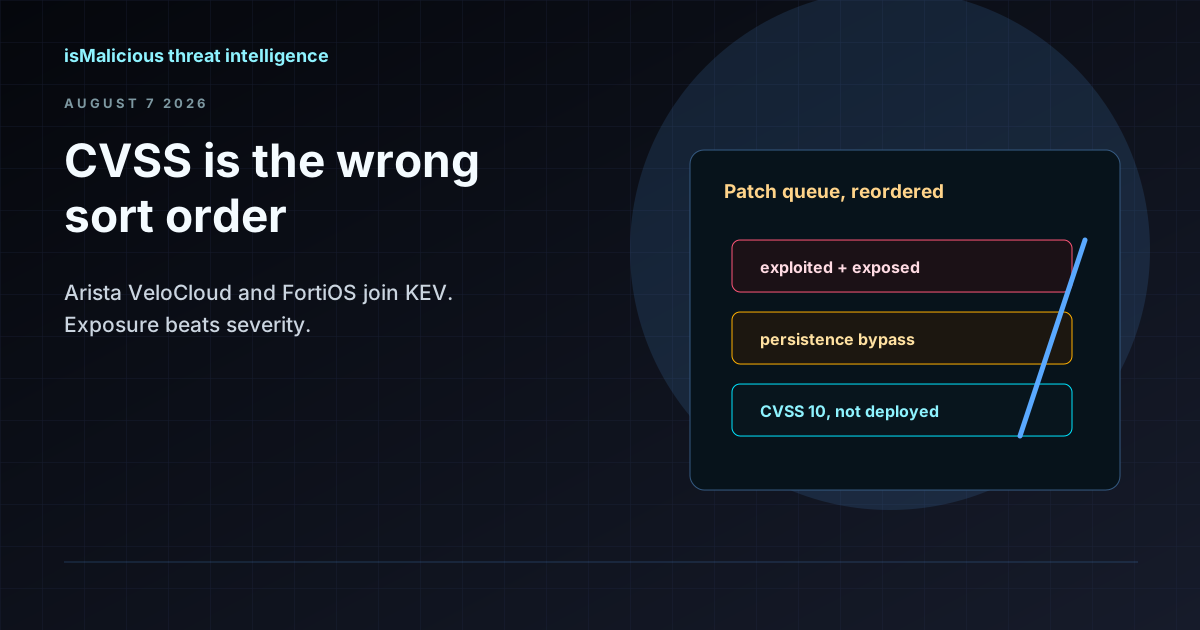
CISA KEV Adds Arista VeloCloud and FortiOS Flaws: Why CVSS Is the Wrong Sort Order
On 27 July 2026 CISA added a CVSS 10.0 command injection in Arista VeloCloud Orchestrator and a medium-severity FortiOS patch bypass to KEV. The pairing shows why exposure and persistence beat severity when ordering a patch queue.
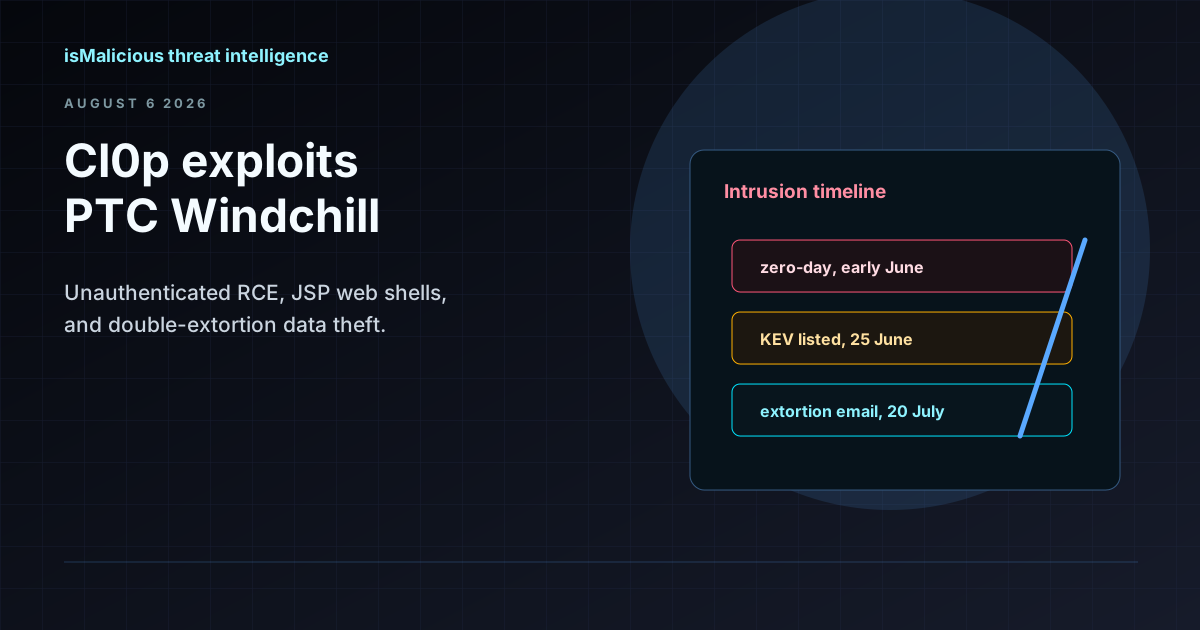
Cl0p Is Exploiting PTC Windchill (CVE-2026-12569) to Steal Engineering Data
A Cl0p affiliate is chaining a FlexPLM information disclosure with an unauthenticated RCE in PTC Windchill to plant JSP web shells and run double-extortion data theft. Here are the detection signals and the triage workflow.
GitHub Actions and CI/CD Pipeline Compromise: A Growing Supply Chain Attack Vector
CI/CD pipeline compromises keep recurring across GitHub Actions ecosystems. Learn the detection signals, hardening steps, and enrichment workflow security teams need.
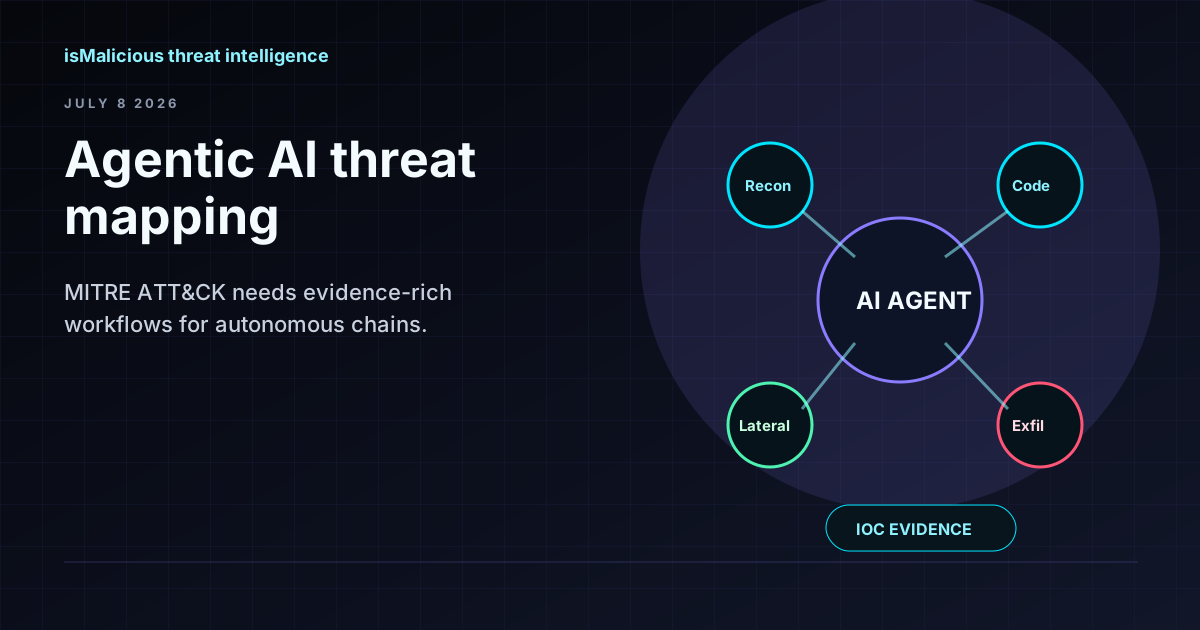
Agentic AI Threat Mapping: MITRE ATT&CK Needs Evidence-Rich Workflows
Anthropic mapped AI-enabled cyber activity to MITRE ATT&CK and found gaps around autonomous orchestration. SOC teams need AI summaries tied to evidence, not unsupported verdicts.
AI-Enabled Cyberattacks and MITRE ATT&CK: Turning New Threat Maps Into SOC Action
AI-enabled threats are being mapped into ATT&CK language, but mapping is only useful when it drives enrichment, detection, triage, and response workflows.
SOC Alert Fatigue: How Threat Intelligence Reduces False Positives Without Hiding Real Attacks
Alert fatigue is not a staffing problem alone. SOC teams need better evidence, source quality, confidence bands, and enrichment workflows that turn noisy alerts into defensible decisions.