isMalicious + Tenzir: Threat Intel in Your Pipeline
Connect isMalicious domain and IP feeds to Tenzir over STIX/TAXII for local DNS and network enrichment, with optional API lookups for investigations.
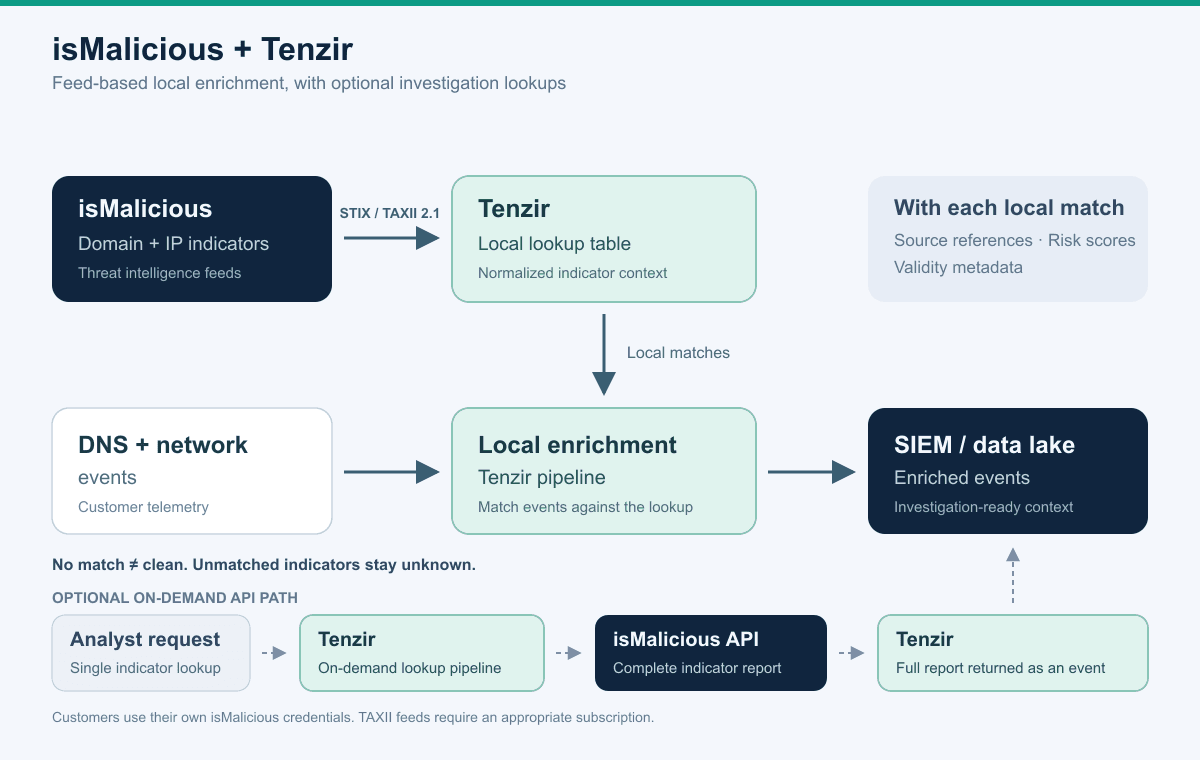
Bring threat intelligence into your security data pipeline with isMalicious and Tenzir.
Load domain and IP indicators over STIX/TAXII, build a local lookup table in Tenzir, and enrich DNS and network events on their way to your SIEM or data lake. Keep source references, risk scores and validity metadata with the matches. Use an optional API lookup when an investigation needs more context.
Unmatched indicators remain unknown.
Use your own isMalicious credentials. TAXII feed access requires an appropriate paid subscription; creating a free account alone does not enable the feeds.
TAXII collection pulls are subject to your plan's per-minute burst limit but do not consume the monthly reputation-check quota. Optional individual API lookups consume that monthly quota.
isMalicious is built by founder and developer Jean-Vincent QUILICHINI. You can also find him on X as @hexablob.
See Tenzir on our partners page and the solution brief.
Related articles
 TAXII Threat Feeds: Build a Continuous SIEM Integration
Connect an isMalicious TAXII collection to your SIEM with safe pagination, durable checkpoints, validation, monitoring, and recovery.
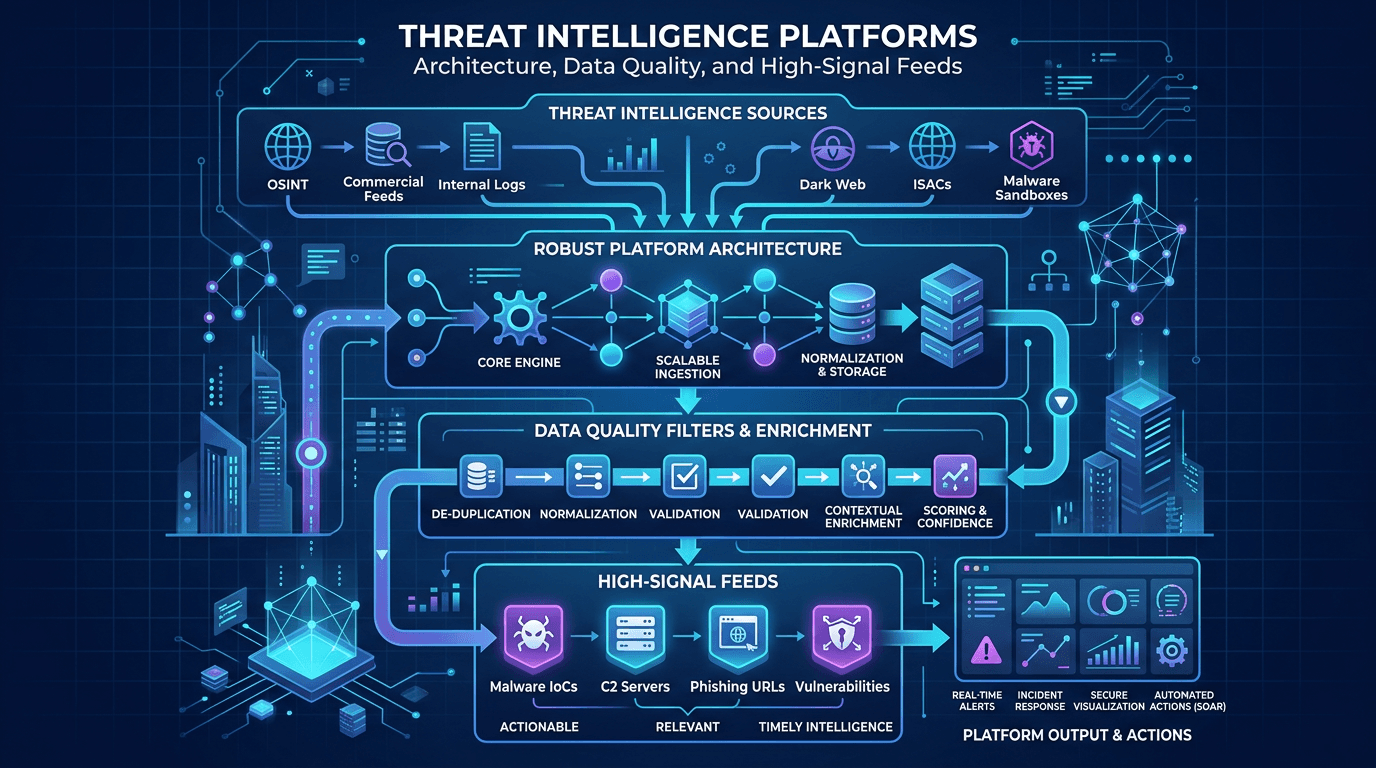 Threat Intelligence Platforms: Architecture, Data Quality, and High-Signal Feeds
Design TIPs and intel pipelines that scale: normalization, confidence scoring, deduplication, API-first delivery, and how to pair platform investments with analyst workflows.
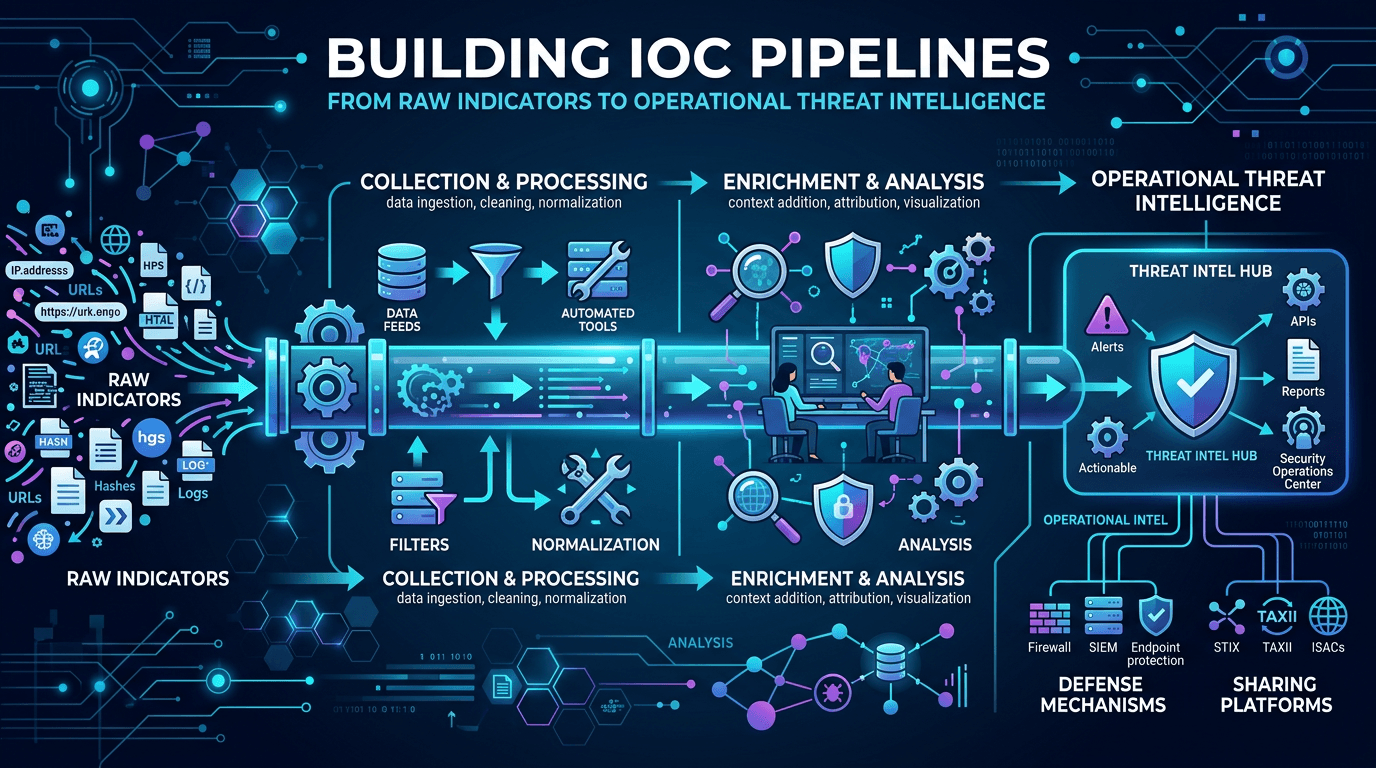 Building IOC Pipelines: From Raw Indicators to Operational Threat Intelligence in 2026
A practical engineering guide to building indicator of compromise (IOC) pipelines—ingestion, normalization, deduplication, enrichment, scoring, distribution, and feedback—to turn raw threat feeds into operational defense.
Check any IP or domain
See what our indexed threat intelligence records say about it.
Try the IP / Domain Checker