Threat Intelligence Blog
Research, insights, and updates from the isMalicious team.


Local Government Network Security: A 90-Day Council Plan
Build a council network security plan around public services, clear ownership, tested segmentation and useful logs, with practical actions across 90 days.

Public Sector Supplier Remote Access: Control Every Session
Control supplier remote access with named identities, agreed work windows, bounded paths and verified revocation, using a practical public sector example.
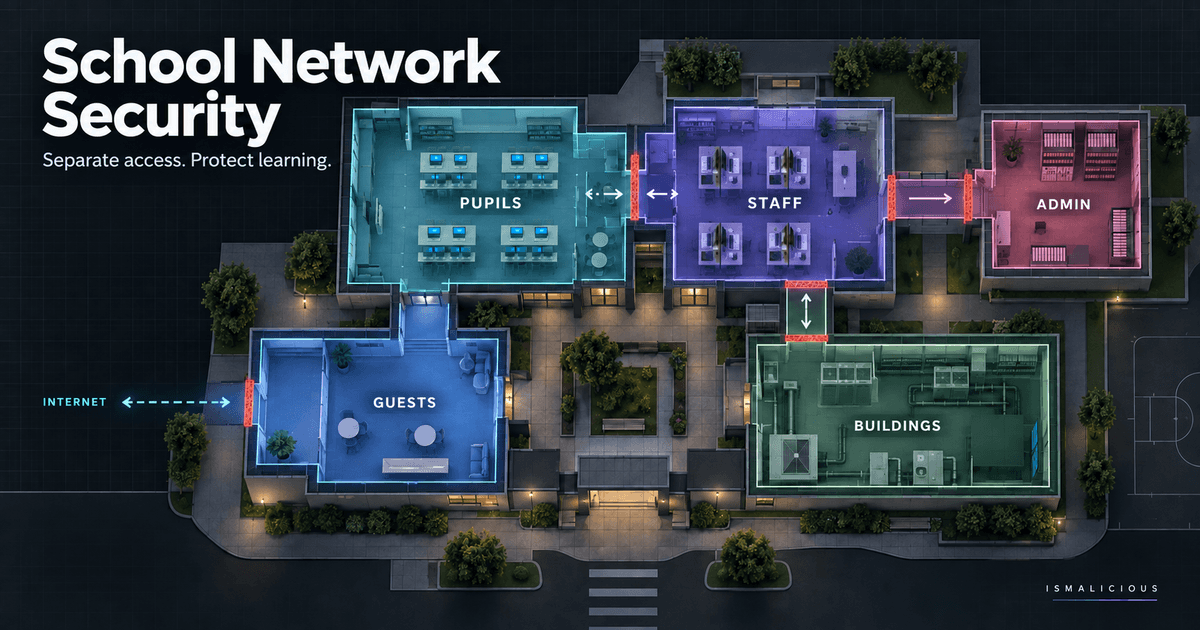
School Network Security: Test Segmentation That Works
Plan school network segmentation around teaching needs, test permitted and blocked paths, protect administration, and manage changes without losing access.
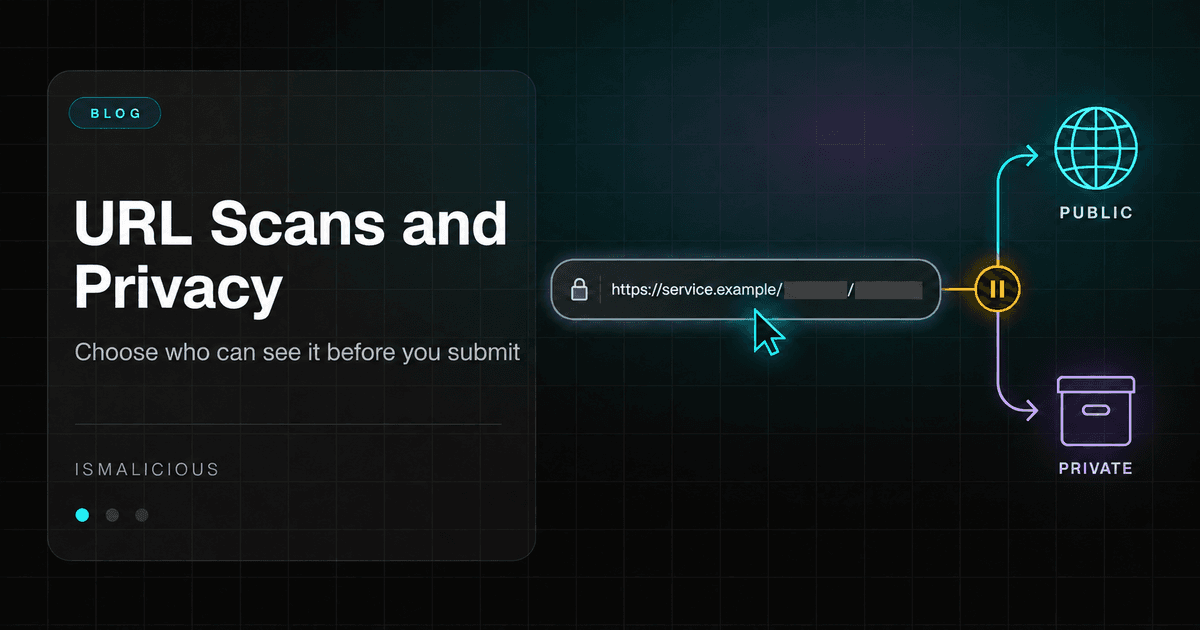
CTI Analyst OPSEC: Scan URLs Without Exposing Secrets
Protect CTI investigations before scanning URLs or files: assess public visibility, signed links, hash lookups, and the right environment for sensitive evidence.
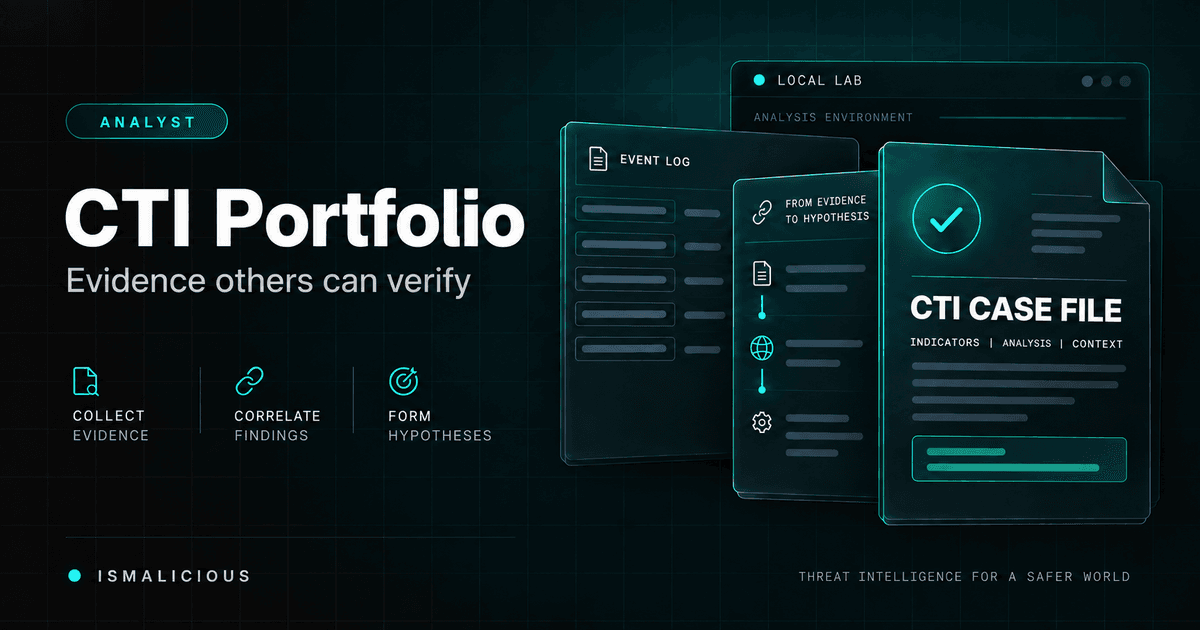
CTI Analyst Portfolio: Build a Safe, Reproducible Lab
Build a CTI analyst portfolio with offline datasets, evidence-led assessments, reproducible results, and a review rubric that shows how you make decisions.
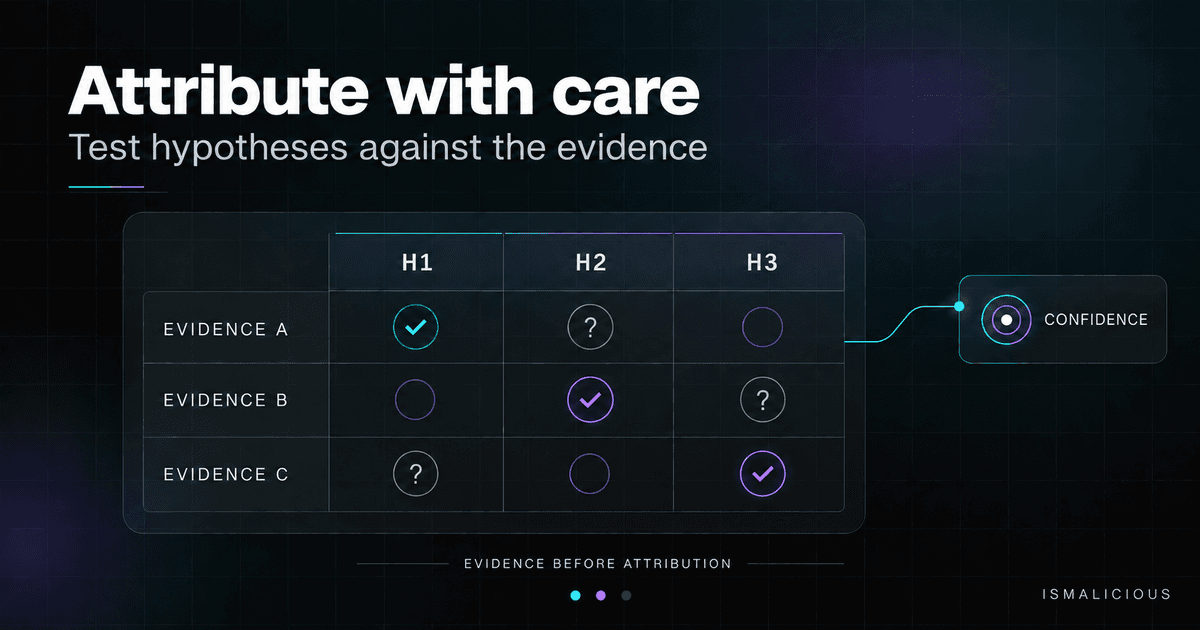
Cyber Attribution: Confidence and Competing Hypotheses
Assess cyber attribution with evidence, competing hypotheses, and explicit confidence. Use a practical judgment record without treating an IOC as an identity.
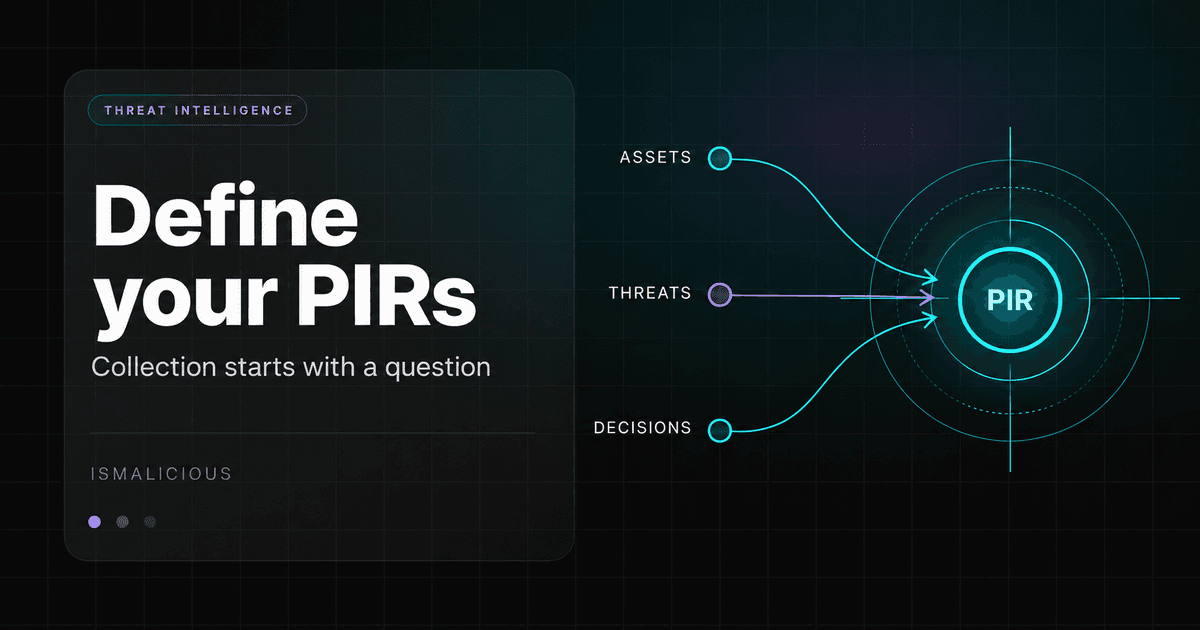
Threat Intelligence PIRs: A Workbook and Collection Plan
Turn threat intelligence requests into useful PIRs with a decision worksheet, collection plan, evidence requirements, ownership, and practical stopping rules.
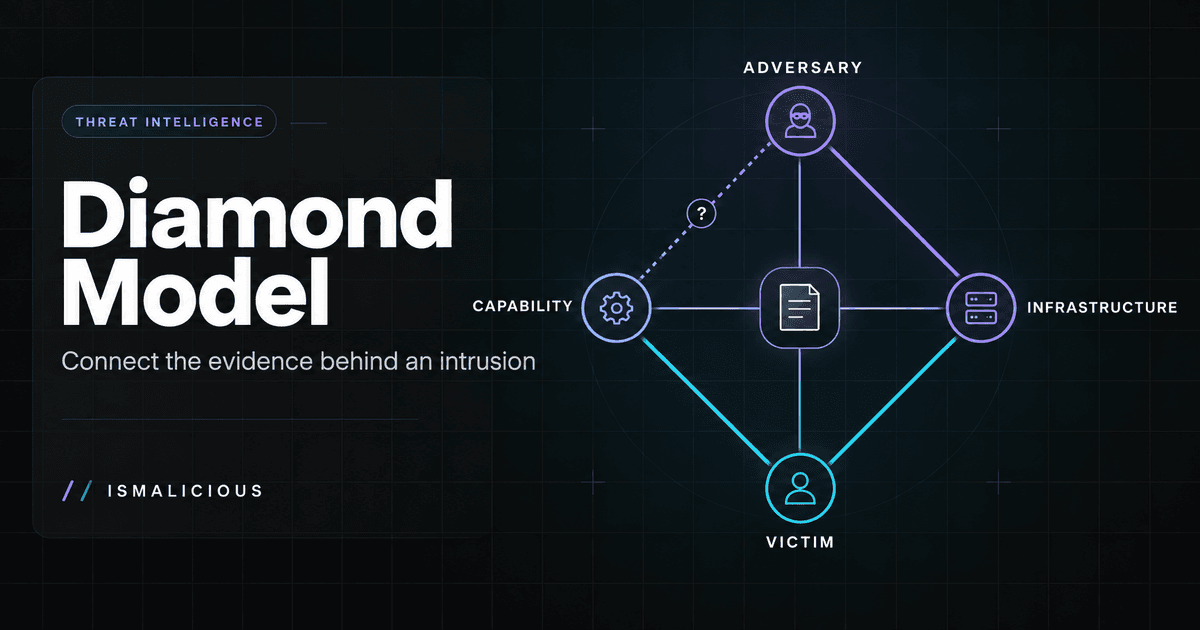
Diamond Model: A Practical CTI Investigation Walkthrough
Use the Diamond Model to connect evidence, test competing explanations, build activity threads, and turn a phishing investigation into defensible decisions.
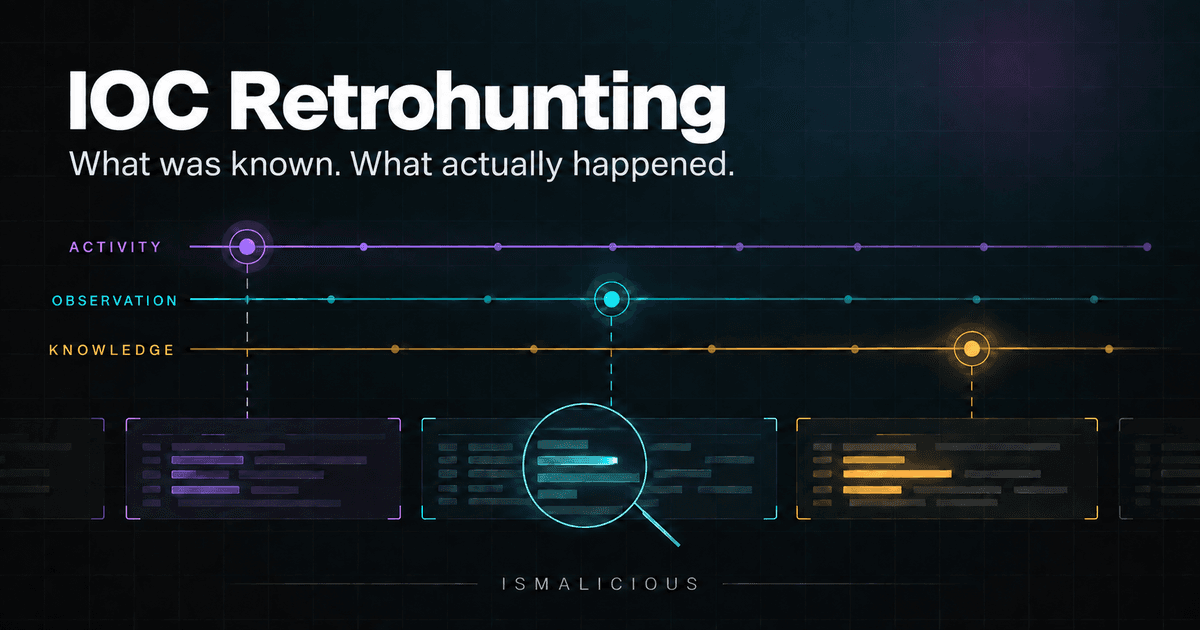
IOC Retrohunting: Investigating Historical Logs Reliably
Run reliable IOC retrohunts by separating event time, intelligence availability, and validity, then document historical evidence and the limits of negative results.
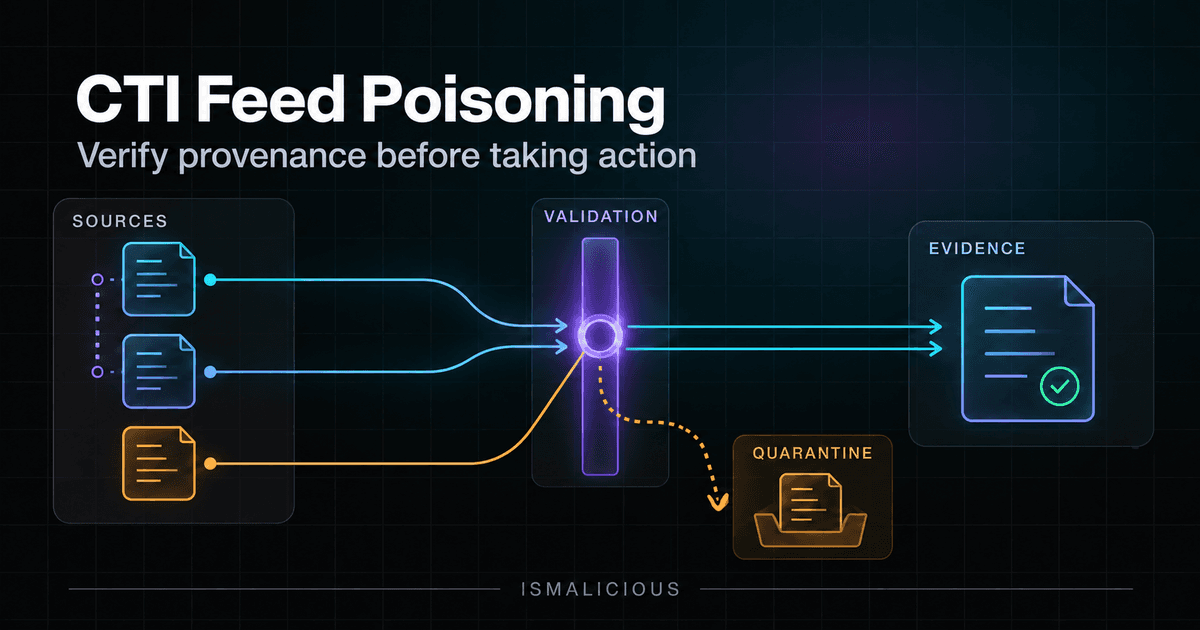
Threat Intelligence Feed Poisoning: Protect Your Evidence
Protect CTI decisions from misleading data with source provenance, mirror detection, contradiction handling, safe ingestion, human review, and tested rollback.
Threat Intelligence Feed ROI: Build a Reliable Benchmark
Evaluate threat intelligence feeds with an independent sample, complete operating costs, and a measure of incremental value before buying or renewing a contract.
Threat Intelligence Reports for Executives: A Practical Template
Write a CTI brief executives can use: the required decision, business impact, evidence, uncertainties, options, and follow-up, with a template and worked example.
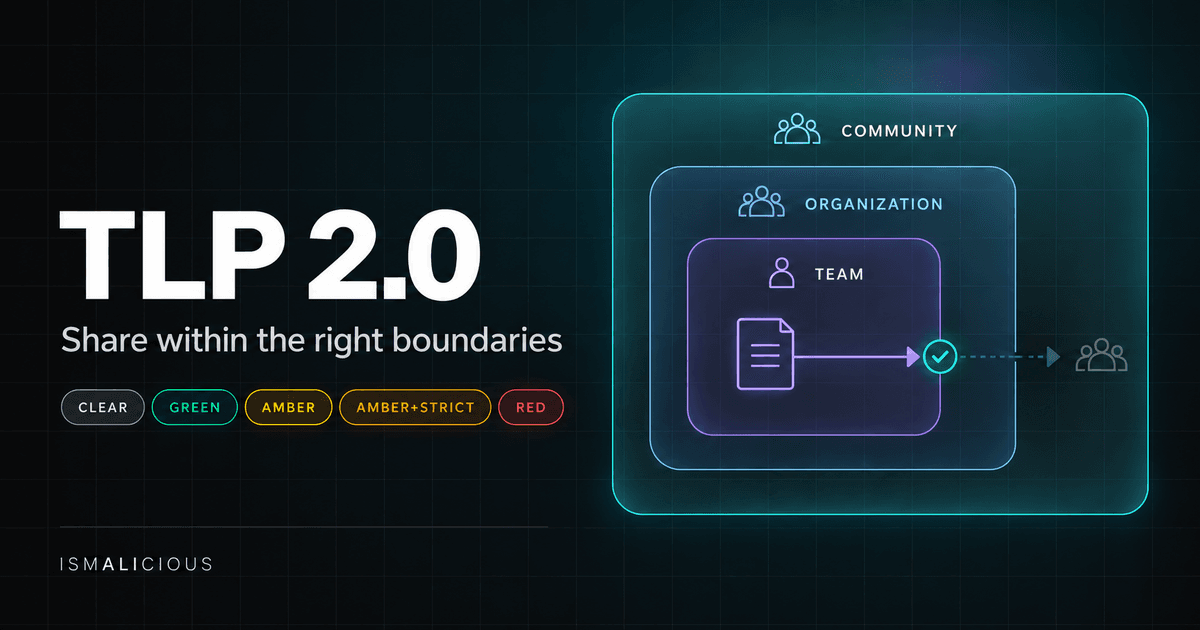
TLP 2.0: Share Threat Intelligence Without Leaking Data
Apply TLP 2.0 to CTI reports, indicators, and supplier exchanges with practical sharing boundaries, permission checks, data minimization, and export controls.
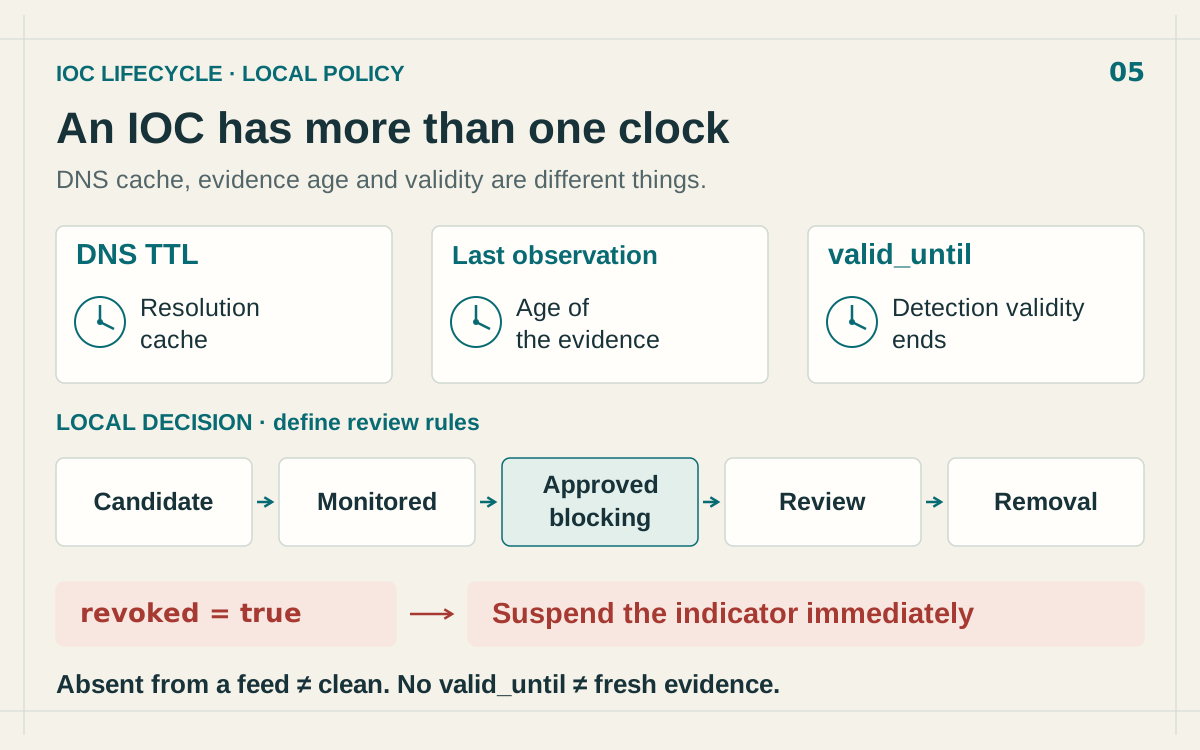
IOC Expiration: When to Remove an IP From a Blocklist
Manage IOC expiration with separate DNS, evidence and STIX validity clocks. Review stale IP blocks, process withdrawals and preserve the audit trail.
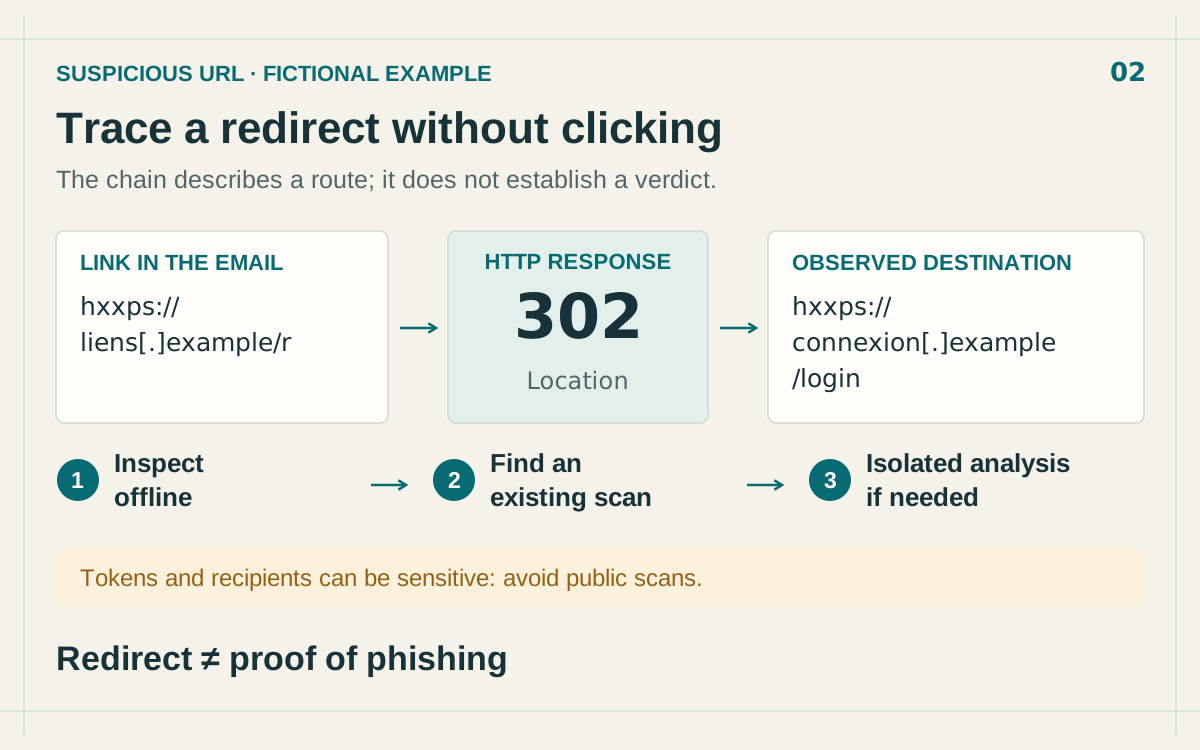
Suspicious URL? Check Redirects Without Opening It
Inspect a suspicious link, find previously observed redirects and protect private tokens before deciding whether to run an isolated scan.
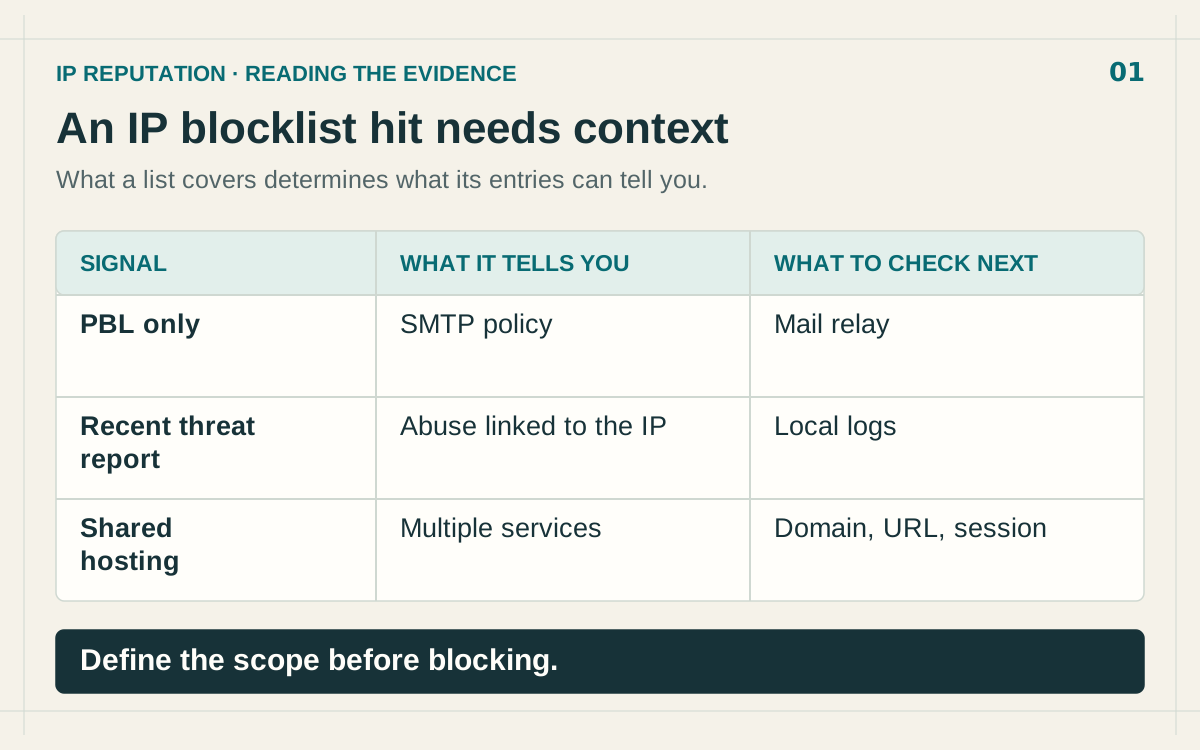
IP Blacklisted? Check for a False Positive Before Blocking
Check DNSBL scope, shared IPs, stale evidence and lookup errors to find why an IP was blacklisted and choose a proportionate response.
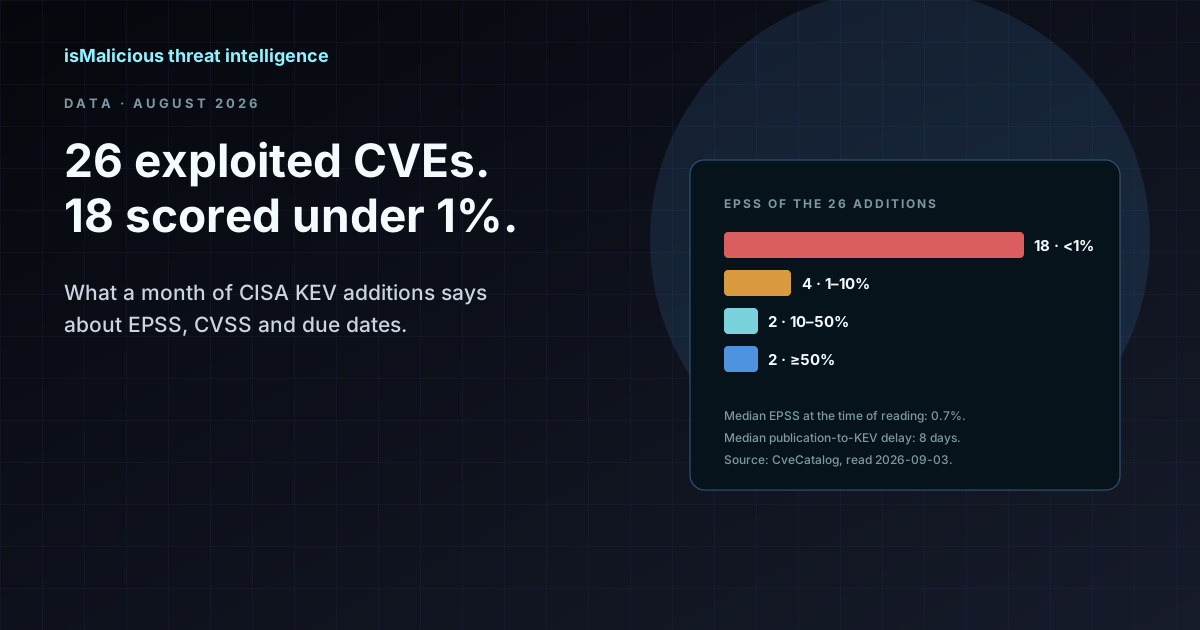
Exploited in August 2026: 26 KEV Additions, 18 With an EPSS Under 1%
A month of CISA KEV additions read against our CVE catalog: 18 of 26 exploited vulnerabilities score under 1% on EPSS today, 4 had no CVSS score when CISA added them, and CISA gave 18 of them a three-day deadline. The numbers, the method, and what they mean for a patch queue.
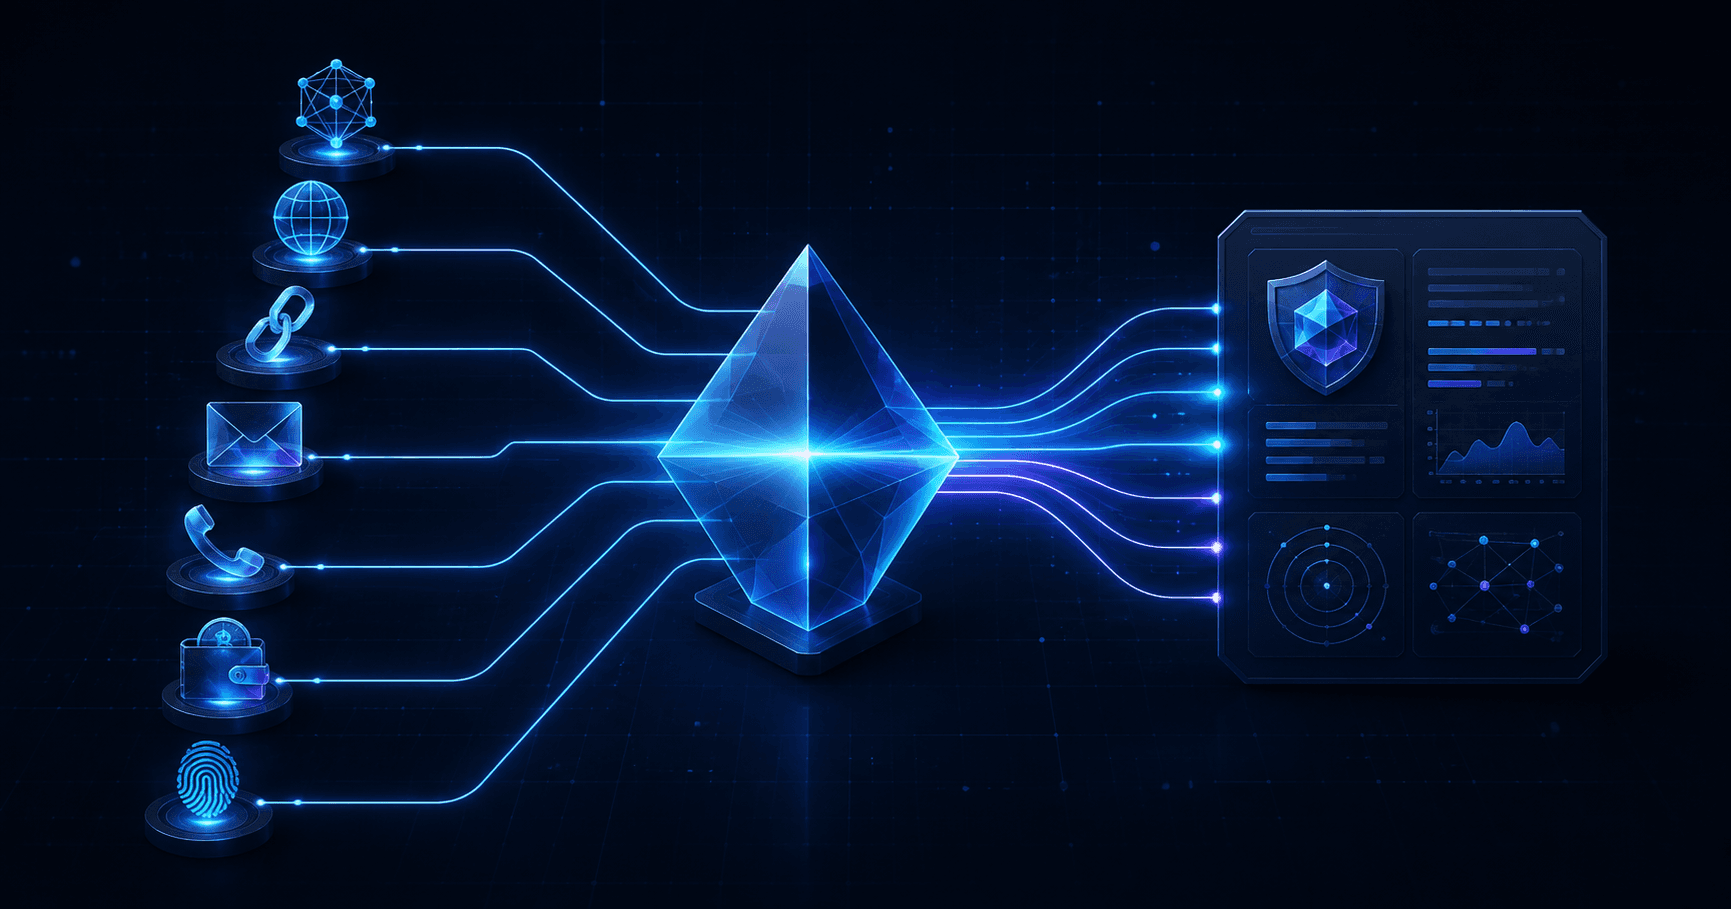
Smart Lookup: Check Any Threat Indicator from One Search
Paste an IP, domain, URL, email, phone number, wallet, file hash, or a complete suspicious message. Smart Lookup routes each indicator to the right threat report.
Composite Threat Reports: Triage Multiple IOCs Together
A phishing message or security alert rarely contains one indicator. Use a composite threat report to scope several IOCs without losing the evidence behind each result.
Threats Dashboard: Turn Current Intelligence into Priorities
Use the isMalicious Threats dashboard to move from a broad threat picture to the sectors, ransomware groups, malware, victims, and evidence that matter to your team.
Threat Alerts and Action Center: Build a Response Workflow
Move from monitored indicators and incoming alerts to a ranked queue, analyst validation, and owned response work with isMalicious Alerts and Action Center.
TAXII Threat Feeds: Build a Continuous SIEM Integration
Connect an isMalicious TAXII collection to your SIEM with safe pagination, durable checkpoints, validation, monitoring, and recovery.
Blocklists for Operational Threat Prevention: Test and Roll Back
Use /app/blocklists to select, test, deploy, measure, and safely reverse IP or domain prevention controls.
Threat Report History: Recheck, Monitor, and Reuse Evidence
Use isMalicious report history to find earlier lookups, run fresh checks, add indicators to monitoring, create cases, and export a reusable lookup index.
Expert Threat Intelligence Analysis
Our blog features in-depth analysis from our threat research team. Each article is backed by real data from our analysis of millions of malicious domains, IPs, and URLs across the global threat landscape. Topics include ransomware campaigns, phishing techniques, malware distribution networks, and emerging threat trends. We publish specific intelligence that security teams can immediately use to improve their defenses.
Practical Security Guidance
Beyond threat analysis, we share practical guidance for security practitioners. Our tutorials cover API integration, SIEM configuration, threat hunting techniques, and building effective threat intelligence programs. Whether you're a SOC analyst, security engineer, or CISO, you'll find content tailored to your role and experience level.
Stay Ahead of Emerging Threats
The threat landscape evolves constantly. Our blog keeps you informed about the latest attack techniques, newly discovered vulnerabilities, and emerging threat actors. Subscribe to our newsletter for weekly digests of the most important developments in cybersecurity.
Subscribe to Our Newsletter
Weekly threat intelligence insights delivered to your inbox.