Threat Intelligence Blog
Research, insights, and updates from the isMalicious team. Page 2 of 4.

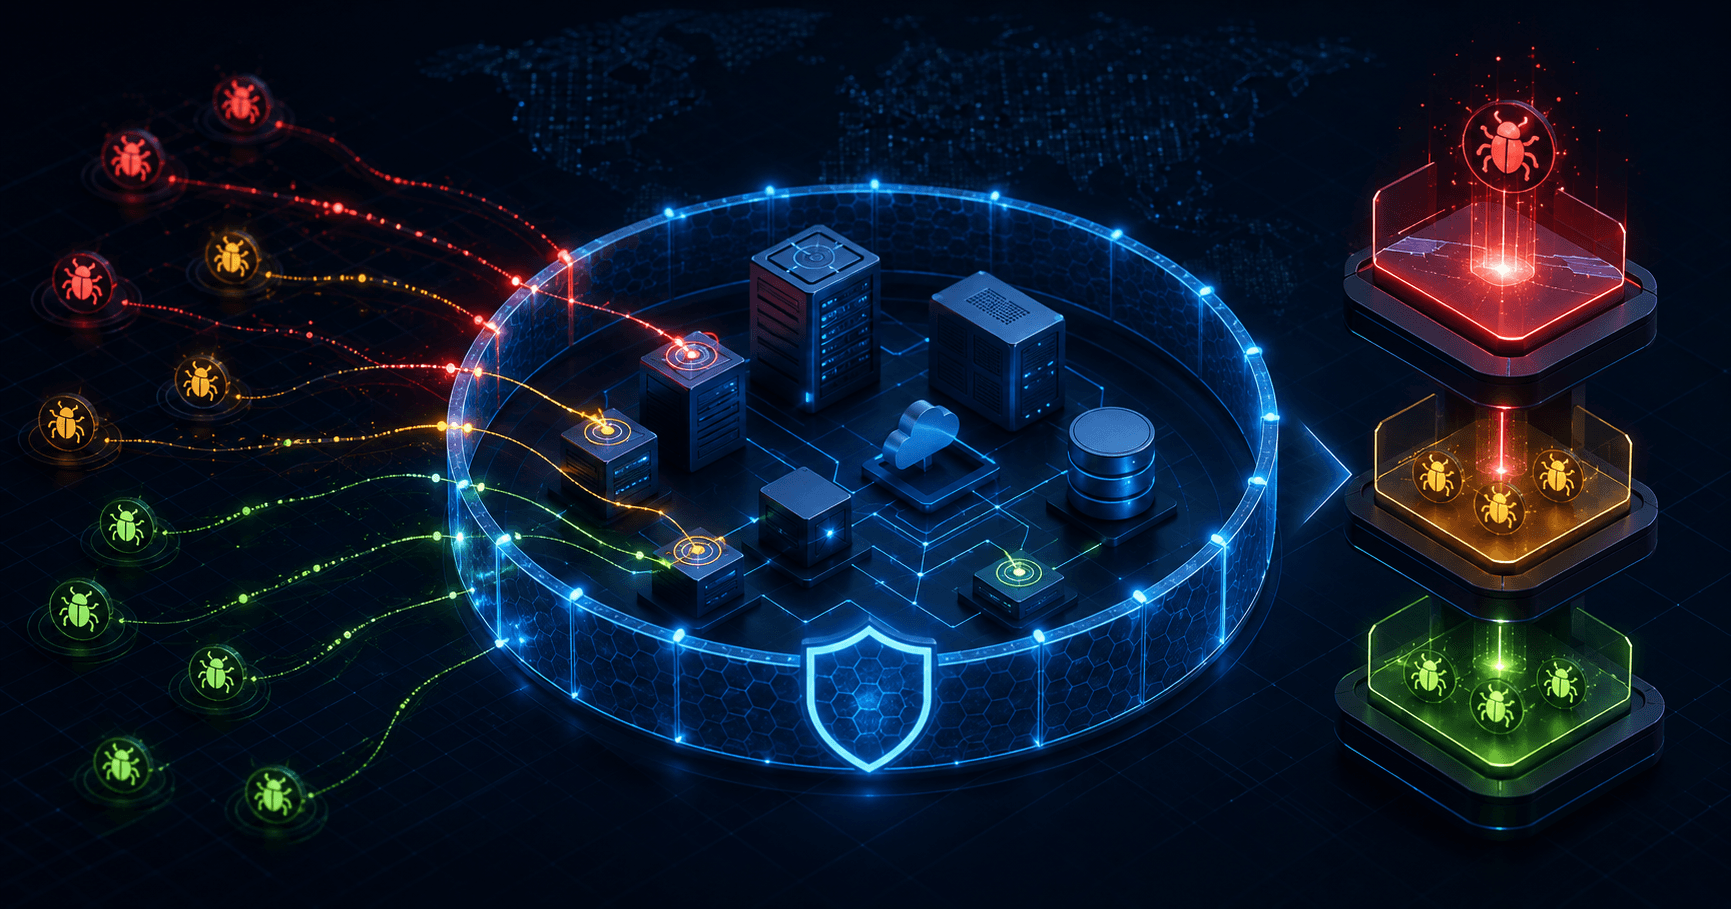
CVE Watch Perimeters: Prioritize Findings by Real Exposure
Map products to CVE Watch perimeters, then combine active exploitation, CISA KEV, EPSS, CVSS, product context, and remediation status to focus vulnerability work.
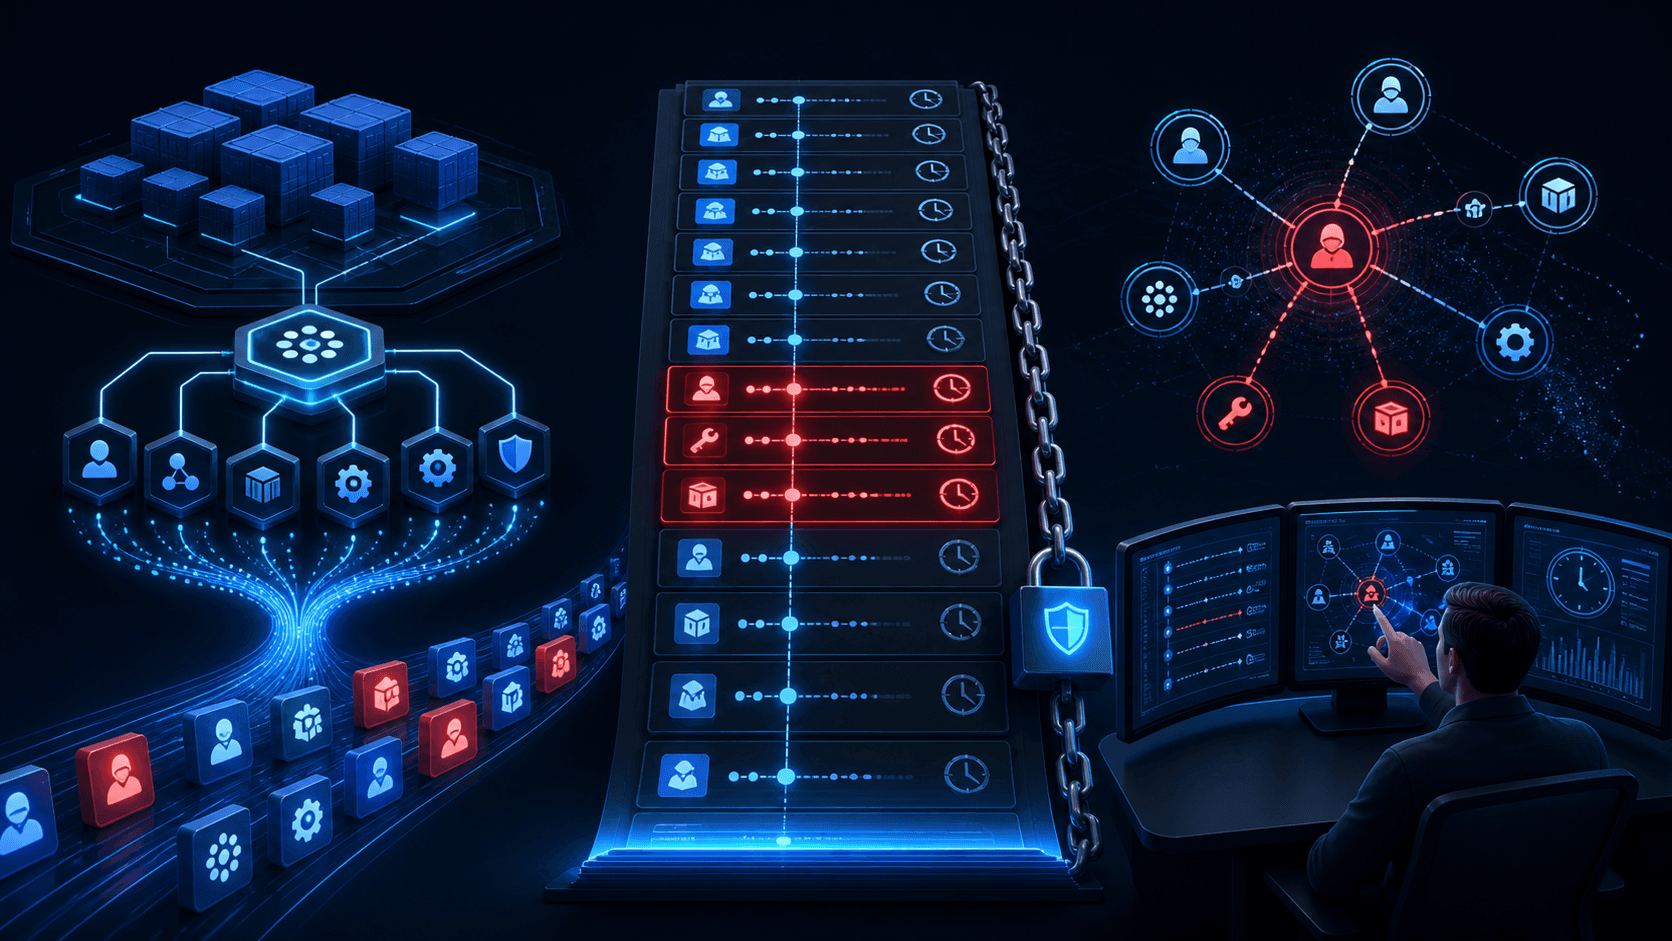
Kubernetes Audit Logs: Threat Detection Guide
Turn Kubernetes audit logs into detections for privilege abuse, secret access, persistence, risky exec, and control-plane compromise.
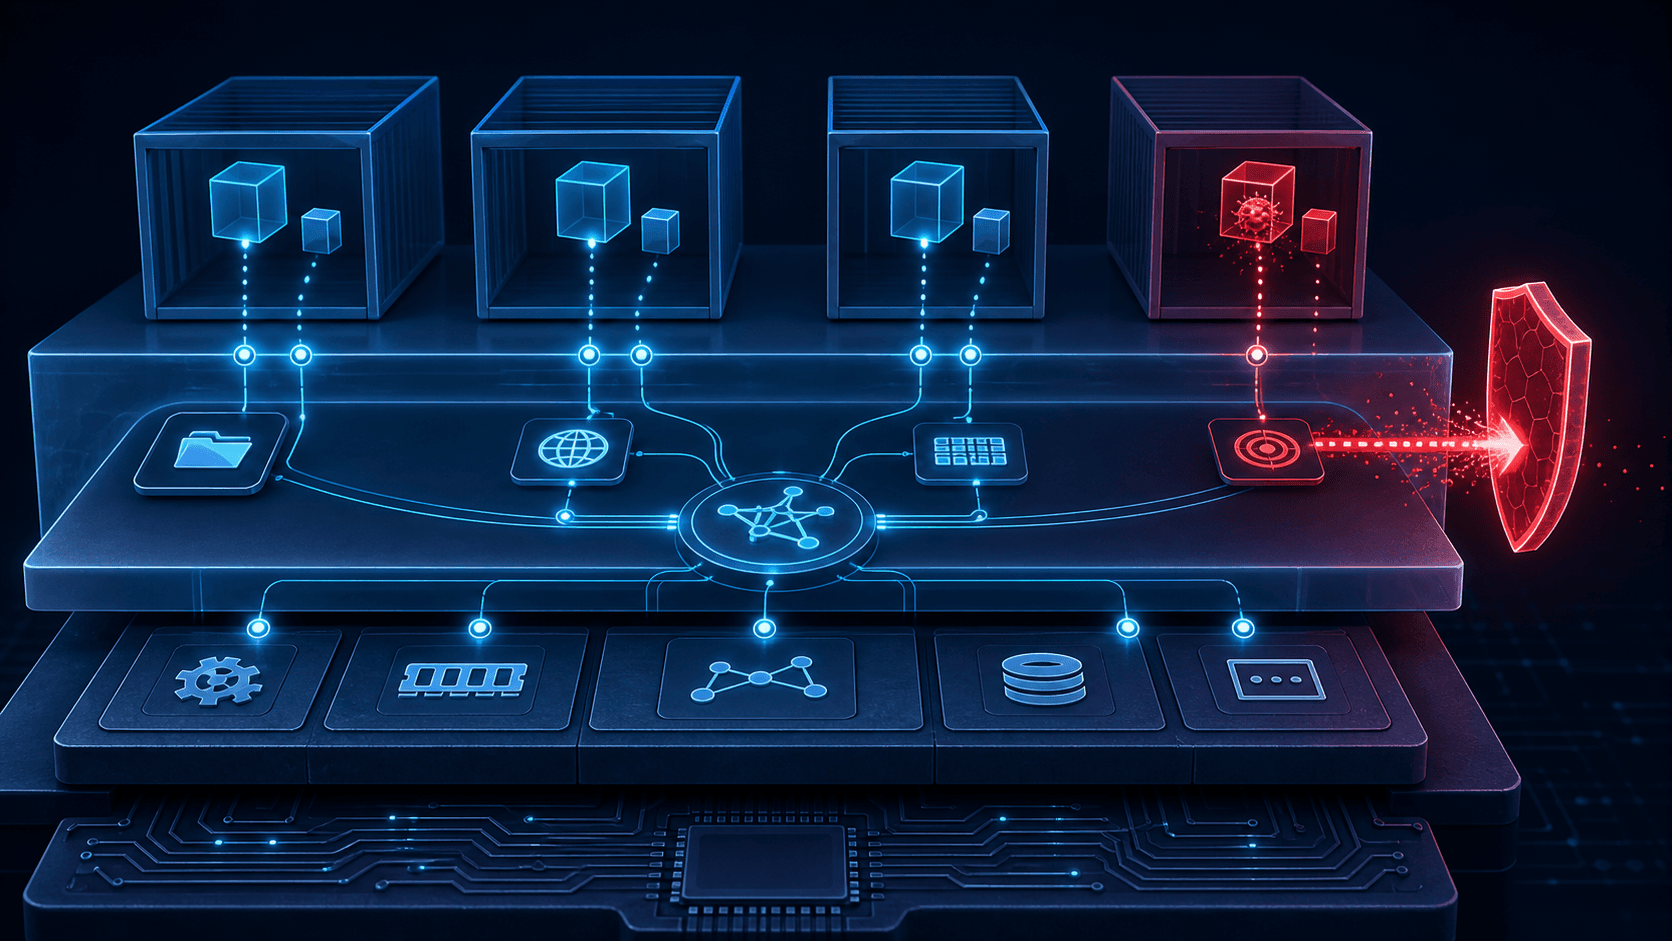
eBPF Runtime Security for Kubernetes
Use eBPF runtime security to observe processes, files, privileges, and network activity in Kubernetes while controlling noise and enforcement risk.
YARA vs Sigma: Which Detection Rule Should You Use?
Compare YARA and Sigma by data source, purpose, portability, performance, false positives, testing, and threat-intelligence workflow.
MFA Fatigue: Stop Push-Bombing Attacks
Detect and prevent MFA fatigue with number matching, rate limits, risk signals, phishing-resistant authentication, and an identity incident playbook.
Bulletproof Hosting: Map Criminal Infrastructure
Identify bulletproof hosting through ASN, prefix, domain, abuse, migration, and campaign signals without treating an entire network as malicious.
JA4 TLS Fingerprinting for Threat Hunting
Use JA4 TLS fingerprints for threat hunting, malware clustering, allowlisting, and anomaly detection without treating a fingerprint as identity.
IPv6 Threat Intelligence: Reputation Beyond IPv4
Build IPv6 threat intelligence with correct normalization, prefix context, dual-stack logging, enrichment, and reputation decisions that avoid overblocking.
Residential Proxy Abuse: Detect Fraud Without Blocking Users
Detect residential proxy abuse by combining IP reputation, identity, velocity, device, and behavioral signals without penalizing legitimate users.

isMalicious vs Censys: Internet Discovery and Reputation Verdicts Are Different Jobs
Censys maps what exists on the internet — hosts, certificates, open ports. isMalicious assesses what is malicious. Most teams comparing the two need the second question answered, not the first.

isMalicious vs OpenCTI: Why This Is the Wrong Comparison (and How They Work Together)
OpenCTI is a threat intelligence platform and knowledge graph. isMalicious is a data provider that feeds it. Teams searching for an OpenCTI alternative usually need a feed, not a replacement TIP.

STIX/TAXII Threat Feeds: Operational Guide for OpenCTI, MISP, and SIEM Pipelines
How to wire STIX 2.1 and TAXII 2.1 collections into OpenCTI, MISP, or your SIEM — what to poll, how to handle confidence and aging indicators, and where enrichment APIs fit alongside feed ingestion.
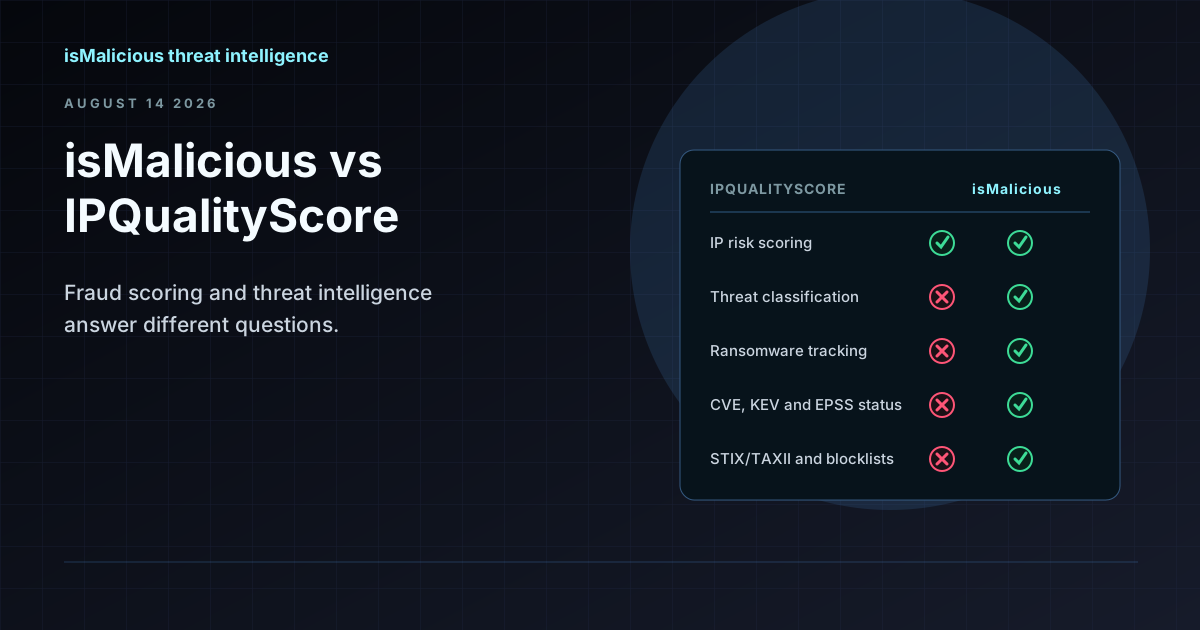
isMalicious vs IPQualityScore: Fraud Scoring and Threat Intelligence Are Different Jobs
IPQS scores whether a signup is fraudulent. isMalicious scores whether infrastructure is malicious. The two get compared constantly because both return a number about an IP address — and they answer different questions.

isMalicious vs MISP: Why This Is the Wrong Comparison (and What to Compare Instead)
MISP is where you store and share indicators. isMalicious is where indicators come from. Teams searching for a MISP alternative are usually looking for a feed, not a replacement platform.
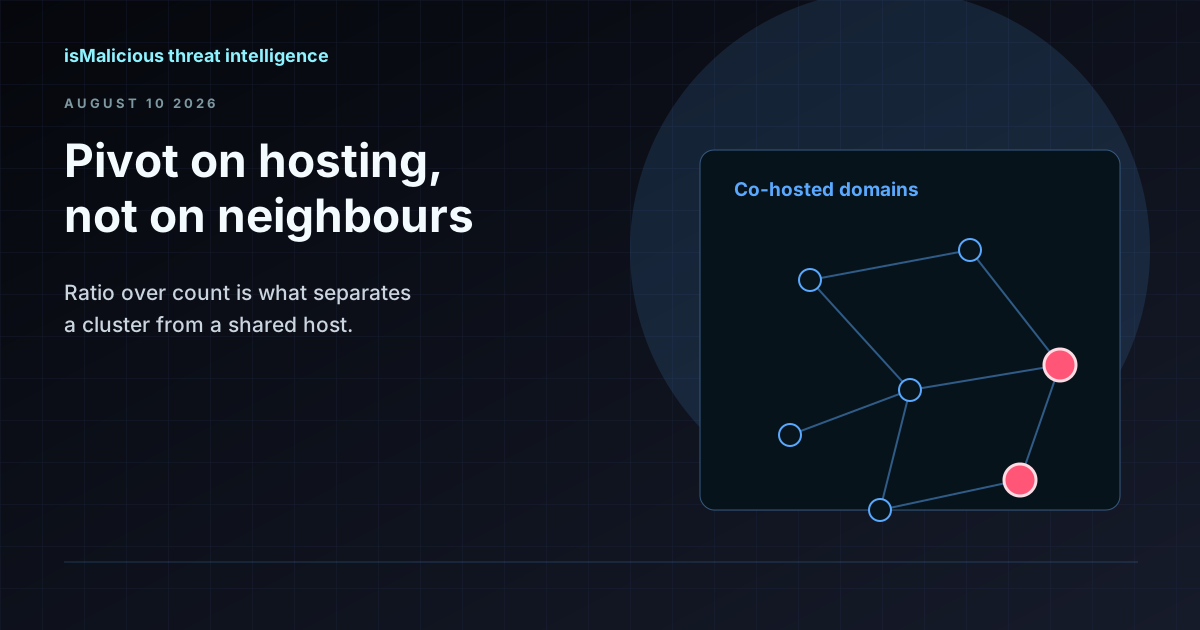
Reverse IP Lookup: Pivoting on Infrastructure Without Drowning in Shared Hosting
A reverse IP lookup turns one indicator into a cluster — or into a thousand innocent neighbours. Here is how to tell the difference, and how to pivot on hosting infrastructure without generating false positives.
urlscan.io vs isMalicious: URL Scanning
urlscan.io captures what a page does; isMalicious tells you if it is malicious. Verdicts, redirect chains, and blocklists compared.
BlueHammer Defender Exploitation: July 2026 Patch SLA For Windows Fleets
BlueHammer coverage shows why endpoint patching, CISA KEV context, CVE Watch, and IOC enrichment have to work together when local privilege escalation becomes ransomware tradecraft.
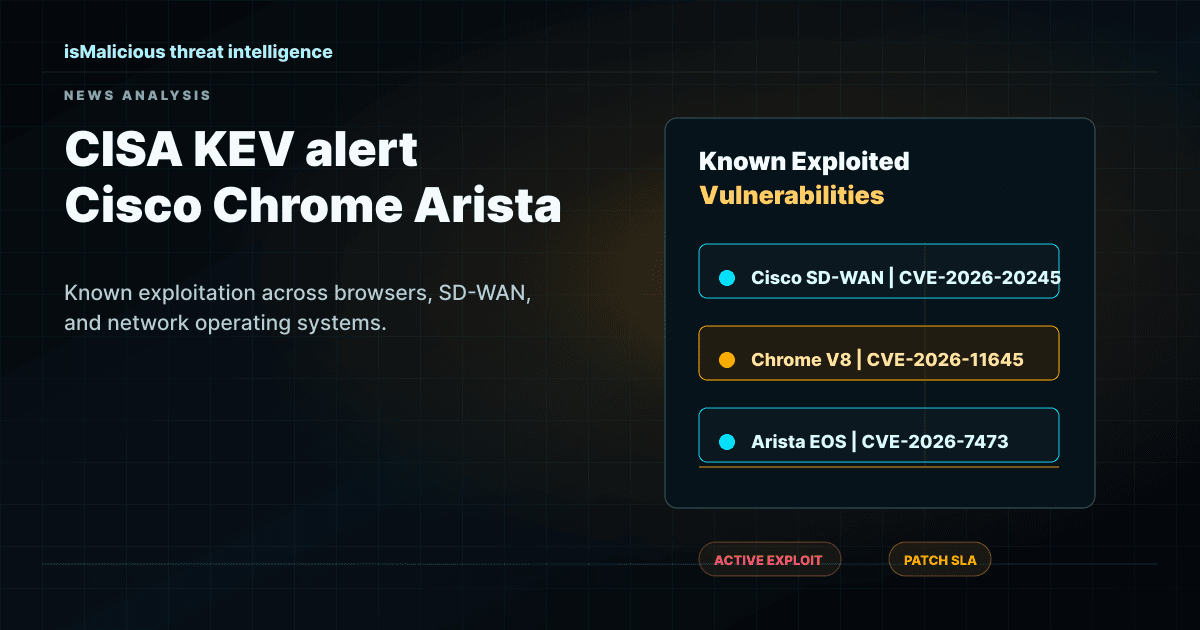
CISA KEV Adds Cisco, Chrome, And Arista Flaws: How To Prioritize Active Exploitation
CISA added Cisco SD-WAN, Google Chromium V8, and Arista EOS vulnerabilities to KEV in June 2026. Here is how SOC and vulnerability teams should turn that signal into action.
YellowKey and BitLocker Bypass: How Security Teams Should Re-Baseline Stolen-Device Risk
YellowKey made a quiet assumption loud again: encrypted endpoints still need vulnerability intelligence, asset context, and incident workflows. Here is how to respond when a last-resort control becomes a live risk.
SIEM and SOAR Threat Intelligence Enrichment: Workflows, Field Mapping, and the Metrics That Keep Teams Sane
A SOAR playbook without enrichment is a ticket printer. A SIEM with unbounded threat feeds is a bill. Here is a practical way to design enrichment for Splunk, Sentinel, or Elastic-style stacks—what to store, when to run playbooks, and what to report upward.
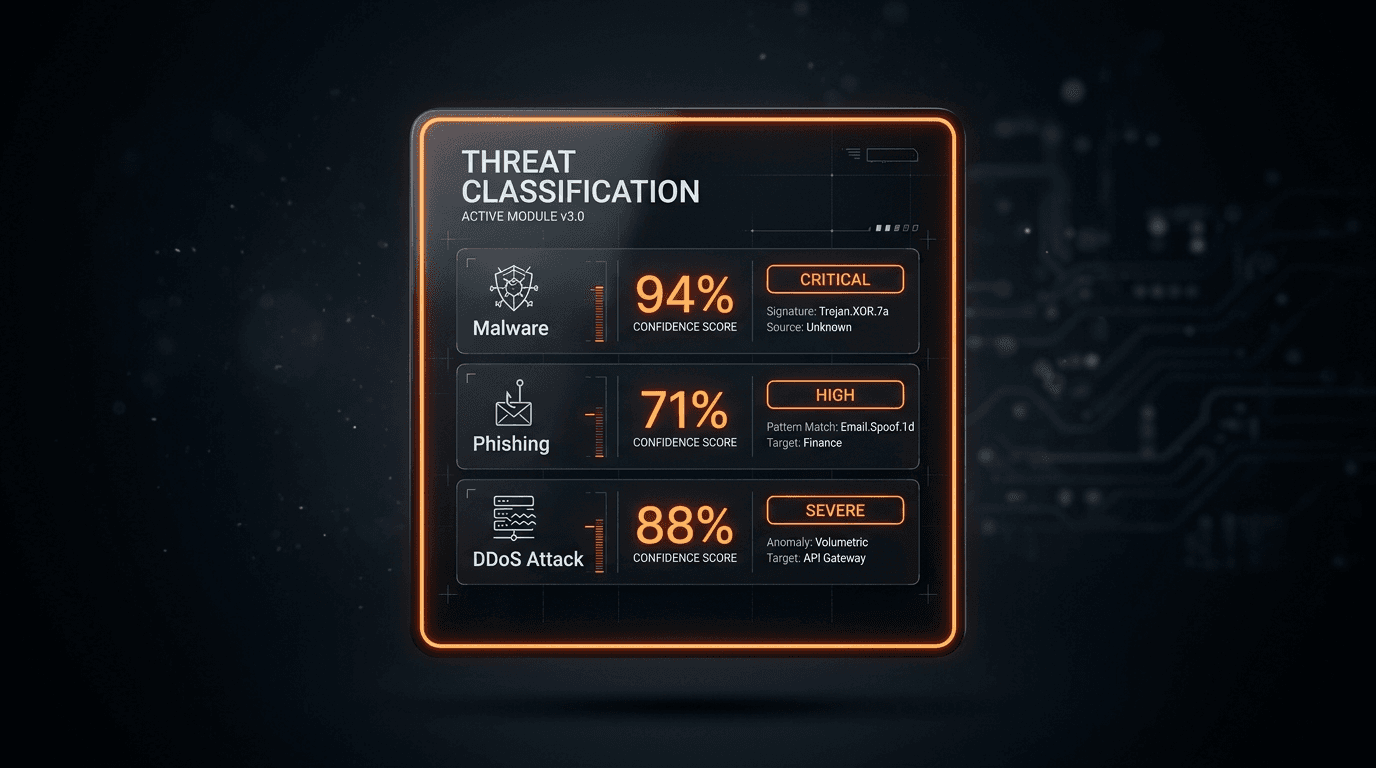
Threat Intelligence Risk Scoring: How to Calibrate Reputation, Reduce False Positives, and Defend Your Decisions
A noisy score is worse than no score. Learn what makes a reputation model trustworthy, how to combine multi-source evidence, and how to communicate uncertainty to your SOC and your executives.
Proxy, VPN, Tor, and Datacenter IPs: A Decision Matrix for WAF, Fraud, and SIEM Rules (Without Breaking Real Users)
Not every "datacenter" IP is malicious, and not every Tor exit is a fraudster. This matrix-style guide helps you combine IP type signals with reputation and product context for safer, explainable security decisions.
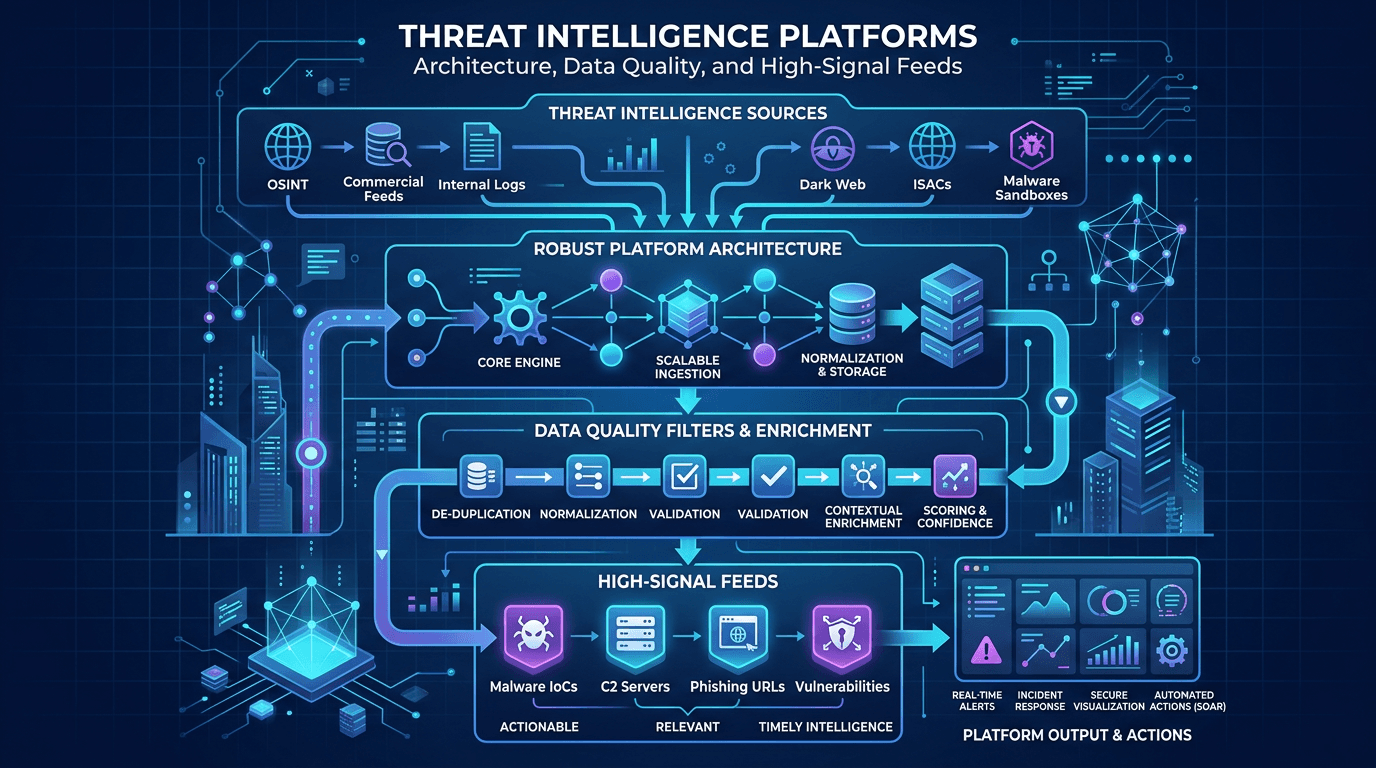
Threat Intelligence Platforms: Architecture, Data Quality, and High-Signal Feeds
Design TIPs and intel pipelines that scale: normalization, confidence scoring, deduplication, API-first delivery, and how to pair platform investments with analyst workflows.
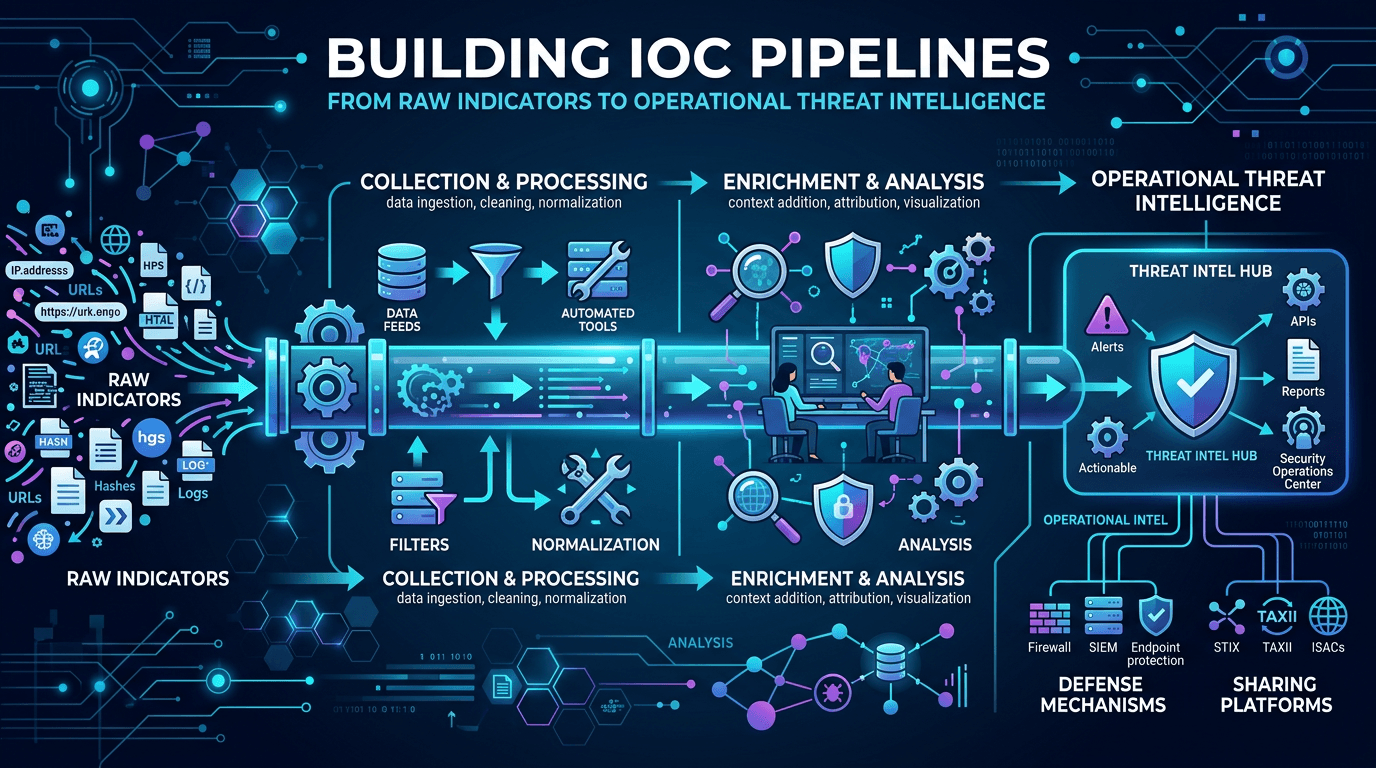
Building IOC Pipelines: From Raw Indicators to Operational Threat Intelligence in 2026
A practical engineering guide to building indicator of compromise (IOC) pipelines—ingestion, normalization, deduplication, enrichment, scoring, distribution, and feedback—to turn raw threat feeds into operational defense.
Subscribe to Our Newsletter
Weekly threat intelligence insights delivered to your inbox.