Threat Intel2026-07-11
China Edge Device Campaigns: Passive DNS And Certificates For Early Warning
Dutch intelligence warnings about Chinese cyber capability reinforce a practical defense priority: monitor edge devices, VPNs, routers, DNS history, and certificate reuse.
3 min read
Threat Intel2026-05-03
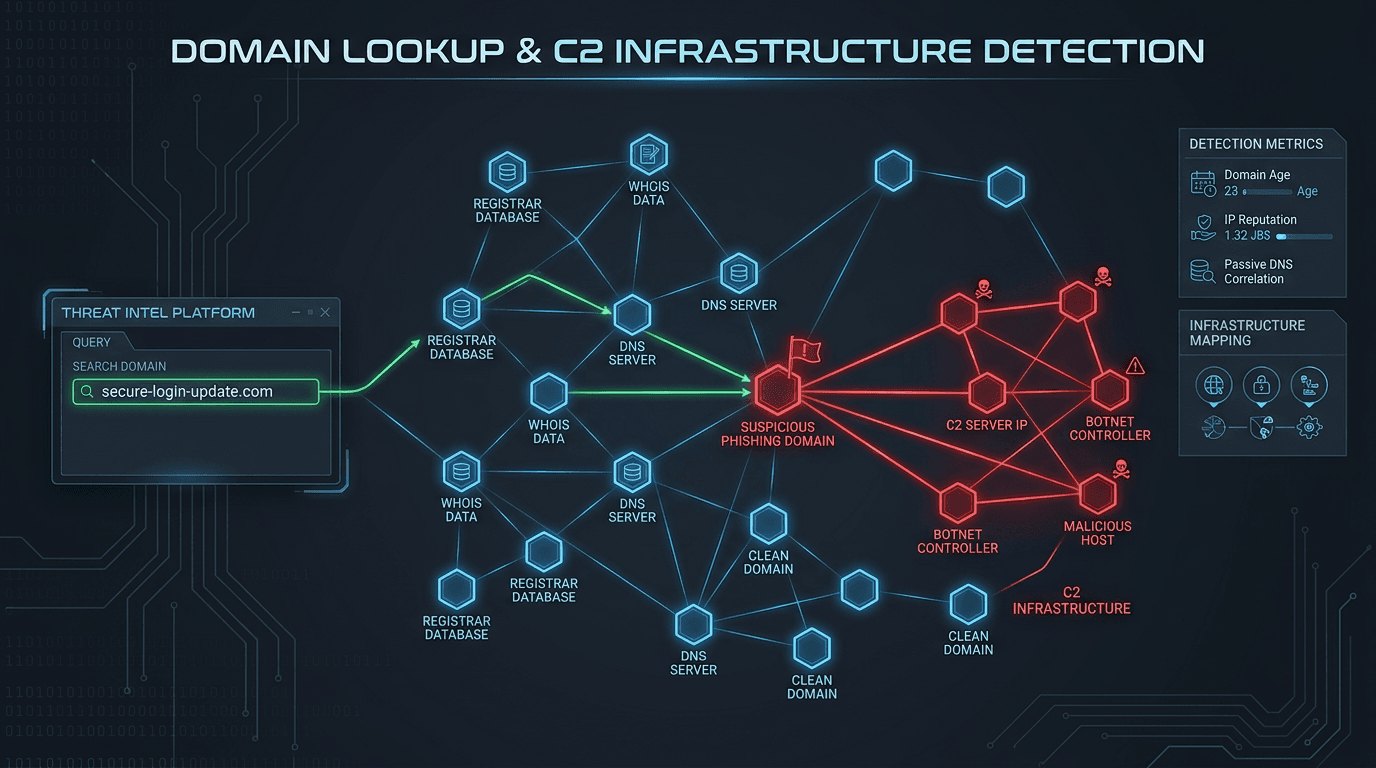
Malicious Infrastructure Clustering: How Passive DNS, TLS Certificates, and ASNs Reveal Shared Campaigns
A single C2 IP is a clue; shared signing patterns and DNS co-occurrence are a map. This guide explains how defenders cluster infrastructure without chasing ghosts—and how to document findings for IR, threat intel, and law enforcement handoffs.
6 min read