IOC Retrohunting: Investigating Historical Logs Reliably
Run reliable IOC retrohunts by separating event time, intelligence availability, and validity, then document historical evidence and the limits of negative results.
YARA vs Sigma: Which Detection Rule Should You Use?
Compare YARA and Sigma by data source, purpose, portability, performance, false positives, testing, and threat-intelligence workflow.
JA4 TLS Fingerprinting for Threat Hunting
Use JA4 TLS fingerprints for threat hunting, malware clustering, allowlisting, and anomaly detection without treating a fingerprint as identity.
DNS over HTTPS Security: Detect DoH Abuse
Secure DNS over HTTPS without losing visibility: govern resolvers, detect bypass attempts, correlate endpoint telemetry, and preserve user privacy.
DGA Detection: Find Algorithmically Generated Domains
Detect domain generation algorithms with lexical, DNS, endpoint, and reputation signals while controlling false positives in production.
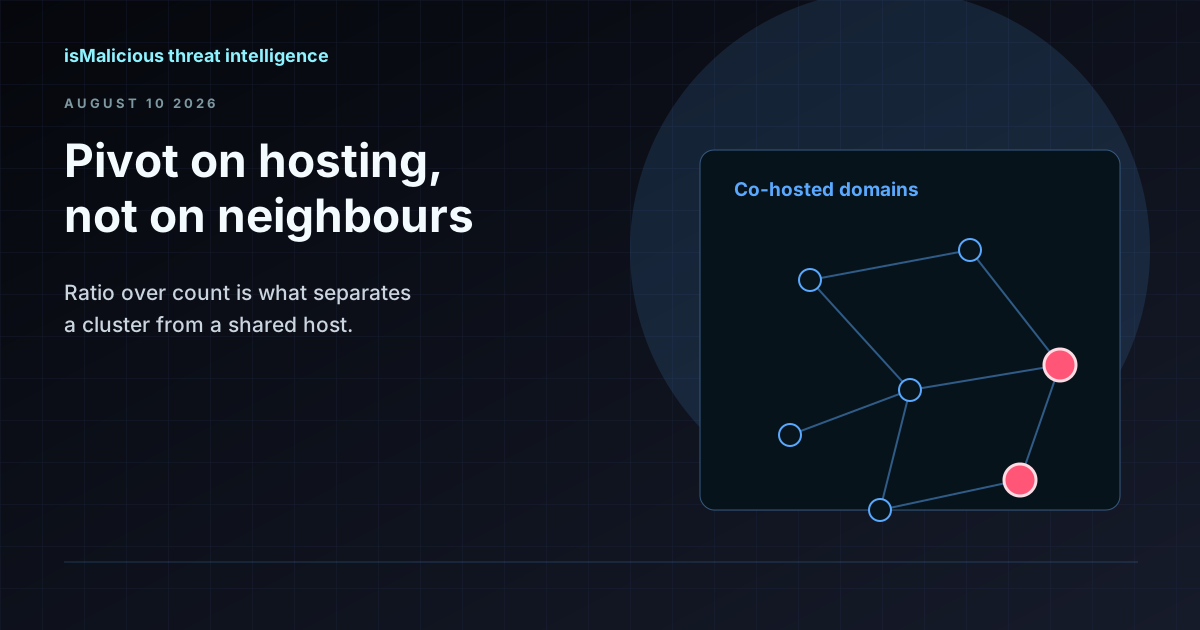
Reverse IP Lookup: Pivoting on Infrastructure Without Drowning in Shared Hosting
A reverse IP lookup turns one indicator into a cluster — or into a thousand innocent neighbours. Here is how to tell the difference, and how to pivot on hosting infrastructure without generating false positives.
Malicious Infrastructure Clustering: How Passive DNS, TLS Certificates, and ASNs Reveal Shared Campaigns
A single C2 IP is a clue; shared signing patterns and DNS co-occurrence are a map. This guide explains how defenders cluster infrastructure without chasing ghosts—and how to document findings for IR, threat intel, and law enforcement handoffs.
OSINT for SOC Analysts: Turning Open Source Intelligence Into Threat intelligence analysts can use
A complete guide to open source intelligence (OSINT) for security operations—tools, techniques, workflows, and legal considerations for collecting, analyzing, and operationalizing open threat data in a modern SOC.
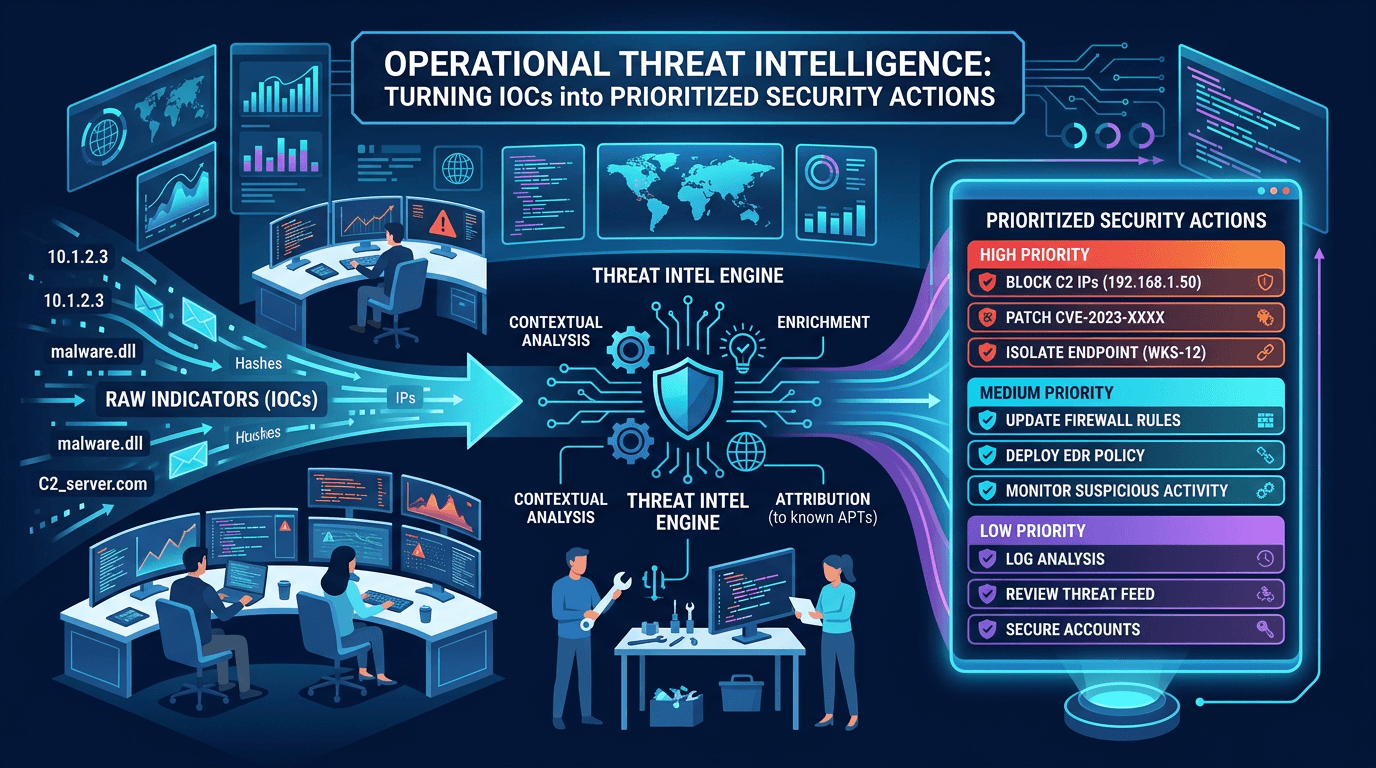
Operational Threat Intelligence: Turning IOCs into Prioritized Security Actions
Define operational CTI that SOC teams can use daily: IOC lifecycle, confidence scoring, feed hygiene, and how to align indicators with detection engineering and incident response.
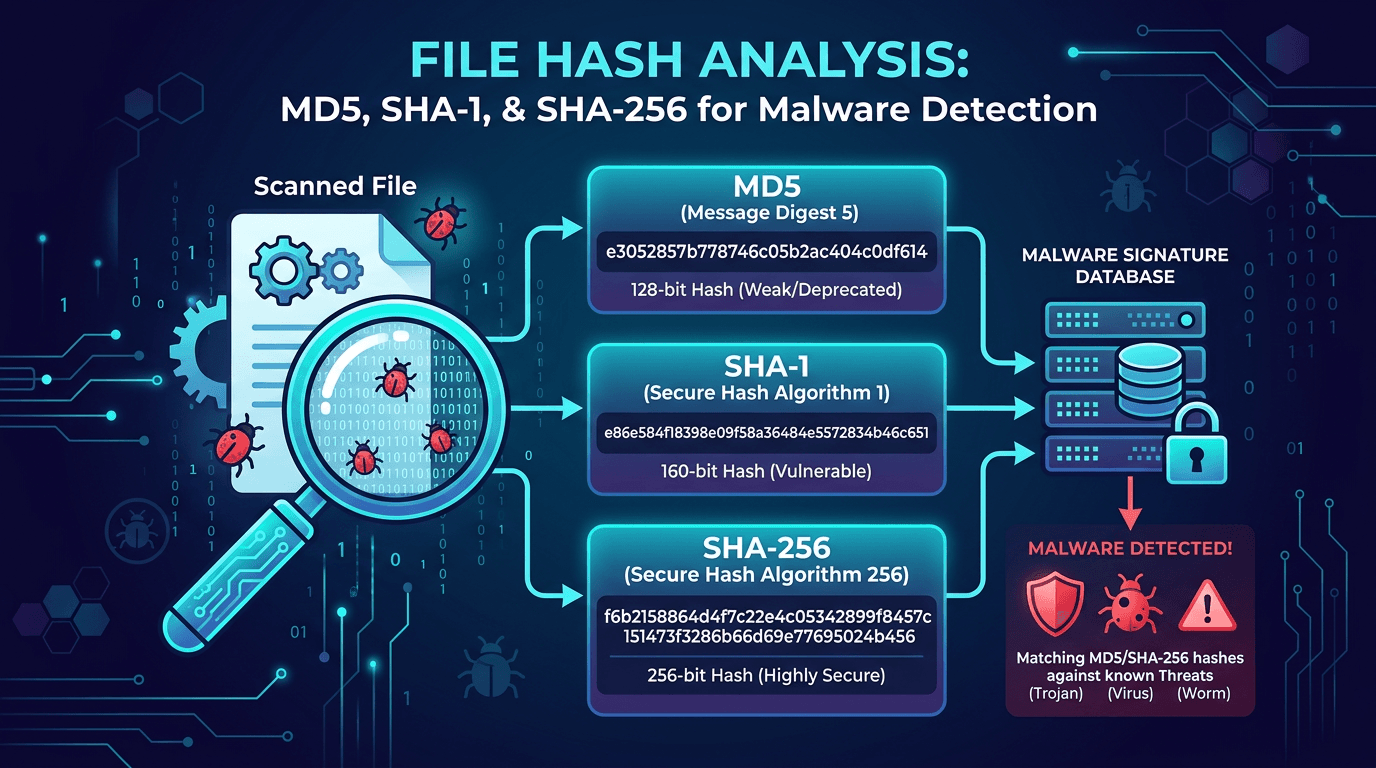
File Hash Analysis: MD5, SHA-1, and SHA-256 for Malware Detection and Threat Hunting
A practical guide to file hashes in cybersecurity—how MD5, SHA-1, and SHA-256 work, why they matter for malware detection, incident response, and threat hunting, and how to use hash lookups to enrich indicators of compromise.
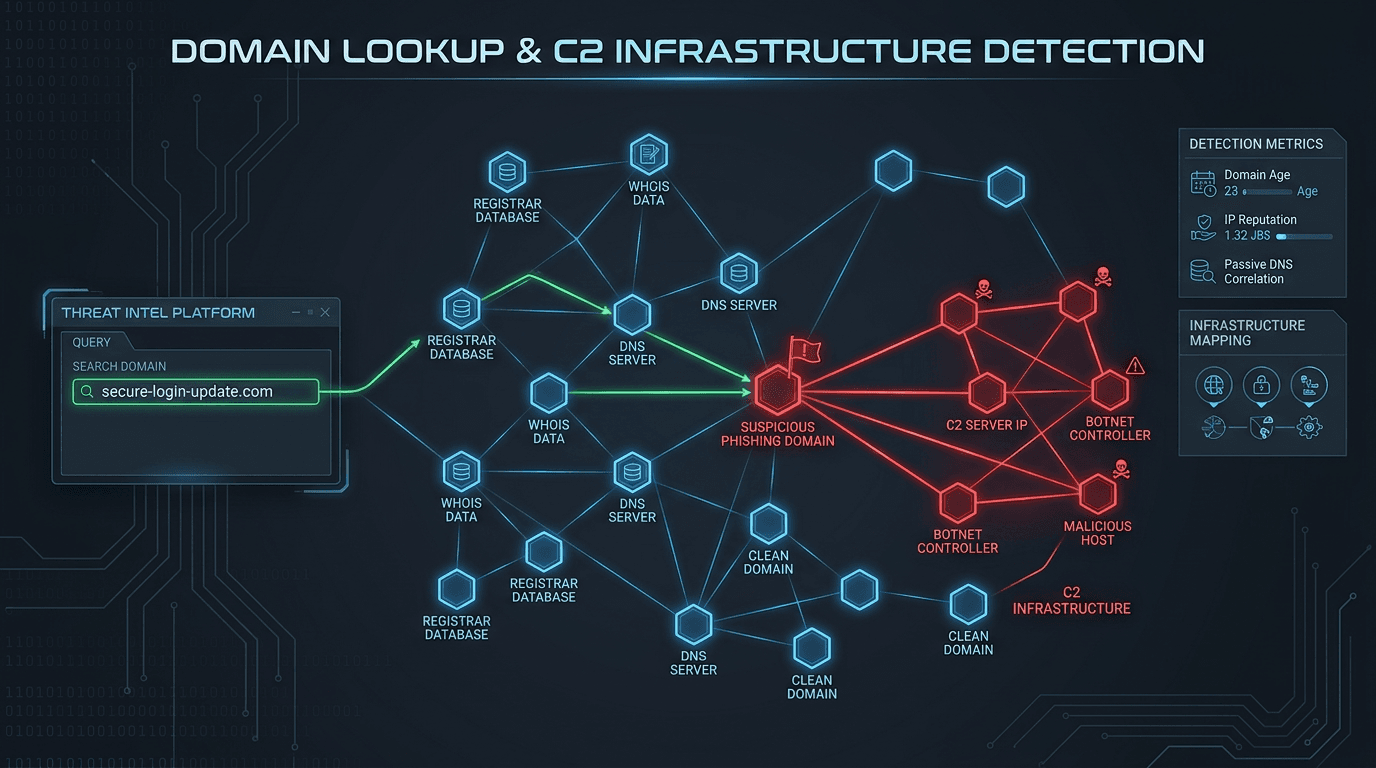
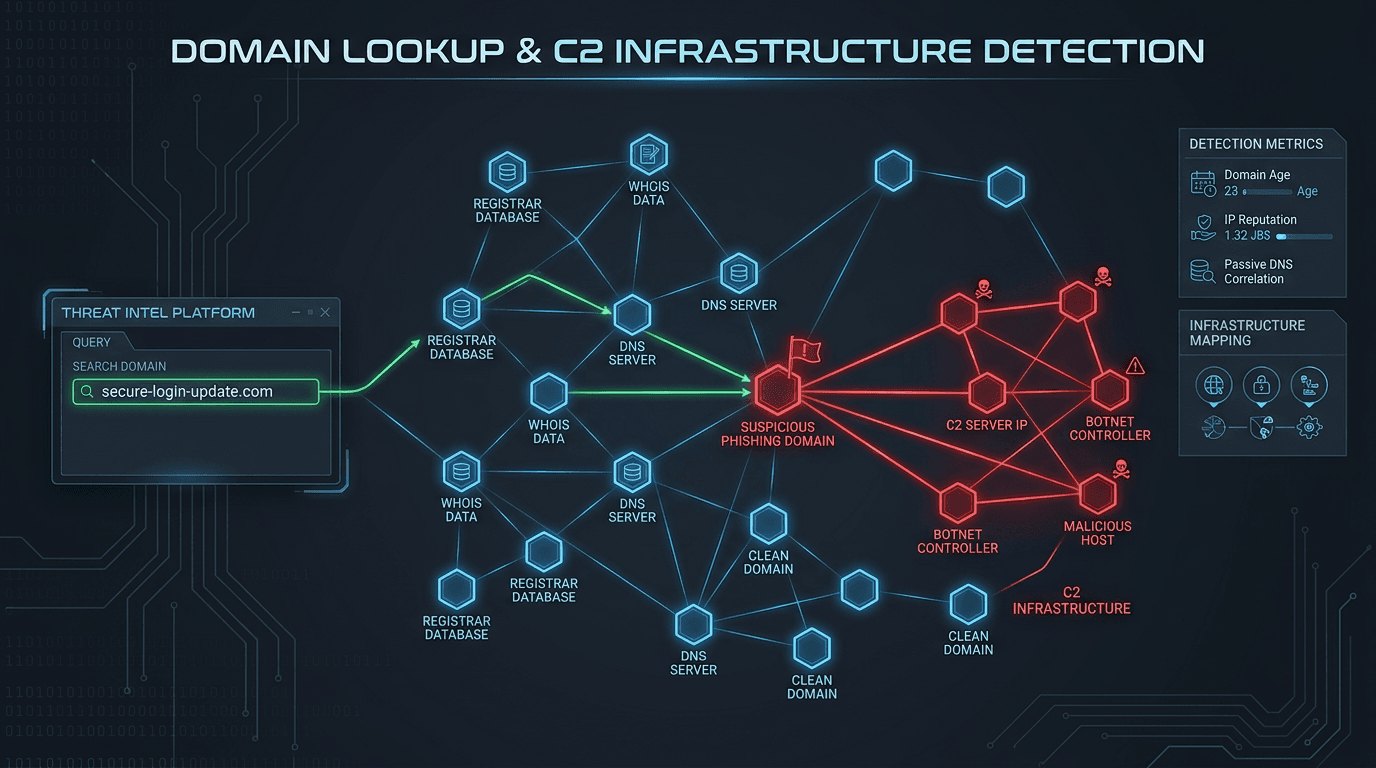
Domain Lookup for Phishing and C2 Infrastructure Detection
Phishing campaigns and malware operations depend on domain infrastructure that leaves detectable traces. Learn how advanced domain lookup techniques help security teams uncover phishing sites and command-and-control servers before they compromise your organization.