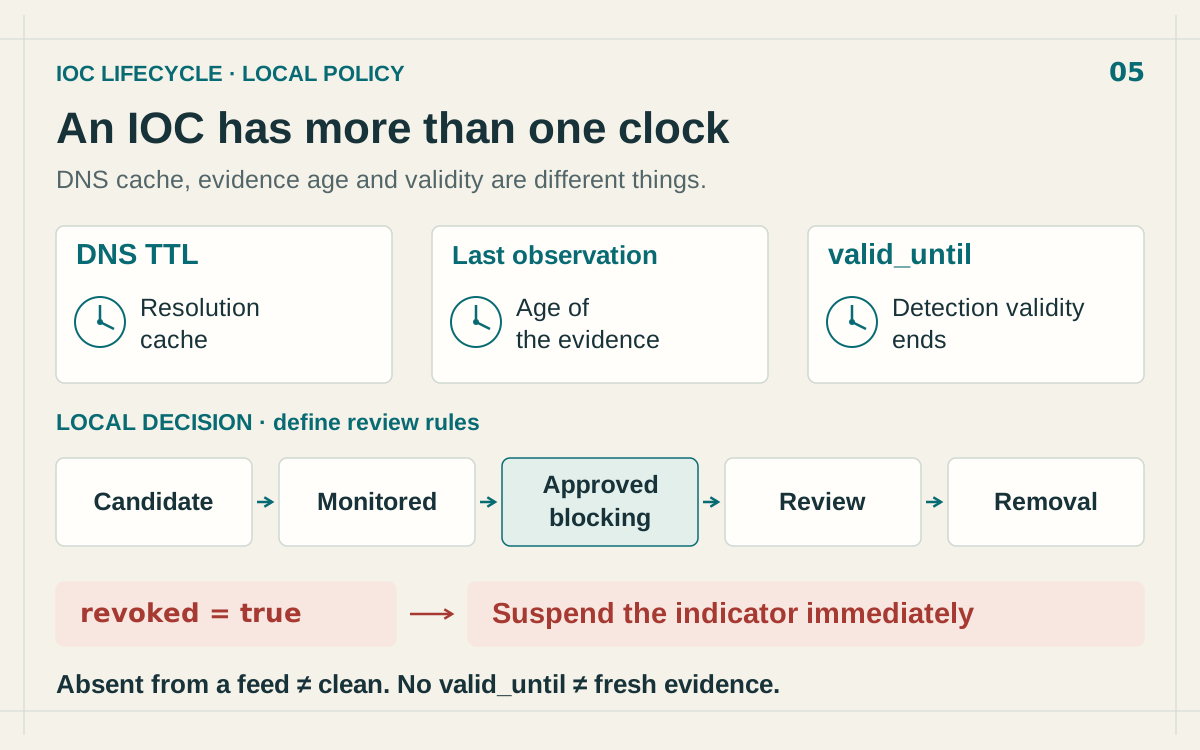
IOC Expiration: When to Remove an IP From a Blocklist
Manage IOC expiration with separate DNS, evidence and STIX validity clocks. Review stale IP blocks, process withdrawals and preserve the audit trail.
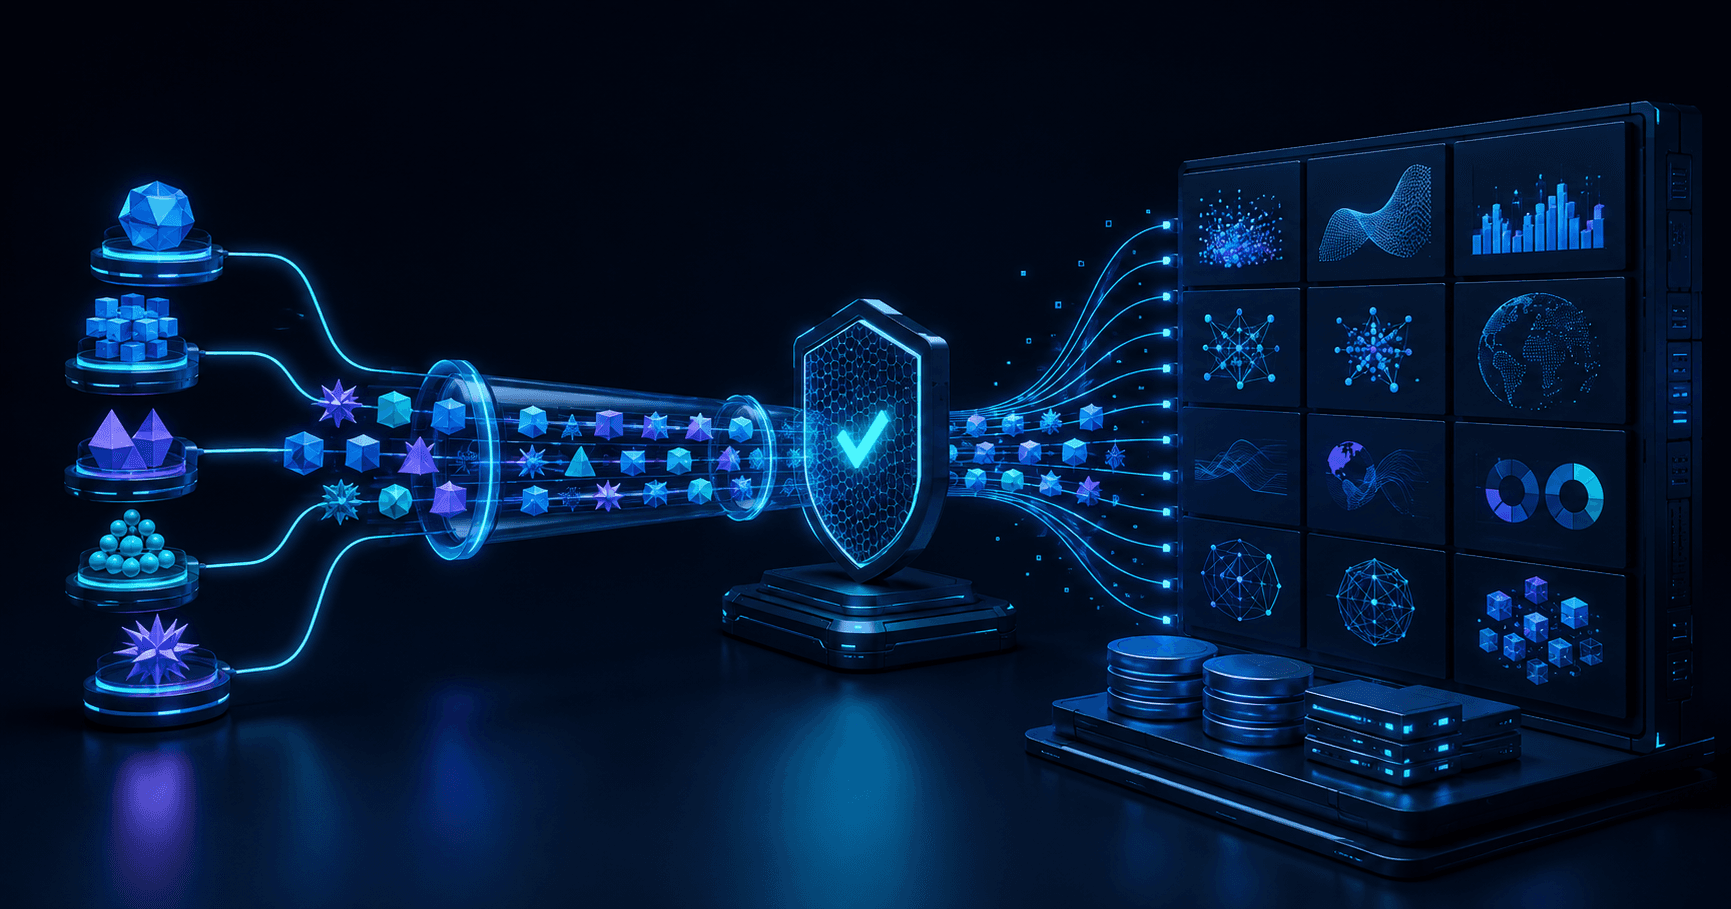
TAXII Threat Feeds: Build a Continuous SIEM Integration
Connect an isMalicious TAXII collection to your SIEM with safe pagination, durable checkpoints, validation, monitoring, and recovery.

STIX/TAXII Threat Feeds: Operational Guide for OpenCTI, MISP, and SIEM Pipelines
How to wire STIX 2.1 and TAXII 2.1 collections into OpenCTI, MISP, or your SIEM — what to poll, how to handle confidence and aging indicators, and where enrichment APIs fit alongside feed ingestion.
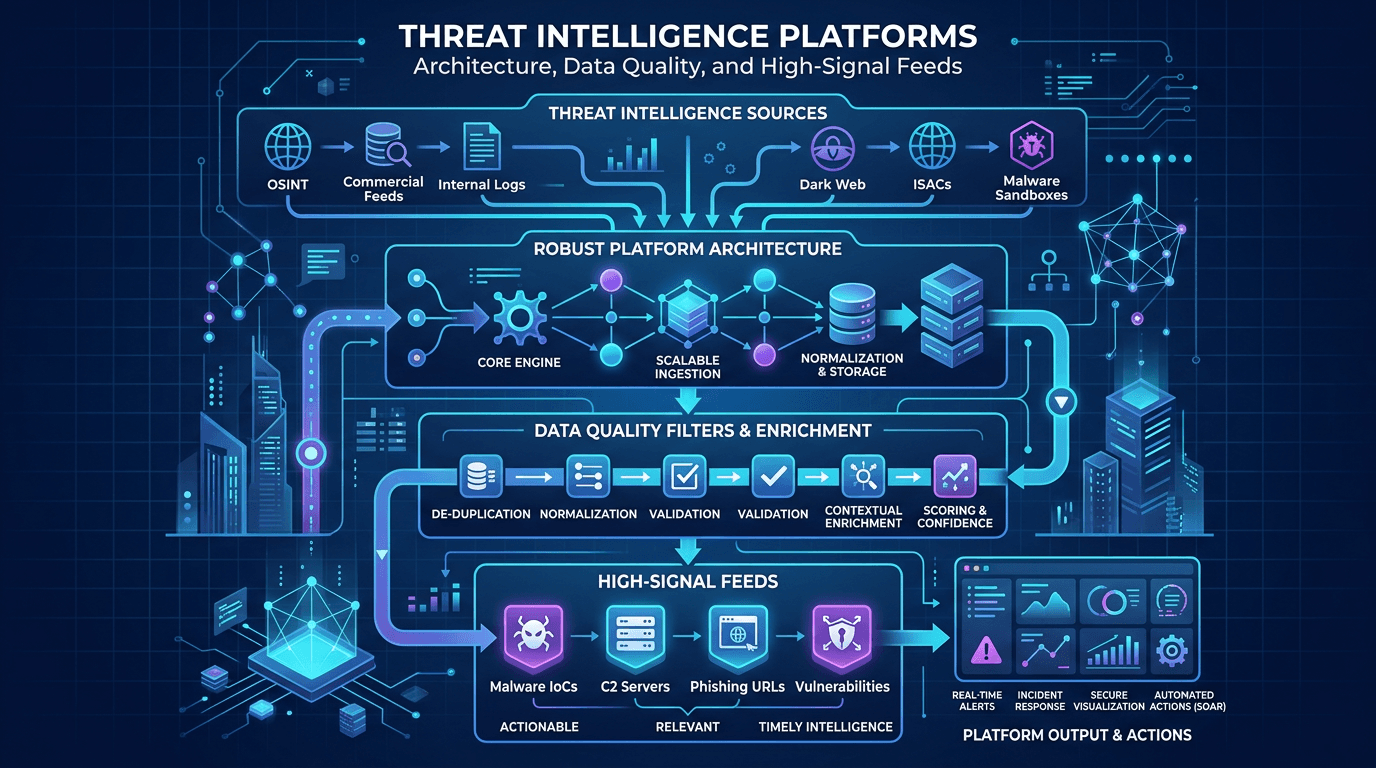
Threat Intelligence Platforms: Architecture, Data Quality, and High-Signal Feeds
Design TIPs and intel pipelines that scale: normalization, confidence scoring, deduplication, API-first delivery, and how to pair platform investments with analyst workflows.
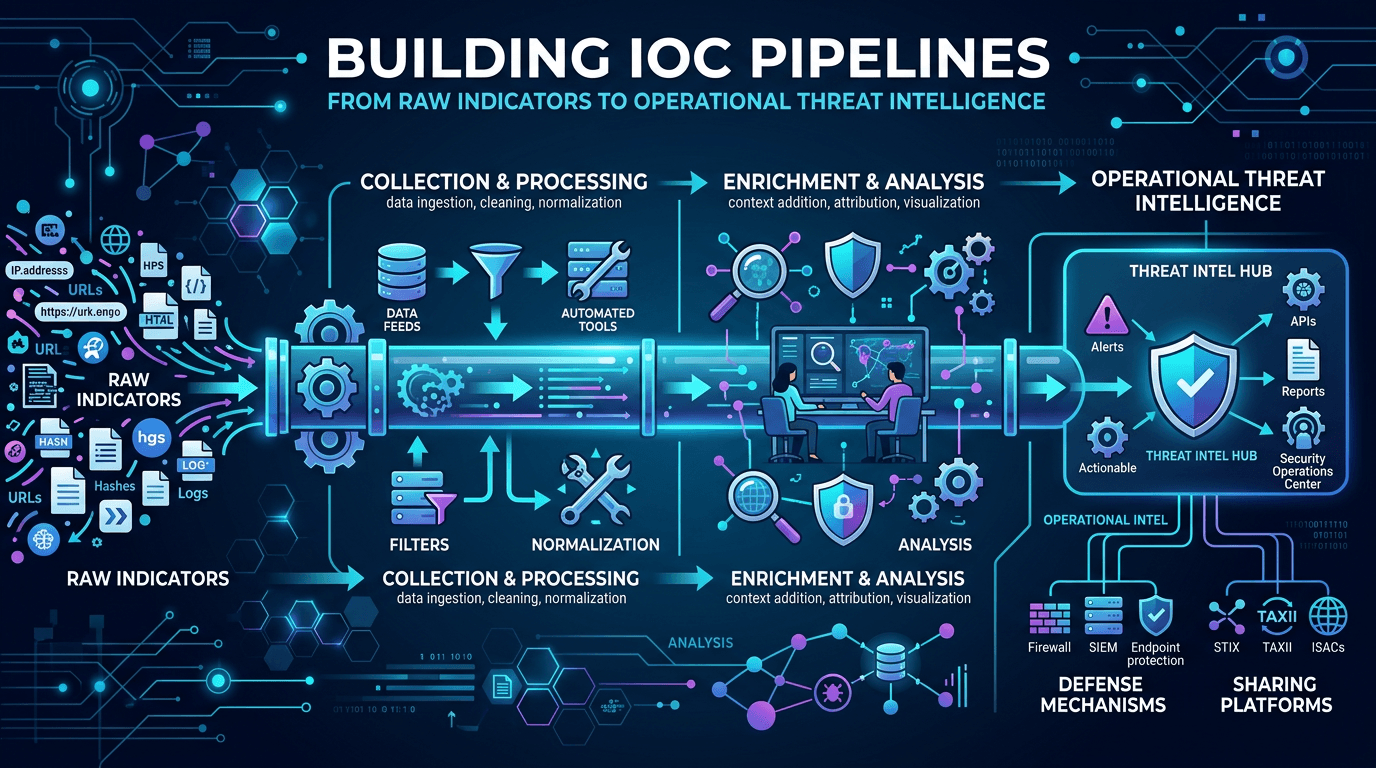
Building IOC Pipelines: From Raw Indicators to Operational Threat Intelligence in 2026
A practical engineering guide to building indicator of compromise (IOC) pipelines—ingestion, normalization, deduplication, enrichment, scoring, distribution, and feedback—to turn raw threat feeds into operational defense.