IOC Retrohunting: Investigating Historical Logs Reliably
Run reliable IOC retrohunts by separating event time, intelligence availability, and validity, then document historical evidence and the limits of negative results.
TAXII Threat Feeds: Build a Continuous SIEM Integration
Connect an isMalicious TAXII collection to your SIEM with safe pagination, durable checkpoints, validation, monitoring, and recovery.
Kubernetes Audit Logs: Threat Detection Guide
Turn Kubernetes audit logs into detections for privilege abuse, secret access, persistence, risky exec, and control-plane compromise.
YARA vs Sigma: Which Detection Rule Should You Use?
Compare YARA and Sigma by data source, purpose, portability, performance, false positives, testing, and threat-intelligence workflow.

isMalicious vs OpenCTI: Why This Is the Wrong Comparison (and How They Work Together)
OpenCTI is a threat intelligence platform and knowledge graph. isMalicious is a data provider that feeds it. Teams searching for an OpenCTI alternative usually need a feed, not a replacement TIP.

isMalicious vs Recorded Future: When a Threat Data API Makes More Sense Than an Enterprise Intel Program
Recorded Future delivers finished intelligence and analyst support at enterprise scale. isMalicious delivers self-serve enrichment and feeds without a sales cycle. The right choice depends on whether you need strategic reports or automated verdicts.

STIX/TAXII Threat Feeds: Operational Guide for OpenCTI, MISP, and SIEM Pipelines
How to wire STIX 2.1 and TAXII 2.1 collections into OpenCTI, MISP, or your SIEM — what to poll, how to handle confidence and aging indicators, and where enrichment APIs fit alongside feed ingestion.

isMalicious vs MISP: Why This Is the Wrong Comparison (and What to Compare Instead)
MISP is where you store and share indicators. isMalicious is where indicators come from. Teams searching for a MISP alternative are usually looking for a feed, not a replacement platform.
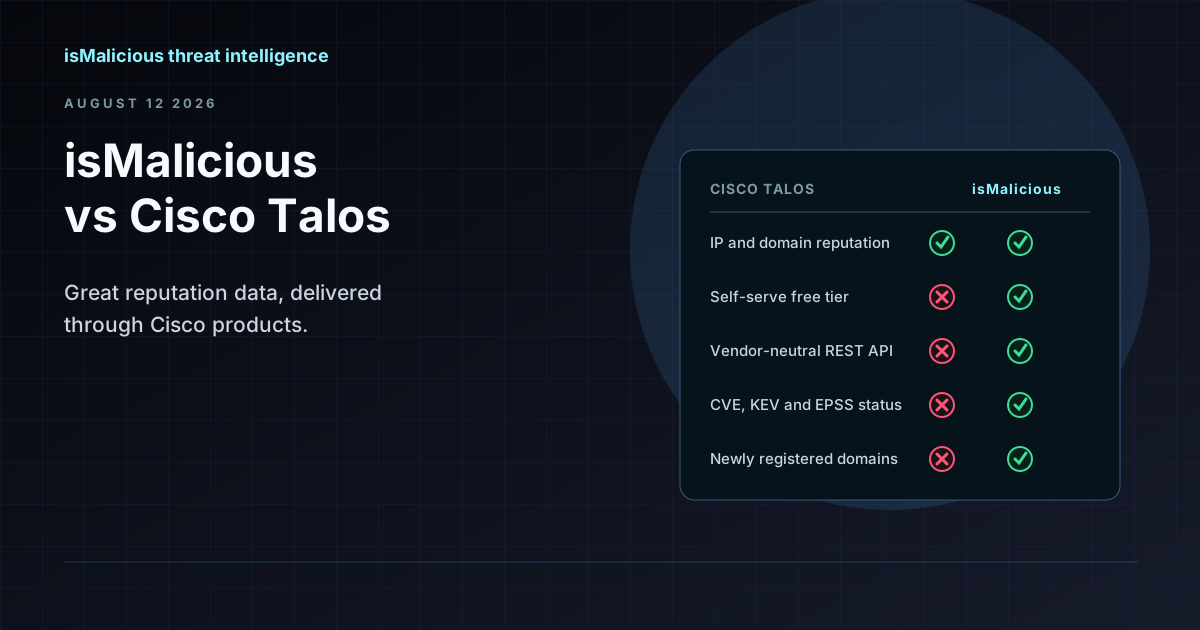
isMalicious vs Cisco Talos: Reputation Lookups Outside the Cisco Stack
Talos reputation is excellent and it lives inside Cisco products. If your stack is not Cisco, or you need an API rather than a web form, that is where the comparison starts.
Bulk IP and Domain Lookups: Designing Indicator Enrichment That Survives Real Volume
One incident produces hundreds of indicators, and per-indicator lookups are where triage stalls. Here is how to build a batch enrichment pipeline that respects quotas, deduplicates properly, and fails gracefully.
SOC Alert Fatigue: How Threat Intelligence Reduces False Positives Without Hiding Real Attacks
Alert fatigue is not a staffing problem alone. SOC teams need better evidence, source quality, confidence bands, and enrichment workflows that turn noisy alerts into defensible decisions.
SIEM and SOAR Threat Intelligence Enrichment: Workflows, Field Mapping, and the Metrics That Keep Teams Sane
A SOAR playbook without enrichment is a ticket printer. A SIEM with unbounded threat feeds is a bill. Here is a practical way to design enrichment for Splunk, Sentinel, or Elastic-style stacks—what to store, when to run playbooks, and what to report upward.
Proxy, VPN, Tor, and Datacenter IPs: A Decision Matrix for WAF, Fraud, and SIEM Rules (Without Breaking Real Users)
Not every "datacenter" IP is malicious, and not every Tor exit is a fraudster. This matrix-style guide helps you combine IP type signals with reputation and product context for safer, explainable security decisions.