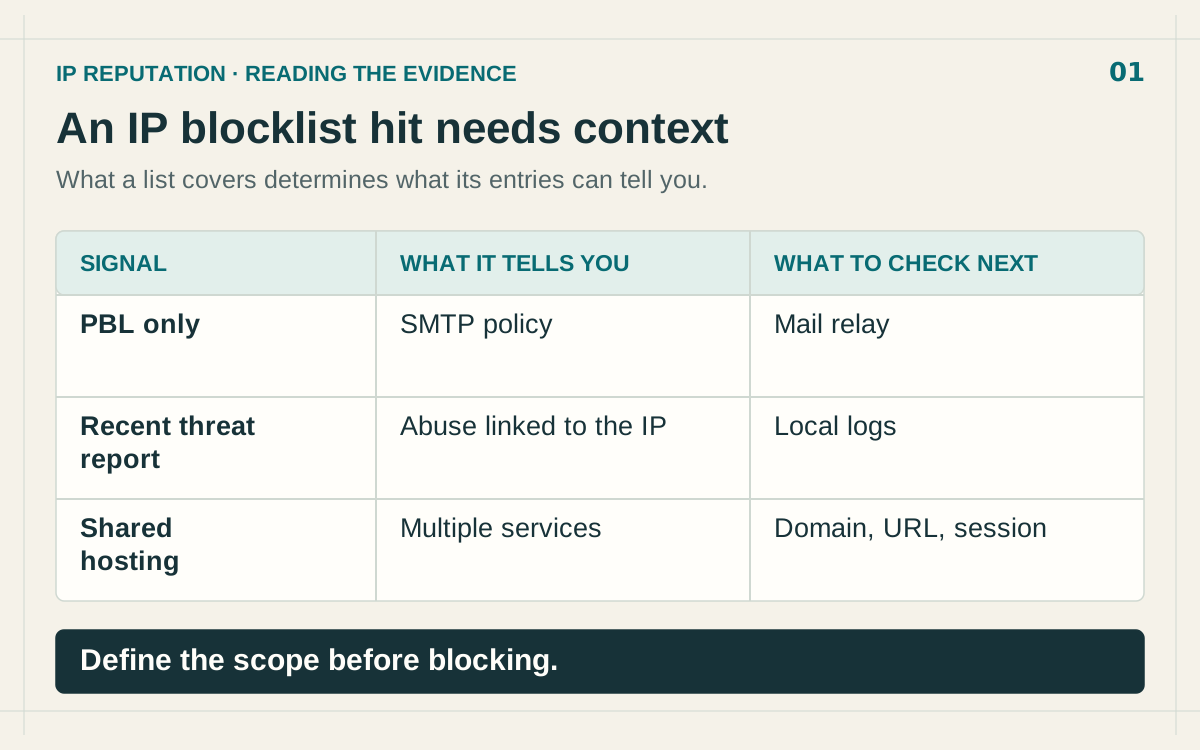
IP Blacklisted? Check for a False Positive Before Blocking
Check DNSBL scope, shared IPs, stale evidence and lookup errors to find why an IP was blacklisted and choose a proportionate response.
IPv6 Threat Intelligence: Reputation Beyond IPv4
Build IPv6 threat intelligence with correct normalization, prefix context, dual-stack logging, enrichment, and reputation decisions that avoid overblocking.
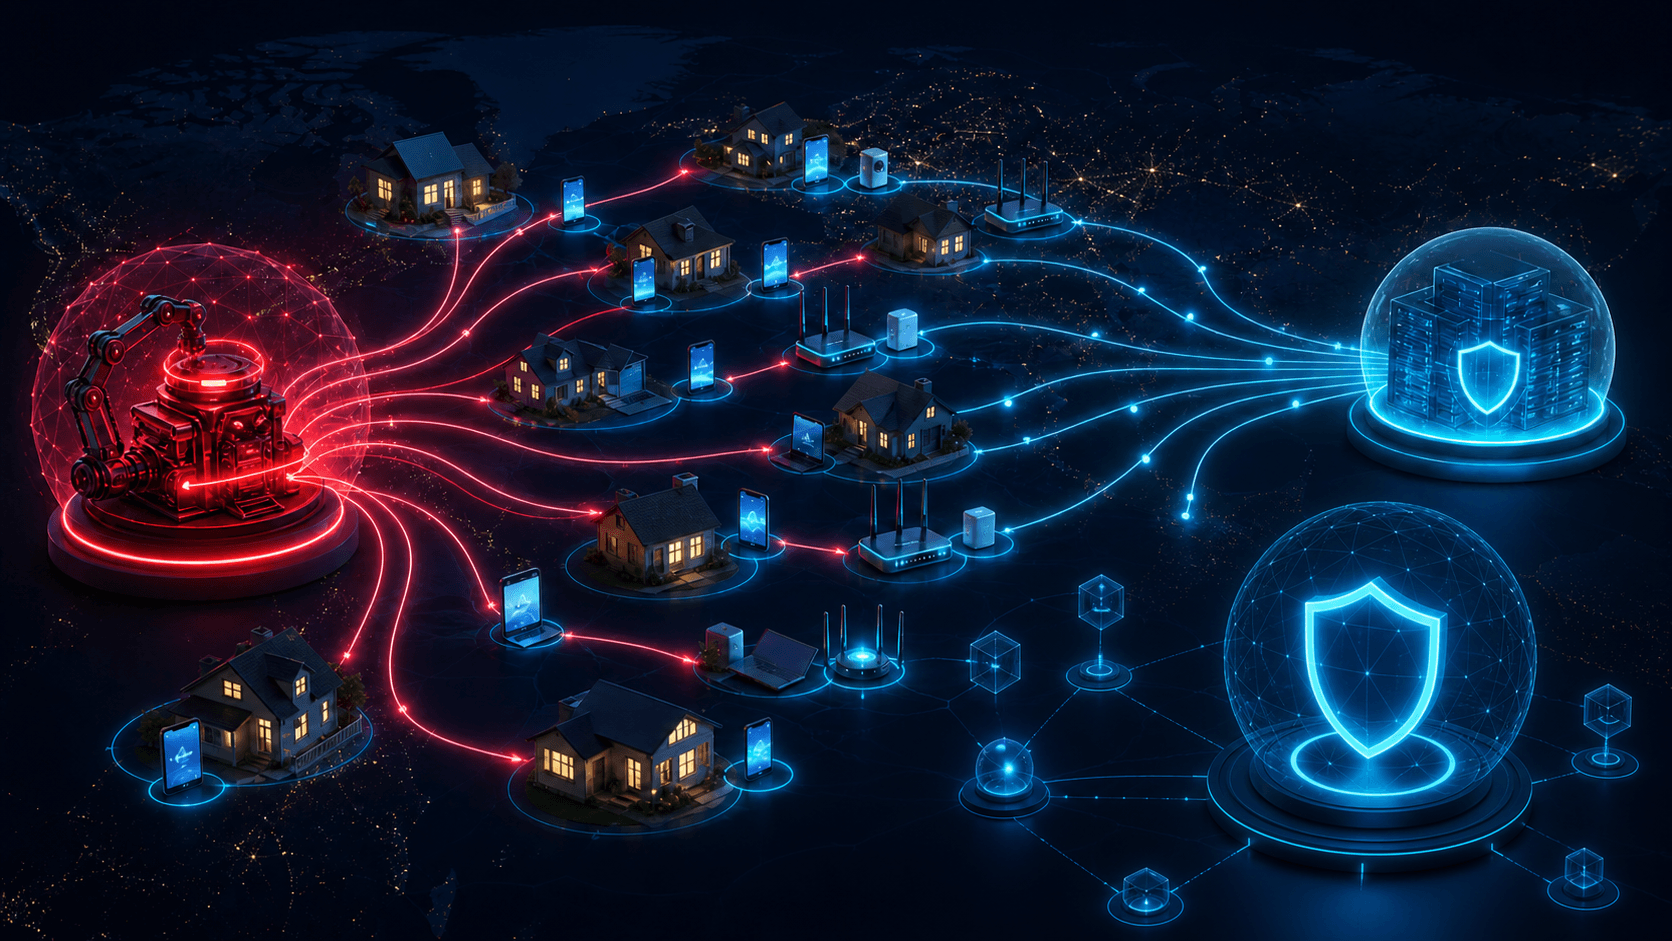
Residential Proxy Abuse: Detect Fraud Without Blocking Users
Detect residential proxy abuse by combining IP reputation, identity, velocity, device, and behavioral signals without penalizing legitimate users.
Proxy, VPN, Tor, and Datacenter IPs: A Decision Matrix for WAF, Fraud, and SIEM Rules (Without Breaking Real Users)
Not every "datacenter" IP is malicious, and not every Tor exit is a fraudster. This matrix-style guide helps you combine IP type signals with reputation and product context for safer, explainable security decisions.
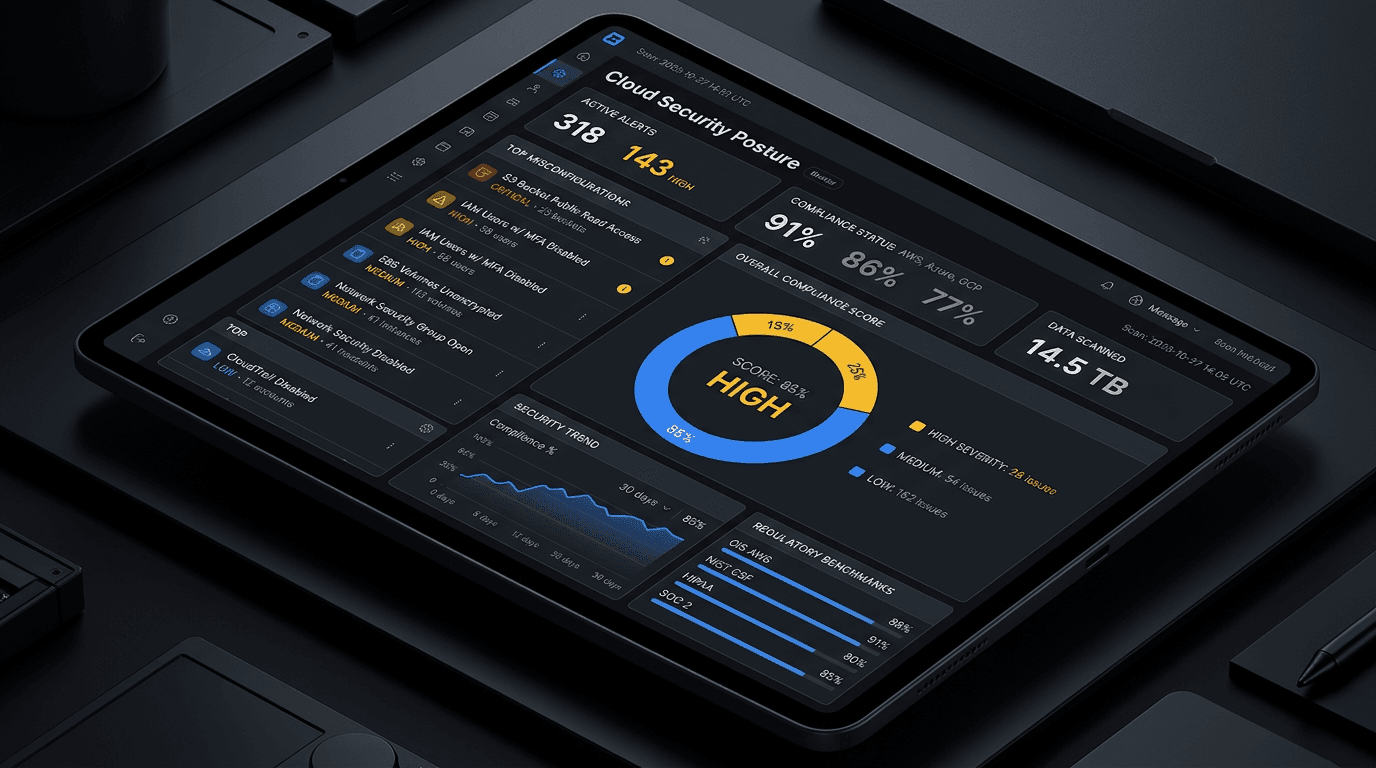
Cloud IP Reputation: What AWS, Azure, and GCP Defenders Should Track in 2026
Cloud IP addresses are shared, recycled, and abused at scale. Learn how to interpret reputation signals, reduce false positives, and align network security with platform-native controls across the three major hyperscalers.
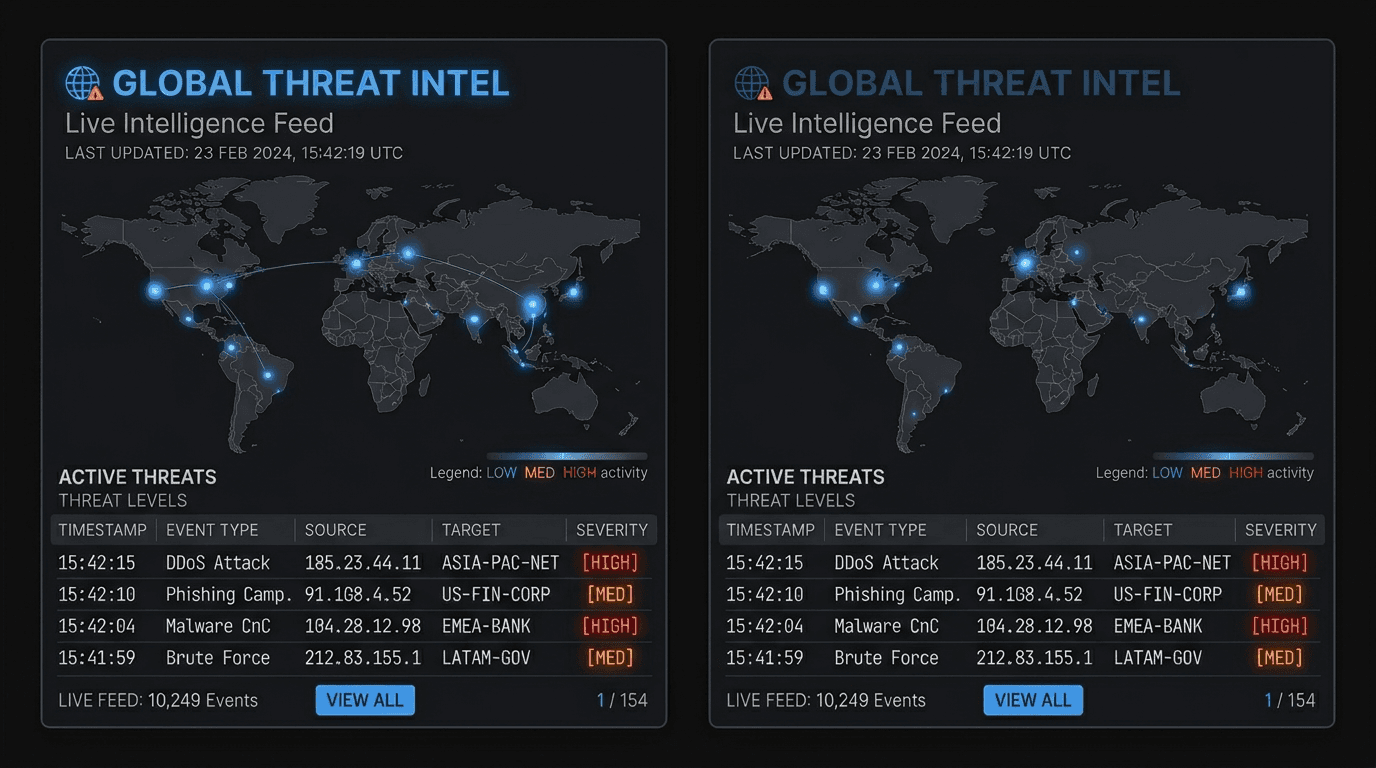
ASN Reputation for Threat Intelligence: How Autonomous System Intelligence Improves Prioritization and Hunt Programs
An IP address is a snapshot; an autonomous system (ASN) is a neighborhood. Learn how to use ASN context safely for triage, fraud, and security operations—without mistaking a giant cloud for a monolithic "bad host".
IP Lookup for Cyber Threat Detection: A Complete Security Guide
Learn how IP lookup works as a frontline defense against cyber threats. Discover how to use IP reputation data, threat intelligence feeds, and automated checks to block malicious actors before they reach your systems.